Connect your AI
Let Claude Code, Cursor, VS Code, or another MCP client read your organization's compliance data. The access is read-only, and your own AI model answers.
devguard offers your organization's compliance data as a remote MCP (Model Context Protocol) server. You bring the AI client and the model, and devguard provides the data. Your AI can list and summarize risks, policies, controls, evidence, audits, findings, and the rest of your data. It cannot change anything.
Endpoint, client settings, and limits: see Reference below.
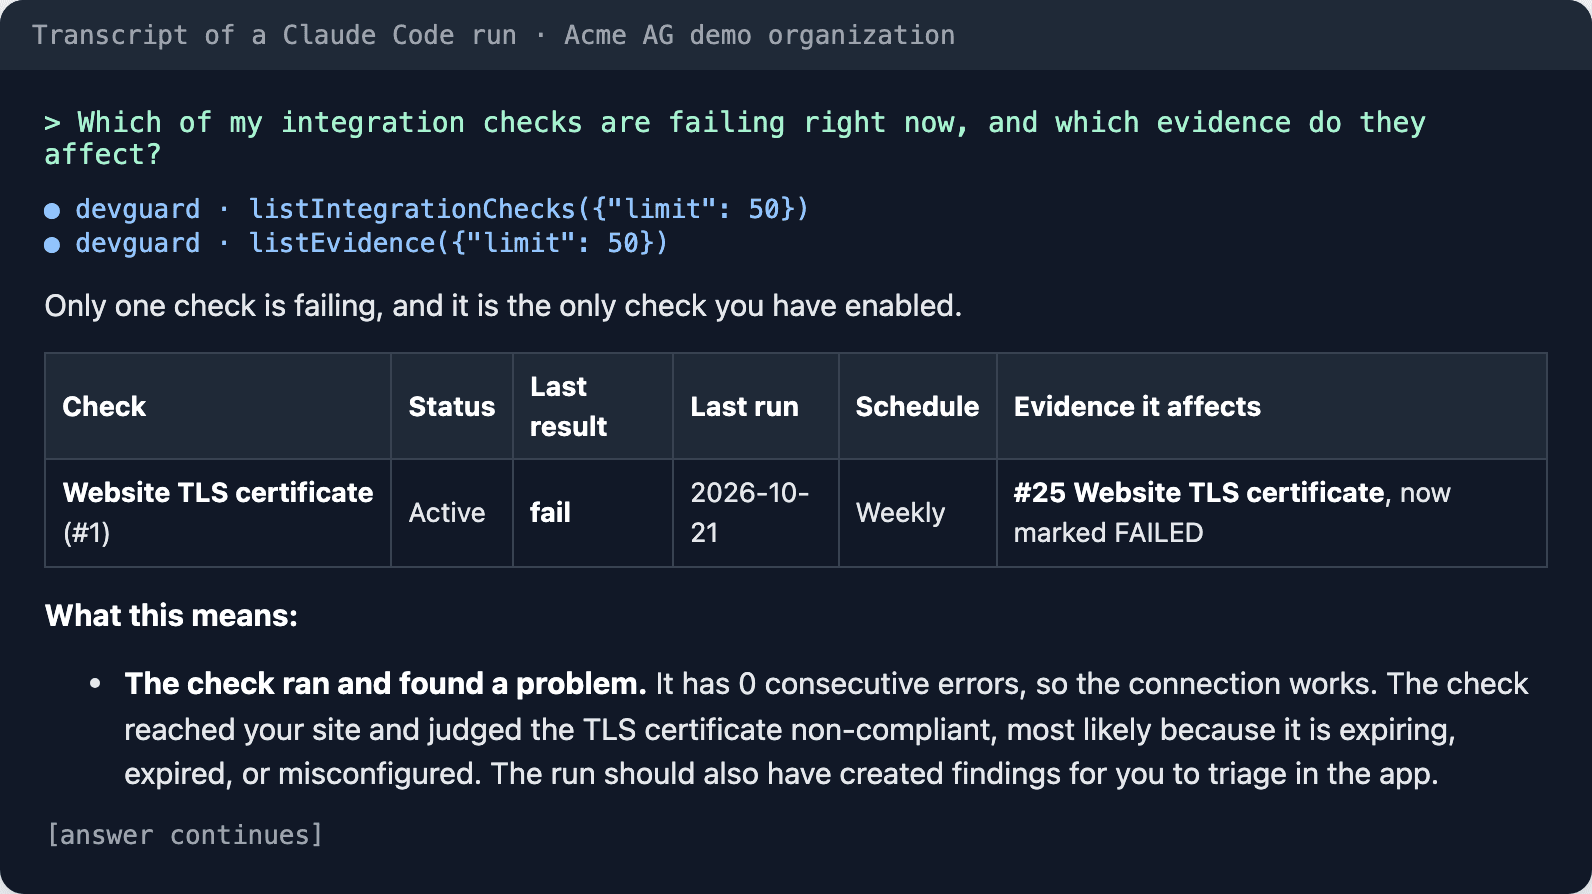
Here Claude Code answers the question Which of my integration checks are failing right now, and which evidence do they affect? The question went over this server, with an organization token in the Acme AG demo organization. The tool calls and the answer are from the real run, shortened after the first point.
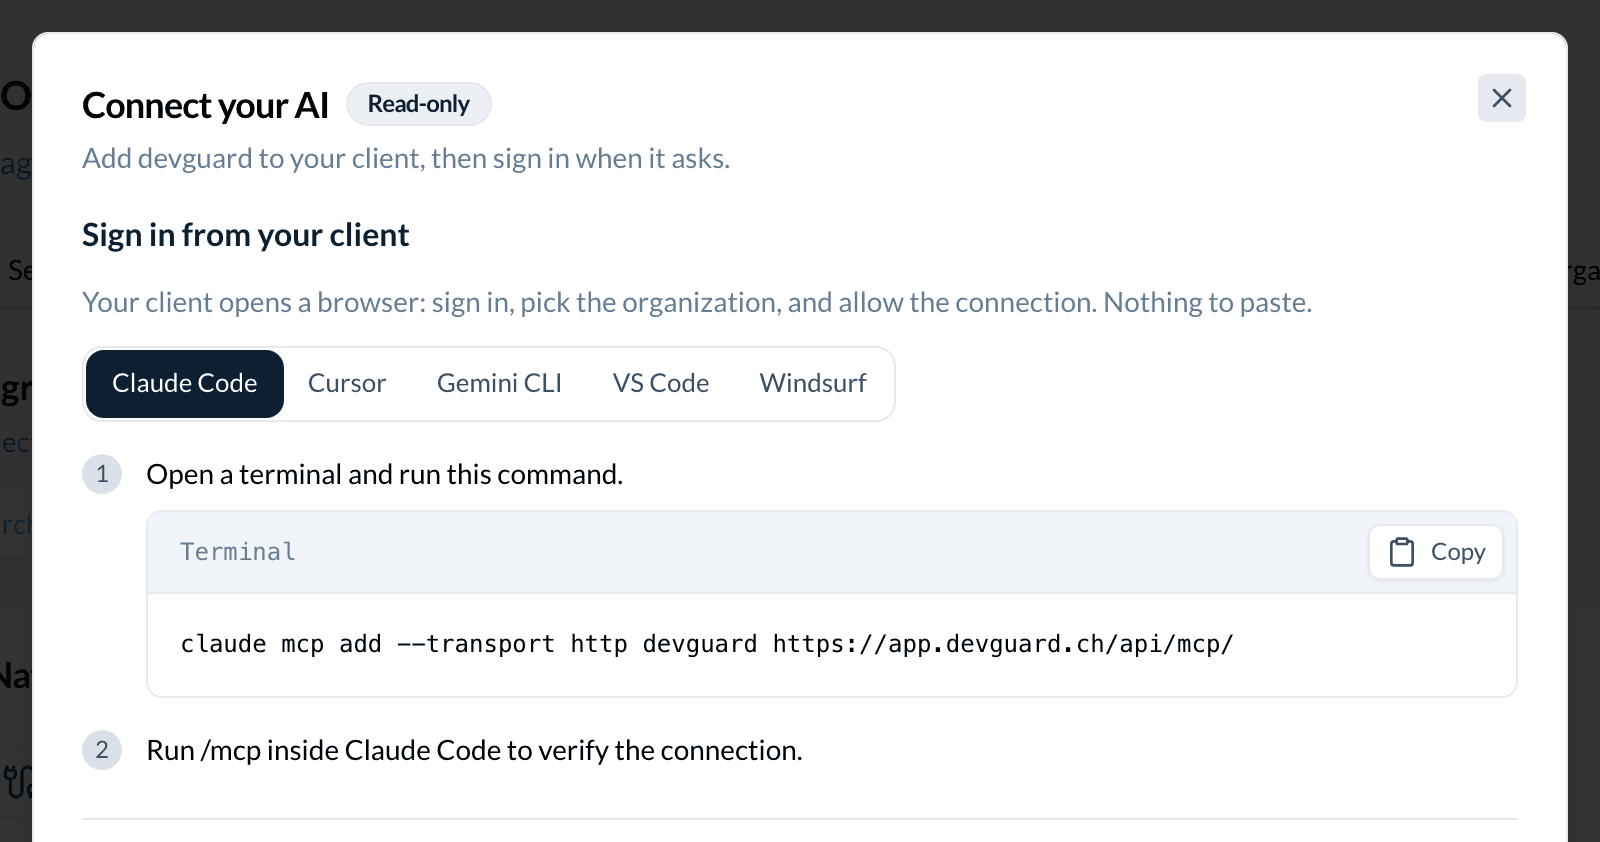
The dialog in the app, Settings → Integrations → Connect your AI, shows the command or settings block for each client, with your endpoint already filled in. This page has the same blocks. It also says what the client can read and where the limits are.
Connect a client that signs in
Claude Code, Cursor, Gemini CLI, VS Code, and Windsurf sign in through the browser. Their configuration holds no credential.
- On the MCP server row of Settings → Integrations, choose Connect your AI.
- Choose your client's tab and copy the block it shows. For Claude Code and Gemini CLI it is a command. For Cursor, VS Code, and Windsurf it is an entry for a settings file.
- Run the command, or paste the entry into the file the tab names. Then start the client.
- When the client first reaches devguard, it opens a browser. Sign in, choose the organization it may read, and allow the connection.
- Ask the assistant to list your organization's risks. If it answers from your data, you are connected. Claude Code and Gemini CLI also list the server under
/mcp.
The client keeps a short-lived token and renews it on its own. An owner or admin can end the connection at any time under Apps.
Connect a client with a token
Claude Desktop reaches remote servers through the mcp-remote bridge, so it uses a token instead. So does anything without a browser, such as a script or an agent in CI.
- Create a token. Create Token in the dialog takes you to Tokens under your account. For a token for One organization, switch on Read for All areas. An organization token with Read on All areas works as well, and it keeps working when you leave.
- Choose the Claude Desktop tab, or Other for anything else, and copy the block.
- Replace
dvg_YOUR_KEYwith the token. - For Claude Desktop, open Settings → Developer and choose Edit config. Add the entry to
mcpServersand save. Quit Claude Desktop completely and start it again. devguard then shows in the connectors menu.
Disconnect
A client that signed in holds a grant on your organization. When you remove devguard from the client's settings, that client stops. The grant stays listed under Apps until an owner or admin disconnects it there. It also ends on its own when the person who granted it is deactivated or removed from the organization.
A client configured with a token stops when the token is revoked, under Tokens or Tokens.
Reference
Endpoint
https://app.devguard.ch/api/mcp/The server uses streamable HTTP and keeps no session. Every request is a POST with a JSON answer. tools/list and tools/call need no initialize first. GET and DELETE answer 405. A request may take up to 30 seconds. A client with no credential, or an expired one, gets a 401. Its WWW-Authenticate header points to the authorization server, so a sign-in client knows where to send you.
Client configuration
Claude Code, in a terminal:
claude mcp add --transport http devguard \
  https://app.devguard.ch/api/mcp/
Cursor, in ~/.cursor/mcp.json or .cursor/mcp.json inside a project, then switch the server on in the MCP list:
{
  "mcpServers": {
    "devguard": {
      "url": "https://app.devguard.ch/api/mcp/"
    }
  }
}
Gemini CLI, in a terminal:
gemini mcp add --transport http devguard \
  https://app.devguard.ch/api/mcp/
VS Code, in .vscode/mcp.json or in the user configuration that MCP: Open User Configuration opens. Choose Start above the entry, then use the tools in agent mode:
{
  "servers": {
    "devguard": {
      "type": "http",
      "url": "https://app.devguard.ch/api/mcp/"
    }
  }
}
Windsurf, in ~/.codeium/windsurf/mcp_config.json, then refresh the server list in Cascade:
{
  "mcpServers": {
    "devguard": {
      "serverUrl": "https://app.devguard.ch/api/mcp/"
    }
  }
}
Claude Desktop, in claude_desktop_config.json; the bridge needs npx:
{
  "mcpServers": {
    "devguard": {
      "command": "npx",
      "args": [
        "-y",
        "mcp-remote",
        "https://app.devguard.ch/api/mcp/",
        "--header",
        "Authorization:${AUTH_HEADER}"
      ],
      "env": { "AUTH_HEADER": "Bearer dvg_YOUR_KEY" }
    }
  }
}
Any other client that speaks streamable HTTP: the endpoint above, and the token as a bearer header.
Authorization: Bearer dvg_YOUR_KEYWhat your AI can read
- Tools: 56 read-only queries over assets, risks, policies, controls, frameworks, coverage and the Statement of Applicability, vendors, people, devices, audits, findings, reviews, deadlines, evidence, processes and their runs, integration checks and their last verdicts, and the knowledge base search. Each tool is advertised to the client as read-only.
- Resources: single records by URI,
devguard://asset/{slug},devguard://risk/{slug},devguard://policy/{slug},devguard://audit/{slug},devguard://vendor/{slug}, anddevguard://evidence/{shortId}. - Prompts: five ready-made workflows,
gap-analysis(takes a framework),summarize-risks(an optional filter),draft-risk-treatment(a risk's short id),audit-prep(an audit's short id), andpolicy-review(a policy's short id).
Prompts that read well once connected:
- Which controls have no evidence newer than 90 days?
- Summarize our open findings by severity and owner.
- Which of my integration checks are failing right now, and which evidence do they affect?
- Which policies are overdue for their annual review?
- Prepare a briefing for the upcoming audit: open findings, failing checks, and stale evidence.
- Run the
gap-analysisprompt for ISO 27001.
Who is let in
| Credential | Reads | Refused when |
|---|---|---|
| A sign-in grant | The organization picked at sign-in | The person is deactivated or removed, or is an external contact |
A personal token (dvg_) for One organization | That organization | It lacks Read on All areas (403), or the owner has no active membership there |
| A personal token for All organizations | The organization that was active when you created it. If the owner has left it, the owner's only remaining organization | The owner has left it and belongs to more than one other organization |
An organization token (dvgo_) | Its own organization | It lacks Read on All areas (403) |
Limits
- Read-only. The server has no tool that writes.
- Every answer leaves out internal record ids. Records are named by name, slug, or short id.
- A token has a budget of 3000 checks per hour, the same as for API calls. A tool call makes at least three checks: the token, its memberships and its session. So a token covers at most about 1000 tool calls an hour. When the budget is spent, the answer is 429, "API key rate limit exceeded, retry later". A sign-in grant has no per-token budget.
- MCP requests are not AI usage. devguard runs no model for them, so they do not count against your AI quota.
How it works
The server gives your client the same read-only tools that the built-in assistant uses. It leaves out the few that only make sense inside the app, and anything that writes. The difference is which model reads the answers. In the app, devguard's model reads them. Over MCP, your own model does. That is why the request limit is on the token and not on an AI quota. It is also why the answers contain no internal ids. They go to a model outside devguard, so they name records the way a person would, by name and short id.
A sign-in and a token are two ways to say who the client acts as. A sign-in grant belongs to a person and to one organization. The client renews it, and it ends when the person leaves. A token is for a client that has no browser to sign in from. It belongs to the person or the organization that created it, and it works until it is revoked or expires. When work depends on the connection, use an organization token, because it keeps working when the person leaves.
Either way, a connection reads one organization: the one you chose at sign-in, or the one the token is bound to.
How is this guide?