Frameworks
Adopt the standards you must meet, follow your coverage, and take each framework to an approved Statement of Applicability.
A framework is a standard or a regulation, split into its controls. ISO/IEC 27001:2022 becomes its clauses and Annex A controls, GDPR its articles, SOC 2 its criteria. devguard publishes a catalog of official frameworks and keeps them current. You cannot edit their controls. A custom framework is one that your organization writes itself, for example for a contract or an internal baseline. You can edit it freely.
A framework does nothing until you adopt it. After that, its controls accept the policies, risks, assets and evidence that implement them, and devguard counts your coverage. The framework then appears on the dashboard, on the Roadmap and in the Statement of Applicability. devguard links many controls to the matching control in another framework. If you adopted both frameworks, the work for one control also counts for the other.
From adoption to audit
The work on a framework happens in this order. Each step links to its instructions.
- Adopt the framework.
- Create the tasks and plan the roadmap toward the date you want to be ready for the audit.
- Link the policies, risks and assets that implement each control. A link makes the control Partial.
- Attach the evidence that shows each control at work. The Statement of Applicability counts it for the auditor.
- Assess each control as Full on the mapping card of the risk, asset or policy section that covers it.
- Mark not applicable the controls that do not apply, with a justification.
- Approve and download the Statement of Applicability for the auditor.
You can also build a custom framework or unadopt a framework. Scripts and integrations: see API below.
Adopt a framework
- Open Frameworks. Find the framework with the search or with the tabs Available and Official.
- Choose Adopt on its card.
- If the Framework wizard opens, decide whether devguard creates the framework's implementation tasks:
- To adopt without tasks, leave Create implementation tasks off and choose Save.
- To create the tasks, turn on Create implementation tasks and choose Save.
- To create the tasks and give them deadlines, also pick 3 months, 6 months or 12 months, or a date under Finish by (optional). Then choose Save.
- To take the adoption back, choose Cancel. devguard unadopts the framework again. Cancel only closes the wizard when the adoption completed the ISO/IEC 27001 and ISO/IEC 27002 pair, or when your role may not unadopt frameworks. The framework then stays adopted.
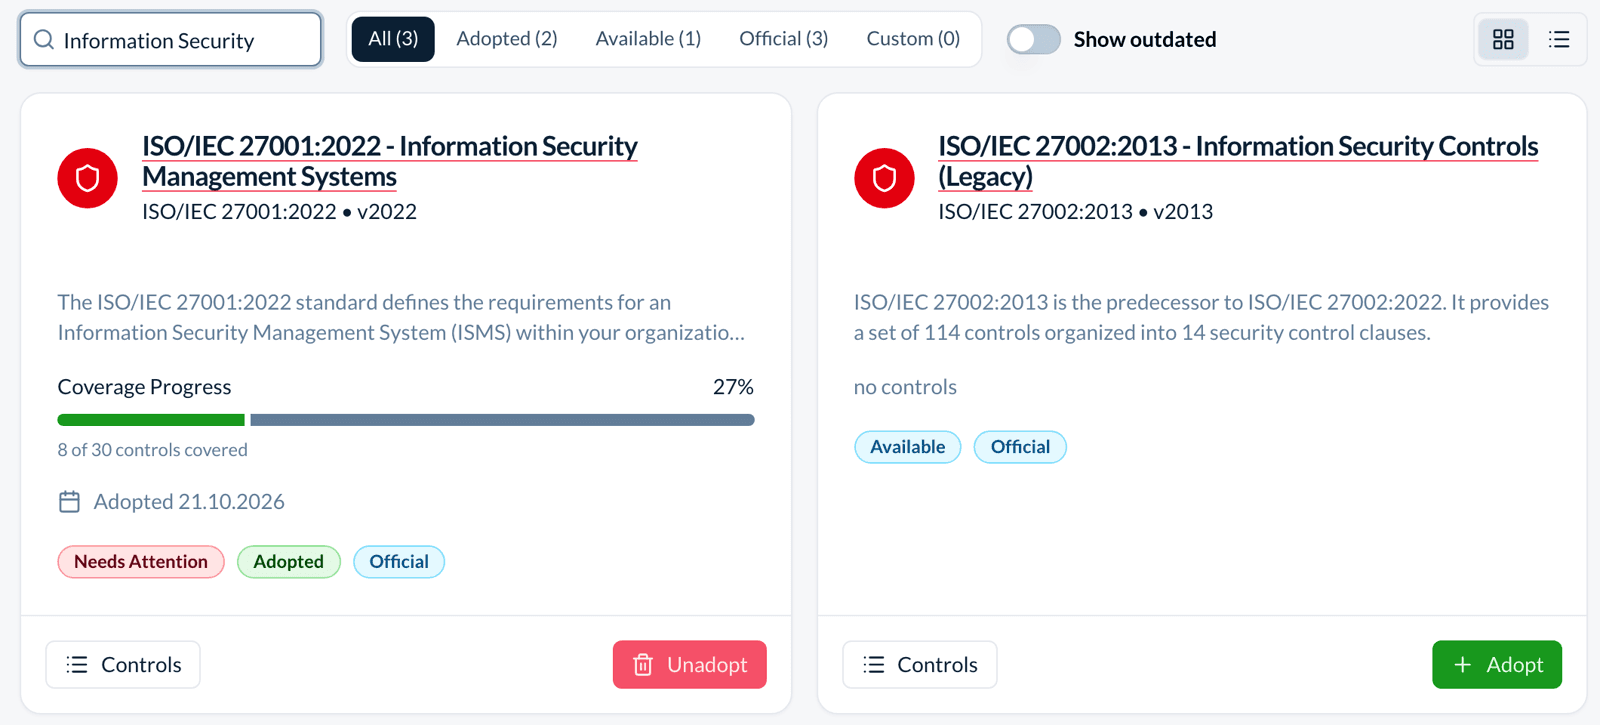
Adopt is also in the framework's row in the list view. On the framework's page, it is in the Adoption panel and the Actions menu. The Framework wizard opens only when devguard ships task templates for the framework. Adopting alone creates no tasks: you can create them later from the framework's Roadmap tab. Owners and admins adopt frameworks. On the Free plan, an organization can adopt one framework (see Plan limits).
Adopting ISO/IEC 27001 also adopts ISO/IEC 27002. In devguard, the Annex A controls of ISO/IEC 27001 are a separate framework, listed as ISO/IEC 27002:2022 - Information Security Controls. It is the companion of ISO/IEC 27001 and arrives in the same step. The pair uses one adoption slot. You unadopt ISO/IEC 27002 together with ISO/IEC 27001, never alone. If you adopted ISO/IEC 27002 first, adopting ISO/IEC 27001 links the two.
The two frameworks of the pair keep separate controls. ISO/IEC 27001 holds clauses 4 to 10, and ISO/IEC 27002 holds Annex A. So each one has its own Roadmap tab, and you plan each one there. Planning ISO/IEC 27001 gives no date to the Annex A tasks. An internal audit of Annex A uses ISO/IEC 27002 as its framework. See Audit programme.
Create the tasks
A framework that you adopted without its tasks shows No tasks yet on its Roadmap tab.
- Open the framework and its Roadmap tab.
- Choose Create tasks. The Framework wizard opens with Create implementation tasks turned on.
- To give the tasks deadlines at once, pick a date under Finish by (optional).
- Choose Save. Here Cancel only closes the wizard.
devguard creates one task for each task template of the framework. The tasks start without an owner, and without a deadline unless you picked a date. Creating the tasks of ISO/IEC 27001 also creates those of ISO/IEC 27002. If an earlier unadopt archived tasks of the framework, they come back in this step (see Unadopt a framework).
Plan the roadmap
- Open the framework and its Roadmap tab.
- Choose Plan roadmap. The Plan roadmap dialog shows how many tasks exist and how many are open.
- Pick 3 months, 6 months or 12 months, or type a date at least two weeks away.
- Choose Plan roadmap.
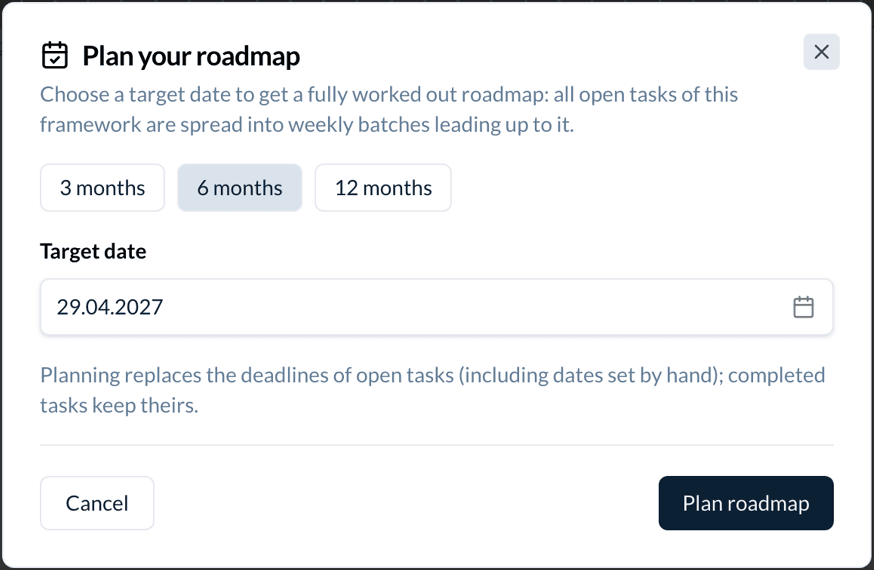
devguard gives a deadline to each open task that came with the framework. It spreads the tasks evenly from one week after today to the target date, in the order of the templates. Each deadline falls on a Friday. Tasks in the last week get the target date itself. When you plan again, these tasks get new dates, even dates that someone set by hand. Tasks that are done or cancelled keep their dates. Tasks that people added themselves are never moved.
After planning, the button shows Target with the date, and a dashed line marks the date on the Roadmap. The button appears once the framework has tasks. A framework without task templates has neither Create tasks nor Plan roadmap. Tasks that you create for its controls still appear on its timeline.
Approve the Statement of Applicability
The Statement of Applicability lists every control of the framework. For each control it shows the status, the number of evidence records and the records behind it. For each excluded control it shows the justification. devguard builds the statement from the coverage you recorded. A person in a role that you choose approves it.
- Open the framework's page.
- In the Adoption panel, pick a business role under Statement of Applicability approver. Create the role first if it does not exist.
- Choose Actions → Generate Report. Reports opens and shows the current draft as a PDF.
- Choose Reset in the Actions panel on the right. The PDF closes and the report settings come back. The framework is still selected.
- Choose Approve as version 1, next to Generate Report. Only members of the approver role see this button. The number goes up by one with each approval.
- Pick the approved version under Version. Choose Generate Report, then Download PDF, and give the file to the auditor.
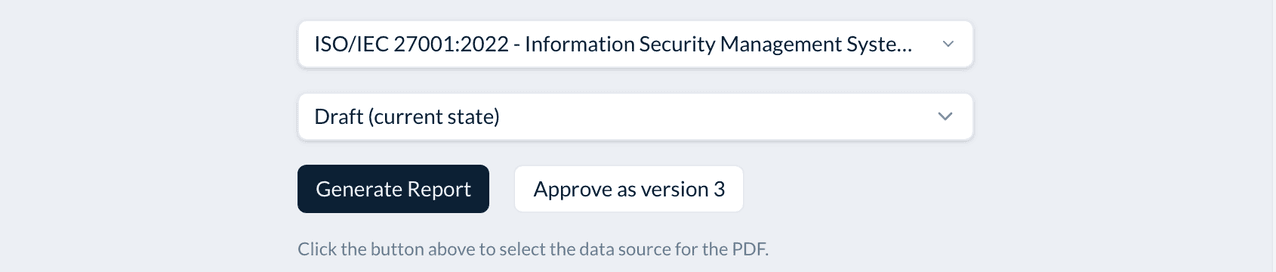
No approve button? Only members of the approver role see it. Being an owner or an admin is not enough. An auditor cannot approve, even as a member of the role. If the settings show "No approver role is set for this framework yet", step 2 is missing. Choose Set it on the framework next to the message to go back.
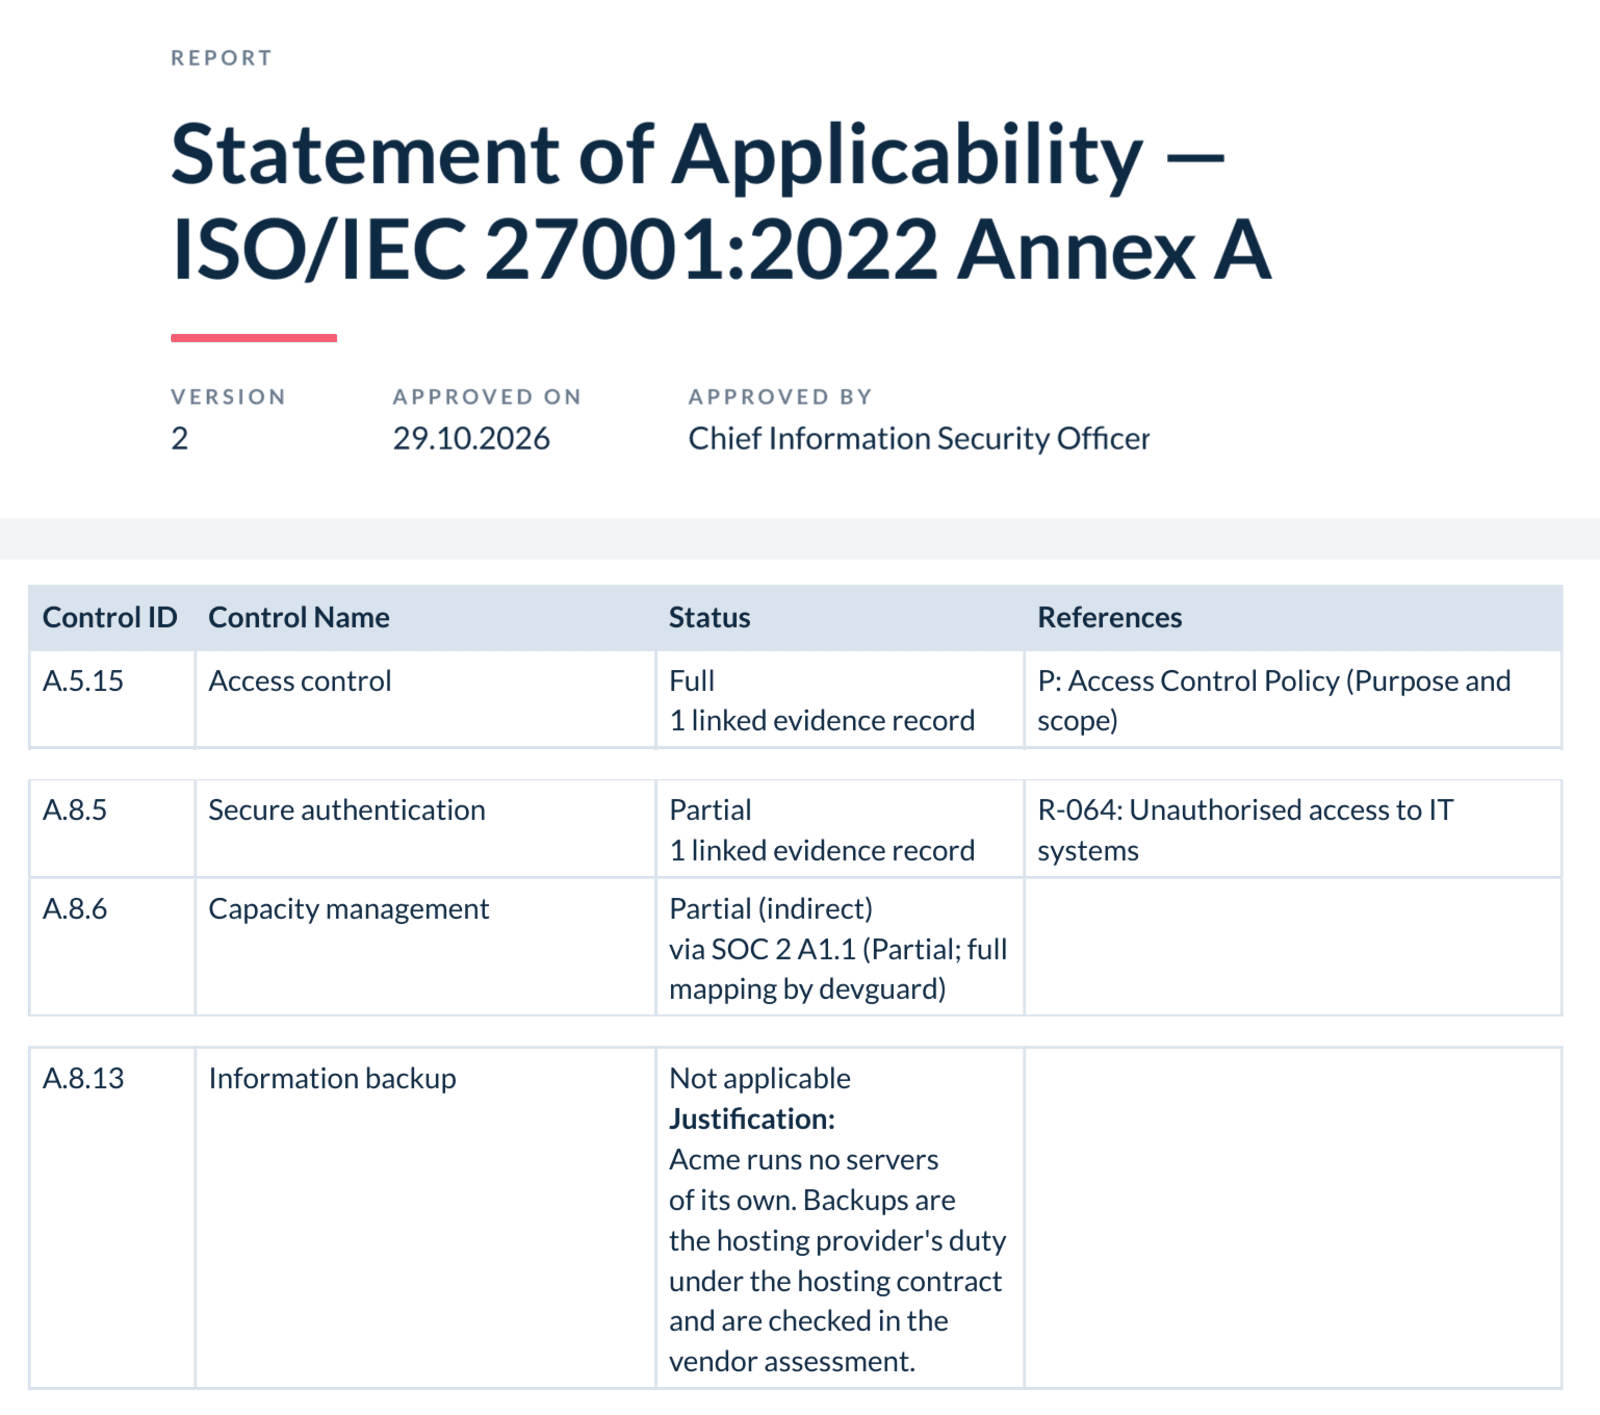
An approved version does not change. The Version list keeps every approved version for download, and they stay when you unadopt the framework. The approver belongs to the main framework of a pair. So ISO/IEC 27002:2022 does not show the setting when you adopted it with ISO/IEC 27001. The statement sorts controls as text, so A.8.10 comes before A.8.2. Reports describes the columns.
Build a custom framework
Create
- Choose Add framework on the Frameworks page.
- Fill in the fields.
- Save. devguard adopts the framework at once and lists it under Custom.
- Add controls with Add control on its card or in its Actions menu. See Controls.
Edit changes the name, identifier, version, color and description. Delete removes the framework with all its controls and their comments. The app offers Delete only while the framework is not adopted.
Import
You can move a custom framework as a CSV file, with its cross-links. So you build a baseline once and import it into every organization of a mandate.
- Choose Import framework on the Frameworks page and pick the file.
- Read the preview. Errors block the import. The preview also lists cross-links that change or that devguard cannot find.
- Choose Import. devguard creates the framework and adopts it at once.
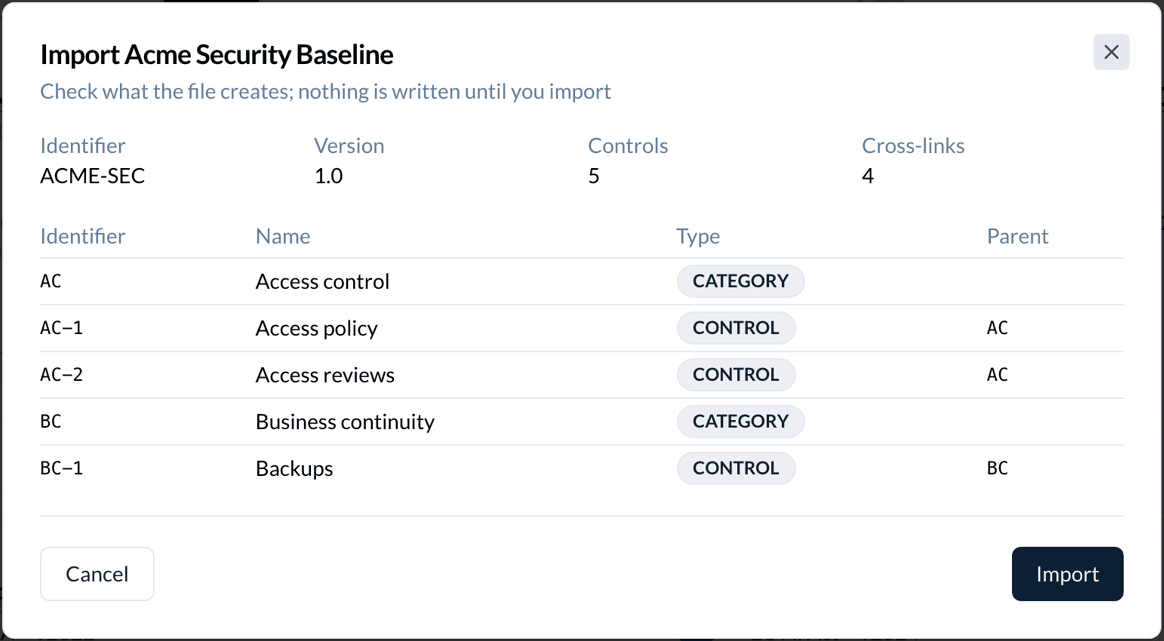
The format and every rule of the preview are in The framework file.
Export
Choose Export framework in the framework's Actions menu, or Export on its card. Any member can export. The export stops if the framework has no controls. It also stops if a control identifier repeats or contains ; or =, and it names those controls. You cannot export official frameworks, because every organization has them already.
Unadopt a framework
- Choose Unadopt on the card, in the list, or in the framework's Actions menu.
- If a dialog lists links to policies, assets or risks, remove those links first.
- Confirm with Remove Framework.
devguard removes the adoption, with its statuses, justifications and links. It archives the tasks that came with the framework. If you adopt the framework again and create its tasks, they come back with their status and assignee. Unfinished tasks come back without a deadline. Tasks that people added stay, but lose their link to the control. Approved versions of the Statement of Applicability stay.
How coverage is counted
Coverage is the share of a framework's controls that something covers. You see it on the framework's card and in its Adoption panel. The Roadmap tab splits it into Full, Partial and Open, and the dashboard adds up all frameworks.
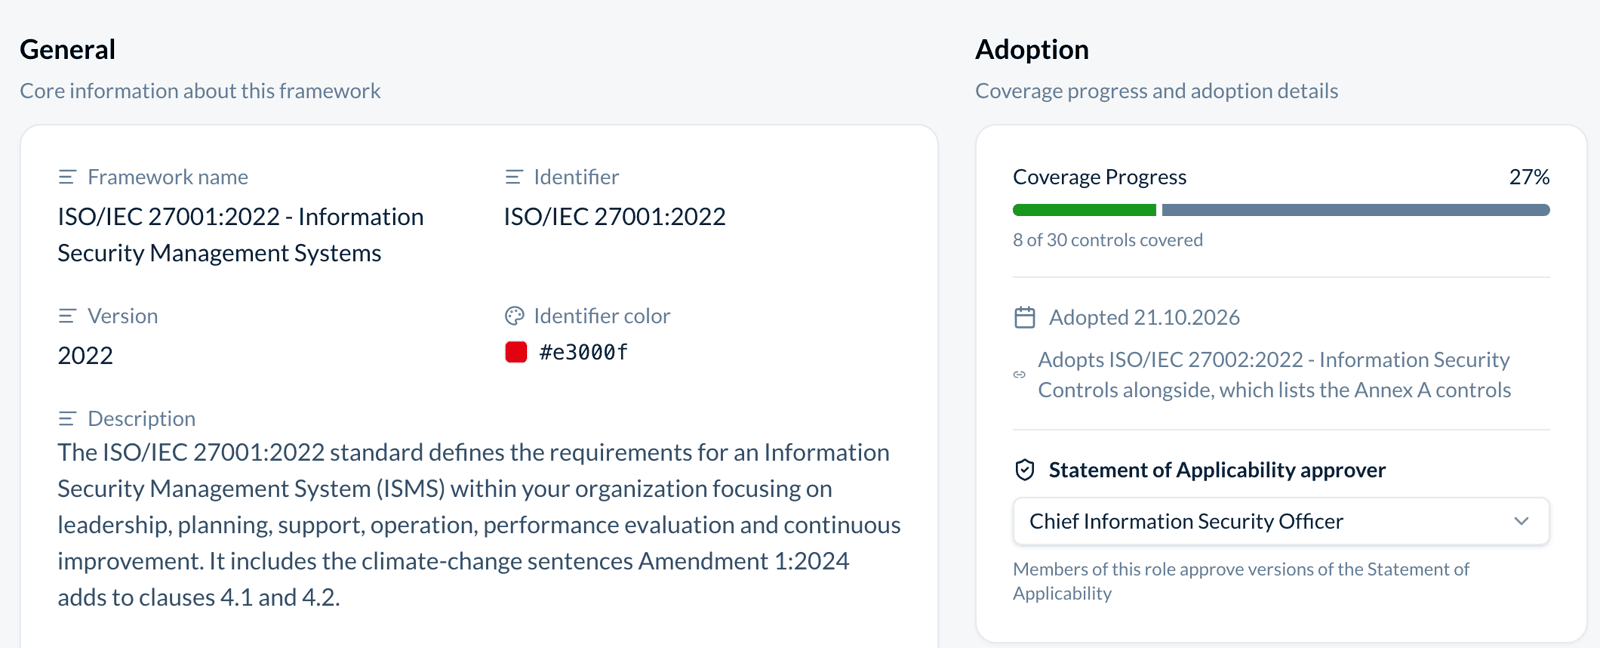
The two numbers differ because coverage counts only the controls that state a requirement: the types Control, Clause and Amendment. Chapters, categories and groups only organize the list, so they never count.
A control counts as covered when its status is Full or Partial. This includes Partial that comes through a cross-link from another framework (indirect coverage). A control that you marked not applicable leaves the total. So an exclusion raises the percentage, but it hides nothing: the Statement of Applicability lists it with its justification. Coverage shows the figure control by control. Coverage badges gives the thresholds.
Reference
The Frameworks page
The search matches the framework name. The tabs All, Adopted, Available, Official and Custom filter the list. The switch at the far right shows cards or a table. Your browser remembers the choice.
An outdated edition has an end date, such as CCM v4.0 after v4.1. The page hides it unless your organization adopted it. Show outdated lists only the outdated editions. You can still adopt one, and its badge shows the end date.
A framework's page
| Tab | Content |
|---|---|
| Detail | Fields, the reference used in framework files, the Adoption panel or Adopt card, and, once adopted, starter content. |
| Controls | The control tree with your coverage status; the badge counts every entry. |
| Roadmap | Full, Partial and Open, Create tasks or Plan roadmap, and the framework's lane of the timeline. |
| History | Adoptions, plans, exports and approver changes. |
Coverage badges
| Coverage | Badge |
|---|---|
| 100% | Completed |
| 80% to 99% | On Track |
| 50% to 79% | In Progress |
| below 50% | Needs Attention |
The percentage is rounded to a whole number.
Fields of a custom framework
| Field | Required | Content |
|---|---|---|
| Framework name | yes | The name shown everywhere. |
| Identifier | yes | A short code such as ACME-SEC, unique in your organization. Its slug is the reference in framework files. |
| Version | yes | Free text. |
| Identifier color | no | Color of the badge and card icon: a hex code such as #1d4ed8, an rgb() or hsl() color, a CSS color name or a linear-gradient(), up to 200 characters. |
| Description | no | Purpose and scope. |
The catalog
Only ISO/IEC 27001:2022 adopts a companion. You adopt every other framework on its own, Annex A editions included.
| Group | Frameworks |
|---|---|
| Management systems | ISO 9001:2026, ISO 9001:2015 (outdated), ISO 14001:2026, ISO 45001:2018, ISO 45001:2018/Amd 1:2024 (outdated), ISO/IEC 27001:2022, ISO/IEC 27001:2022/Amd 1:2024 (outdated), ISO/IEC 27002:2022, ISO/IEC 27017:2026, ISO/IEC 27017:2015 (outdated), ISO/IEC 27018:2025, ISO/IEC 27701:2025 and its Annex A, ISO/IEC 42001:2023 and its Annex A |
| Laws and regulations | GDPR, Swiss nFADP, NIS2 Directive, DORA, EU AI Act, HIPAA |
| Industry frameworks | SOC 1, SOC 2, NIST CSF 2.0, CIS Controls v8.1, CCM v4.1, CCM v4.0 (outdated), PCI DSS v4.0.1, OWASP Top 10:2025 |
The list on the Frameworks page is what counts for your organization. It can also hold a retired edition such as ISO/IEC 27002:2013 (Legacy). devguard removed it from the catalog, and it has no controls. It leaves your list at the next full catalog update, unless your organization adopted it.
Plan limits
| Plan | Framework adoptions | Custom frameworks |
|---|---|---|
| Free | 1 | 1 |
| Business | unlimited | unlimited |
Only adoptions of official frameworks count toward the first limit, and a pair counts once. Creating or importing a custom framework counts toward the second limit, not the first. At a limit, Adopt, Add framework and Import framework open the upgrade dialog.
Permissions
| Action | Owner, Admin | Member | Auditor |
|---|---|---|---|
| See frameworks and coverage | yes | yes | yes |
| Export a custom framework | yes | yes | yes |
| Adopt, create, import | yes | no | no |
| Edit, create tasks, plan, set the approver | yes | no | no |
| Unadopt, delete | yes | no | no |
| Approve the Statement of Applicability | only in the approver role | only in the approver role | no |
An organization token can do what an admin can.
API
The public API covers adopting, planning and custom frameworks. Import, export, the approver role and the Statement of Applicability (approval, versions, PDF) are in the app only. Every call needs organizationId, even where the schema marks it optional. The full reference is at docs.devguard.ch/api.
GET /frameworks/: Lists frameworks with your adoption. Query:organizationId.GET /frameworks/{id}/: One framework with its controls. Query:organizationId.GET /frameworks/adopted/: Adoptions with covered and total counts. Query:organizationId.POST /frameworks/adopt/: Adopts. Body:frameworkId,organizationId; optionalcreateTasks(defaultfalse) also creates the tasks.POST /frameworks/create-tasks/: Creates the tasks from the framework's task templates. Body:frameworkAdoptionId,organizationId.DELETE /frameworks/unadopt/: Unadopts. Query:frameworkAdoptionId,organizationId.POST /frameworks/plan-roadmap/: Gives open tasks deadlines. Body:frameworkAdoptionId,organizationId,targetDate.POST /frameworks/: Creates a custom framework. Body:organizationId,identifier,name;versiondefaults to1.0.PATCH /frameworks/{id}/: Updates a custom framework. Body:organizationId,identifier,name; optionalversion,identifierColor,description.DELETE /frameworks/{id}/: Deletes a custom framework, adopted or not. Query:organizationId.GET /coverage/adoptions/: Adoptions withcoverageStats. Query:organizationId.
adopt returns the adoption with hasTaskTemplates and taskTemplateCount. create-tasks returns { createdCount }, the number of tasks created or restored. It skips templates that are already tasks, so calling it again is safe, and for ISO/IEC 27001 it also creates the tasks of ISO/IEC 27002. targetDate is an ISO date at least 14 days away. coverageStats holds the total, covered, full, partial, uncovered and not-applicable counts, and the percentage.
This call plans a roadmap. DG_TOKEN is your API token, DG_ORG your organization id, and DG_ADOPTION the adoption's id from GET /frameworks/adopted/:
API=https://app.devguard.ch/api

curl -sS -X POST "$API/frameworks/plan-roadmap/" \
  -H "Authorization: Bearer $DG_TOKEN" \
  -H "Content-Type: application/json" \
  -d "{\"organizationId\": \"$DG_ORG\",
       \"frameworkAdoptionId\": \"$DG_ADOPTION\",
       \"targetDate\": \"2027-04-30\"}"
The answer is { "scheduledCount": 42, "targetDate": "2027-04-30T00:00:00.000Z" }. scheduledCount is the number of tasks that got a deadline.
| Error code | When |
|---|---|
NOT_FOUND | The framework or adoption is not visible to the organization. |
CONFLICT | Already adopted, or the identifier is taken. |
PRECONDITION_FAILED | Unadopt blocked by links, or by the 27001 pair. |
BAD_REQUEST | Target date less than 14 days away. |
FORBIDDEN | A plan limit: LIMIT_REACHED:frameworkAdoptions or LIMIT_REACHED:customFrameworks. |
Errors return as { message, code, status }.
The AI assistant, and through it the MCP server, reads approved versions of the Statement of Applicability. The tool listSoaVersions lists them and getSoaVersion reads one. Both take frameworkSlug, such as iso-27001-2022. Without version, getSoaVersion returns the latest version.
The framework file
One row is one control. devguard reads the framework columns from the first row; they can be empty on the other rows. The columns can come in any order, and devguard ignores unknown columns.
| Column | Content |
|---|---|
frameworkIdentifier | Required, the same on every row. |
frameworkName | Required. |
frameworkVersion | 1.0 when empty. |
frameworkDescription | Optional. |
frameworkColor | Optional, such as #1d4ed8. |
identifier | Required, unique in the file. |
parent | The parent's identifier; empty at the top. |
type | CATEGORY, CONTROL, CLAUSE, CHAPTER, AMENDMENT or GROUP; CONTROL when empty. |
isMandatory | true/false, yes/no, 1/0; true when empty. |
name | Required. |
purpose, description | Optional; the description takes Markdown. |
links | Cross-links, see below. |
linkNotes | One rationale per line, in the order of the links. |
The structure of a file, without the optional columns:
frameworkIdentifier,frameworkName,identifier,parent,type,name
ACME-SEC,Acme Security Baseline,AC,,CATEGORY,Access control
ACME-SEC,,AC-1,AC,CONTROL,Access policy
ACME-SEC,,AC-2,AC,CONTROL,Access reviews
ACME-SEC,,BC,,CATEGORY,Business continuity
ACME-SEC,,BC-1,BC,CONTROL,Backups
Write a cross-link as reference:identifier. Add =PARTIAL for a partial match; a full match needs nothing. Separate links with ;. A framework's page shows its reference as Reference in framework files, such as iso-27002-2022. A link inside the same file uses the slug of the imported framework's identifier. The same controls with their links:
identifier,links,linkNotes
AC-1,iso-27002-2022:A.5.15,Both need an access policy
AC-2,iso-27002-2022:A.5.18=PARTIAL; acme-sec:AC-1,
BC-1,iso-27002-2022:A.8.13,Restore tests cover backups
To give the second link of a row a rationale, start a new line in its linkNotes cell (Alt+Enter, or Option+Enter on a Mac). The first line belongs to the first link, the second line to the second link.
| Outcome | Case |
|---|---|
| Blocks the import | An empty file; no framework identifier or name; a row with another frameworkIdentifier; a row without identifier or name; a repeated identifier; a parent not in the file, or a loop of parents; an unknown type or isMandatory value; an unreadable link; more than 50 links on a row or 20,000 in the file; more linkNotes lines than links; a rationale over 2,000 characters; an identifier your organization already uses. |
| Imports with a change | A full match without a rationale becomes Partial. Two controls of the file that link each other at different levels get one link, at Partial. |
| Skips the link | The target framework does not exist or is not adopted; the control is not in it or matches more than one; a control links to itself. |
Each error names its row; the header is row 1. A file holds up to 5,000 rows. A cell holds up to 500 characters, the name 1,000, and descriptions and purposes 20,000. Links to policies, risks and other records are not part of the file, because those records belong to one organization.
How is this guide?