Reports
Turn your registers, reviews and audits into PDF files that you can give to an auditor, your management or a customer.
Reports is where devguard turns your data into PDF files. An auditor asks for documents such as the Statement of Applicability, the risk register or the result of an access review. Each of these is one card on the Reports page. You choose what goes in, generate the PDF and download it.
The tasks below follow the order of the work:
- Find the report for a request
- Generate a report
- Mark the PDF as confidential
- Start from the record instead
To learn when a report goes out of date, see What a report shows. Scripts and links: see For developers.
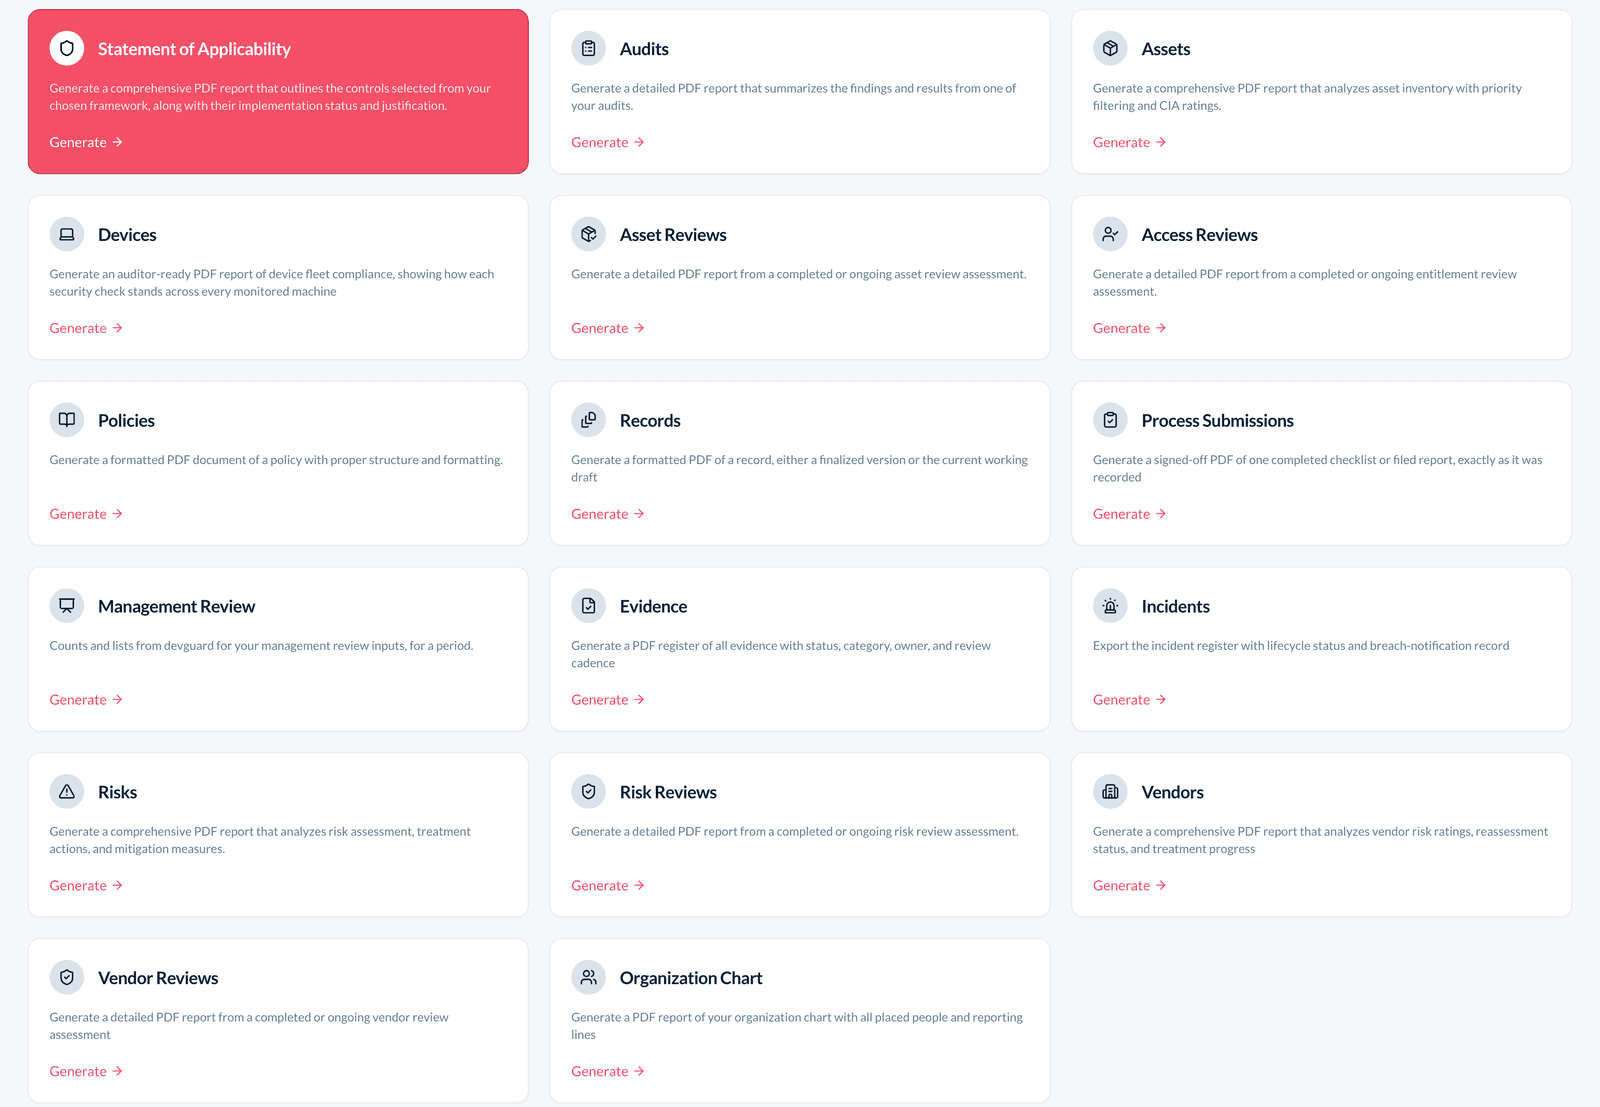
Find the report for a request
Most requests from an auditor match one card. Find the request in the table, then generate the card next to it.
| The request | The card |
|---|---|
| Which controls apply to you, and why are others excluded? | Statement of Applicability |
| Show us the risk register and the treatment. | Risks |
| Show that the risk owners reviewed the risks. | Risk Reviews |
| Show the inventory of information assets. | Assets |
| Who reviewed access rights, and what did they decide? | Access Reviews |
| Show the list of suppliers and their risk. | Vendors, and Vendor Reviews for the periodic check |
| Show the policy as approved. | Policies, with a published version |
| Show this record as finalized. | Records, with a finalized version |
| Show the evidence for the controls. | Evidence |
| Show the result of your internal audit. | Audits |
| Show the inputs to the management review. | Management Review |
| Who reports to whom? | Organization Chart |
| Are the laptops encrypted and up to date? | Devices |
| Show all incidents and which were personal data breaches. | Incidents |
Generate a report
This example makes the report of an external audit. All reports work the same way.
- Open Reports and choose Generate on the Audits card.
- Open the dropdown and choose the audit. Reports on a register, such as Assets or Risks, ask for a scope instead. Some reports, such as Evidence, ask for nothing.
- Choose Generate Report. A large report can take up to a minute. Keep the tab open while the preview area shows Generating the report.
- Check the preview. Then choose Download PDF in the Actions panel.
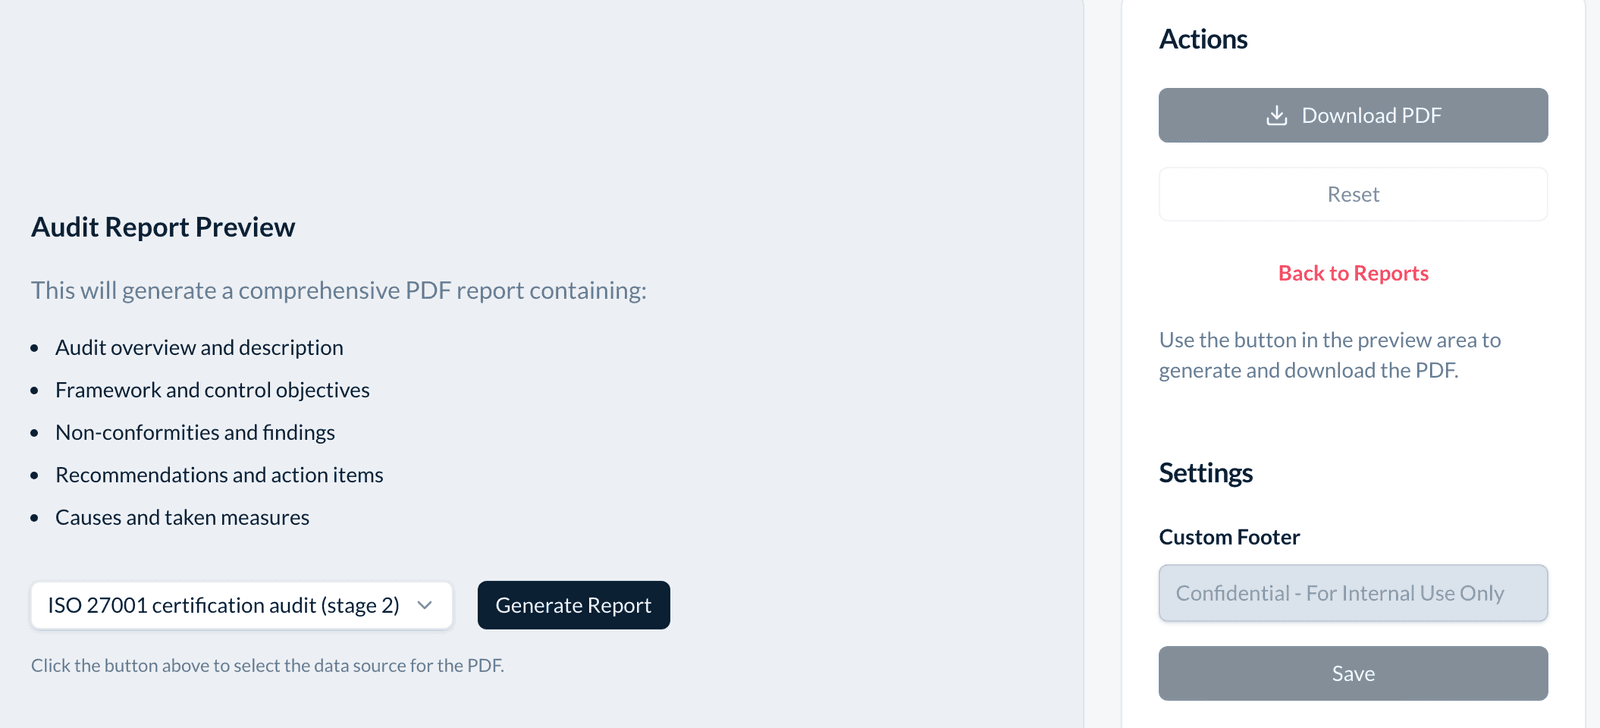
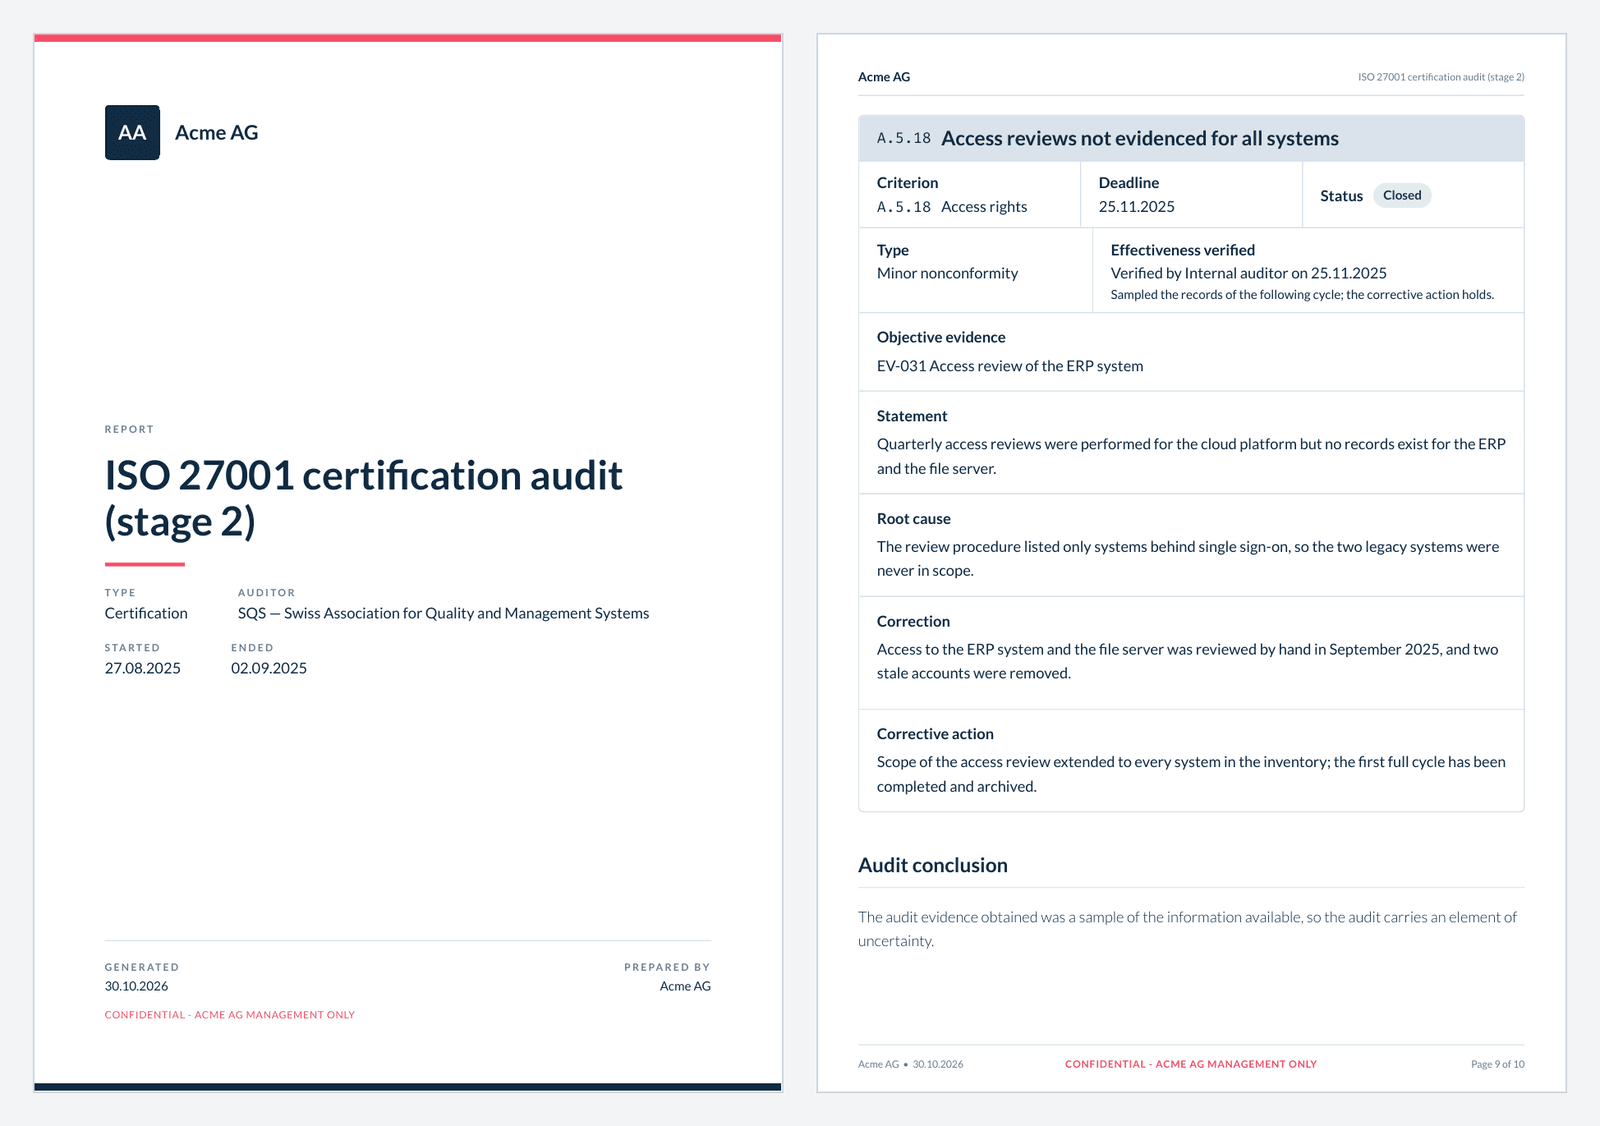
To make the report for another audit, choose Reset. The preview closes and you can choose again. Back to Reports returns to the list of cards.
After you download
devguard does not keep a copy of the PDF. To keep it as proof in devguard:
- Attach the PDF to an evidence record. See Attach the file.
- Link the record to the audit's findings or to the controls it supports.
- For a management review, upload the PDF to the review submission instead.
What a report shows
A report shows your data as it is at the moment you generate it. The file does not change when your data changes later. So if you fix something after you download, generate the report again and send the new file.
Three reports can also print a fixed version instead of today's data: the Statement of Applicability (approved versions), Policies (published versions) and Records (finalized versions). Give an auditor the fixed version: it shows what was approved and when.
Mark the PDF as confidential
A custom footer prints a line such as "Confidential" on the cover and at the foot of every page. Use it to show who may read the file.
- Generate the report first. The Custom Footer field stays off until the preview is ready.
- Under Settings, type the text in Custom Footer. For example: "Confidential - Acme AG management only".
- Choose Save. devguard generates the report again with the footer.
- Choose Download PDF.
The footer prints in capital letters, as in the audit report above. devguard does not save it. When you open the report again, the field is empty.
Start from the record instead
You do not have to go through the Reports page. Many pages link to their report and open it with the record already chosen.
| Where you are | What to choose | What opens |
|---|---|---|
| An adopted framework | Actions, then Generate Report | Statement of Applicability. See Frameworks. |
| An audit | Actions, then Generate Report | Audit Report. See Audits. |
| A policy in the editor | Generate Report | Policy Report. See Policies. |
| A record | Actions, then Generate Report | Record Report. See the warning below. |
| A risk, asset, access or vendor review | Actions, then Generate Report | The report for that review |
| A management review process or submission | Open the inputs report for this period | Management Review, with the period filled in |
Watch out: a report opened from a record, or from a link to a record report, prints the current working draft, even when the record is final. To print the finalized version, choose Reset, choose the record again, then choose Generate. The newest finalized version is then selected. The Records page explains this.
Reference
The reports
| Card | You choose | The PDF contains |
|---|---|---|
| Statement of Applicability | Framework and Version (the draft or an approved version) | Executive summary, every control with its status, evidence count, justification and references, and a detailed analysis per control. See below. |
| Audits | The audit | Audit details, objectives, scope, criteria, clauses in scope, each finding with criterion, evidence, root cause, correction, corrective action and verification, and the conclusion |
| Assets | Risk tier (all, high, medium or low) and labels | Statistics and the asset inventory with confidentiality, integrity and availability ratings |
| Devices | Nothing | Fleet compliance per posture check, the device inventory, the devices that fail a check, and a note on method |
| Asset Reviews | The review | Scope, coordinator, each asset with its decision, and the progress |
| Access Reviews | The review | Review type, coordinator, the access rights reviewed and each decision |
| Policies | The policy, and Latest (Current Draft) or a published version | Cover with owner and review schedule, table of contents, the sections, and for a published version the change history |
| Records | The record, and a finalized version or Current working draft | Cover with category, status, assignee and version, and the content. A finalized version adds its change note. A draft carries a "not finalized" warning on the cover. |
| Process Submissions | The submission | Every row with who checked it and when, how a report was handled, and the timeline |
| Management Review | From, To and Framework | Counts and lists for each input of the management review. See below. |
| Evidence | Nothing | Status overview and every evidence record with owner and next review |
| Incidents | Nothing | Status overview and every incident with severity, status, owner, detection date and whether it was a personal data breach |
| Risks | Kind (risks or opportunities) and, for risks, the tier | Risk criteria, the register by level, each risk with initial and residual level, treatment and acceptance |
| Risk Reviews | The review | Scope, coordinator, each risk with its changes, and the decisions |
| Vendors | Risk tier | Statistics, vendors overdue for reassessment, and each vendor with inherent, residual and current rating |
| Vendor Reviews | The review | Scope, coordinator, each vendor with its rating, and the decisions |
| Organization Chart | Nothing | The chart with every placed person and the reporting lines |
Reports without a date filter, such as Incidents and Evidence, list every record, including old ones. The Devices report covers active devices only. The pickers for records and process submissions list the first 100 entries. A link from the record itself still works for older ones.
Generate Report stays off until you have made a choice. It also stays off in these cases:
- Statement of Applicability: ISO/IEC 27001 is chosen, but its Annex A is not adopted. A note offers to adopt it.
- Management Review: the From date is after the To date.
- Assets, Risks, Vendors, Devices, Evidence, Incidents: the register has no entries.
On the Records card, the button reads Generate.
Statement of Applicability
The Statement of Applicability (SoA) is required by ISO/IEC 27001. It lists every control of Annex A, or of the framework you choose. For each control, it says whether it applies, how far it is implemented, and why. An auditor reads it to see which controls you apply and which you exclude. You approve versions on the report page. The Frameworks page shows how.
Each control takes one row with four columns: the control ID, the control name, the status and the references.
- Status is the implementation status, followed by the number of evidence records linked to the control.
- A control may have no links of its own, or be assessed None by hand. If a mapped control in another framework has coverage, the status reads Partial (indirect). The row names the mapped control. It shows no evidence count.
- A control marked not applicable shows no evidence count. Its justification appears under the status.
- References lists the linked policies (with the section, where one is linked), and the assets and risks with their register codes, such as
A-003orR-020. - Controls are sorted as text, so A.8.10 comes before A.8.2.
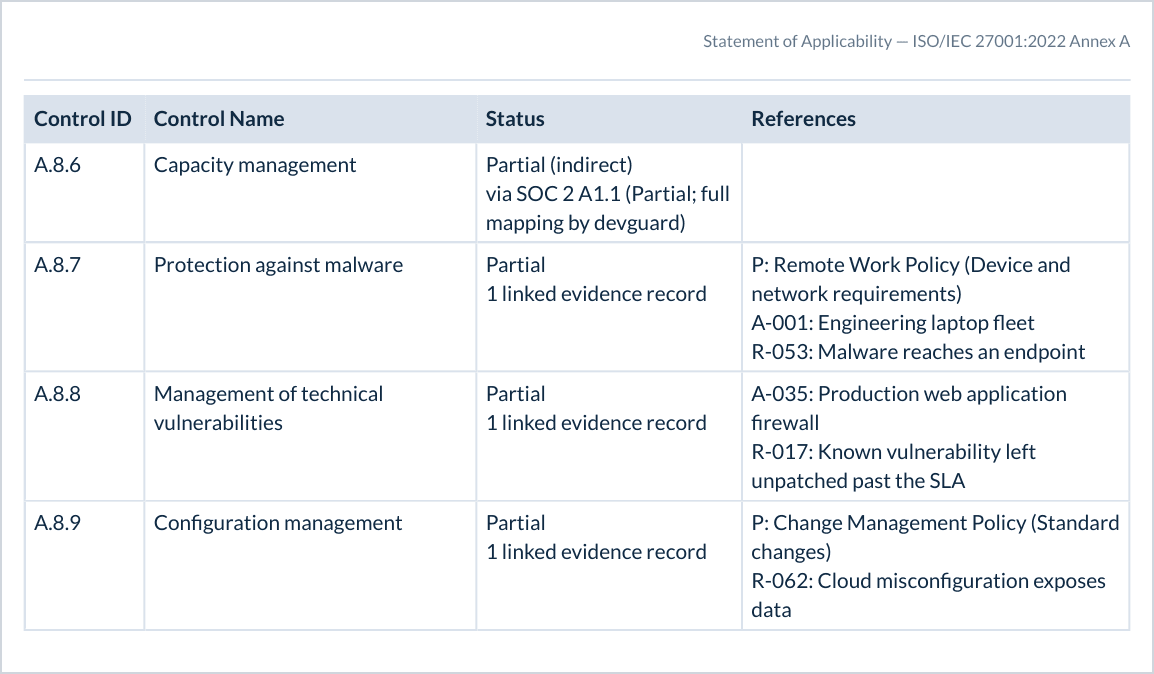
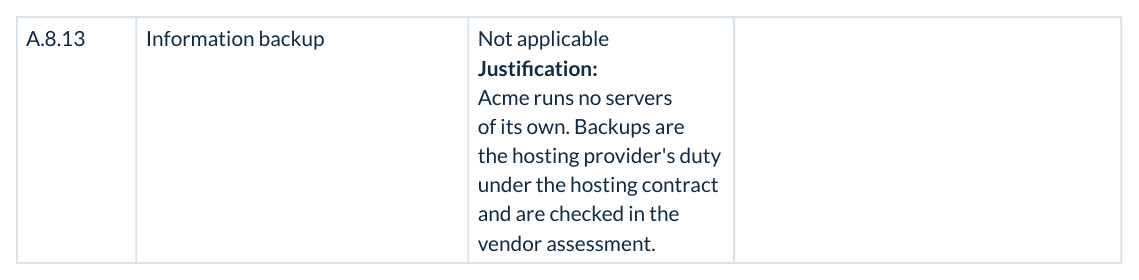
The column headings repeat on every page. A row stays on one page unless it is taller than a page.
Until you approve a version, the report is a draft. An approved version stores its number, approval date and approver, and the cover prints them. For a framework outside information security, the same report is called Applicability and exclusions, because an SoA belongs to ISO/IEC 27001.
Management Review
The report collects counts and lists from devguard for the inputs of a management review. Choose the From and To dates and the Framework whose wording the headings use (ISO 9001 or ISO/IEC 27001). When you open the card, the period is the last 12 months.
Each section of the PDF is one input of the management review. Its first line says what it shows.
| Input | What the report shows |
|---|---|
| Actions from previous reviews | Tasks on your management review process that are open now or changed in the period |
| Customer feedback and complaints | Submissions of processes made from the Customer complaint template, by status |
| Process submissions | For each process: how many are in progress, submitted and resolved |
| Change requests | Submissions of processes made from the Change request template, by status |
| Nonconformities and corrective actions | Findings raised, changed or open in the period, by type and source. How many had their effectiveness verified. |
| Monitoring and measurement | Each number field of a report process with values in the period. Archived and anonymous processes are left out. How many values met the target saved with their submission. The latest value. |
| Audit results | Audits held in the period, their audit items and their nonconformities |
| Supplier performance | Vendor approval status, finished assessments and finished vendor reviews |
| Competence | Training status from the competence matrix. Only owners, admins and auditors see the figures. |
| Risks | Counts by level, treatment and action status. Risk reviews finished in the period. |
| Opportunities | Counts by level and response |
| Incidents | Counts by severity and status. Personal data breaches and reporting stages. |
The statuses are the ones on the day you generate the PDF. Each section that shows statuses says this. A section with no data says so. If no process uses the Customer complaint or Change request template, the section names the missing template. The last section lists the inputs the report does not cover, such as changes in external and internal issues. Record those in the review checklist.
Incidents appear as counts only, never by name or content. Processes with anonymous submissions appear by name with their counts, never with what was submitted.
A management review process and each of its submissions link to this report. From a submission, the period runs from the previous review to this one. Without a previous review, and from the process page, it is the last 12 months. To keep the inputs with the minutes, download the PDF and upload it to the review submission. After the upload, the file in the submission no longer changes.
What a PDF has
- A cover with your organization's name, the report title, the date it was generated and Prepared by with your organization's name.
- A table of contents after the cover, when the report has sections.
- A header on each page with the organization and the report title. The Organization Chart has no header.
- A footer on each page with your organization, the date, your custom footer and the page number.
- Your brand colors from Branding, if your plan includes branding. The Devices, Incidents, Management Review, Process Submissions and Records reports use the default colors.
- A file name with the subject and the date, such as
ISO 27001 certification audit (stage 2) 30.10.2026.pdforincident-register-30.10.2026.pdf.
If a report fails, the preview shows The report could not be generated. The browser loads the fonts of the PDF from Google Fonts (fonts.gstatic.com). A network that blocks this address stops every report.
Permissions
Reports has no permission of its own. A report reads the same data as the pages it comes from.
| Role | Generate a report | Approve a version of the Statement of Applicability |
|---|---|---|
| Owner, admin | Yes | Only as a member of the framework's approver role |
| Member | Yes, on the data they can open | Only as a member of the approver role |
| Auditor | Yes, on the data they can open | No, even as a member of the approver role |
| Employee | No. Employees use the portal | No |
| External contact | No. External contacts cannot open the app pages | No |
| Organization token | No. Tokens work only with the API, and no API returns a report | No |
The approver role is set on the framework. See Frameworks.
Where reports appear elsewhere
- The pages listed under Start from the record instead.
- The risk overview links to the Risks report from its Risk Process card.
- Policies: employees read the latest published policy as a PDF in the portal. That PDF has no brand colors and no custom footer.
For developers
The PDF is built in the browser from the data the app shows. No API endpoint returns a report PDF. To get the same data for your own tools, use the API of each register, for example Evidence.
You can link straight to a report. The address opens the report page with the choice made and generates the PDF. For most reports, the app writes this address into the browser bar when you generate.
| Report | Address |
|---|---|
| Assets | /reports/assets/?report=high-assets |
| Vendors | /reports/vendors/?report=all-vendors |
| Risks | /reports/risks/?report=all-risks |
| Opportunities | /reports/risks/?report=opportunities |
| Evidence | /reports/evidence/?report=evidence-register |
| Incidents | /reports/incidents/?report=incident-register |
| Devices | /reports/devices/?report=device-compliance |
| Audit | /reports/audits/?report=<audit id> |
| Risk review | /reports/risk-reviews/?report=<review id> |
| Asset review | /reports/asset-reviews/?report=<review id> |
| Access review | /reports/entitlement-reviews/?report=<review id> |
| Vendor review | /reports/vendor-reviews/?report=<review id> |
| Statement of Applicability | /reports/soa/?report=<framework id> |
| Process submission | /reports/processes/?report=<submission id> |
| Record | /reports/records/?report=<record id> |
| Policy | /reports/policies/?report=<slug>&version=1.0.0 |
| Management Review | /reports/management-review/?from=2026-01-01&to=2026-06-30&framework=iso-27001 |
| Organization Chart | /reports/organization-chart/ (no parameters) |
- For assets, vendors and risks, the tier is
all,high,mediumorlow. An unknown tier is ignored: the report is generated for all records, and the address changes toall-…. - A policy
versionis the published version number, such as1.0.0. Without it, the policy opens at Latest (Current Draft). - A record link has no
versionparameter and prints the working draft. See the warning under Start from the record instead. frameworktakesiso-27001oriso-9001. Dates use the formYYYY-MM-DD. The Management Review address only fills in the choices. Choose Generate Report yourself. The Organization Chart address opens the page. Choose Generate Report there too.- An unknown id shows an error message and resets the page.
The AI assistant, and through it the MCP server, can list and read approved versions of the Statement of Applicability. The tools are listSoaVersions and getSoaVersion. The Frameworks page describes them.
How is this guide?