Audit Log
See who changed what in your organization and when, find one change, and give the record to an auditor.
The audit log is devguard's record of changes: who did what, to which item, and when. devguard writes an entry when someone changes something in the app. The app has no way to edit or delete a single entry. Entries leave the log only when they are older than your plan keeps them.
What this gives you: your auditor sees every change with the person and the time, without a spreadsheet.
The audit log is not an audit. To plan an internal or external audit and record its findings, see Audits.
The tasks below follow the order of the work:
Scripts and integrations: see API below.
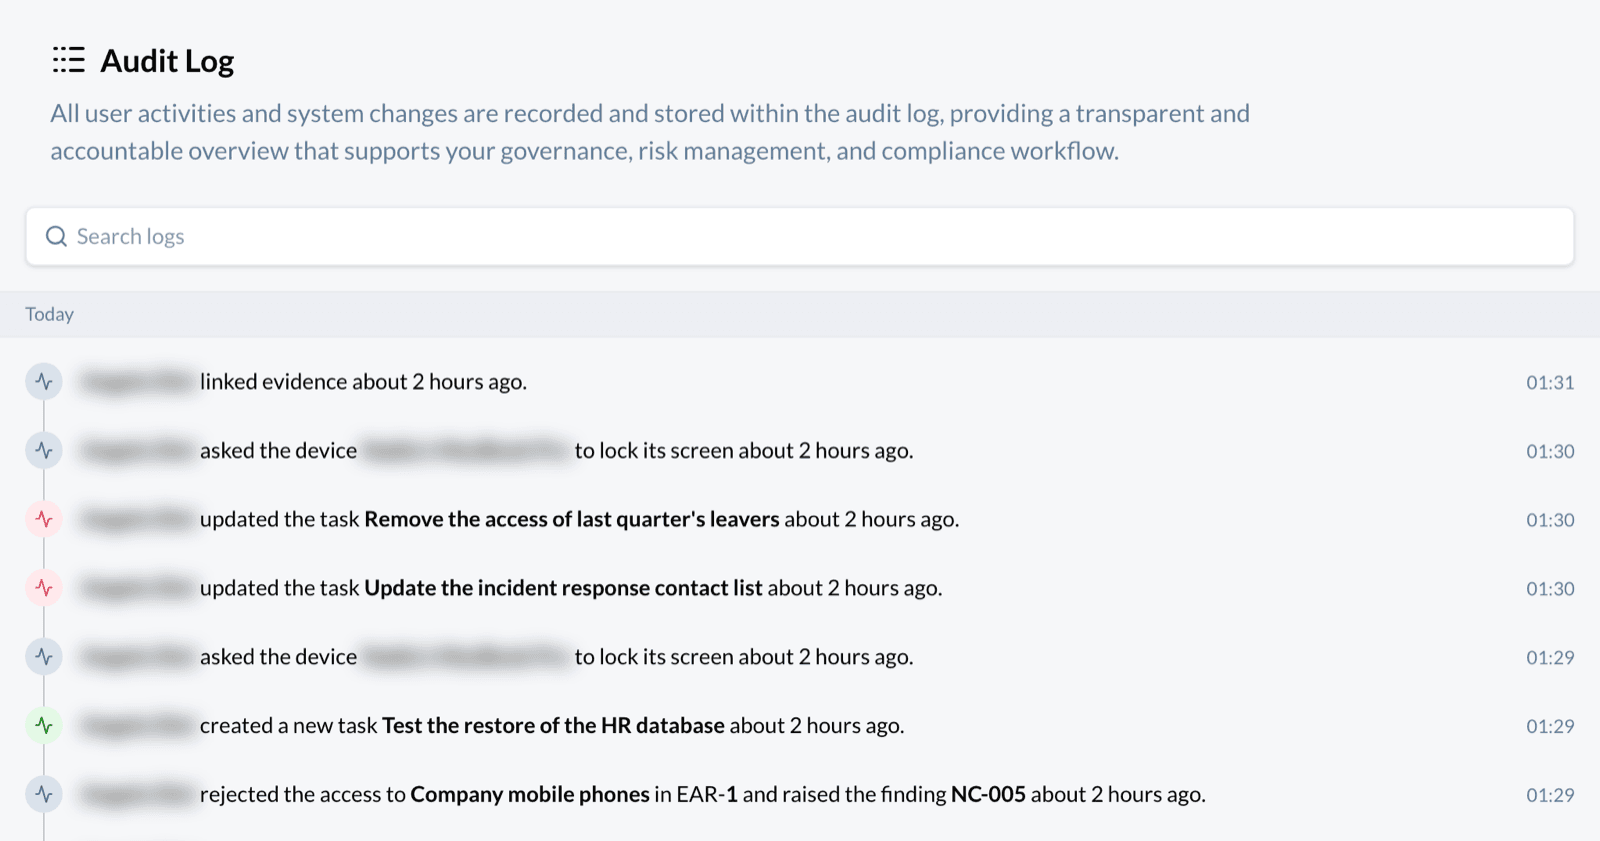
Read the log
- Open Audit Log in the sidebar. It is in the Monitor group.
- Read the entries from the top. The newest entry is first. The entries are grouped by day: Today, Yesterday, then the date.
- Read each entry as one sentence: the person, what they did, the item, and how long ago. The time of day is on the right.
- To see the exact date and time, point at the "ago" part of the sentence.
- To see older entries, use the page numbers at the bottom. Each page holds 100 entries.
The icon at the start of an entry shows the kind of change: green for something added, red for something deleted, light red for something updated, and gray for other actions, such as a link or an approval. Account changes, such as a member removed, are always gray.
Give the log to an auditor
The audit log can support ISO 27001 clause 7.5.3 (control of documented information) and control A.5.33 (protection of records). Your auditor decides whether it is enough evidence. The entries about members, roles and tokens also support A.5.15 to A.5.18 (access control, identities, authentication and access rights).
Choose how the auditor gets the log
The Audit Log page has no export button. Use one of these three ways:
| Way | What the auditor gets | Limits |
|---|---|---|
| An Auditor seat | Invite the auditor in People with the Auditor role. They read the log and every History tab in devguard, and can change nothing. | Shows what your plan still keeps. |
| The organization export | An owner or admin opens Settings. On the Export all data card, they choose Start export, then Download when devguard notifies them. The ZIP file holds data/audit_logs.json and data/audit_logs.csv with every entry devguard still keeps. | Only changes in the app. Account changes (members, roles, tokens, organization settings, connected apps) are not in it. |
| The API | A file you build with the script below. It holds both kinds of entries. | Only the 5,000 newest entries. |
A new export replaces the previous one, so keep each ZIP file you download. The export writes its own entries into the log: who asked for the export, and who asked for the download link.
Record how you made the file
The auditor needs to know where a file comes from. For each file you hand over:
- Write down who made it, when, and how: the export, or the API call with its parameters.
- Write down the date of the first and the last entry in the file. If the API reported
authLogUnavailable, write that down too. - Upload it to an evidence record, for example "Audit log export, Q3". devguard shows the file's SHA-256 checksum and keeps older files under Previous versions.
- Give the auditor the full checksum with the file. devguard shows its first 12 characters; point at them to see the full value. For an API file, you can also use the value from the script's
shasumline. With the checksum, the auditor can check that the file has not changed since you uploaded it. The checksum does not show that the file is complete.
Check the period the log covers
The app has no way to edit or delete a single entry. Entries do leave the log in two cases:
- They pass the retention period of your plan, see the table below.
- The organization moves to the Free plan. Entries older than 30 days disappear at once. After a failed payment they are only hidden: they come back once the payment goes through, unless the subscription ends first.
| Plan | Entries kept for |
|---|---|
| Free | 30 days |
| Business | 3 years (1,095 days) |
A busy organization can pass 5,000 entries in a few weeks. Save both files at least once a month. Save the API file sooner if close to 5,000 new entries have built up since the last one. The oldest entry of each new API file must be older than the newest entry of the previous file. Then the files together cover the whole audit period:
- The ZIP export has no 5,000 limit, but holds only the changes in the app.
- The API file holds the account changes too, but only the 5,000 newest entries.
Record who reviewed the log
The auditor will also ask who reviews the log, and where that review is recorded. One way in devguard:
- Create an evidence record "Audit log review" with an owner, an approver and a review schedule, for example monthly.
- Choose an approver who is not the owner and did not make the changes the review checks. In a small team, a second person can do this.
- Each month, the owner attaches the new file. In a comment on the record, the owner writes what they checked and what they found. If they found a problem, they add a task on the record's Tasks tab to follow it up.
- The approver approves the record. devguard records who approved it and when.
Find one change
- Type a word in Search logs. The list updates after a short pause.
- Search for a word of the entry, such as "deleted", "finding" or "token". Search also finds the names of the items, such as the title of a task or an audit finding.
- To share the result, copy the address from the browser. The search word is part of it.
- To clear the search, choose the cross next to the field.
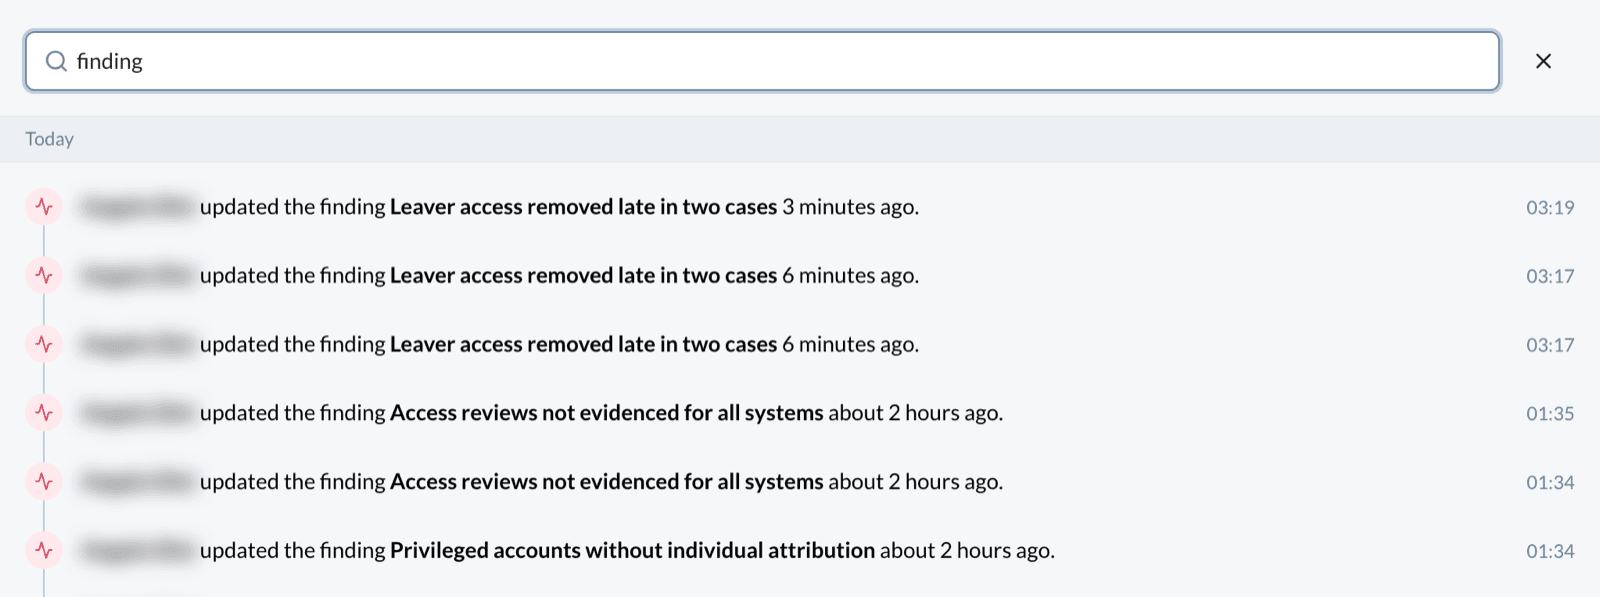
Watch out: search does not find a person's name or a date. To see everything that happened to one item, open it and use its History tab.
See the history of one record or one person
Most records have a History tab. It shows the same log, but only the entries for that record. Risks, assets, controls, evidence, vendors, incidents, audits, tasks, records, processes, trainings, devices and the items in Collections all have one.
- Open the record, for example an evidence record.
- Choose the History tab. You can search it in the same way.
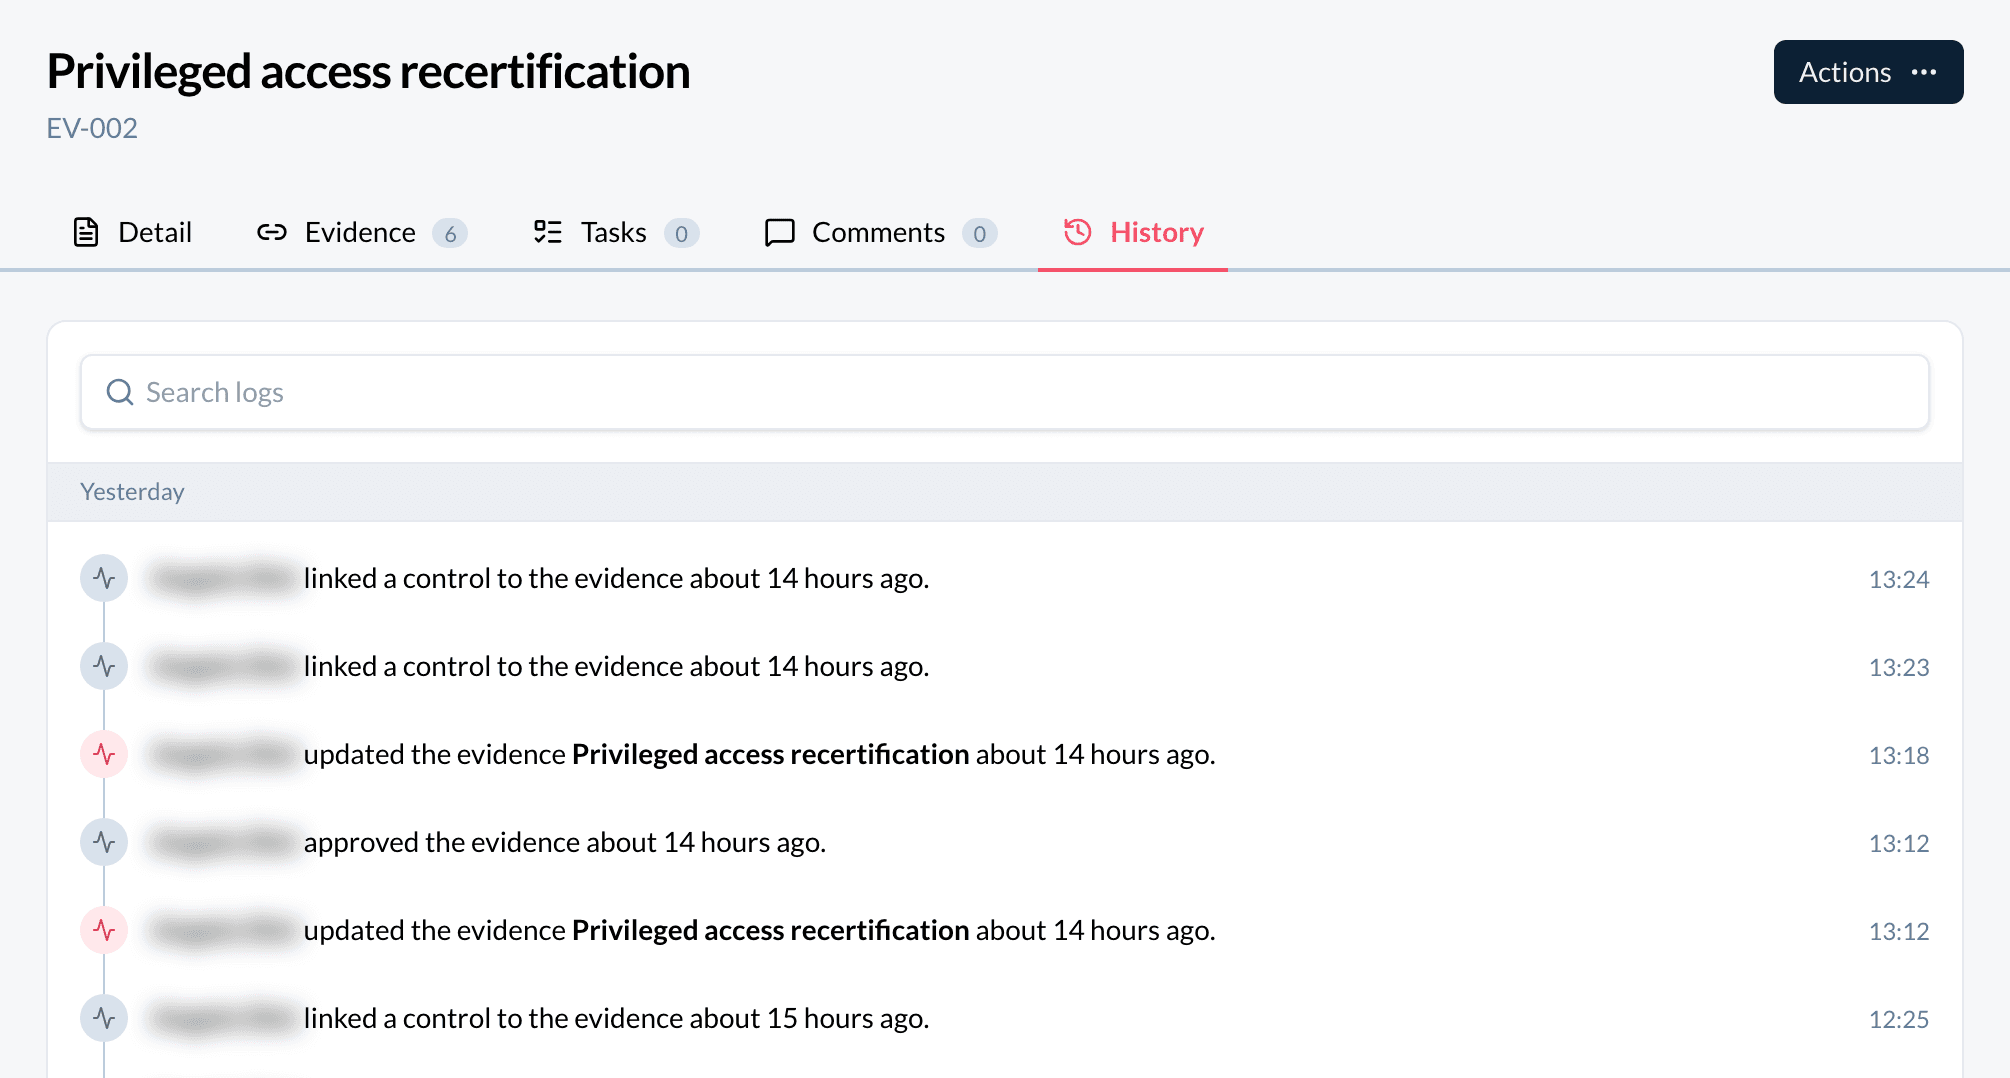
To see what one person did, open People, choose the person, then their History tab. The dashboard also has a History tab with the latest entries.
How devguard keeps the log
devguard writes an entry at the moment of the change. The app only adds entries. Nothing in the app edits or removes an entry after it is written.
The log has two sources, shown as one list:
- Changes in the app, for example a risk created, a control linked, evidence approved or a file uploaded.
- Account changes from the sign-in service: a member invited, removed, deactivated or given a new role, a token created or revoked, a change to the organization settings, and an app connected or disconnected.
If the sign-in service cannot be reached, the page shows the warning Part of this log could not be loaded. All changes in the app are still shown. Load the page again later to see the account changes.
Reference
What an entry contains
| On the page | In the API | Meaning |
|---|---|---|
| Person | userId | The user who made the change. When the user was removed from the organization, or devguard made the change itself, the page shows devguard Bot. |
| Sentence | logMessage | What happened, as a template with placeholders such as {username} and {data.name}. |
| Item in bold | logData | The data of the changed item at the time of the change. The sentence takes the item name from here. |
| Time | createdAt | When the change was saved. |
| Icon | logType | The kind of change, for example risk.create or organization.members. |
Permissions
| Role | Read the log and History tabs | Change or delete entries |
|---|---|---|
| Owner, admin | Yes | No |
| Member | Yes | No |
| Auditor | Yes | No |
| Organization token | Yes, over the API | No |
| Employee (portal only) | No | No |
Limits
- 100 entries per page.
- You can page through the 5,000 newest entries. To reach older ones, narrow the list with a search.
- Entries are kept for 30 days on the Free plan and 3 years on the Business plan.
Where the log appears
- The Audit Log page.
- The History tab of most records, and of each person in People.
- The History tab on the dashboard.
- The audit log of a mandate, for partners who manage several organizations.
API
- Base URL:
https://app.devguard.ch/api. - Authentication: an API token or an organization token, sent as
Authorization: Bearer <token>. A token with limited scopes needsreadorread:audit-log. - Scope: read only. There is no call to change or delete an entry.
| Call | Endpoint | Organization id |
|---|---|---|
| List entries | GET /audit-log/ | query, required |
| Parameter | Meaning |
|---|---|
organizationId | Your organization id. Required. |
page | Page number, from 1. |
limit | Entries per page, 5 to 100. Default 100. |
filterByName | The same search as the page. For account changes, it matches the sentence only. |
userId | Only the entries of one user. This is the user id, not the member id. |
entityId | Only the entries of one record, by its id. Account changes are not included. |
The answer is { "items": [...], "total": 240, "page": 1, "limit": 100, "authLogUnavailable": false }. Each item has the fields from the table above. total stops at 5,000. When authLogUnavailable is true, the account changes from the sign-in service are missing from this answer.
This script saves every entry the API can reach to one file, one entry per line, and prints the file's SHA-256 checksum. DG_TOKEN is your token and DG_ORG is your organization id. It needs curl and jq:
API=https://app.devguard.ch/api/audit-log/
OUT=audit-log.jsonl
TMP=$(mktemp)
page=1
while :; do
  body=$(curl -sS -G "$API" \
    -H "Authorization: Bearer $DG_TOKEN" \
    --data-urlencode "organizationId=$DG_ORG" \
    --data-urlencode "limit=100" \
    --data-urlencode "page=$page")
  if ! echo "$body" | jq -e .items >/dev/null; then
    [ "$page" -gt 50 ] && break
    echo "page $page failed: $body" >&2; exit 1
  fi
  if echo "$body" | jq -e .authLogUnavailable >/dev/null; then
    echo "page $page: account changes missing" >&2; exit 1
  fi
  n=$(echo "$body" | jq '.items | length')
  [ "$n" -gt 0 ] || break
  echo "$body" | jq -c '.items[]' >> "$TMP"
  page=$((page + 1))
done
jq -c -s 'unique_by(.id) | sort_by(.createdAt) | reverse | .[]' \
  "$TMP" > "$OUT"
shasum -a 256 "$OUT"
The script stops with an error, and prints no checksum, when a page fails or when a page reports that the account changes are missing (authLogUnavailable). Run it again later. It stops after page 50, the 5,000-entry limit. New entries that arrive during the run shift the pages, so the script removes duplicates before it writes the file. Run it at a quiet time.
createdAtis in UTC, as ISO 8601 (for example2026-10-30T13:12:04.512Z). The page shows local time.- The API returns the user id, not the name. To find who an id belongs to, find the same entry on the Audit Log page (same time and sentence). The page shows the name. The devguard API has no call that lists members' names.
logMessageis a template. Replace{username}with the person,{date}with the time, and each{data.x}with the fieldxfromlogData.
Errors: 400 for a page after the 5,000 newest entries, a limit outside 5 to 100 or a missing organizationId. 401 without a valid token. 403 when the token has no access to the organization, lacks the scope, or belongs to a deactivated member or an employee.
How is this guide?