People
Invite your colleagues, decide what each person may do in devguard, and end their access cleanly when they leave.
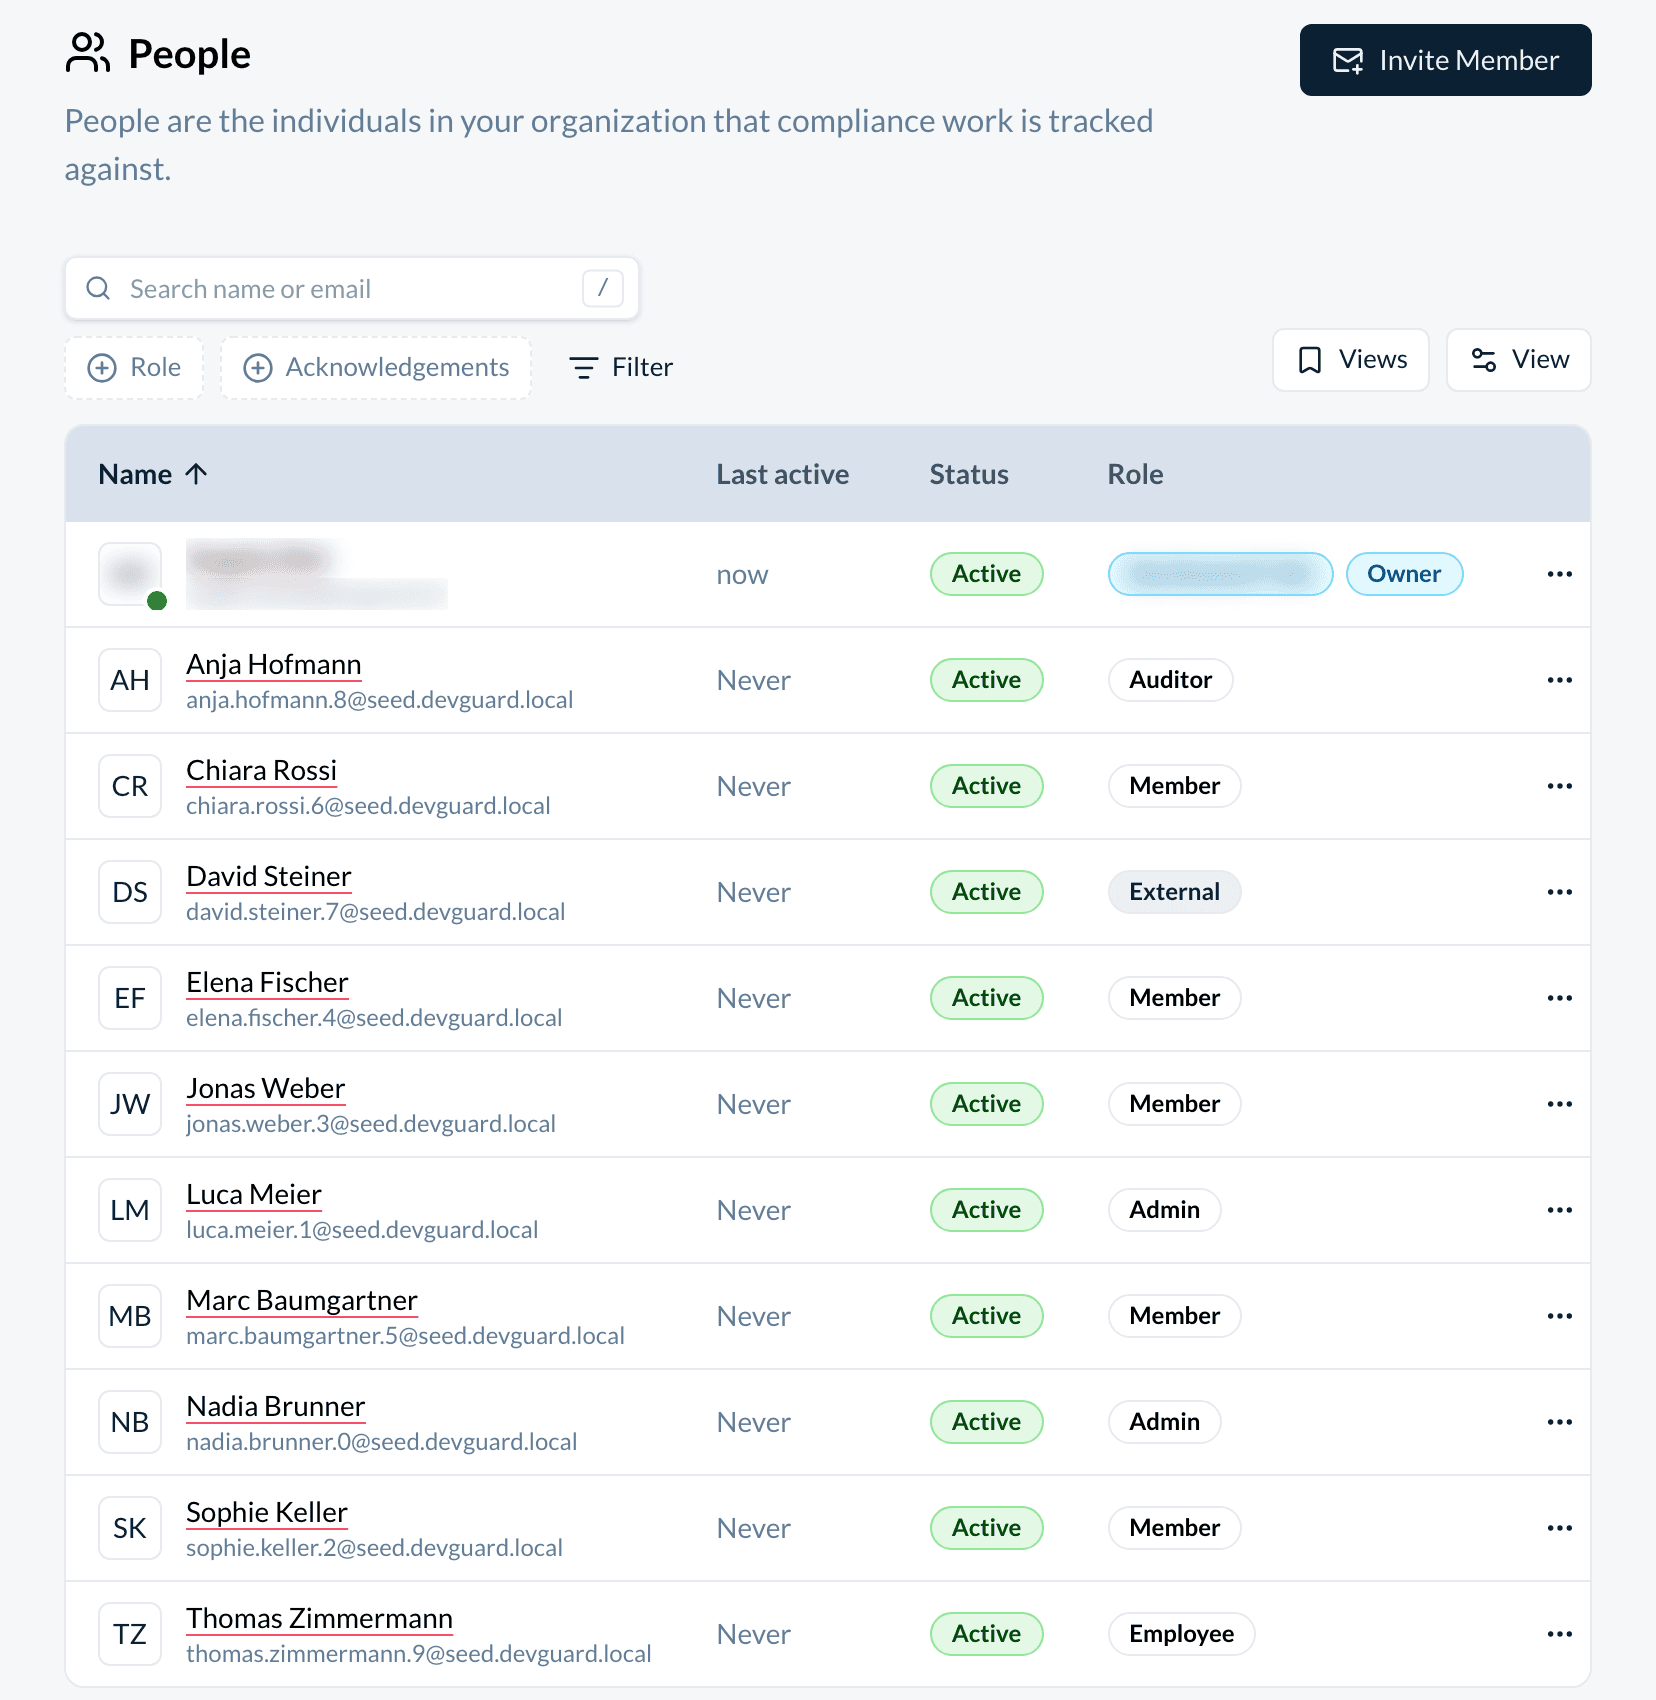
People lists everyone in your organization: colleagues who use devguard, employees who use only the portal, and external contacts. Each person has one app role that decides what they can open and change. Owners and admins invite people, change their role and end their access.
The tasks below follow the order of the work:
- Invite a person
- Change a person's app role
- Add a person to a business role
- See what a person is responsible for
- Find people
- Onboard or offboard a person
- Deactivate or delete a person
People has two sub-pages: Roles for business roles, and the Organization Chart. Scripts and integrations: see API below.
Two kinds of role
devguard uses the word "role" for two different things. Keep them apart:
- An app role decides what a person can do in devguard: Owner, Admin, Member, Auditor, Employee or External. Each person has exactly one. You set it on this page.
- A business role is a job in your company, such as "Head of IT" or "Data Protection Officer". Risks, assets, evidence and other records are owned by business roles, not by people. A person can be in many business roles, or in none. A business role gives no access in devguard. You manage business roles under Roles.
For example, Luca Meier has the app role Admin, so he can change records. He is also in three business roles, so he owns the risks and assets of those roles. If Luca leaves, you put someone else into those business roles, and the records keep their owner.
Invite a person
You need the app role Owner or Admin.
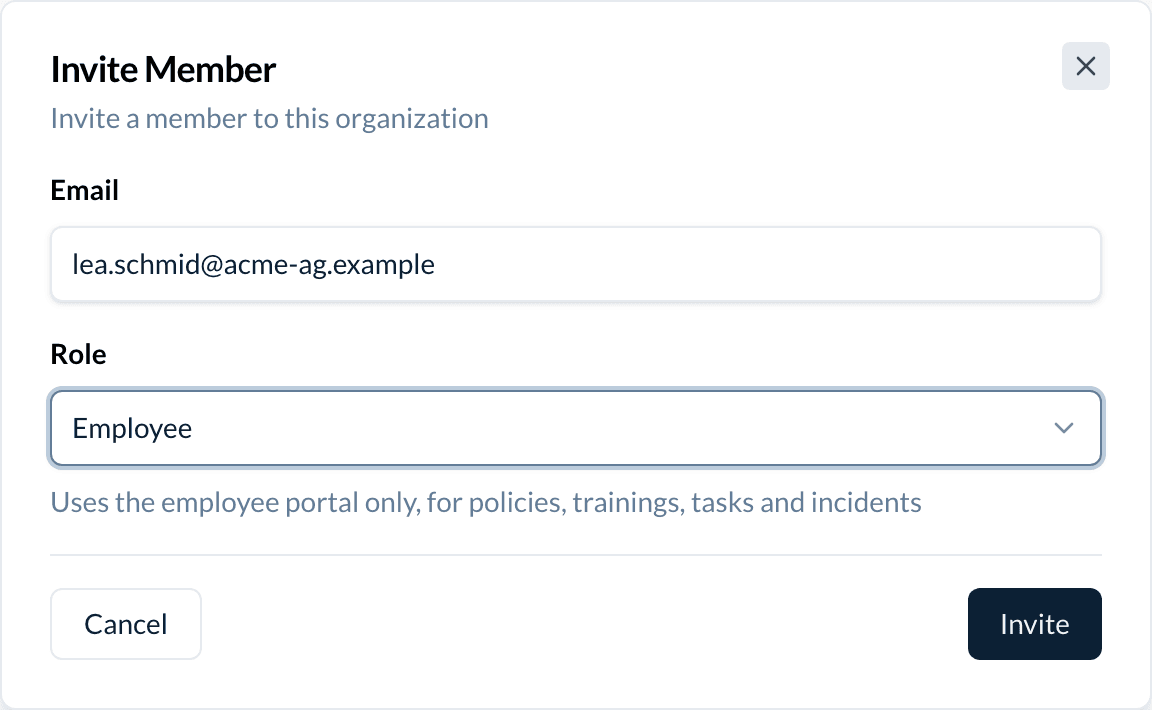
- Open People and choose Invite Member.
- Enter the person's Email.
- Choose the Role. The text under the field says what the role can do. See App roles below.
- Choose Invite. devguard sends the person an email with a link.
The person opens the link, signs in and chooses Accept. An Employee then works in the employee portal. It shows only the work that concerns them, such as policies to accept, trainings, tasks, evidence and incident reports. Owners and admins choose its sections in the portal settings.
The invitation appears in the list with the status Pending. The link works for two days. After that, the status is Expired. To send a new link, open the row's … menu, delete the invitation and invite the person again.
Watch out: a pending invitation uses a seat on your plan until it is accepted, deleted or expired. The Free plan has three seats. External contacts use no seat.
Change a person's app role
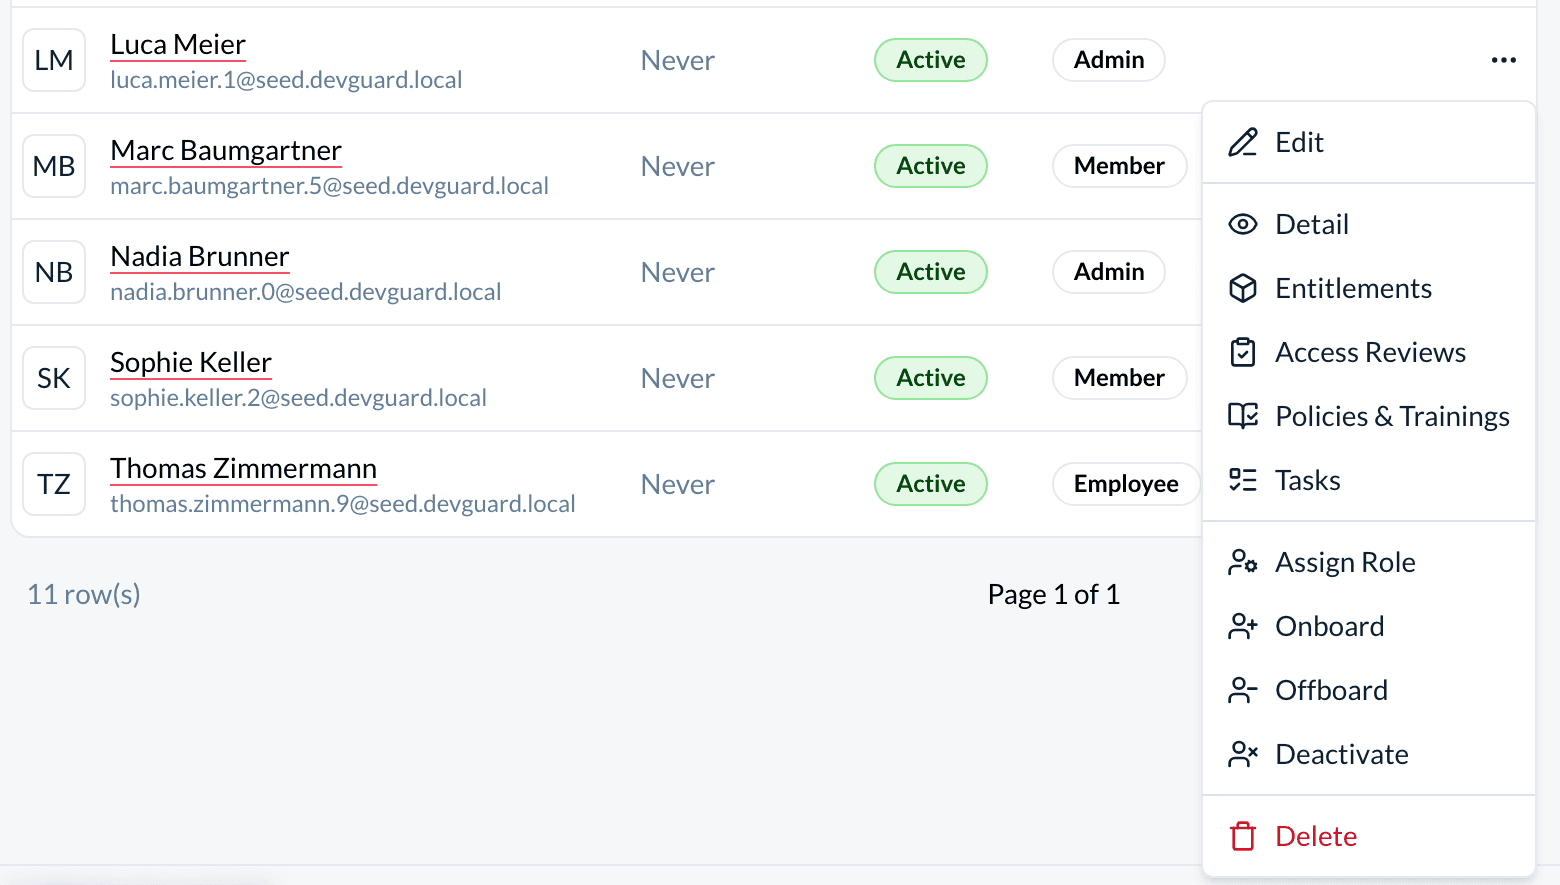
- In the list, open the … menu at the end of the person's row and choose Edit.
- Choose the new Role and choose Save.
You cannot change the owner's role here. To make someone else the owner, the owner transfers the ownership in the organization settings. If you change an external contact to any other role, the person starts to use a seat.
Add a person to a business role
- Open the … menu on the person's row and choose Assign Role. On the person's page, you can also use Assign Role in the Member Details panel.
- Search for the business role and choose it.
The person is now responsible for everything the business role owns, together with the other members of the role. The business role must exist first; see Roles. A deactivated person cannot be added to a business role.
See what a person is responsible for
Choose a name in the list to open the person's page. The header shows the app role, the join date and, for owners and admins, when the person was last active.
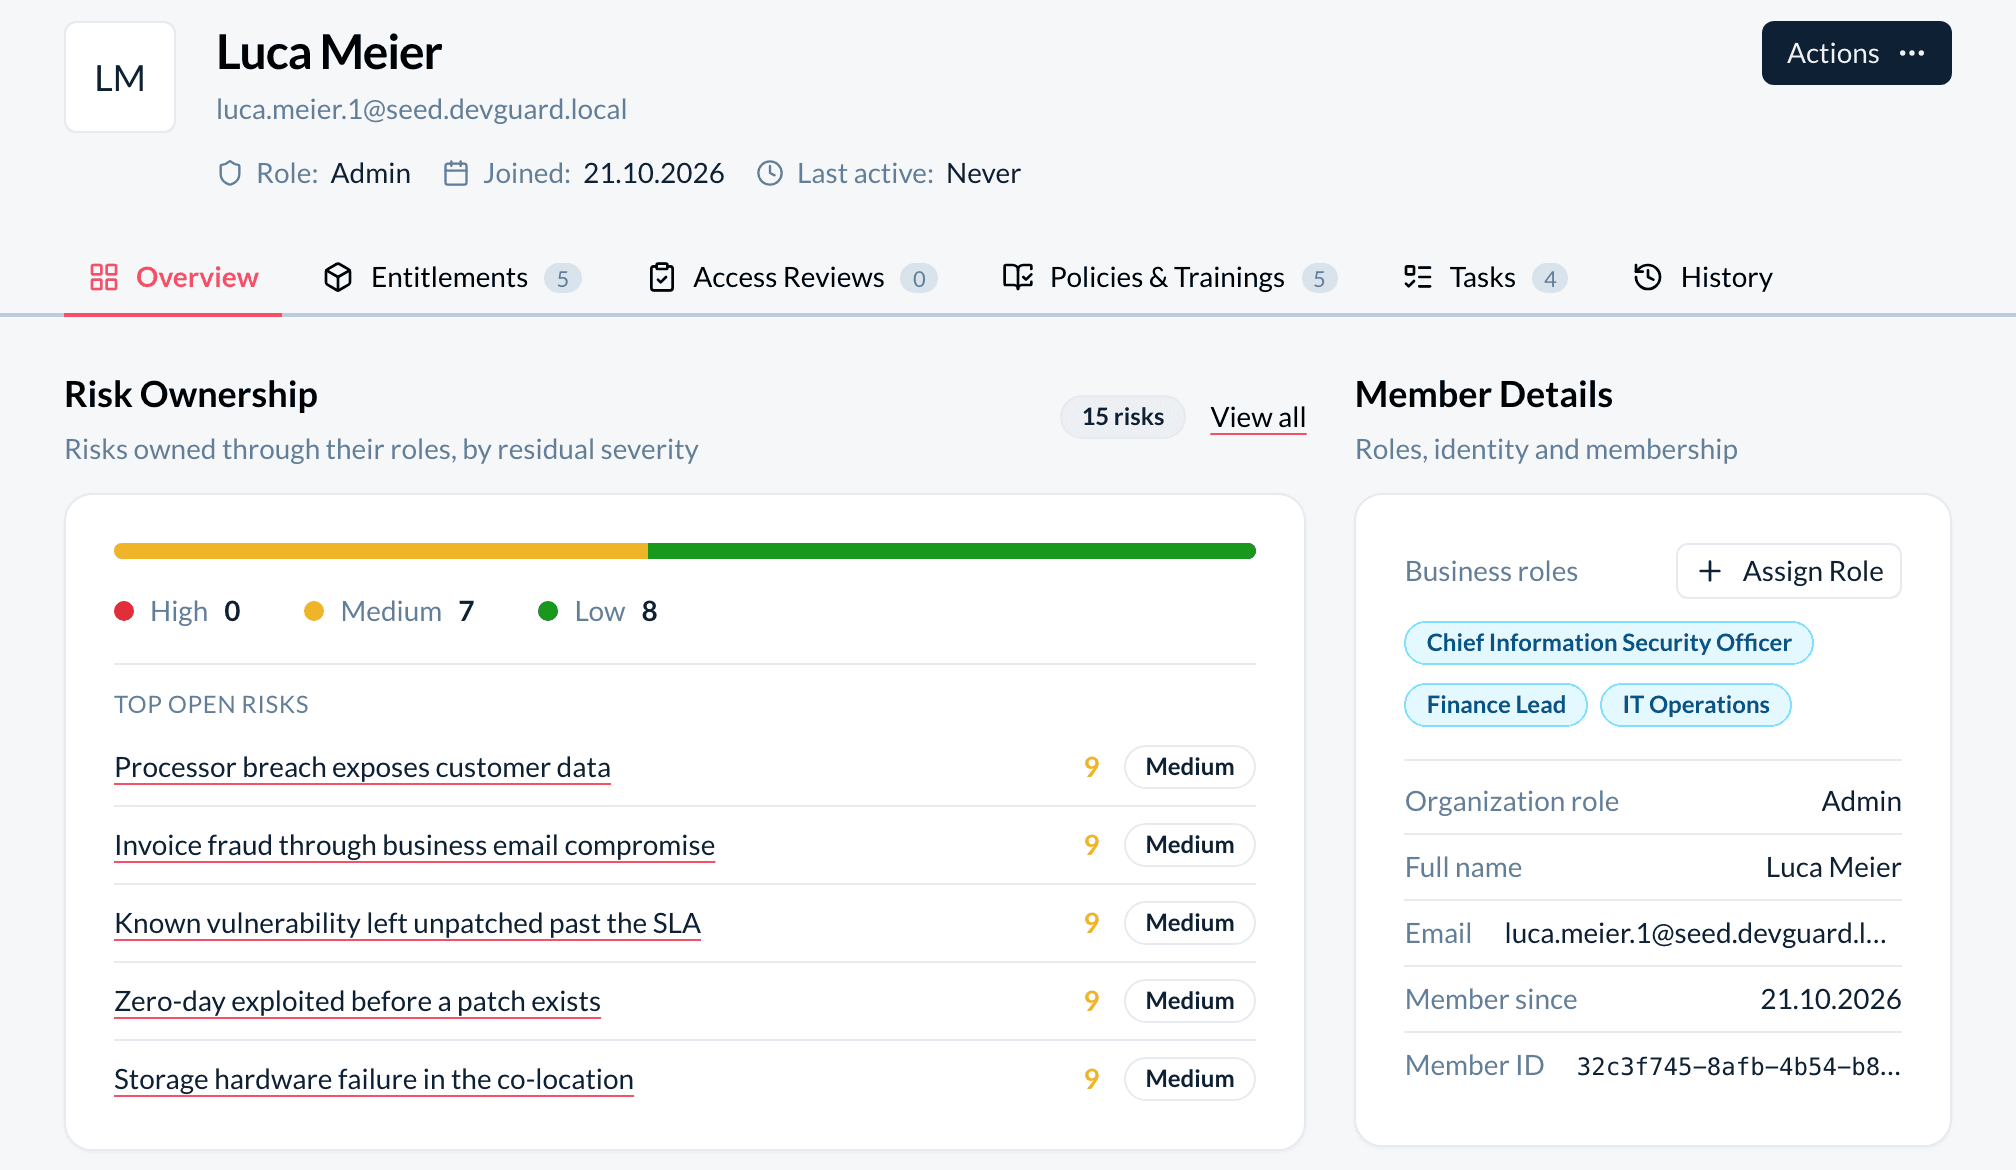
The tabs show:
- Overview: the risks and assets the person owns through their business roles, their recent activity, and the Member Details (business roles, app role, email, member since, member id).
- Entitlements: the systems and other assets outside devguard that the person can access through their business roles, and which role gives each access. This is access recorded in your asset register, not access to devguard.
- Access Reviews: the access reviews that include this person, directly or through a business role.
- Policies & Trainings: the policies to acknowledge and the trainings to complete, with their status.
- Tasks: the tasks the person is responsible for. Add task on this tab assigns a new task to this person.
- History: everything the person did in devguard, from the audit log.
Find people
- Search name or email finds a person by name or email.
- Role shows only the app roles you choose. Owners and admins shows everyone who can manage the organization. Check this list before you transfer ownership or review admin access.
- Acknowledgements shows the people with Overdue policies or Overdue trainings.
- Filter, then Status, then Inactive shows only deactivated people. The normal list hides them.
Onboard or offboard a person
When a person joins or leaves, check which systems they can access. Onboard and Offboard start an access review for this person.
- Open the … menu on the person's row, or Actions on the person's page.
- Choose Onboard or Offboard. The access review form opens with the type and the person filled in.
- Complete the form and create the review.
Deactivate or delete a person
Deactivate blocks a person's access to this organization. The account, the history and the business roles stay. Use it when a person leaves but their records must stay traceable.
- Open the … menu on the person's row, or Actions on the person's page.
- Choose Deactivate. The status changes to Inactive, and the row leaves the normal list.
When the person opens devguard, a message tells them that their access was deactivated. They keep their access to other organizations. The person stays in their business roles, but does not count as a member while deactivated. To give the access back, filter for Inactive people and choose Reactivate.
Delete takes the person out of the organization. Choose Delete in the same menu and confirm. On your own row, the menu shows Remove instead: it explains that you leave the organization from your account settings. The owner cannot be deactivated or deleted.
Watch out: for people who leave, prefer Deactivate to Delete. A deactivated person stays visible in records, reviews and the audit log. An auditor checks these.
Reference
List columns
| Column | Shows |
|---|---|
| Name | The name and email. For an invitation, only the email. Owners and admins also see a green dot when the person is online. |
| Last active | How long ago the person was last active, or Never. Only owners and admins see this column. |
| Status | Active, Inactive (deactivated), Pending (open invitation) or Expired (invitation older than two days). |
| Role | The app role. A person who comes from your compliance provider also shows the provider's name. |
App roles
| App role | What the person can do |
|---|---|
| Owner | Everything an admin can do. Also transfers ownership and deletes the organization. |
| Admin | Manages people, settings, billing and every register. |
| Member | Reads every register and takes part in comments. Cannot change records. |
| Auditor | Reads everything a member can read. Changes nothing, not even a comment. For a certification auditor or an internal audit. |
| Employee | Uses only the employee portal, for example for policies, trainings, tasks and incident reports. Never sees the app. |
| External | No access to the app or the portal. A contact you can put into a business role or an access review. Uses no seat. |
Permissions on this page
| Action | Owner, admin | Member, auditor | Employee, external |
|---|---|---|---|
| See the list and a person's page | Yes | Yes | No |
| See online status and last active | Yes | No | No |
| See pending invitations | Yes | No | No |
| Invite, edit, deactivate, delete | Yes | No | No |
| Assign a business role, onboard, offboard | Yes | No | No |
Seats
Every person uses a seat, except external contacts and the people of your compliance provider. Pending invitations use a seat too. The Free plan has three seats; the Business plan has no limit. A banner above the list shows the seats used when you get close to the limit. At the limit, Invite Member opens the upgrade dialog instead.
People in a mandate
In a mandate, People lists only the mandate's own people, with no roles and no organization chart. A person's page has two tabs: Overview and Access. Access lists the mandate's clients and shows which ones the person can open. Owners and admins open every client. Members and auditors open only the clients that an owner or admin of the mandate turns on for them. A member or auditor sees only their own Access tab, which lists just the clients granted to them. A deactivated person keeps their grants, shown read-only, and reaches those clients again once reactivated.
In a client of a mandate, the mandate's people appear with the mandate's name next to their role. Only the people with access to this client appear. The client cannot edit or delete them.
API
The public API has no calls for people or invitations. Invite, change, deactivate and delete people in the app. The business roles and the organization chart have API calls.
When an API call asks for member ids, for example to put people into a business role, use the person's member id. It is the last part of the address of the person's page, /people/detail/<member id>/, and it also shows as Member ID under Member Details. A member id is not the same as the person's user id.
How is this guide?
Mandates
Run compliance for several client organizations from one place, see which client needs you first, and show each client your brand instead of devguard's.
Organization Chart
Draw who reports to whom, with people and roles, so you can show an auditor a current organization chart that follows your People list.