Risks
Keep a risk register an auditor can follow. Rate each risk against your own criteria, decide its treatment, have the owner accept what remains, and review it on a schedule.
devguard rates your risks against criteria that you define. You can start from ready-made catalogs for ISO, NIS2, and DORA. The risk owner approves the risk that remains, and each review leaves a record. A rejected risk in a review becomes an audit finding.
The five tasks, in the order you do them:
Developers and integrators: the reference at the end of this page lists every field, permission, limit, and endpoint, with worked API examples.
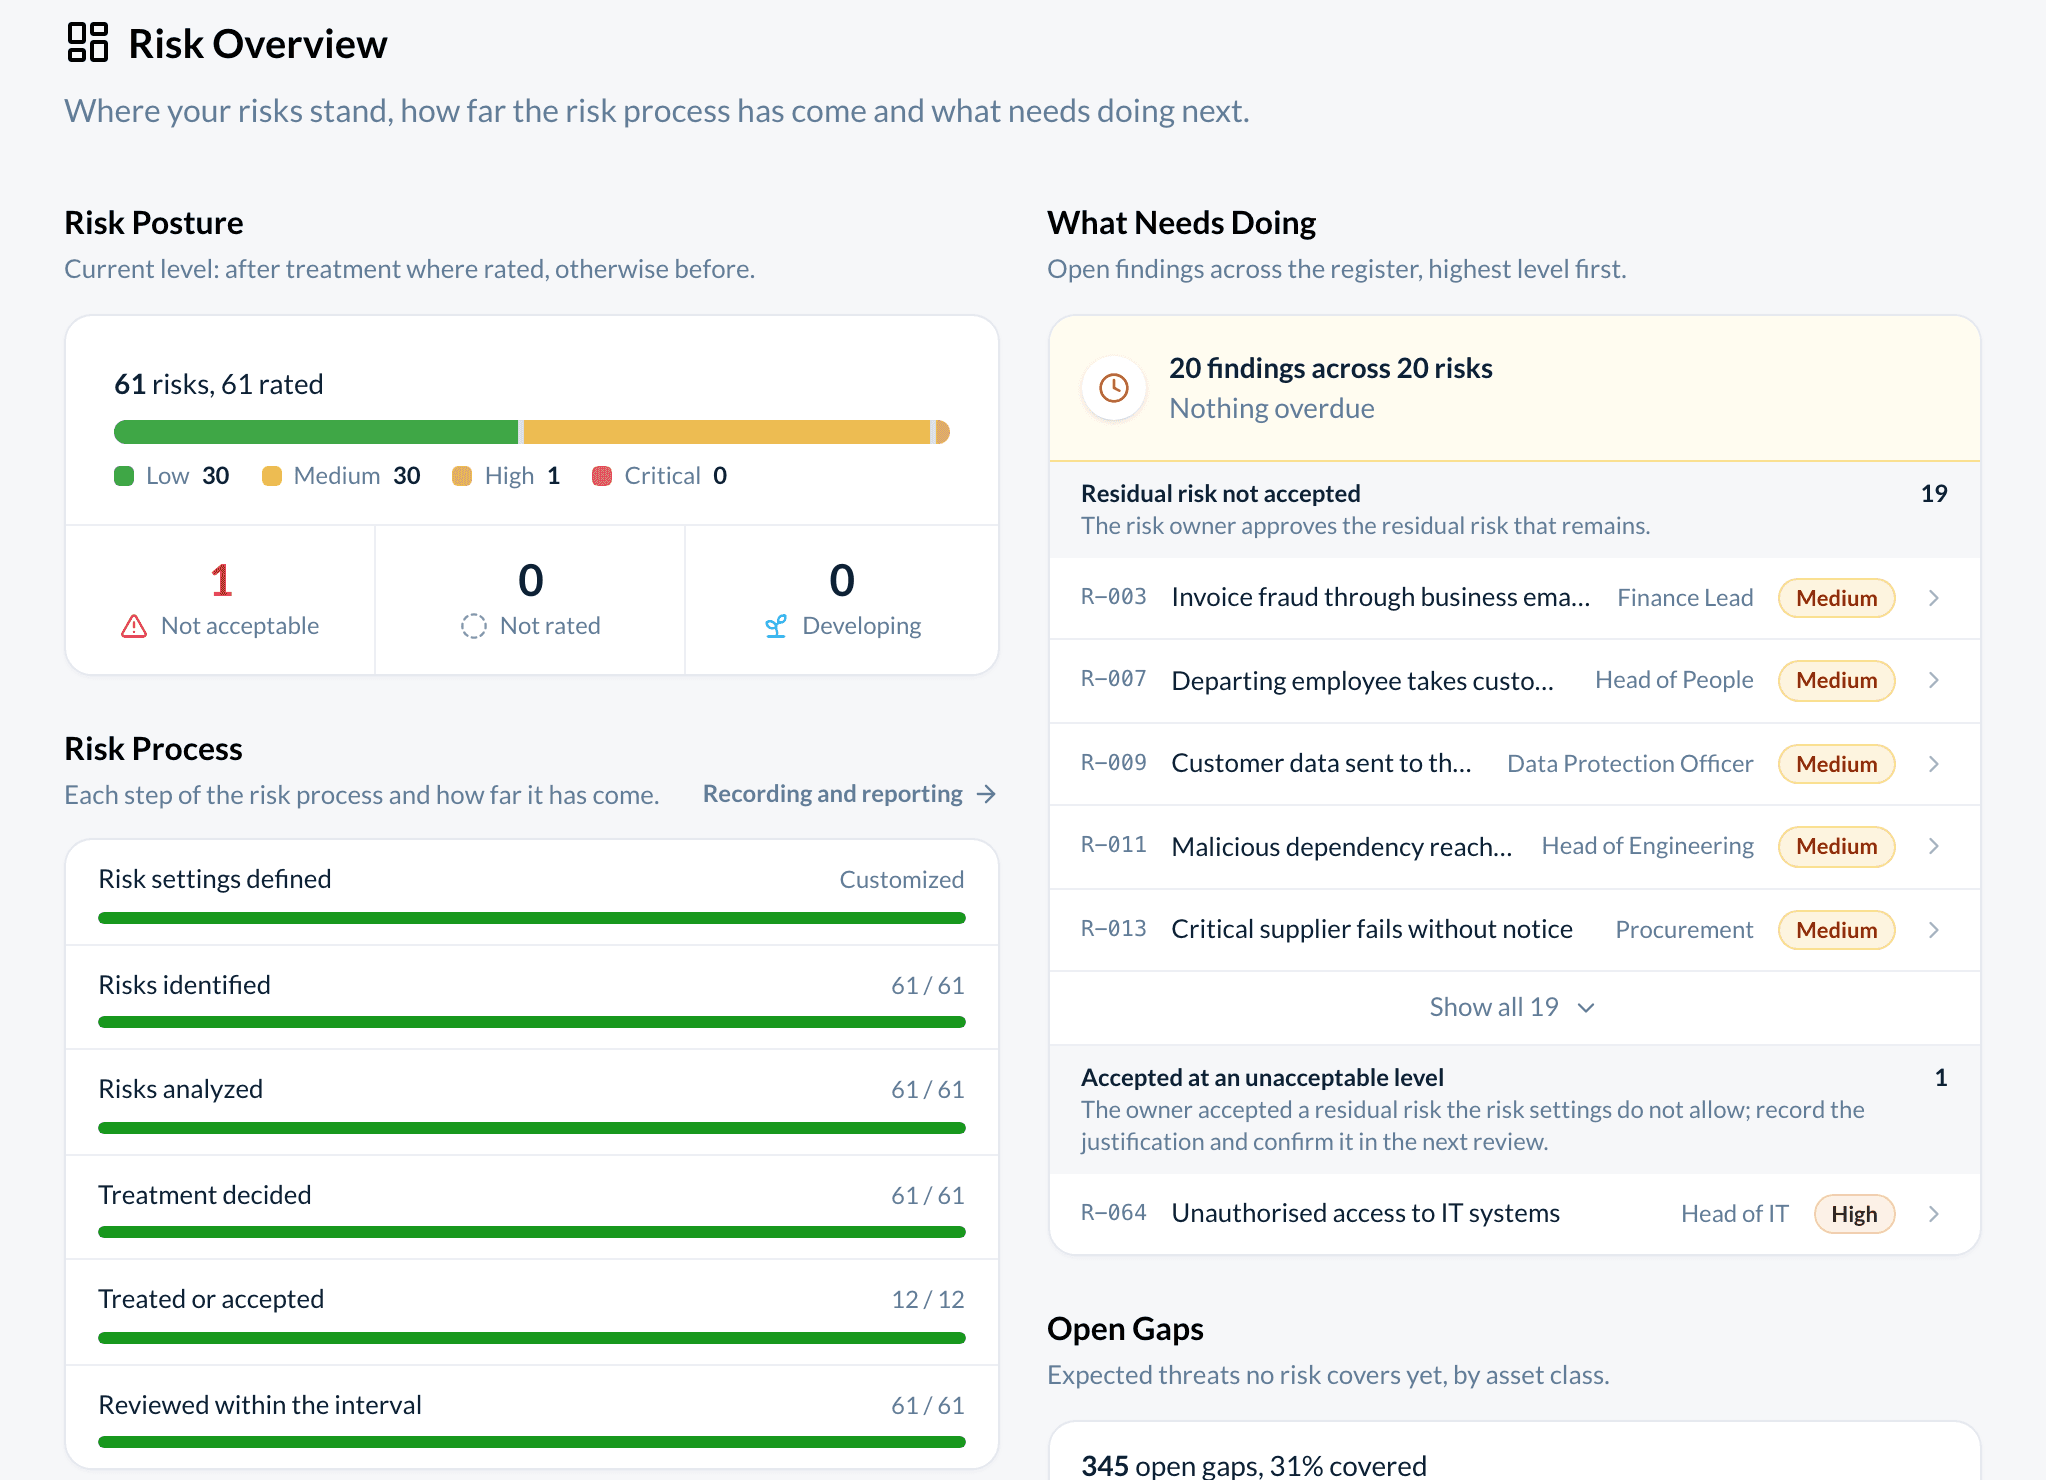
Open Risks → Overview to see where you stand. It shows the current level of every risk, the progress of each step of the risk process, and the open findings. The overview in the reference says what clears each finding.
How a risk is rated
Two ideas explain the whole feature.
A rating is a position on your scale, and the matrix gives the level. You rate probability and impact by picking one step of each scale, for example Likely and Major. That pair points to one cell of your risk matrix. The cell gives the risk its level, for example High. The level decides whether the risk is acceptable and what response it needs.
When you hover over a rating, the app also shows a score: the probability step times the impact step. The score never decides the level. The risk report prints both, for example "15 (High)".
Every risk is rated twice. The initial rating shows the risk before you do anything about it. The residual rating shows the risk after the treatment is in place. The residual rating cannot be higher than the initial one. The difference between the two shows what your treatment achieves.
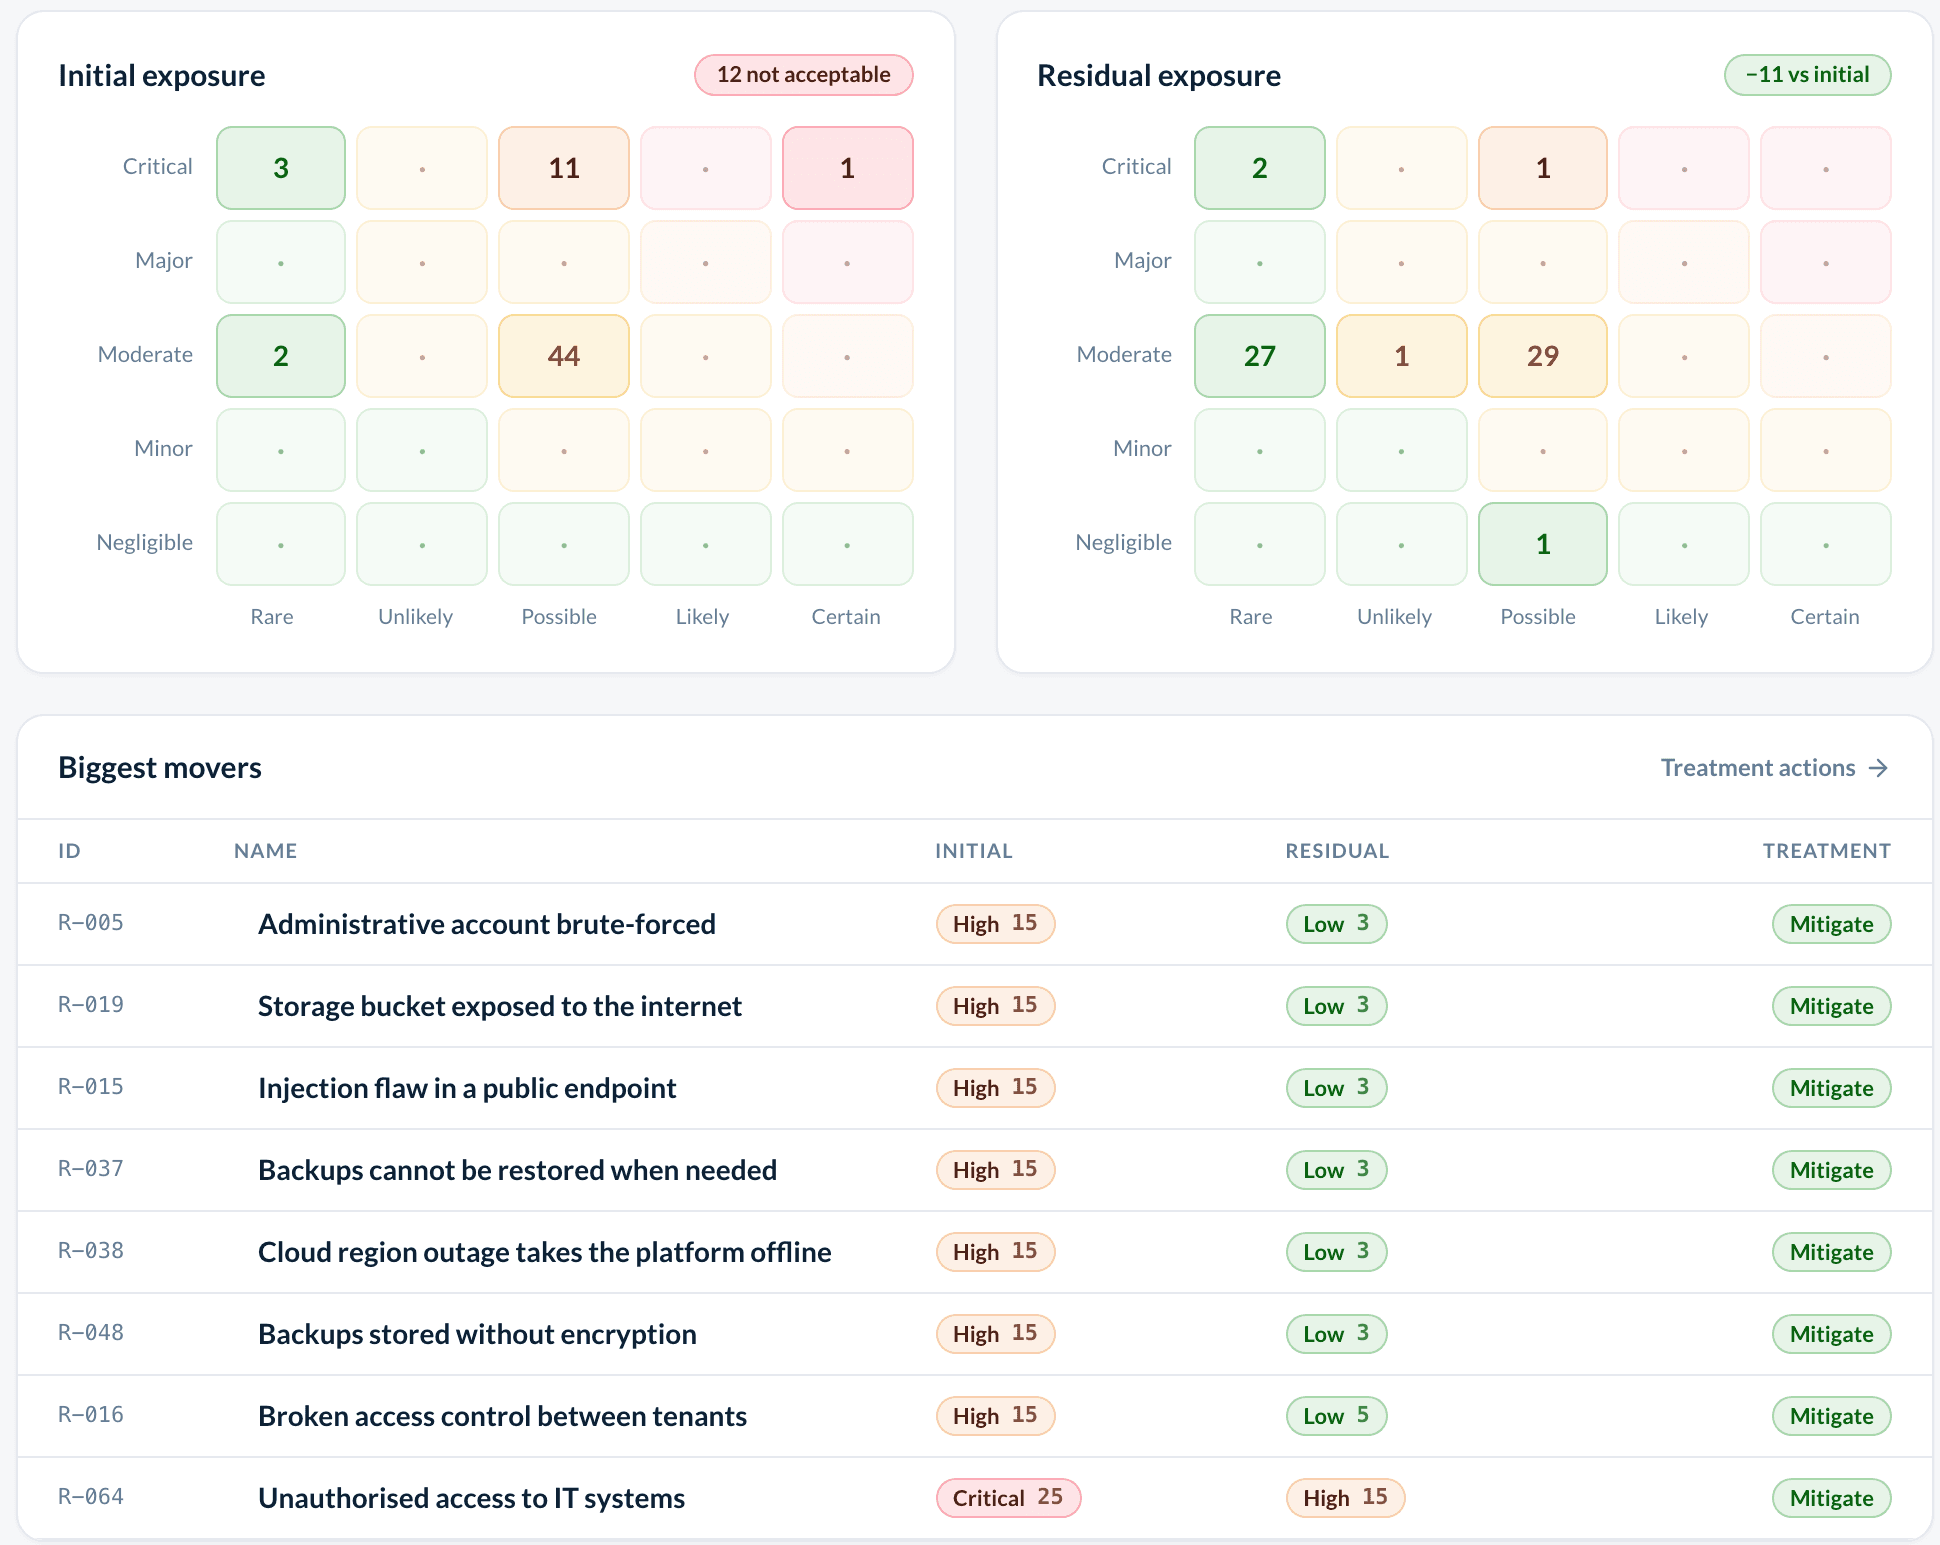
The assessment matrix shows the register in this way. Its list of biggest movers shows which risks dropped the most.
Set your criteria
Do this once, before you add risks. You can resize a scale later, but that moves every stored rating.
- Open Risks → Settings. devguard starts you with a 5 × 5 matrix and four levels: Low, Medium, High, and Critical. High and Critical are not acceptable.
- Rename the levels and describe what each one means for your organization. Decide which levels you do not accept.
- Set the review interval: how many months a risk may go without a review. The settings guide explains each tab.
- Under People → Roles, create the roles that will own risks and actions, for example a CISO, a head of IT, and a data protection officer. Add the people who hold them.
A risk belongs to a role, not to a person. The owner role gets a notification when a risk is assigned to it or changes in an important way. A member of that role accepts the residual risk.
Add risks
You can add risks in three ways: by hand, from a catalog, or from a CSV file. The register lists every entry with its ID (R-001, R-002, and so on), its owner, and its initial and residual level in the level's color.
By hand
- Open Risks and select Add risk. The form opens as a panel.
- Give the risk a name that says what goes wrong, for example "Laptop lost while traveling" rather than "Device security". devguard creates the slug from the name.
- Choose the owner role.
- Under Impact, choose a threat class and a vulnerability class. Link the assets at risk, name the affected parties, and describe the consequences.
- Under Analysis, set the probability rating and the impact rating, and link the controls that mitigate the risk.
- Save. You can add the treatment later. The overview lists every risk that is not rated yet.
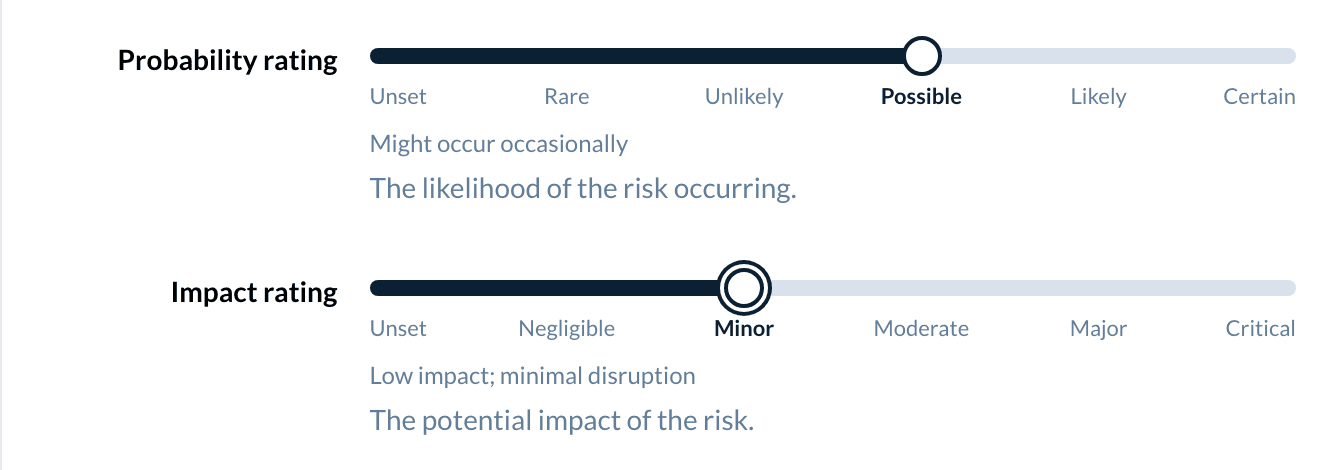
The same section asks for the speed of impact: how fast the damage happens, from hours to a year or more. It also asks whether the risk is developing, which means that its causes and consequences are not yet clear. For a developing risk, describe the warning signs you watch for. The overview reminds you while they are missing.
From a catalog
The arrow beside Add risk opens the template picker. It holds ready-made entries in English and German from these catalogs:
- the BSI IT-Grundschutz elementary threats, the ENISA Threat Landscape, the CSA Top Threats to Cloud Computing, and the OWASP Top 10;
- the NIS2 and DORA risk areas;
- quality risks and opportunities for ISO 9001, AI risks for ISO/IEC 42001, environmental aspects for ISO 14001, and OH&S hazards for ISO 45001.
Catalogs that match a framework you have adopted come first, marked For your frameworks.
- Select the arrow beside Add risk.
- Search the catalogs or browse one. Tick every entry that applies to you. An entry you already created is marked Already in your register. You can create up to 60 entries at once.
- Choose the owner role for all of them. Select the create button, which counts your entries, for example Create 2 risks.
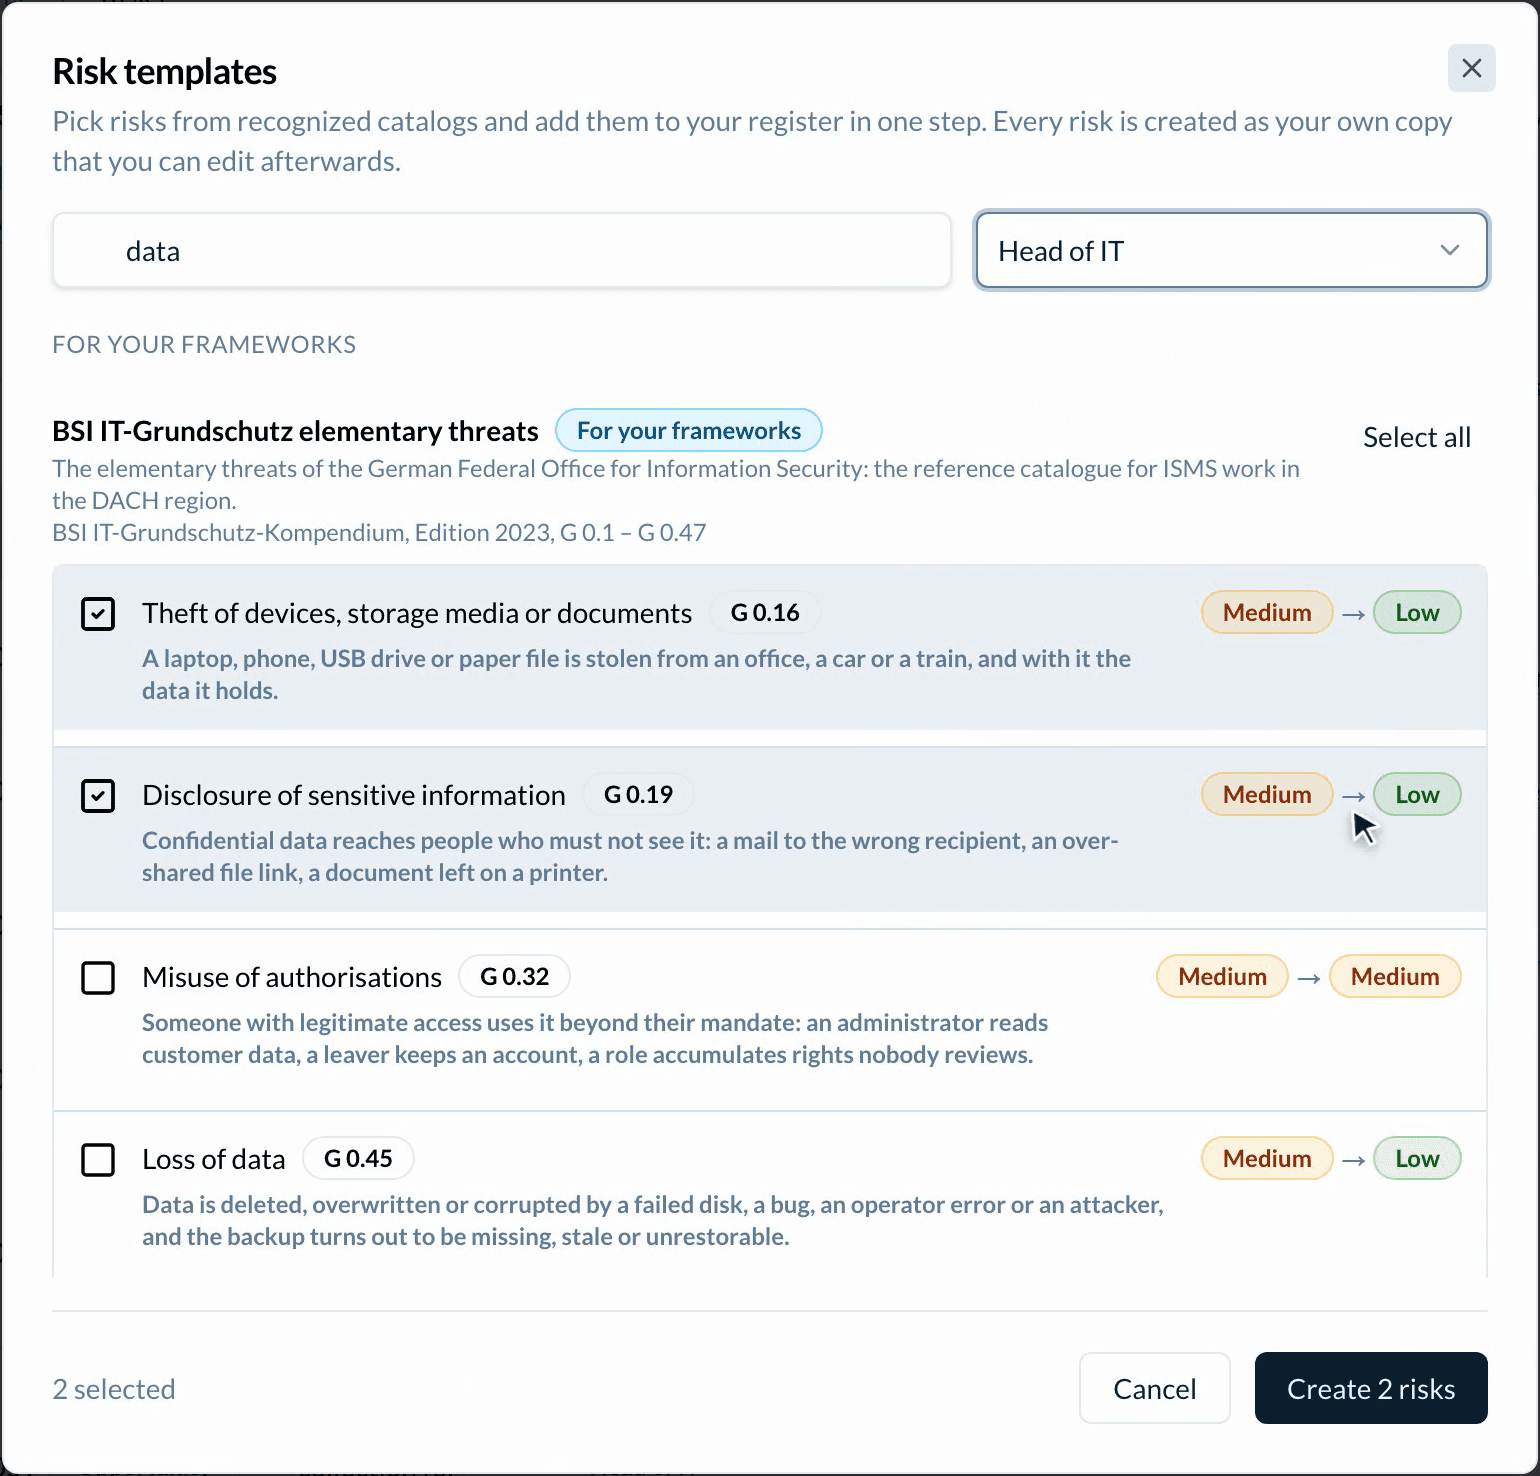
Each new risk is your own copy. It comes with a description, an impact description, a treatment strategy, and initial and residual ratings on your scales. The picker links the threat class and vulnerability class that the template names. If your organization has no class of that name, the picker creates it. You can edit the copies; the catalog never changes them again.
From a file
-
Open the menu at the right of the register's toolbar (the three dots) and select Download CSV template.
-
In a spreadsheet, fill in one row per risk. For the owner, the classes, the affected parties, and the labels, use the names you see in the app:
risks.csv name;ownerId;treatmentType;initialProbabilityRating;initialImpactRating Lack of capacity management;IT Management;mitigate;4;5 Data leak via a SaaS provider;CISO;ACCEPT;2;5 -
Save it as CSV and select Import CSV in the same menu.
-
A successful import ends with a message that counts the rows. If a row is refused, a dialog shows its row number, the column, and the reason. Correct those rows and import only them again.
Every column and its accepted values are in the reference under Import and export.
Decide the treatment
After you rate a risk, the register knows its level and whether that level is acceptable. The treatment says what you do about it.
-
Open the risk and select Edit. You can also edit a field directly on the detail page.
-
Under Treatment, pick the treatment type:
- Mitigate: reduce the risk.
- Transfer: insure it or give it to a contractor.
- Avoid: stop the activity that causes it.
- Accept: keep the risk as it is.
Describe the treatment in a sentence or two.
-
For Mitigate, Transfer, or Avoid, link the treatment actions that carry it out. If an action does not exist yet, select Manage beside the field. Treatment Actions opens in a new tab. Add the action there with an owner, a status, and a due date. Then come back to the form and pick it. One action can treat several risks.
-
Set the residual probability and residual impact: where the risk stands after the actions are done. Neither value may be higher than its initial value.
Accept the residual risk
ISO/IEC 27001 (6.1.3 f) requires the risk owner to approve the risk that remains. devguard records that approval on the risk.
- Open the risk's detail page. The Residual Risk Acceptance card shows whether the residual risk is rated and accepted.
- As a member of the risk's owner role, select Accept residual risk. People outside that role see a note with the name of the role that can accept.
Note: auditors can only read. An auditor in the owner role sees the button, but devguard refuses the acceptance. See Who can do what.
The risk report prints this record for every risk in its scope, with the initial and residual level and the treatment. You give this report to the auditor.
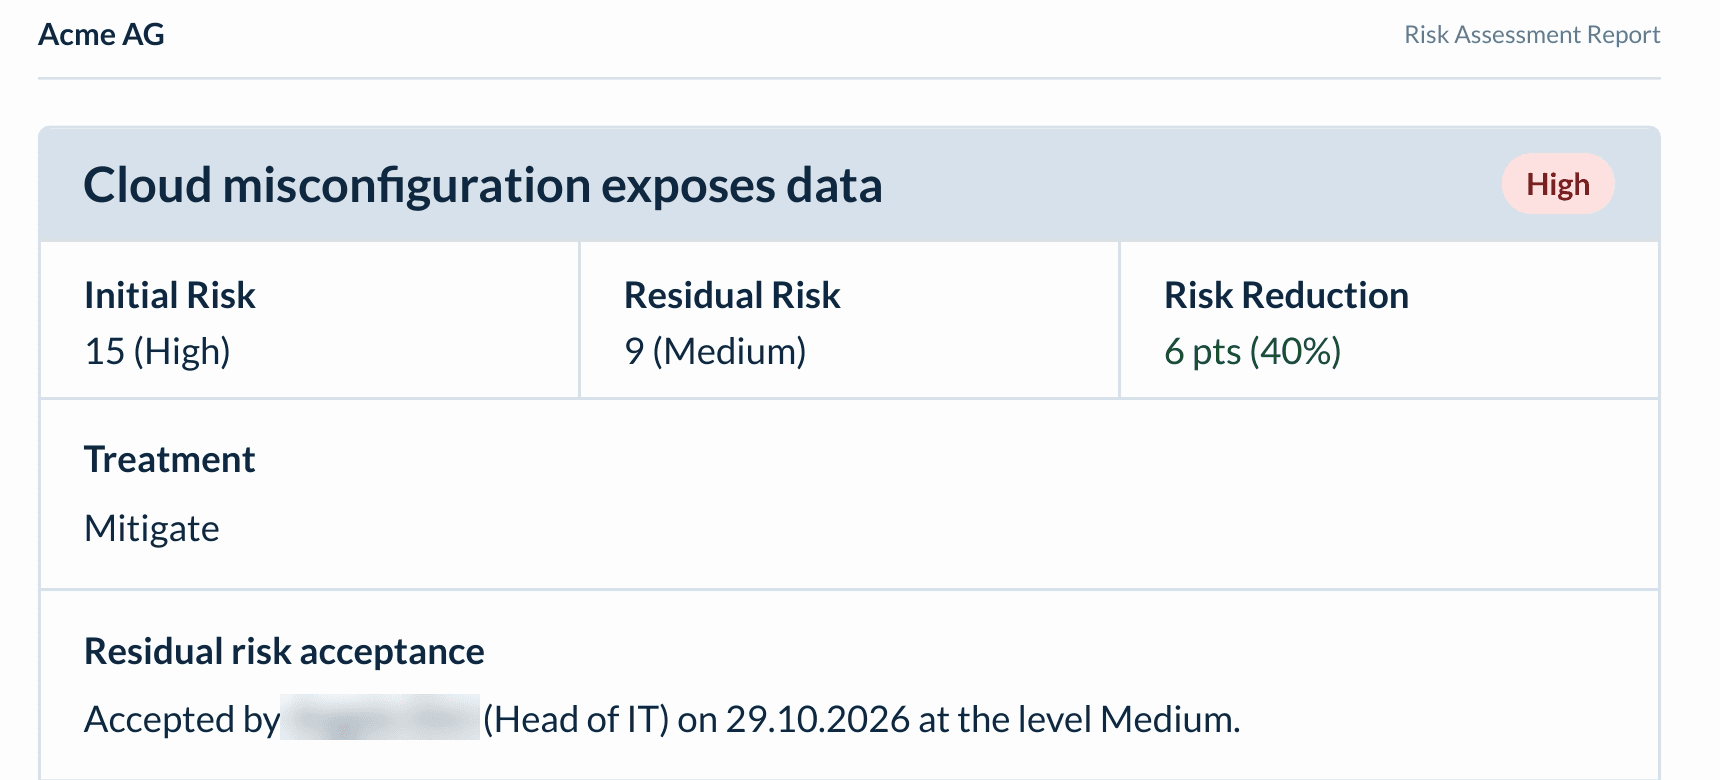
devguard withdraws the acceptance when its basis changes:
- a change to the owner, the treatment type, a residual rating, or the kind;
- a change to the risk criteria that moves the risk to another level;
- a change to the risk criteria that makes its level acceptable or not acceptable.
The owner then accepts again.
The owner may accept a residual risk at a level that is not acceptable, because that decision is theirs. The overview keeps listing such a risk while its level stays not acceptable. Write the reason in the treatment description, so that the next review finds it.
Review the register
- Open Risks → Reviews and select Start Risk Review.
- Give it a name and choose the Coordinator role, the Priority (all risks, or only the high, medium, or low ones), and the deadline.
- The coordinator approves or rejects each risk against its snapshot, a copy of the risk taken when the review started. A rejection needs a reason and creates a finding in the audit findings register.
- When every item is decided, select Finish Review. The review is now locked.
Run a review at least once per review interval. Then the overview no longer shows Review due. The reviews guide explains the comparison views, how to withdraw a decision, and the report.
Opportunities
ISO 9001 and ISO 14001 (clause 6.1) ask for opportunities as well as risks. An opportunity is an entry in the same register with the kind Opportunity. Add one with Add opportunity, or change the kind of an entry in its edit form.
An opportunity is rated for likelihood and benefit. Its second rating is a target, not a residual. It never counts toward your risk exposure. Opportunity fields in the reference lists every difference.
Reference
The overview
The overview counts risks only, not opportunities.
- Risk Posture shows each risk's current level: after treatment where rated. Select a level to open the register filtered to it.
- Risk Process shows one bar per step of the process.
- Open Gaps links to the gap analysis.
- What Needs Doing lists the open findings, highest level first:
| Finding | Listed when | Cleared by |
|---|---|---|
| Not yet rated | No initial rating | Rating the risk |
| Not acceptable, no treatment decided | Level not acceptable, treatment unknown | Picking a treatment type |
| Treatment decided, no actions planned | Level not acceptable, mitigate, transfer or avoid, no action | Linking an action |
| Treatment actions overdue | An open action is past its due date | Closing it or moving the date |
| Residual risk not accepted | Treatment decided, residual rated, not accepted | The owner accepting |
| Accepted at an unacceptable level | Accepted at a level that is not acceptable | Treating further, or revisiting the criteria |
| Review due | Not approved in a review within the interval | Running a review |
| Developing risk without warning signs | Marked developing, no warning signs | Describing them |
An overdue action appears once, under the highest-level risk it treats. For a risk that was never reviewed, Review due counts from the date it was created.
Fields
Name, owner, and kind are required. The button you use to add the entry sets the kind. You can change it in the edit form. devguard creates the slug from the name.
| Section | Fields |
|---|---|
| General | Name, owner role, description, labels (managed under Collections → Labels) |
| Impact | Affected parties (roles), threat class, vulnerability class, assets, impact description |
| Analysis | Probability rating, impact rating, speed of impact (very fast, fast, moderate, slow), developing risk, warning signs, controls |
| Treatment | Treatment type (unknown, mitigate, accept, avoid, transfer), treatment description, treatment actions, residual probability, residual impact |
A rating is a step of the scale, or empty. A residual rating is at most the initial one. You can link only controls of a framework you have adopted; devguard skips any other. The accept action records the residual acceptance: who, which role, when, at which level, and under which settings version. The changes listed under Accept the residual risk clear it.
Opportunity fields
| Risk | Opportunity | |
|---|---|---|
| Rating | Probability × impact | Likelihood × benefit; higher is better |
| Second rating | Residual, at most the initial | Target, may exceed the initial |
| Treatment field | Treatment type: Mitigate, Transfer, Avoid, Accept | Response: Enhance, Share, Pursue, Accept (same order, so switching the kind keeps the choice) |
| Threat and vulnerability class, speed of impact, developing | Yes | Hidden |
| Residual acceptance | Yes | No |
| Color scale | Risk levels | Blue |
| Counted in the dashboard, overview, risk report, banded reviews | Yes | No |
A review of all risks includes opportunities, marked with a badge. The register's Kind filter separates them. The matrix has an Opportunity matrix, and the Kind select of the risk report switches to the opportunity report.
The register
| Toolbar item | Does |
|---|---|
| Search | Name or ID (R-012) |
| Kind, Owner, Treatment type | Quick filters |
| Filter | Affected parties, labels, threat class, vulnerability class, residual rating band, current, initial, and residual level, speed of impact, developing, last change |
| Archived | Shows archived risks; they keep data, links, and history and can be restored |
| Views | Saves a filter set |
| Row selection | Deletes or exports several risks at once |
| Detail tab | Holds |
|---|---|
| Detail | Fields, assessment, residual acceptance, related data |
| Controls | Linked controls |
| Actions | Integration actions that create tickets elsewhere (not treatment actions) |
| Evidence, Tasks, Comments, History | Linked evidence, follow-up tasks, the discussion, every change |
IDs: R-001 for risks, RTA-001 for treatment actions, RAR-001 for risk reviews.
Import and export
The template lists every column you can import. devguard matches columns by their header, so you can import any subset in any order.
| Column | Accepts |
|---|---|
name | Required, 2 to 255 characters |
slug | Lowercase letters, digits, hyphens; derived from the name when blank (Zürich office becomes zuerich-office) |
ownerId | Required. A role's name as shown in the app, in any case, or its id |
affectedParties, threatClassId, vulnerabilityClassId, labels | Names or ids; several separated by a comma or a semicolon |
riskTreatments, controlLinks, assetLinks | Ids only |
kind | RISK or OPPORTUNITY; empty means risk |
treatmentType | UNKNOWN, MITIGATE, ACCEPT, AVOID, TRANSFER, or the label in your language (Mindern) |
velocity | VERY_FAST, FAST, MODERATE, SLOW, or the label (Fast (weeks)) |
emerging | yes, no, true, false, ja, nein, 1, 0 |
| Rating columns | Level numbers from 1 (the lowest) to the size of the scale |
If two records share a name, devguard refuses the name; use the id. devguard detects the delimiter (comma or semicolon). Both UTF-8 and Excel's Windows encoding work.
devguard creates the rows one by one, so the valid rows stay when others fail. Rows over your plan's limit are counted separately. Export writes the rows the register shows, with its filters. Export all writes every risk. Linked records appear as JSON in their cell.
Who can do what
| Role | Register (risks, classes, actions, reviews) | Risk settings | Comments | Accept a residual risk |
|---|---|---|---|---|
| Owner | Create, edit, archive, delete | Change | Write | If in the risk's owner role |
| Admin | Create, edit, archive, delete | Change | Write | If in the risk's owner role |
| Member | Read | Read | Write | If in the risk's owner role |
| Auditor | Read | Read | Read | No: refused with "Your role can read this organization but not change it." |
| Organization token | Create, edit, archive, delete, within its scopes | Read | None: comments are not in the API | No: the app never puts a token in a role |
To mark expected threats in the gap analysis, you need the right to edit asset classes. Owners and admins have it.
Limits
The free plan holds 100 risks, 10 treatment actions, and 4 risk reviews. The business plans have no limit. A banner on the register warns you from 80 percent of the limit. Creating risks from templates checks the limit once for all selected entries. Archiving a risk frees its place, and restoring it takes the place again.
Where risks appear elsewhere
| Where | What appears |
|---|---|
| Coverage | A linked risk makes a control Partial, unless the control is assessed by hand or not relevant. It shows under Linked Items |
| Incidents | The risk that came true, linked under Relations |
| Vendors | Risks linked through the API's riskLinks |
| Tasks | Follow-up tasks on the risk's Tasks tab |
| Deadlines | Treatment actions with a due date, until archived, Implemented, or Deprecated |
| Risk report | The criteria in force, the register by level, the inventory, each residual acceptance |
| Audit log | Every change to risks, actions, classes, reviews, and the criteria |
AI assistant and MCP
| Surface | Tools and resources |
|---|---|
| AI assistant | listRisks, createRisk, listRiskTemplates, createRisksFromTemplates, getRiskCriteria, getRiskOverview, getRiskGapAnalysis, listTreatmentActions, listRiskReviews |
| MCP (read-only) | listRisks, getRiskCriteria, getRiskOverview, getRiskGapAnalysis, listRiskTemplates, listRiskReviews, listTreatmentActions |
| MCP resource | devguard://risk/<slug> |
| MCP prompts | summarize-risks, draft-risk-treatment |
API
The base URL is https://app.devguard.ch/api.
- Every call sends
Authorization: Bearer <key>with a personal or organization token. - Every
POST,PUT, andPATCHsendsContent-Type: application/json. - Errors come back as
{ "message", "code", "status" }. - Every list and create call sends
organizationId. Calls on/{id}/take the organization from the record. - A personal key that belongs to two organizations makes one call per organization. An organization token must send its own organization, or the call fails with 403.
The API reference lists every field.
Ratings are positions, not levels. A rating is an integer: its position on the scale, starting at 1, or null when unrated. A value outside your scale is refused. The API never returns a level. Compute it as criteria.matrix[impact - 1][likelihood - 1], an index into criteria.levels from GET /risks/criteria/.
Create a risk:
curl -X POST https://app.devguard.ch/api/risks/ \
  -H "Authorization: Bearer $DEVGUARD_API_KEY" \
  -H "Content-Type: application/json" \
-d @risk.json{
"organizationId": "<organization-id>",
"slug": "laptop-lost-while-traveling",
"name": "Laptop lost while traveling",
"ownerId": "<role-id>",
"treatmentType": "MITIGATE",
"initialProbabilityRating": 4,
"initialImpactRating": 4,
"residualProbabilityRating": 2,
"residualImpactRating": 3,
"treatmentDescription": "Disk encryption, remote wipe",
"assetLinks": ["<asset-id>"]
}The response is the risk without relations and without a level. On the default criteria, 4 × 4 is High and 2 × 3 is Medium, but you compute that yourself. A shortId of 12 is what the app shows as R-012.
A taken slug, a rating outside your scale, or a residual above the initial rating returns 400 with a message naming the problem.
Accept the residual risk, as a member of the owner role:
curl -X POST \
  https://app.devguard.ch/api/risks/<risk-id>/accept-residual/ \
  -H "Authorization: Bearer $DEVGUARD_API_KEY" \
  -H "Content-Type: application/json" \
-d '{}'{
"residualAcceptedAt": "2026-10-29T09:20:03.551Z",
"residualAcceptedByName": "Anna Muster",
"residualAcceptedRoleName": "CISO",
"residualAcceptedLevel": "Medium",
"residualAcceptedCriteriaVersion": 1,
"residualAcceptedRating": 6
}A caller outside the owner role gets 403. An organization token also gets 403, because the app never puts a token in a role. An opportunity, an archived risk, or a missing residual rating gets 412. An unknown id gets 404.
| Method | Path | Purpose |
|---|---|---|
GET | /risks/ | List risks (parameters below) |
POST | /risks/ | Create a risk; slug, name, ownerId, organizationId required |
GET | /risks/{id}/ | Read one risk with its relations |
PATCH | /risks/{id}/ | Update; not partial, see below |
DELETE | /risks/{id}/ | Delete |
POST | /risks/{id}/archive/ | Archive |
POST | /risks/{id}/restore/ | Restore; re-checks the plan limit |
POST | /risks/{id}/accept-residual/ | Accept the residual risk |
GET | /risks/templates/ | List the catalog |
POST | /risks/from-templates/ | Create up to 60 risks: templateIds, ownerId, locale (en default, or de), organizationId |
GET, PUT | /risks/criteria/ | Read or replace the criteria; see the settings guide |
GET | /risks/criteria/versions/ | List criteria versions |
GET | /risks/overview/ | The overview |
GET | /risks/gap-analysis/ | The gap analysis; see the gap analysis guide |
POST | /risk-control/map/ | Link a control |
DELETE | /risk-control/unmap/ | Unlink a control |
GET | /risk-control/mappings/ | List linked controls |
GET | /risk-control/search/ | Search controls to link |
GET, POST | /risk-reviews/ | List and start reviews |
PATCH | /risk-reviews/{id}/ | Update or finish a review |
GET, DELETE | /risk-review/{id}/ | Read or delete a review (singular path) |
PATCH | /risk-review-items/{id}/ | Approve an item, or null to withdraw |
POST | /risk-review-items/{id}/reject/ | Reject an item: reason, findingType |
GET, POST | /treatment-actions/ | List and create actions |
GET, PATCH, DELETE | /treatment-actions/{id}/ | Read, update, delete an action |
GET, POST | /threat-classes/ | List and create threat classes |
GET, PATCH, DELETE | /threat-classes/{id}/ | Read, update, delete a threat class |
GET, POST | /vulnerability-classes/ | List and create vulnerability classes |
GET, PATCH, DELETE | /vulnerability-classes/{id}/ | Read, update, delete a vulnerability class |
Reviews, treatment actions, threat classes, and vulnerability classes also take POST /{id}/archive/ and POST /{id}/restore/. The /risk-action/ paths (map, unmap, mappings, search) link integration actions in the same way as /risk-control/.
GET /risks/ needs organizationId. Optional parameters:
page(from 1) andlimit(5 to 100, default 100);filterByName(a name orR-012) andfilterByArchived(activeorarchived);filterByRating(high,medium,low) andfilterByLabels(label ids);sortColumnwithsortDirection, orsortandfiltersas JSON.
It returns items, total, page, and limit.
PATCH is not partial. PATCH /risks/{id}/ needs slug, name, ownerId, the four ratings, and treatmentDescription in every call. Link arrays replace the existing links. The same holds for the other resources: send slug and name every time, and ownerId for an action.
Bulk delete and the slug lookup are not in the public API. There are no CLI commands for risks; the CLI pushes evidence.
How is this guide?