Audits
Record each audit and its findings, correct every nonconformity and act on its cause, and close it only after you have checked that the corrective action worked.
An audit checks, with evidence, how far you meet a set of requirements (the audit criteria), for example in a certification, surveillance or internal audit. A finding is the result of evaluating the evidence against one requirement: a conformity, a nonconformity (the requirement is not met), an observation or an opportunity for improvement. devguard keeps a nonconformity open until someone records that its corrective action worked.
The tasks below follow the order of the work:
- Add an audit
- Prepare a SOC 2 review period
- Record a finding
- Correct a nonconformity and act on its cause
- Check the corrective action and close the finding
- Create the audit report
- Use the findings register
- Archive or delete an audit
To plan which clauses your internal audits cover over the certification cycle, see the audit programme. Scripts and integrations: see API below.
Add an audit
- Open Audits and choose Add audit.
- Enter a Name. The Slug (the short name in the link) is filled from the name.
- Choose the Type: Certification, Re-certification, Internal, External or Other. Choose External for a surveillance audit. Certification and Re-certification would start a new three-year cycle in the audit programme.
- Choose the Framework you are audited against. Only adopted frameworks are offered.
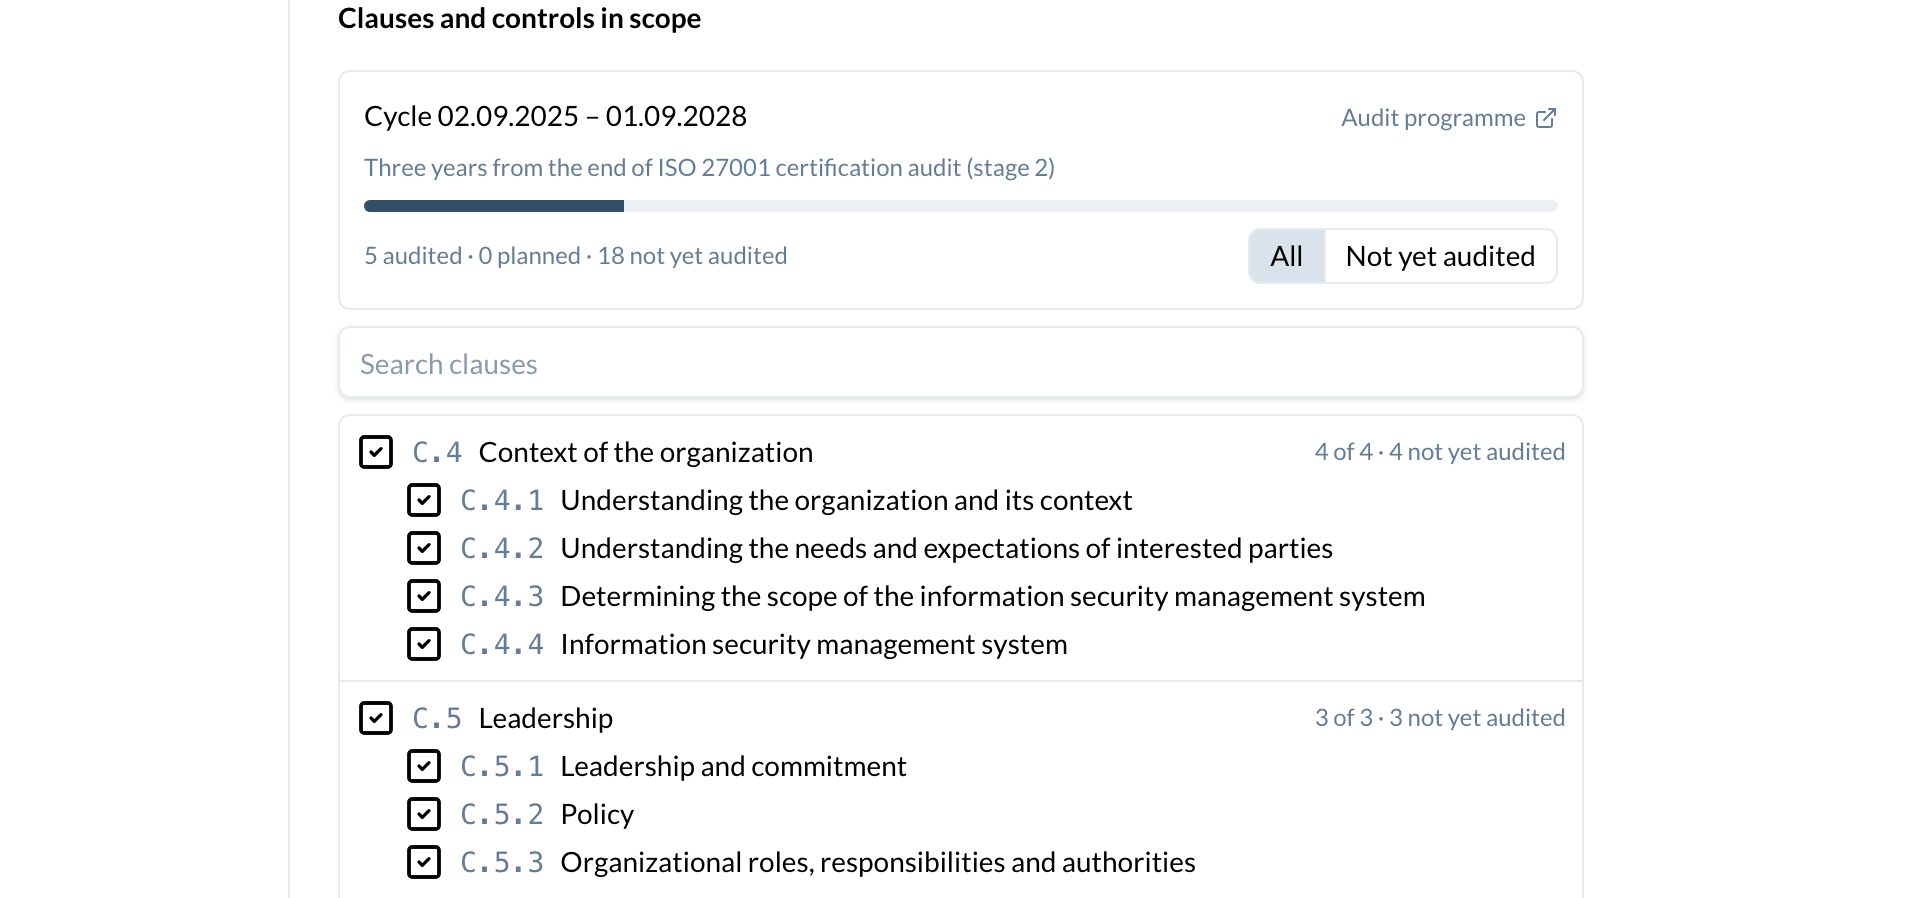
- Under Clauses and controls in scope, tick what this audit will examine. Ticking a chapter ticks all of its clauses. For an internal audit, the box above the list shows the certification cycle and how many clauses are already audited or planned in it. Choose Not yet audited to see only the gaps.
- Set Started at and Ended at. Enter the Auditor: the person or the certification body. For an internal audit, choose someone who does not audit their own work. In a small company, swap areas with a colleague or ask an external auditor.
- Fill in Audit objectives, Audit scope and Audit criteria. Leave Audit conclusion empty until the audit is over.
- Choose Create. To change the audit later, open it and choose Edit.
Watch out: pressing Enter in a one-line field, such as a date or the name, saves the form at once. Fields that you have not filled yet stay empty.
Audit scope is free text for locations, units and processes. Clauses and controls in scope is the list of requirements. Only the list counts in the audit programme.
Prepare a SOC 2 review period
A SOC 2 Type II report tests a period, often twelve months, and not only the days of the audit. Set the period before the fieldwork starts, so you see the gaps in time.
- Open the audit, choose Edit, and set Review period start and Review period end. The period can be at most 18 months.
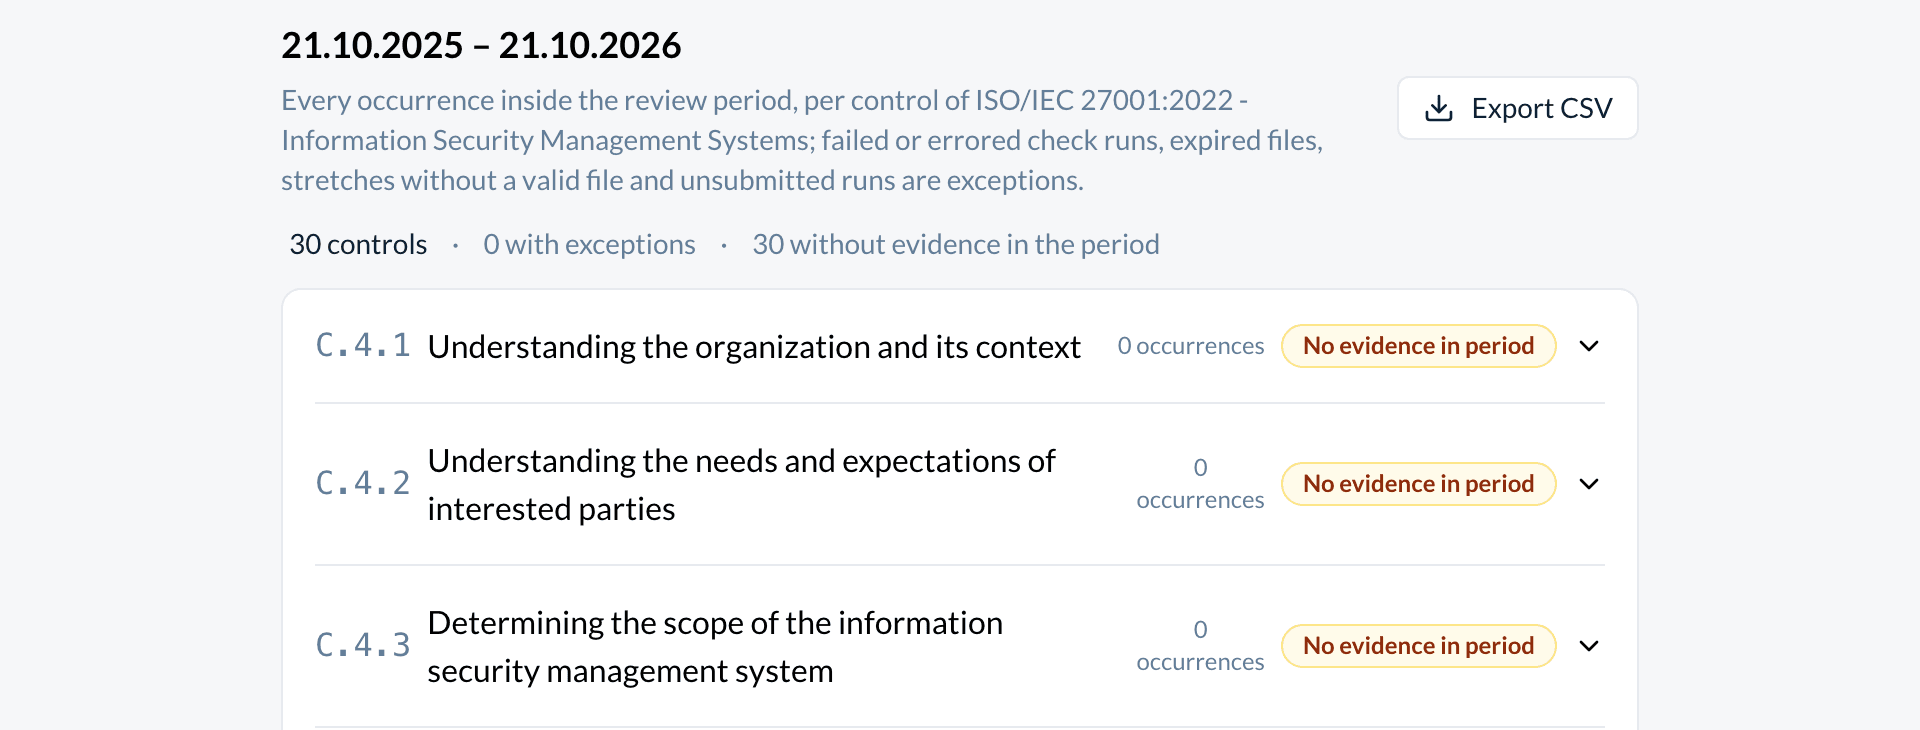
- Open the Review period tab. For each control of the audit's framework, it lists what happened in the period: evidence files, integration check runs, process submissions used as evidence, and the policy versions in effect. Below the controls, Reviews lists the risk, asset, vendor and access reviews of the period.
- Look at the controls marked No evidence in period and at the exceptions: failed checks, expired files, and reviews that are unfinished, overdue or have rejected items. Fix them before the auditor asks. If your access role cannot see a source, a control that draws on it shows Not visible with your role instead, and its counts can be incomplete.
- Choose Export CSV to send the full list to the auditor.
How a finding is closed
A finding has three statuses: Open, In progress and Closed. You move it forward in the ... menu of the finding. Mark in progress appears while it is Open, and Close finding appears while it is In progress. A nonconformity shows Close finding only once its effectiveness check is recorded.
A nonconformity (major, minor or not graded) needs one more step before it can be closed: the effectiveness check. Someone checks that the corrective action works and records what the check showed. Without this record, devguard refuses to close the nonconformity. Observations, opportunities for improvement and conformities can be closed without a check, but you can record one for them too.
If the problem comes back, choose Reopen finding. The finding goes back to Open, and its verification is removed, because the corrective action did not work. For a finding of an audit, the History tab of the audit still shows who verified it and when.
Record a finding
- Open the audit and go to the Findings tab. Choose Add finding.
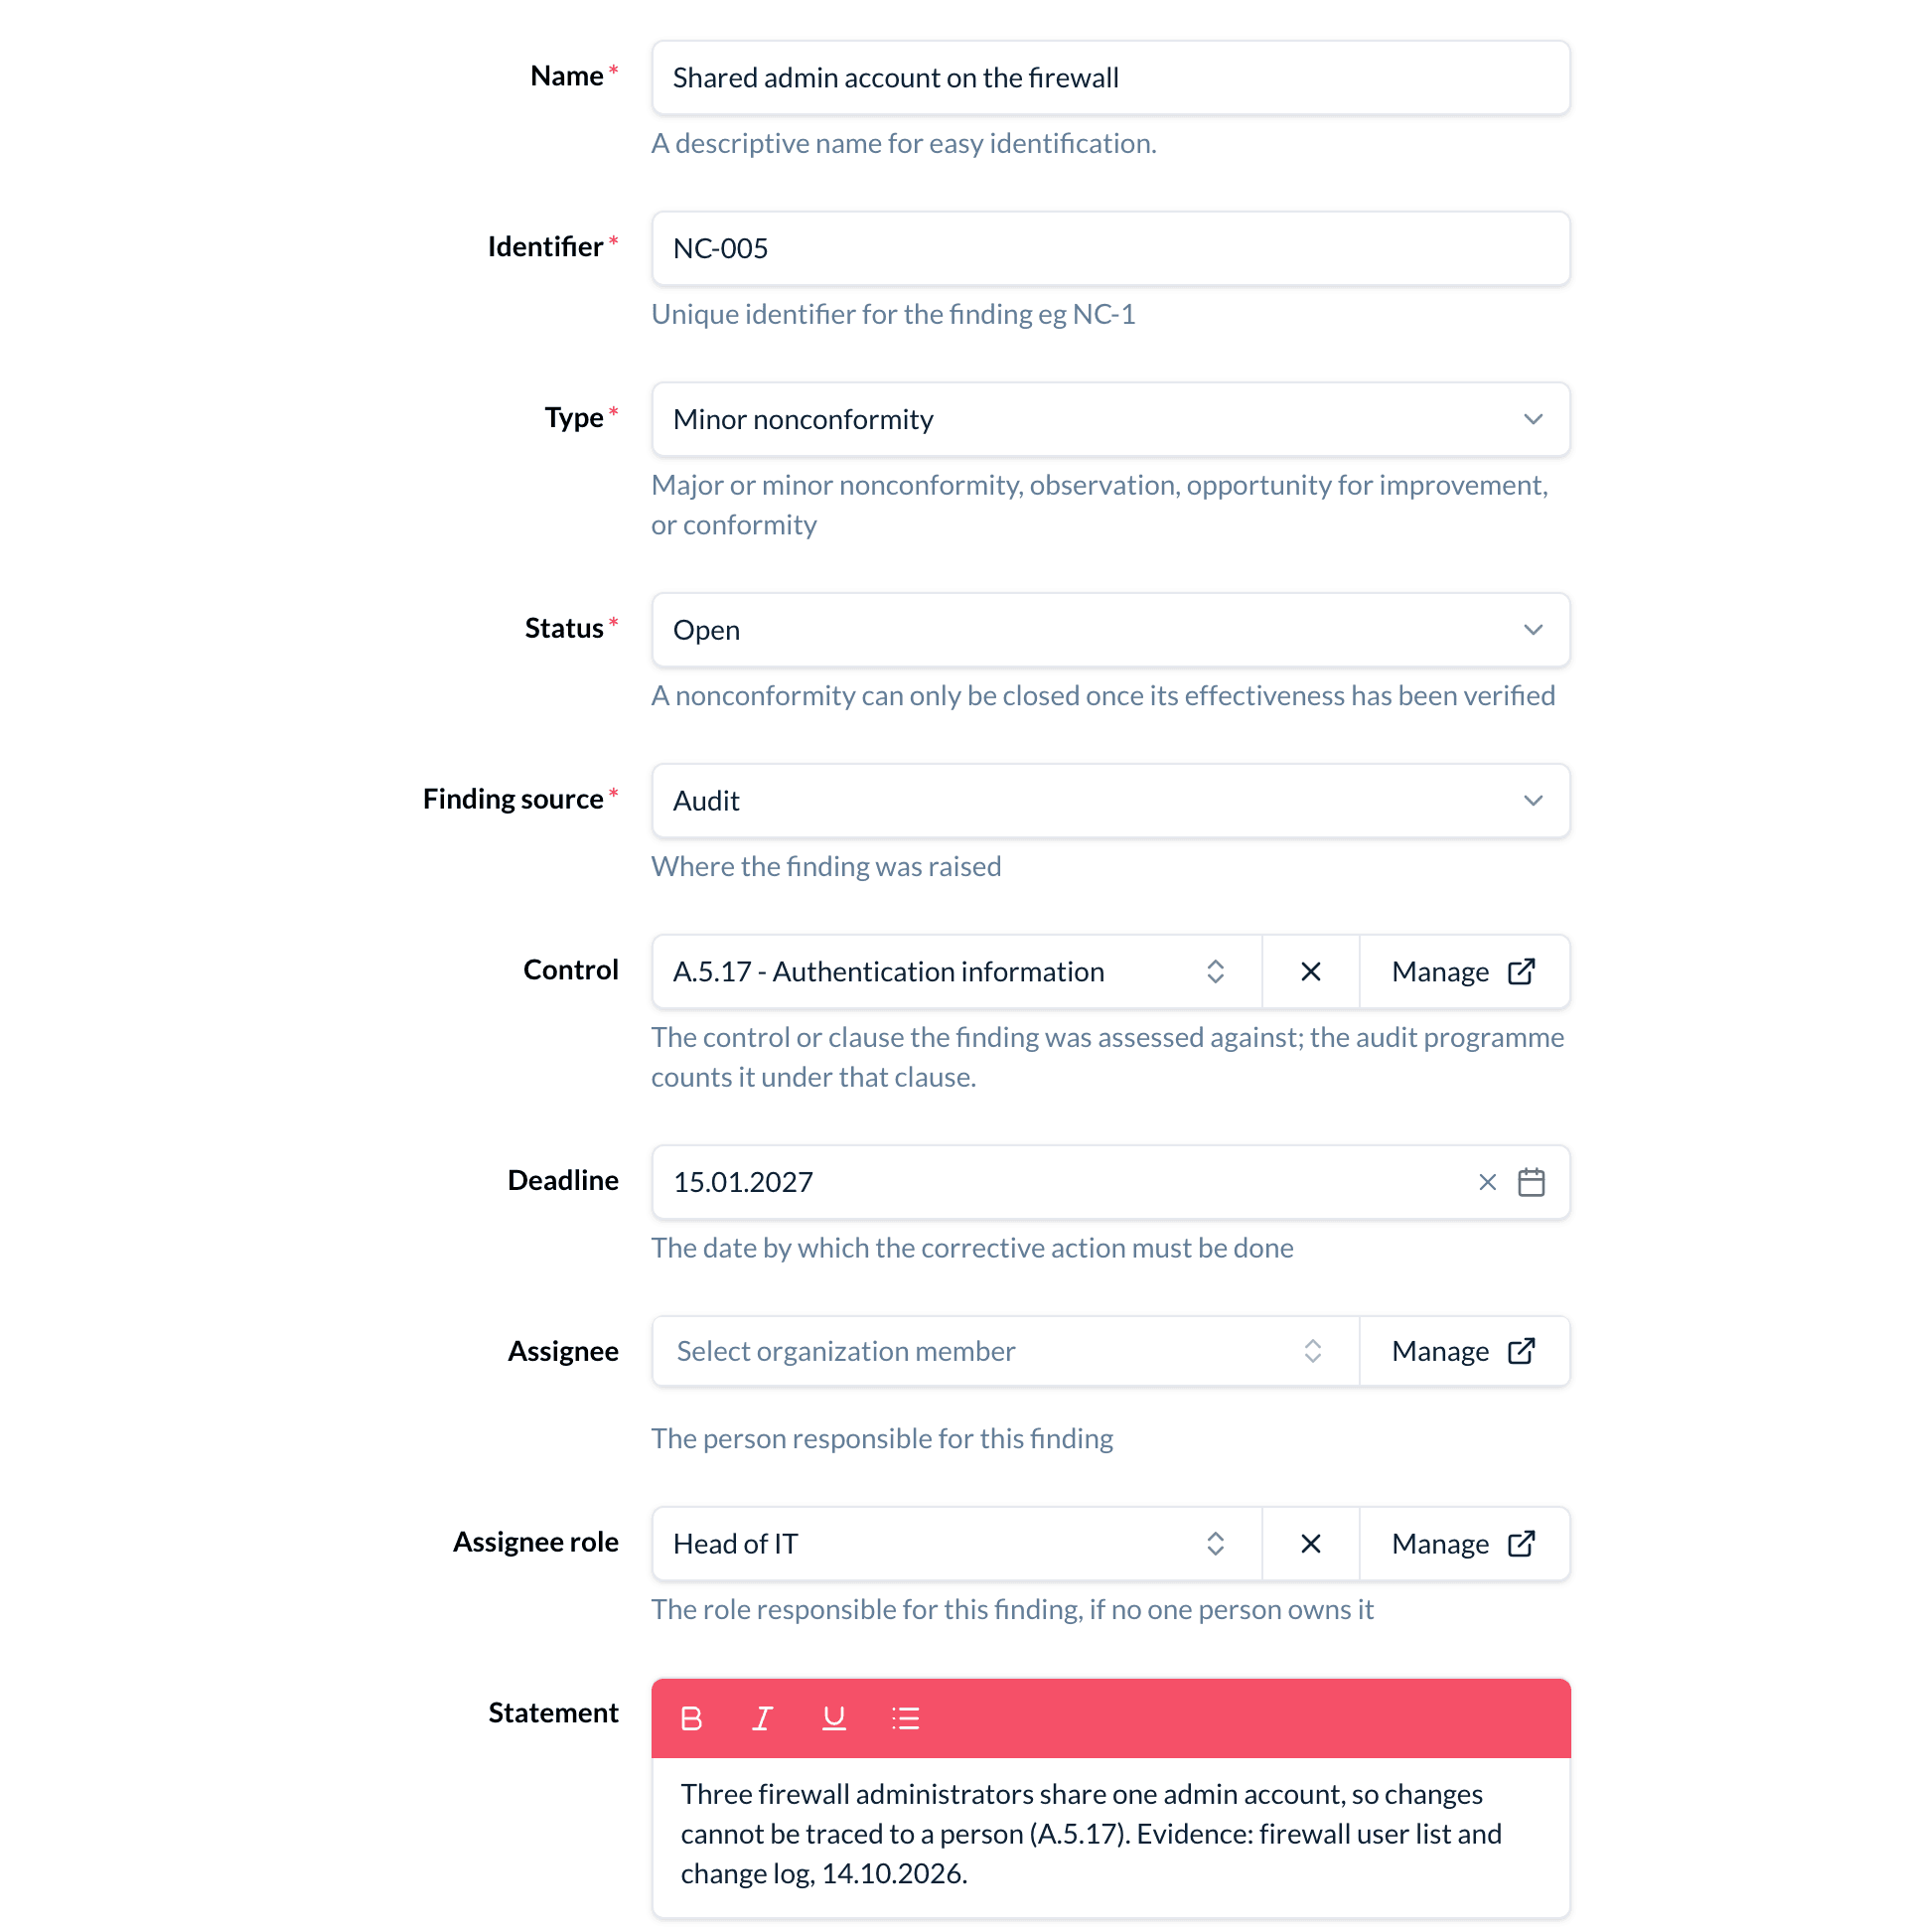
- Enter a Name and an Identifier that people can say in a meeting, for example "NC-5" or the clause number.
- Choose the Type and leave Status on Open. The types are listed under Finding types.
- Choose the Control: the requirement from the audit criteria that the finding is assessed against. The report prints it with the finding.
- Write the Statement: what was found, against which requirement, and the evidence the auditor saw.
- For a nonconformity, set a Deadline. Choose an Assignee (one person) or an Assignee role, not both.
- Choose Create. The finding appears on the audit and in the findings register.
Record conformities too. A conformity on a clause shows in the audit programme what was actually examined, even when nothing was wrong.
Correct a nonconformity and act on its cause
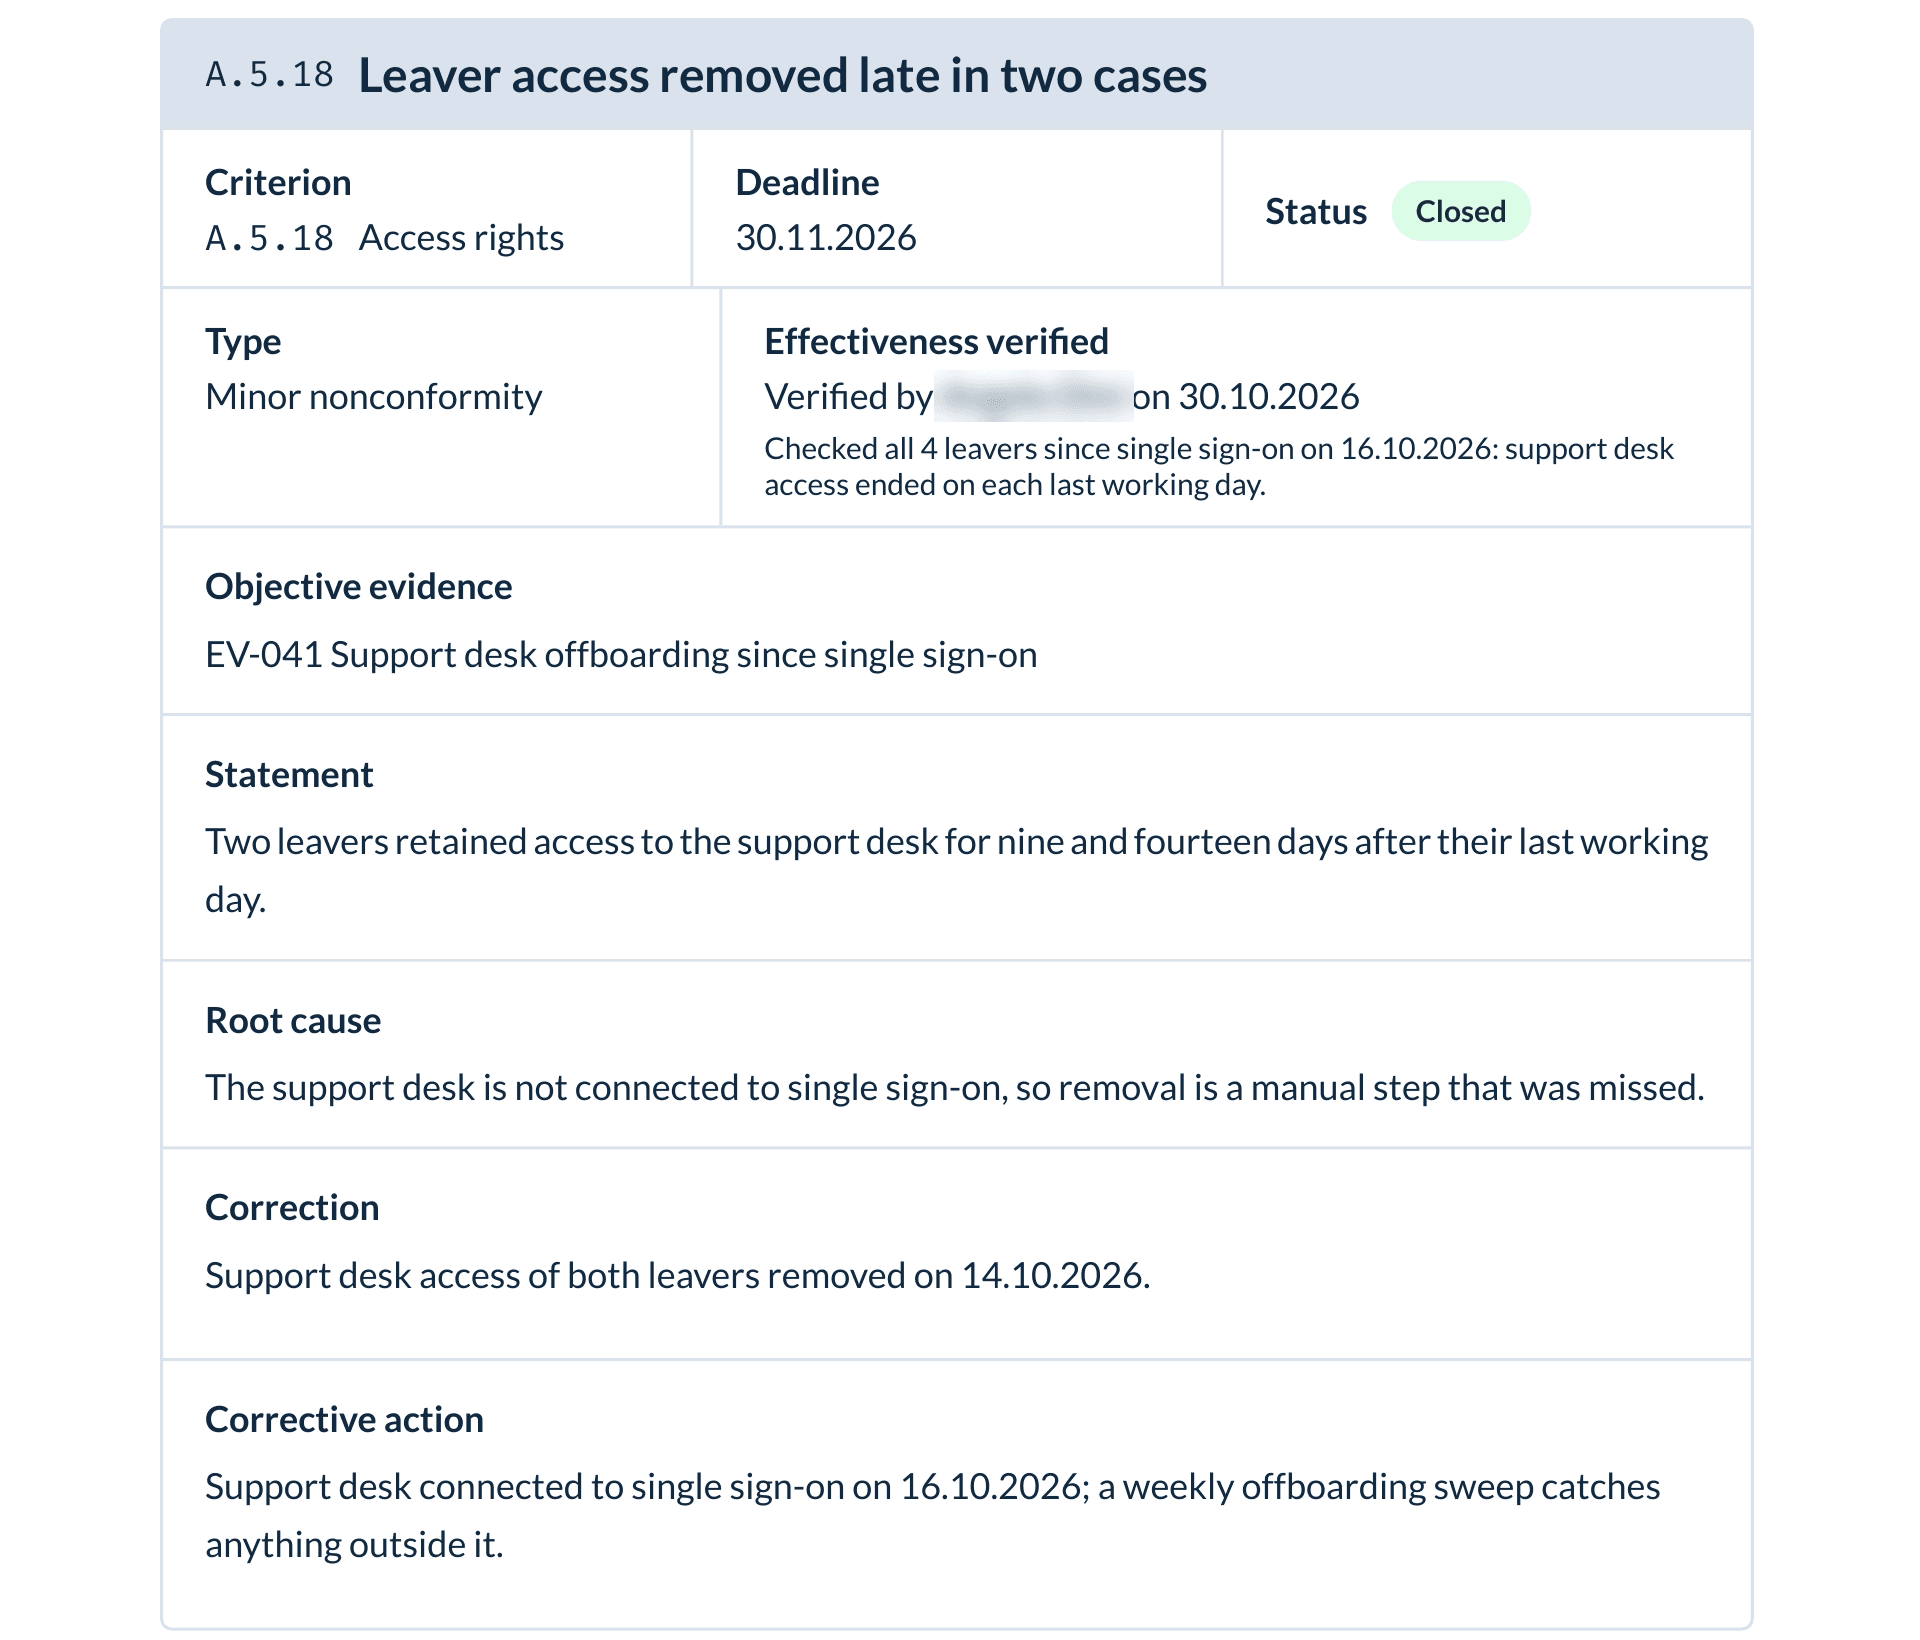
ISO/IEC 27001 clause 10.2 lists five steps after a nonconformity, and asks you to keep a record of them. The finding is that record:
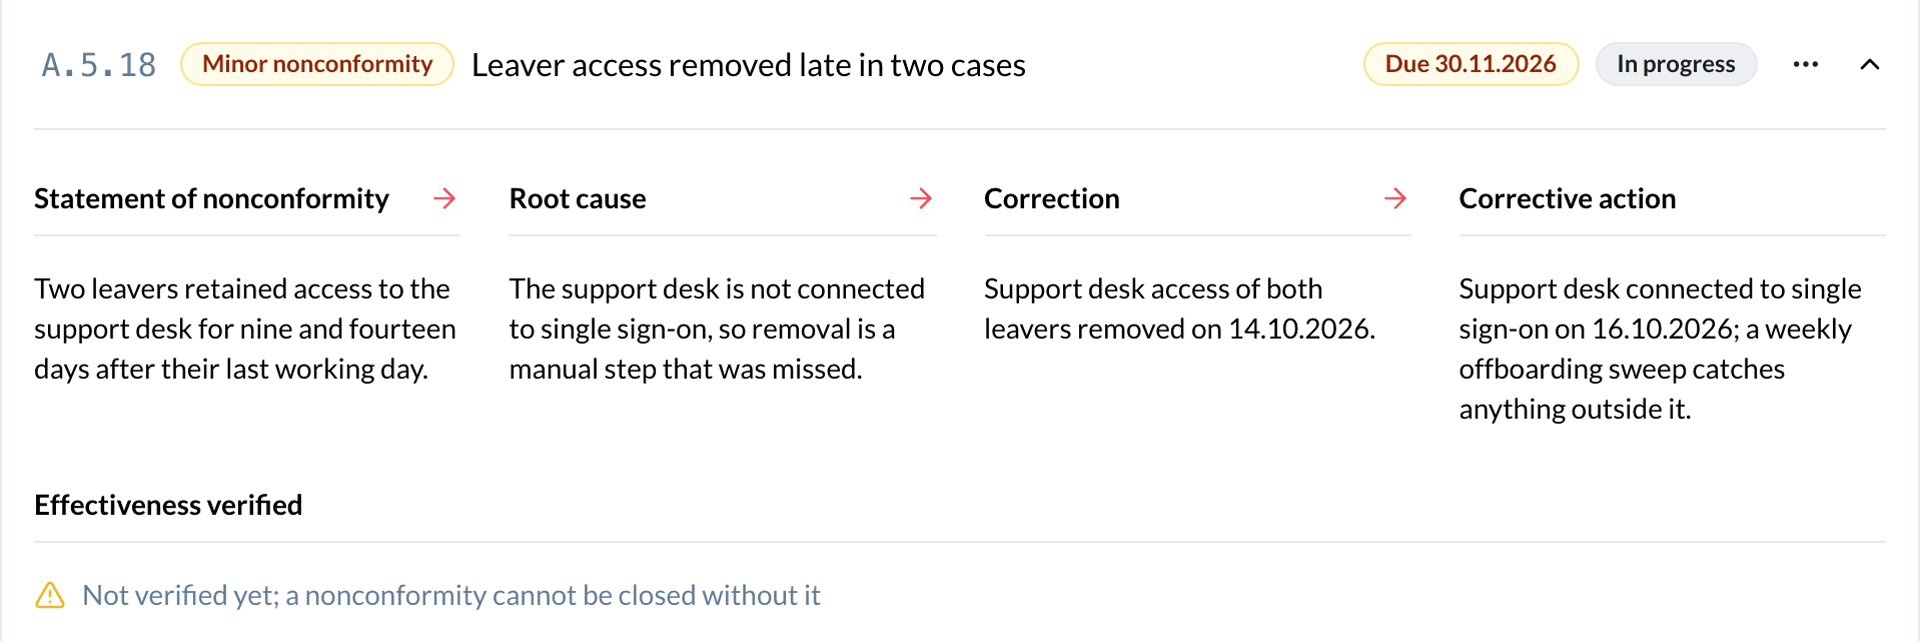
- a) React. Control and correct the problem, and deal with its consequences. Write this in Correction. For example, you removed the access of two leavers.
- b) Decide what action is needed. Find the cause, and check whether similar nonconformities exist or could occur. Write both in Root cause.
- c) Take the action. Write it in Corrective action, and add a task for each step under Tasks inside the finding. For example, you connected the system to single sign-on.
- d) Check that it worked. This is the effectiveness check in the next task.
- e) Change the ISMS if needed, for example a policy or a process. Add a task for it.
- When the work starts, open the ... menu of the finding and choose Mark in progress.
- In the same menu, choose Edit. Fill in Root cause, Correction and Corrective action, and choose Save.
- Under Objective evidence, attach evidence that the action was taken, such as an export or a ticket. You can link an existing evidence record or drop a file.
Check the corrective action and close the finding
- Give the corrective action time to work. Then check cases that happened after it took effect, for example all leavers since the change. The problem must not occur again.
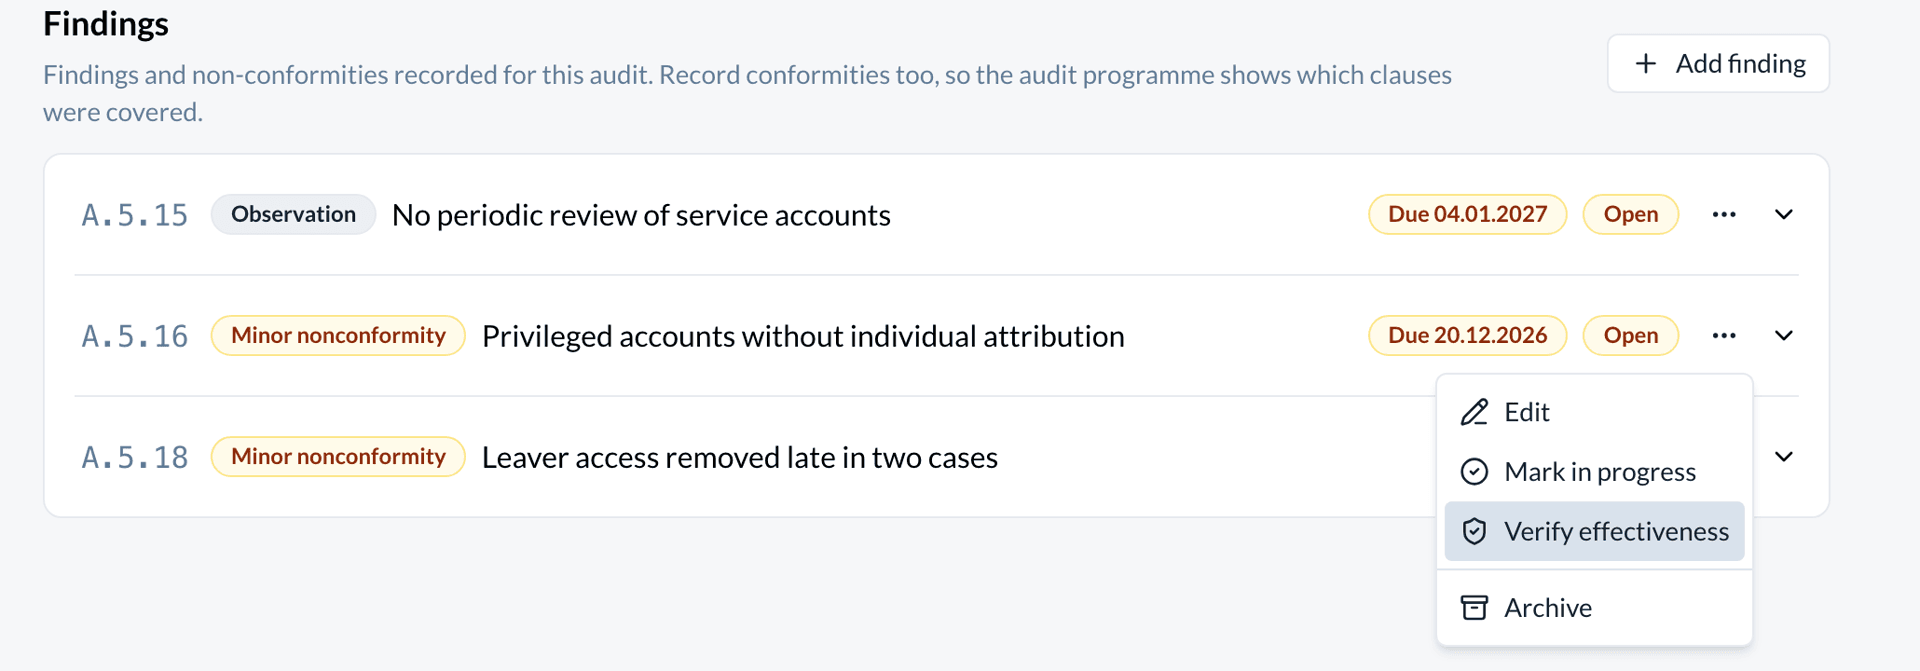
- Open the ... menu of the finding and choose Verify effectiveness.
- In Verification note, write what you checked and what the check showed. Choose Record verification. devguard adds your name and the date. The auditor will ask for this record.
- Open the ... menu again and choose Close finding. If tasks of the finding are still open, devguard asks you to confirm.
Create the audit report
- Open the audit and write the Audit conclusion.
- Open Actions and choose Generate Report. The PDF report opens in Reports.
The report contains the audit details, the objectives, the scope, the criteria and the clauses in scope. For each finding, it shows the control, the linked evidence, the statement, the root cause, the correction, the corrective action and the verification. It ends with your conclusion and a note that the audit was based on a sample.
Use the findings register
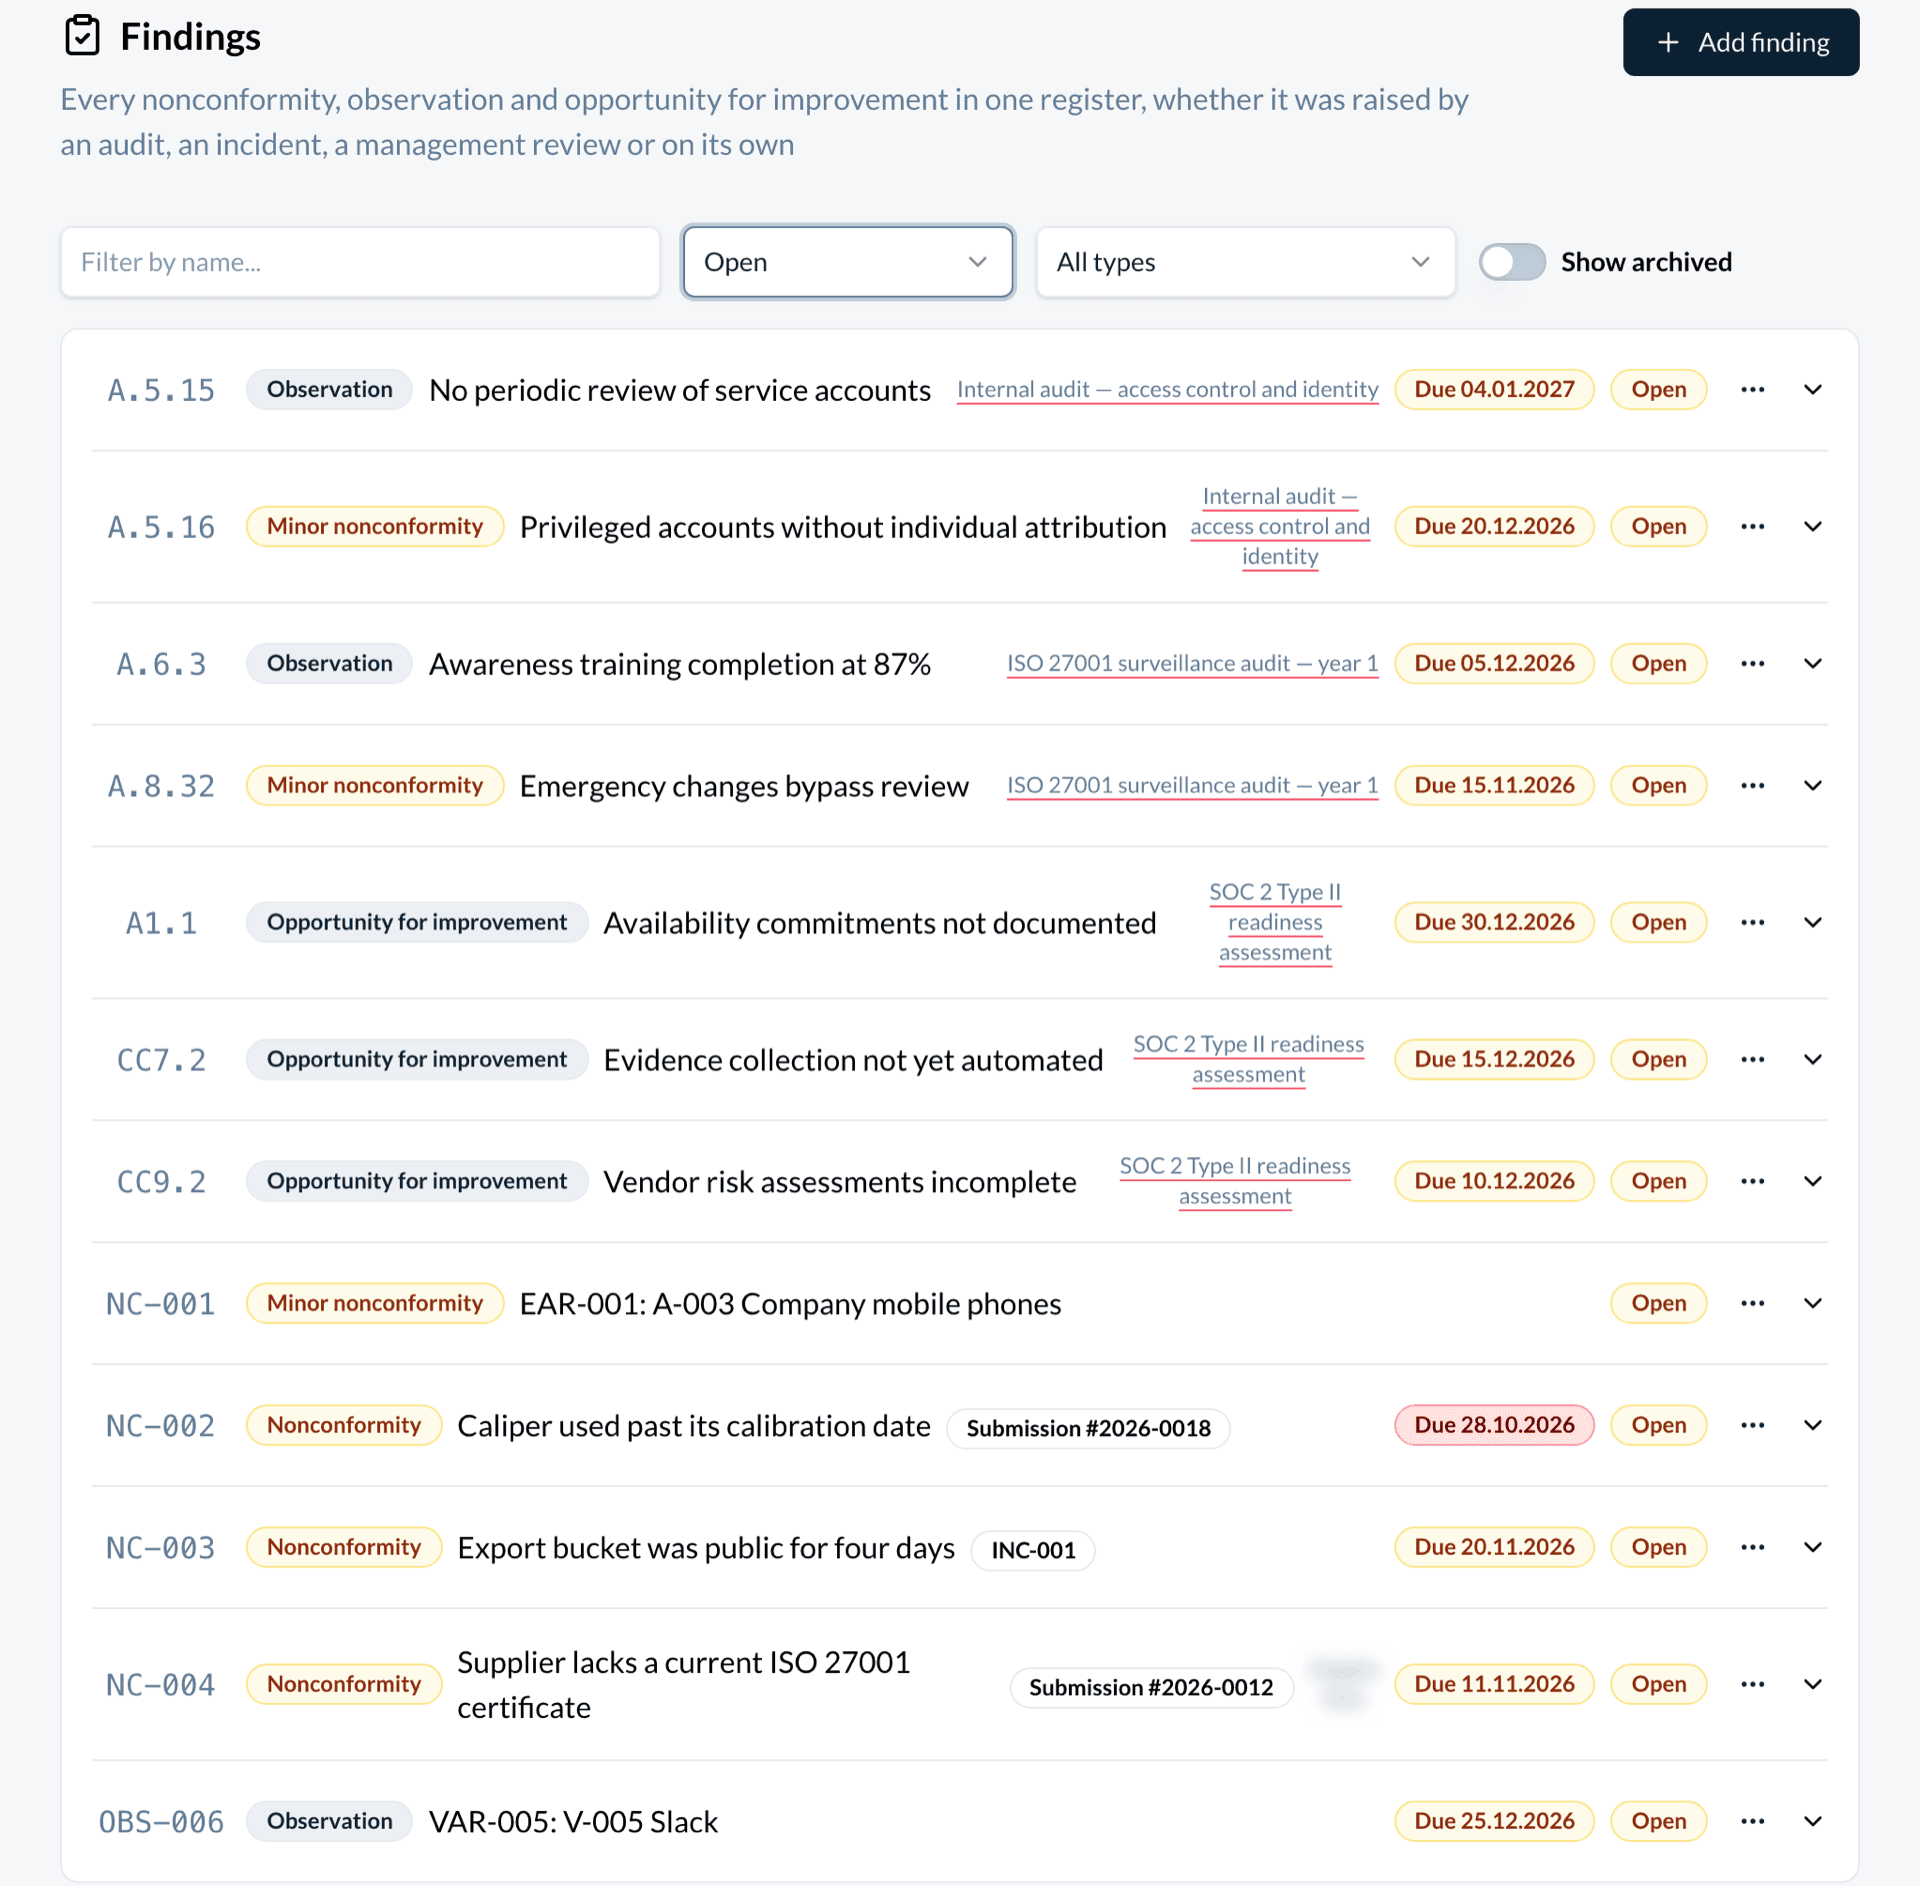
Audits → Findings lists the findings of all audits in one place. It also lists findings that did not come from an audit:
- A rejected item in a risk review, an asset review, a vendor review or an access review raises a finding with the source Review.
- Raise finding on an incident or on a process submission opens the finding form with that record as its source. A nonconformity raised this way needs a deadline.
- Add finding on the register creates a finding from any other source, such as a management review.
- Choose a status, such as Open, and a type to filter the list. Type in Filter by name... to search.
- Open a finding with the arrow at the end of its row.
- To archive a finding, open its ... menu and choose Archive. Findings cannot be deleted. Turn on Show archived to see them and restore them.
Archive or delete an audit
- Archive, in the ... menu of the audit list, hides the audit. Its findings leave Deadlines and the open findings on the dashboard. To restore it, choose Archived in the list.
- Delete, in Actions on the audit or in the ... menu of the list, removes the audit. Its findings stay in the findings register and in Deadlines, without an audit.
Reference
Audit fields
| Field | What it holds |
|---|---|
| Name, Slug | The name, and the short name used in the link. Both are required. |
| Type | Certification, Re-certification, Internal, External or Other. Required. Only internal audits appear in the audit programme. |
| Framework | An adopted framework. If you change it, the clauses in scope are cleared. |
| Clauses and controls in scope | The clauses and controls of the framework that this audit examines. |
| Started at, Ended at | The audit dates. They decide whether the audit is planned, in progress or done. |
| Auditor | The person or body that does the audit. |
| Audit objectives, Audit scope, Audit criteria, Audit conclusion | Formatted text (bold, italic, underline, lists). All four print in the report. |
| Notes | Plain text for anything else. |
| Review period start, Review period end | The period a SOC 2 Type II report tests. At most 18 months. |
An audit has the tabs Detail, Findings, Review period, Tasks, Comments and History. When the type or the dates of an audit change, the owners and admins get a notification.
Finding fields
| Field | What it holds |
|---|---|
| Name, Slug, Identifier | The name, the short name in the link, and a code such as NC-5. Required. |
| Type, Status, Finding source | Required. See Finding types. Status is Open, In progress or Closed. Source is Audit, Incident, Management review, Process, Review or Other. |
| Audit | The audit the finding belongs to. Optional. |
| Control | The requirement from the audit criteria that the finding is assessed against. |
| Deadline | When the corrective action must be done. |
| Assignee or Assignee role | One person or one role, not both. |
| Statement, Root cause, Correction, Corrective action | Formatted text. |
| Notes | Plain text. |
Finding types
| Type | Short form | API value | Check needed before Closed |
|---|---|---|---|
| Major nonconformity | Major NC | MAJOR_NONCONFORMITY | Yes |
| Minor nonconformity | Minor NC | MINOR_NONCONFORMITY | Yes |
| Nonconformity (not graded as major or minor) | NC | NONCONFORMITY | Yes |
| Observation | OBS | OBSERVATION | No |
| Opportunity for improvement | OFI | OPPORTUNITY_FOR_IMPROVEMENT | No |
| Conformity | C | CONFORMITY | No |
Deadlines and reminders
A finding with a deadline appears in Deadlines until it is closed. The reminder goes to the assignee, or to every member of the assignee role. When nobody is assigned, the owners and admins get it. If the assignee role has no members, nobody is reminded.
Permissions
| Role | Audits | Findings |
|---|---|---|
| Owner, admin | Create, edit, archive, delete | Create, edit, verify, close, archive |
| Member | Read | Read |
| Auditor | Read | Read |
| Organization token | Create, edit, archive, delete over the API | Create, edit, verify, close, archive over the API |
Members can also write comments. The auditor role reads comments but cannot write them. A personal API token has the role of its owner.
Limits
On the Free plan you can keep 4 audits. Archived audits do not count, and restoring one counts again. There is no limit on findings.
Where audits appear elsewhere
- The dashboard shows the current or next audit, the open findings and how many are overdue.
- Deadlines lists every finding with a deadline that is not closed.
- Reports creates the audit report.
- The audit programme shows internal audits against the clauses of a framework.
API
- Base URL:
https://app.devguard.ch/api. All endpoints are in the API reference. - Authentication: an API token, sent as
Authorization: Bearer <token>. Send JSON withContent-Type: application/json. - Names: in the API, a finding is an
auditItem. The statement isfindings, the root cause iscausesand the corrective action ismeasures. - Scope: the API covers audits and findings. The programme, the review period and the report are in the app only. To plan the programme from a script, create audits with
typeset toINTERNAL, theframeworkId,scopeControlIds,startedandended: the programme reads them.
| Method | Path | Purpose | Organization id |
|---|---|---|---|
GET | /audits/ | List audits | query, required |
POST | /audits/ | Create an audit | body, required |
GET | /audits/{id}/ | Read an audit with its findings | not used |
PATCH | /audits/{id}/ | Update an audit | not used |
POST | /audits/{id}/archive/ | Archive an audit (/restore/ to undo) | not used |
DELETE | /audits/{id}/ | Delete an audit | not used |
GET | /audit-items/ | List findings | query, required |
POST | /audit-items/ | Create a finding | body, required |
PATCH | /audit-items/{id}/ | Update a finding | not used |
POST | /audit-items/{id}/verify/ | Record the effectiveness check | body, required |
POST | /audit-items/{id}/archive/ | Archive a finding (/restore/ to undo) | not used |
Lists return { "items": [...], "total": 12, "page": 1, "limit": 100 }. limit is 100 at most, and 100 by default. GET /audit-items/ filters with filterByStatus (OPEN, IN_PROGRESS, CLOSED), filterByType (an API value from Finding types), filterByName, auditId and filterByArchived (active or archived). On an audit, scopeControlIds takes only ids of controls of the audit's own framework. Annex A controls belong to the Annex A framework, so they go on an audit of that framework.
A single finding comes back as one object, for example from POST /audit-items/ or verify. Shortened:
{
  "id": "…", "slug": "nc-5", "identifier": "NC-5",
  "name": "Shared admin account on the firewall",
  "type": "MINOR_NONCONFORMITY", "status": "OPEN",
  "source": "AUDIT", "auditId": "…", "controlId": "…",
  "deadline": "2027-01-15T00:00:00.000Z",
  "findings": "…", "causes": null,
  "correction": null, "measures": null,
  "verifiedAt": null, "verificationNote": null
}
PATCH is not a partial update for every field. On an audit, send name and slug every time. On a finding, send name, slug and identifier every time.
This call lists the open findings. DG_TOKEN is your API token and DG_ORG is your organization id:
API=https://app.devguard.ch/api
AUTH="Authorization: Bearer $DG_TOKEN"

curl -sS -G "$API/audit-items/" -H "$AUTH" \
  --data-urlencode "organizationId=$DG_ORG" \
  --data-urlencode "filterByStatus=OPEN" \
  | jq '.items[] | {id, slug, identifier, name}'
To close a nonconformity, record the check first. Then set the status, and send the name, slug and identifier with it:
curl -sS -X POST "$API/audit-items/$ID/verify/" \
  -H "$AUTH" -H "Content-Type: application/json" \
  -d "{\"organizationId\":\"$DG_ORG\",\"note\":\"Sample OK\"}"

curl -sS -X PATCH "$API/audit-items/$ID/" \
  -H "$AUTH" -H "Content-Type: application/json" \
  -d '{"name":"Shared admin account on the firewall",
       "slug":"nc-5","identifier":"NC-5",
       "status":"CLOSED"}'
verify replaces an earlier check on the same finding.
| Code | When |
|---|---|
400 | A slug is already in use, or a required field is missing. |
400 | A linked id (audit, control, role, framework, scope control) is not in your organization, or not in the audit's framework. |
400 | A nonconformity raised from an incident or a submission has no deadline. |
400 | A finding has both an assignee and an assignee role. |
400 | The review period ends before it starts, or is longer than 18 months. |
403 | The id belongs to another organization (verify answers 404), your role cannot write, or the audit plan limit is reached (also on restore). |
404 | The audit or the finding does not exist. |
412 | A nonconformity would be closed, or created as closed, without a verification. |
How is this guide?
Processes
Turn your checklists and report forms into processes your people fill in, handle the reports they file, and keep each submission as a dated record for your auditor.
Audit programme
Plan your internal audits so that they cover the clauses of a framework over the certification cycle, and see the gaps before the cycle ends.