Coverage
See how much of each adopted framework your controls cover, find the controls that still need work, and set the level each control should reach.
Use Coverage to find the controls that nothing covers yet, before an auditor does. The page lists every control of the frameworks you have adopted, with its coverage status: Full, Partial, None, Unknown or Not applicable. At the top, a summary shows the share of controls that are covered.
You do not set coverage on this page. You link policies, risks, assets, vendors and evidence to a control, and you assess it on the control's page. This page collects the result. The tasks below follow the order of the work:
- Read your coverage
- Find the controls that need work
- Exclude controls that do not apply
- Cover a control
- Set a target coverage
Scripts and integrations: see API below.
Read your coverage
- Open Coverage.
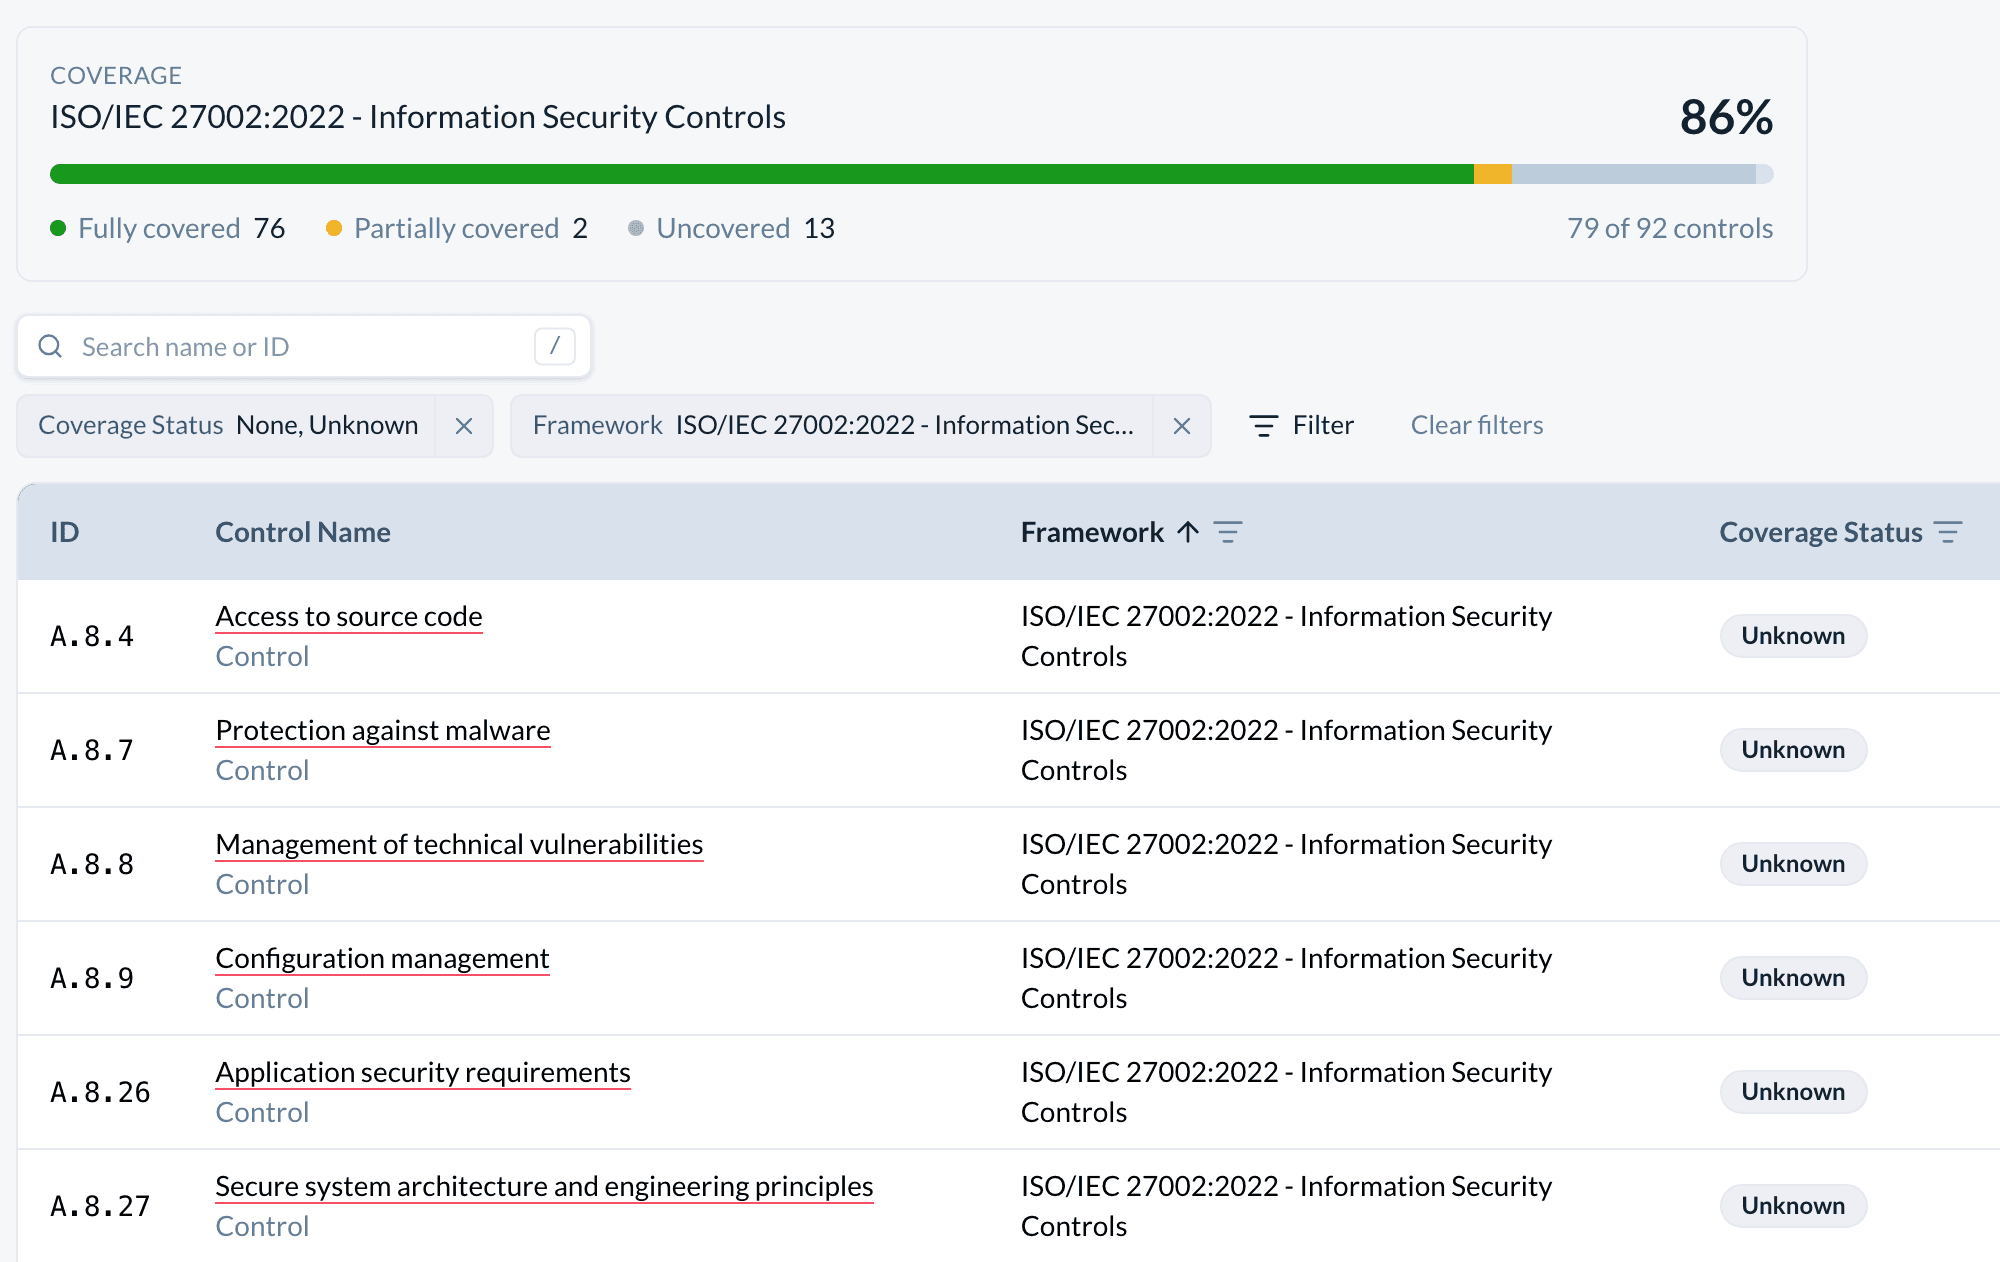
- Read the summary at the top. It shows the percentage of covered controls and a bar with Fully covered, Partially covered, Covered only through a mapping and Uncovered. On the right, it shows how many controls are covered, for example "79 of 92 controls".
- To see one framework, choose Framework and select it. The summary then counts only that framework.
The summary follows only the Framework filter. The other filters change the list, not the summary. A control covered indirectly counts as covered and appears under Covered only through a mapping. In the list, the same control shows the status Partial, so the Partial filter can return more controls than Partially covered counts. How coverage is counted explains what counts as covered. It also explains why a framework lists more entries than it counts.
Find the controls that need work
- Choose Coverage Status and select None and Unknown. The list now shows only the controls that nothing covers yet.
- Choose Framework to work on one framework at a time.
- To start with the required controls, open Filter, choose Mandatory and select Yes.
- Type in Search name or ID to find one control, for example
A.8.13. - Choose the control's name to open it.
To keep this list, save it under Views. The Mapped and Unmapped figures on the dashboard open this page with the matching filter.
A Partial status with a link icon means that the control is covered indirectly, through a control in another framework. Such a control is not in the None and Unknown list. See Columns.
Exclude controls that do not apply
Some controls do not apply to your organization. For example, a company that develops no software has no secure coding to show. Exclude such a control with a justification. It then leaves the coverage figures, and the Statement of Applicability prints the justification for the auditor.
- Open the menu (⋯) at the end of the control's row.
- Choose Mark as not applicable.
- Write the Justification and confirm with Mark as not applicable.
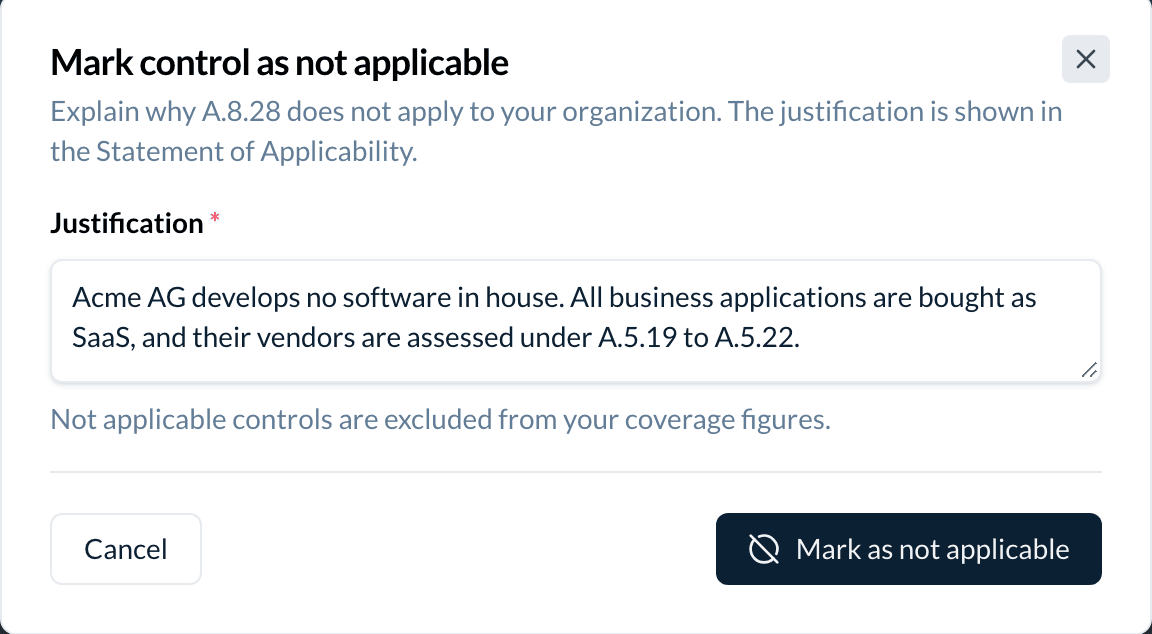
The status changes to Not applicable. To list all excluded controls and check their justifications, choose Coverage Status and select Not applicable. To undo an exclusion, choose Mark as applicable in the same menu. The same steps are described for the control's page in Mark a control not applicable.
CIS Controls: exclude a whole Implementation Group
In CIS Controls, each safeguard belongs to an Implementation Group: IG1, IG2 or IG3. If you aim for IG1, you can exclude the IG2 and IG3 safeguards in one step.
- Choose Framework and select only CIS Controls. The Implementation Group filter appears under Filter.
- Select the groups above your target. For IG1, select IG2 and IG3. Remove all other filters and the search, because the step marks every control in the list.
- Choose Mark not relevant… in the toolbar.
- Keep or change the Reason. It is filled in, for example "Outside the targeted Implementation Group (IG1)".
- Confirm with the button that names the number, for example Mark 18 controls.
Each safeguard gets the reason on its own, so you can still change it per control later. Safeguards that were already excluded keep their own reason.
Cover a control
Coverage comes from the control's links and from your assessment. Both are set on the control and on the linked records, not here.
- Choose the control's name to open it.
- Link the policy section, risk, asset or vendor that implements it, or attach evidence. The control becomes Partial. See Link the records that implement a control.
- When the control is fully implemented, assess it as Full on the mapping card. See Assess a control as Full.
- Return to Coverage. The control leaves the None and Unknown list.
Only a person can set Full. Links alone never go beyond Partial.
Set a target coverage
A target is the coverage a control should reach, for example the target profile of a framework. Targets are optional.
- Choose View and turn on the Target column.
- In the Target column, choose Full Coverage, Partial Coverage or No Coverage for each control. Not set removes the target.
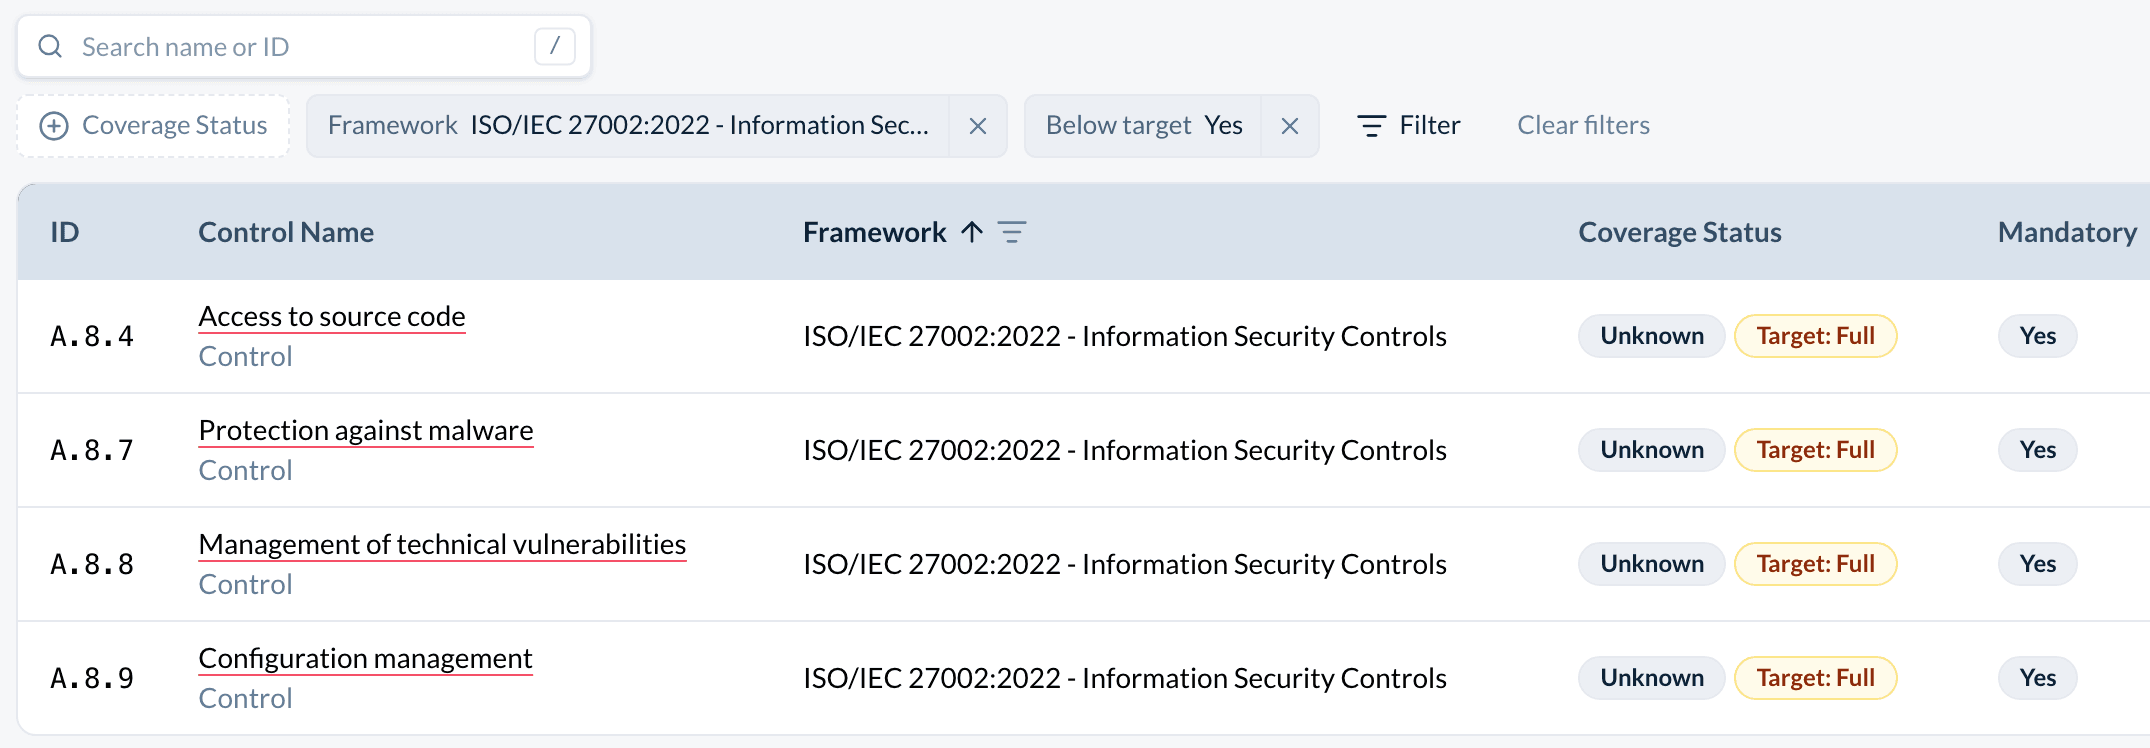
- To list the controls that have not reached their target yet, open Filter and turn on Below target.
A control without a target never appears under Below target. While the Target column is hidden, a control below its target shows a badge next to its status, for example Target: Full.
Reference
Columns
| Column | Content |
|---|---|
| ID | The control's identifier. Opens the framework's roadmap. |
| Control Name | The name and the control type. Opens the control. |
| Framework | The framework the control belongs to. |
| Coverage Status | Full, Partial, None, Unknown or Not applicable. A link icon marks indirect coverage. |
| Target | Hidden by default. The target coverage, see Set a target coverage. |
| Mandatory | Whether the framework requires the control. |
| Linked Items | Linked policies (with the section), assets, risks and cross-linked controls. Linked vendors and evidence count too, but show only on the control's own page. |
What each status means is defined in Coverage status on the Controls page.
Indirect coverage: the control has no coverage of its own, and a cross-linked control in another framework raises its status to Partial. Hover over the link icon to see which controls give the coverage. When a cross-link counts is explained in Cross-link controls.
Filters
| Filter | Values |
|---|---|
| Coverage Status | Full, Partial (indirect coverage included), None, Unknown, Not applicable |
| Framework | Your adopted frameworks |
| Mandatory | Yes, No |
| Implementation Group | IG1, IG2, IG3; shown only when the list is filtered to CIS Controls alone |
| Below target | Controls whose status is below their target |
The filters are part of the page address, so you can share a filtered list as a link.
Permissions
| Action | Owner, admin | Member | Auditor |
|---|---|---|---|
| See coverage and the summary | yes | yes | yes |
| Mark controls not applicable or applicable | yes | no | no |
| Set a target | yes | no | no |
An organization token may do over the API what an admin may, including these coverage changes. It can only read tokens, members, organization settings and billing. A personal API token acts with the role of its owner.
Where coverage shows up
- The Compliance Health card on the dashboard shows the same figures, and its Mapped and Unmapped links open this page.
- Each framework shows its own percentage, see Frameworks.
- The Statement of Applicability lists each control with its status and the justification of each exclusion.
- The Roadmap splits each framework into Full, Partial and Open.
API
- Base URL:
https://app.devguard.ch/api. - Authentication: an API token, sent as
Authorization: Bearer <token>. - Scope: the API returns coverage per framework. The control-by-control list of this page is in the app only. To read single controls with their status, use
GET /controls/on the Controls page.
| Call | Endpoint | Organization id |
|---|---|---|
| Coverage per framework | GET /coverage/adoptions/ | query, required |
| Assess a coverage row | PATCH /control-coverage/status/ | body, required |
| Set a target | PATCH /control-coverage/target/ | body, required |
| Exclude or restore one control | PATCH /control-coverage/not-relevant/ | body, required |
| Exclude several controls | PATCH /control-coverage/not-relevant/bulk/ | body, required |
The bodies of the PATCH calls are described on the Controls page.
GET /coverage/adoptions/ returns one entry per adopted framework, newest adoption first. Each entry has the adoption, the framework and coverageStats. Besides frameworkId and frameworkAdoptionId, coverageStats holds:
| Field | Content |
|---|---|
totalControls | The scored controls, without the excluded ones |
coveredControls | Full, Partial and indirectly covered controls |
fullyCoveredControls | Controls with the status Full |
partiallyCoveredControls | Controls with the status Partial of their own |
indirectlyCoveredControls | Controls covered only through a cross-link |
uncoveredControls | totalControls minus coveredControls |
notRelevantControls | The excluded controls |
coveragePercentage | coveredControls of totalControls, rounded to a whole number |
fullyCoveredControls, partiallyCoveredControls and indirectlyCoveredControls add up to coveredControls.
This call prints the percentage of each framework. DG_TOKEN is your API token and DG_ORG is your organization id:
API=https://app.devguard.ch/api

curl -sS -G "$API/coverage/adoptions/" \
  -H "Authorization: Bearer $DG_TOKEN" \
  --data-urlencode "organizationId=$DG_ORG" \
  | jq '.[] | {name: .framework.name,
      pct: .coverageStats.coveragePercentage}'
A call without a valid token gets 401. A token of another organization gets 403 ("No membership found"). Errors return as { message, code, status }; a 400 adds issues.
How is this guide?