Automations
Let devguard check your tools on a schedule and keep the evidence current, and open recurring tickets in GitHub, GitLab, Jira, Asana or Slack.
Automations does two kinds of recurring work for you. A check reads a setting in one of your tools on a schedule. For example, it tests whether www.example.com redirects to HTTPS. It writes the result into an evidence record, so the proof for a control stays current without a screenshot. A ticket rule opens a ticket in GitHub, GitLab, Jira or Asana, or posts a Slack message, on a schedule. A person then does the work, such as a quarterly access review.
Use a check when the proof is a setting in a tool. Use a ticket rule when the proof is that a person did something.
The tasks below follow the order of the work:
- Enable a check from the catalog
- Read what a check found
- Act on a failed check
- Change, pause or remove a check
- Create a ticket rule
- Follow the tickets
When the catalog has no check for what you need, build your own check. The tools themselves are connected under Integrations. Scripts and integrations: see API below.
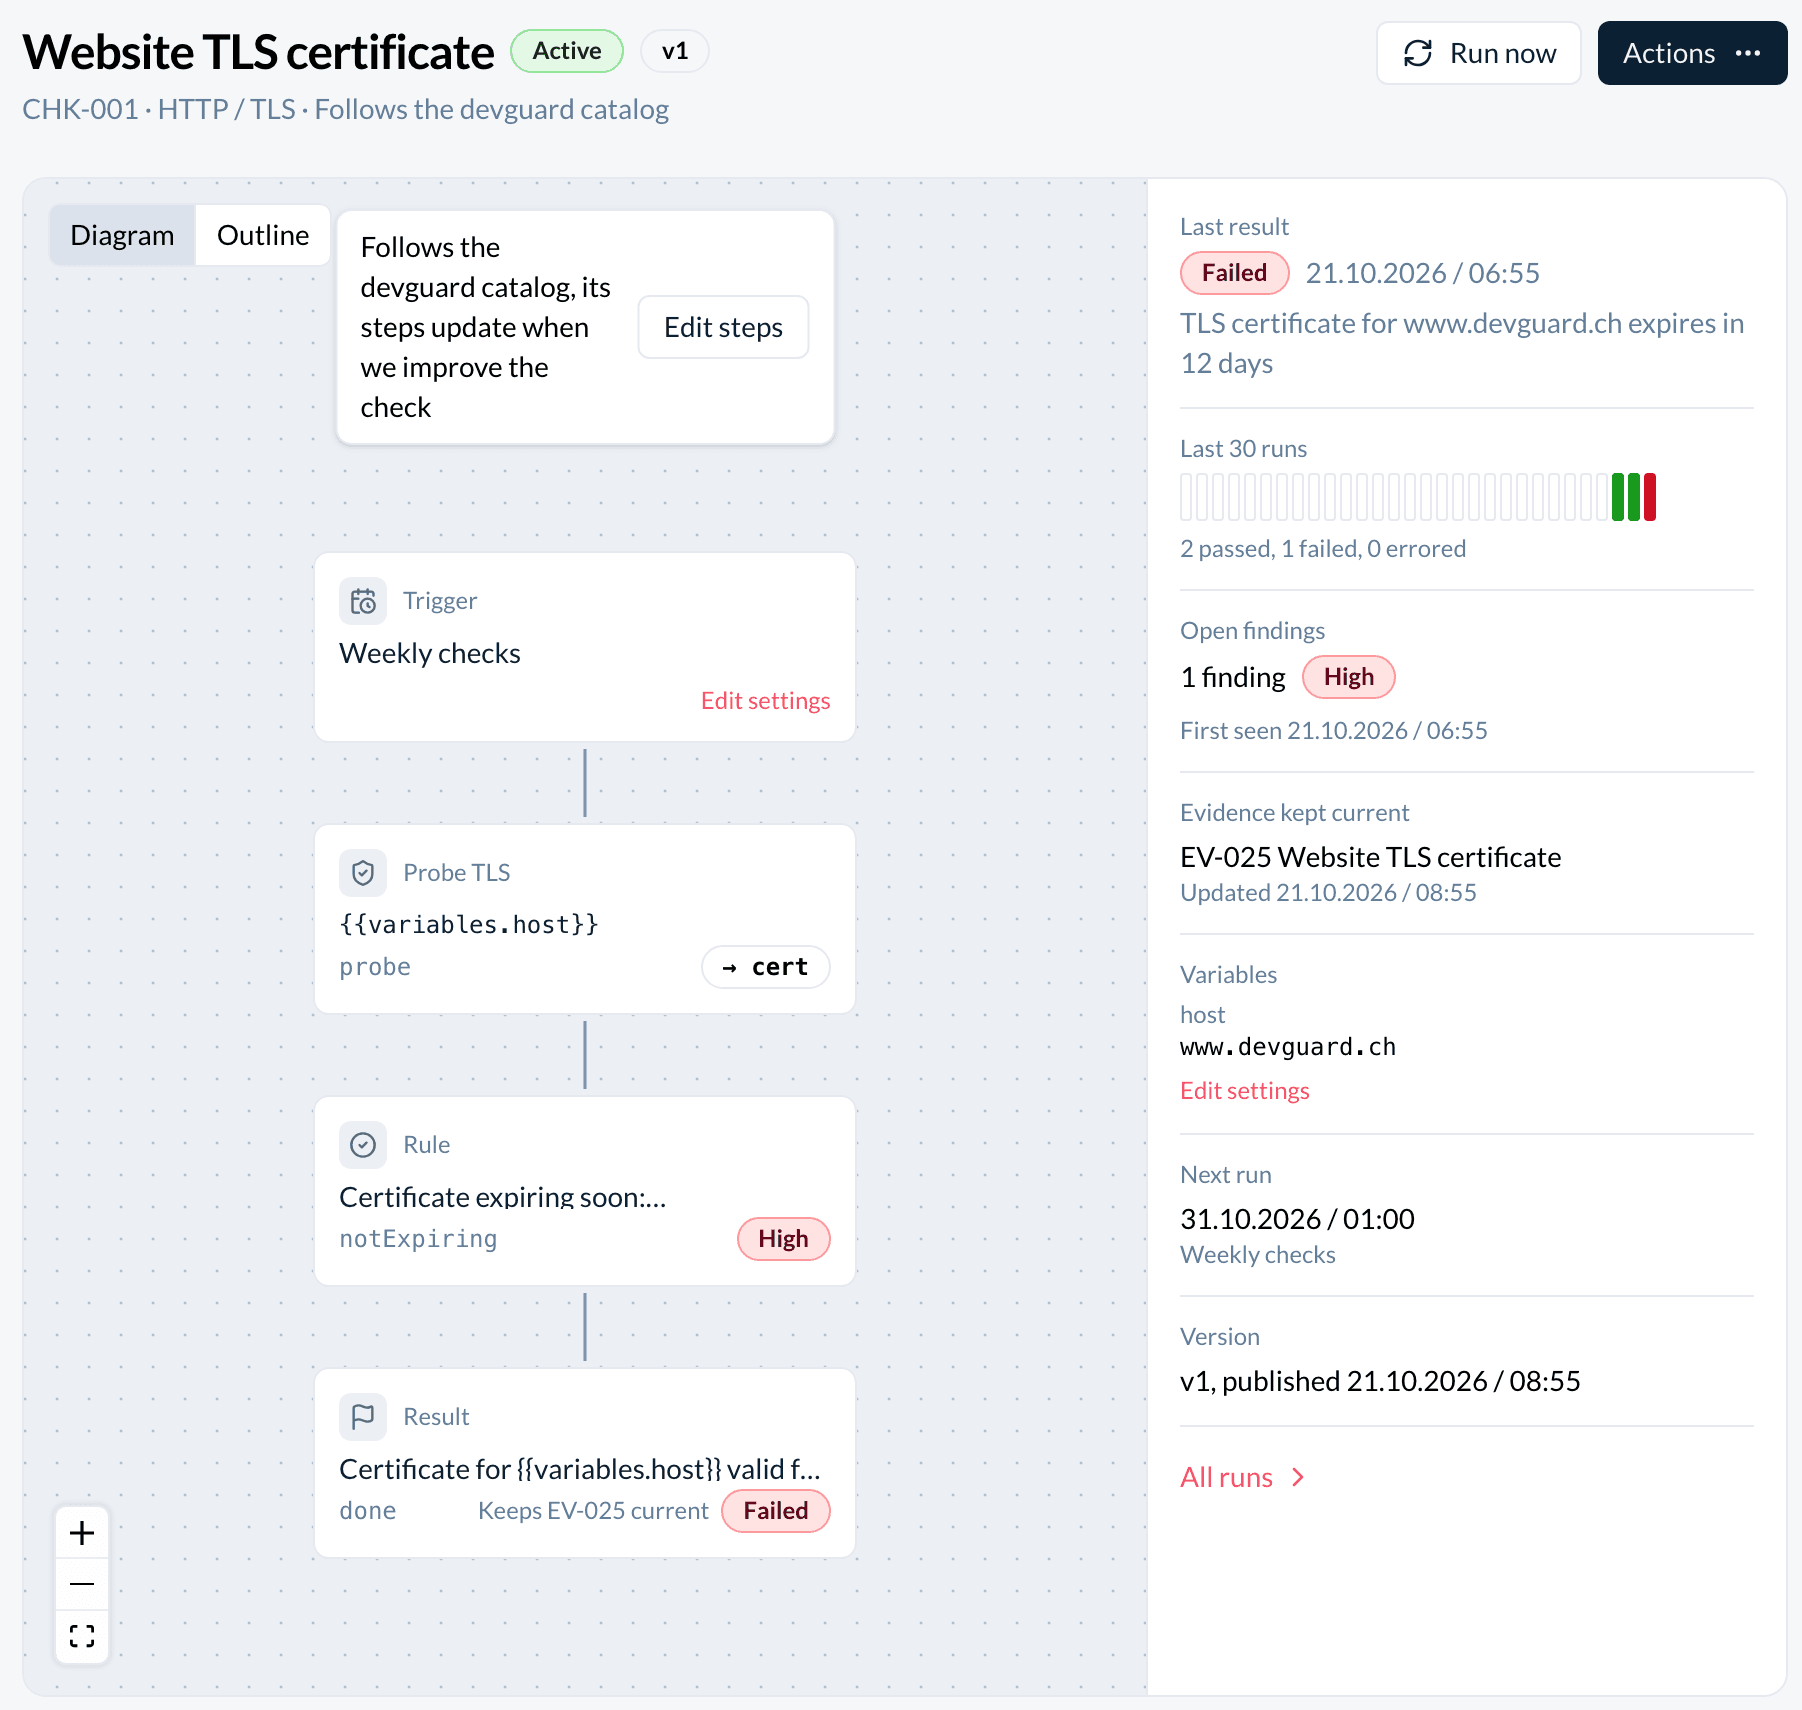
Enable a check from the catalog
The catalog lists every check that devguard provides, grouped by category. Most checks need a connection to the tool first. Connect it under Integrations. The HTTP / TLS checks need no connection: they test web addresses that you name. Neither do the devguard Devices checks: they read the devices enrolled on Devices.
- Open Automations and choose New automation, then From the catalog.
- Type the tool or the topic into Search integrations and checks. Each card shows a tool and the names of its checks.
- Choose a check. The Enable panel opens on the right.
- Keep or change the Check name. It is also the title of the evidence record.
- Fill in the variables that the check asks for, such as the domains to test. A list takes one entry per line. Commas also work.
- If the panel shows Credential, choose the connection the check uses.
- Choose a Schedule. Every check needs one. Schedules are kept under Collections → Schedules.
- Choose the Owner and the Approver of the evidence record. Both are business roles.
- Choose Enable check. The check opens and is Active. It runs at the next time in its schedule.
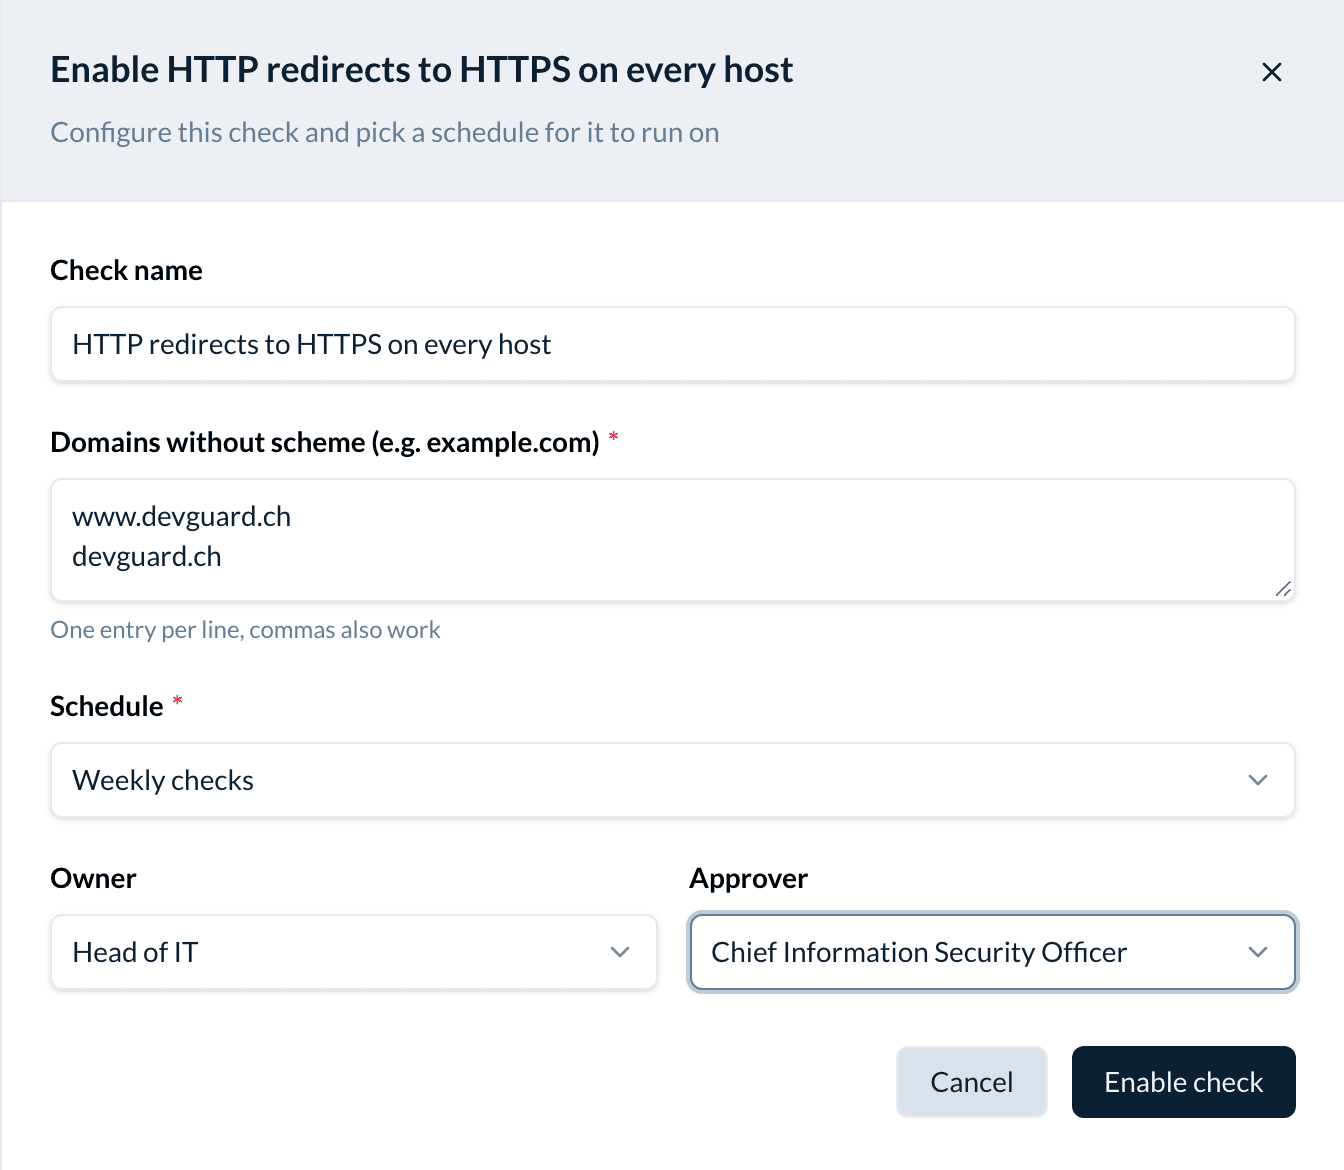
Enabling also creates the evidence record, with the status To do. Link that record to the controls it proves, on the record's Evidence tab. See Link it to controls.
Read what a check found
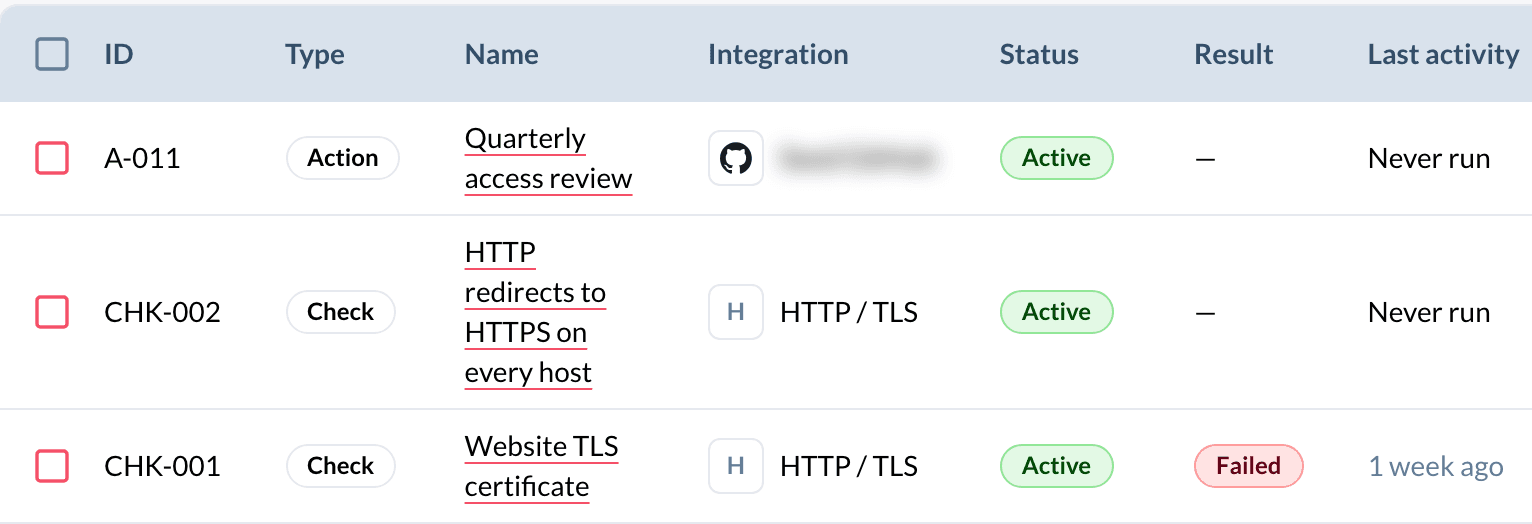
The Automations list shows checks and ticket rules together. For a check, Result shows how its last run ended.
Open the check from the list. The left side shows the steps of the check, from the Trigger (the schedule) to the Result. Switch between Diagram and Outline at the top left. The panel on the right shows how the check is doing: Last result, Last 30 runs, Open findings, Evidence kept current, Variables, Next run and Version.
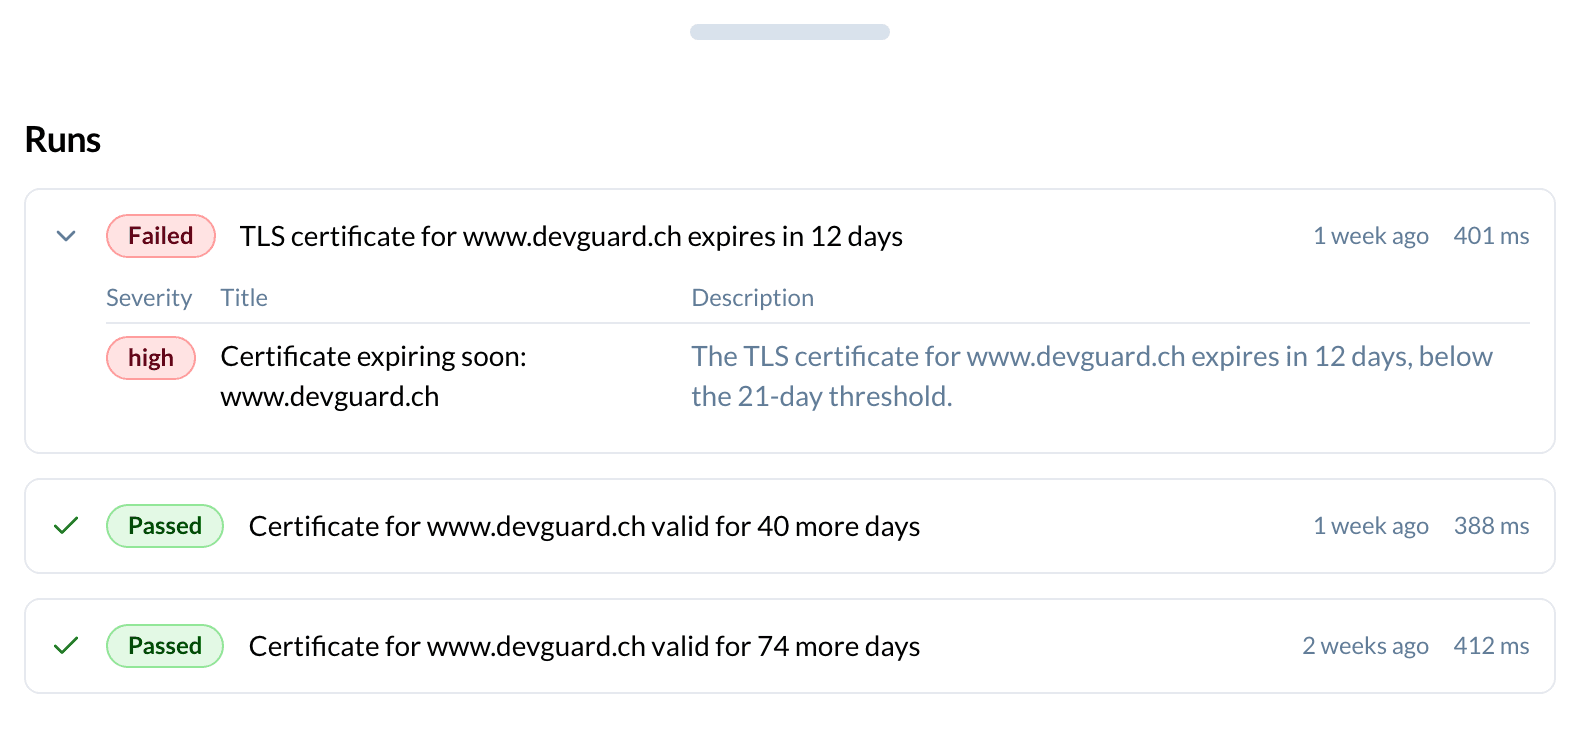
A finding is one problem that a run found, with a severity: critical, high, medium, low or info. To see each run, choose All runs. The Runs panel lists each run with its result, its age and its duration. Open a failed run to see its findings. If the run kept data as proof, the data is below the findings, as JSON. For example, it lists the users that a finding is about. On a run that did not fail, choose Show data to see it. Copy and Download give you the complete data. Show logs shows the lines that the run logged instead.
Act on a failed check
- Open the check and read the finding under Open findings or in All runs.
- Fix the problem in the tool itself. For example, renew the certificate.
- Choose Run now. This is a real run. When it passes, the evidence record goes back to Done. Run now works only on an active check that is not archived.
If the check is Unhealthy, fix the cause first. Often a key has expired or was revoked: reconnect it. Or a variable is wrong: choose Edit settings on the right and correct it. Then choose Run now.
How a check keeps evidence current
Each run ends with one of three results. Only two of them change the evidence.
| Result | What it means | What happens to the evidence record |
|---|---|---|
| Passed | Every rule of the check held. | Status Done. Last reviewed is today. The next review is the next run plus three days. If the check saves what it read, devguard attaches it to the record as a file, in place of the previous one. |
| Failed | At least one rule did not hold. | Status Failed. The active members of the owner role are notified when the check starts to fail. |
| Errored | The check could not finish, for example because the key was refused or the site did not answer. | No change. A run that could not finish says nothing about the control. |
So a passing run counts as a review of the record. Nobody has to approve it again each week. An auditor sees in the record when the check last passed, and the file it read.
When a check errors three times in a row, it gets the Unhealthy badge. The members of the evidence owner role get the notice "Check needs attention", in the app and by email if they turned email on. The problem is then the connection or the address, not the control. The badge goes away with the next run that passes or fails.
Change, pause or remove a check
| To | Do this |
|---|---|
| Change the name, variables, connection or schedule | Choose Edit settings on the check, or Actions, then Edit. The next run uses the new settings. |
| Pause the check | Choose Actions, then Deactivate. The check stops running. Its evidence and history stay. Activate starts it again. |
| Retire the check | In the list, open the row menu and choose Archive. The check stops and leaves the list, the dashboard and search. Its runs and evidence stay. Archived above the list shows it again, and Restore brings it back. |
| Delete the check | Choose Actions, then Delete. This removes the check and its runs. The evidence record and its files stay. |
devguard updates the checks in its catalog. Your check gets each update until you publish your own version of its steps. See Build your own check.
Create a ticket rule
A ticket rule needs a connection to GitHub, GitLab, Jira, Asana or Slack. Connect it under Integrations first. The Integration field lists only these connections.
- Choose New automation, then Create ticket rule. The Create ticket rule panel opens on the right.
- Enter a Name, such as "Quarterly access review". It becomes the ticket title.
- Choose a Schedule. Without a schedule, the rule never runs by itself.
- Choose the Integration. More fields appear for that tool, for example Repository, Assignees and Labels for GitHub. See Fields for each tool.
- In Template content, write what the person must do. You can use Markdown.
- Leave Status on Active and choose Create.
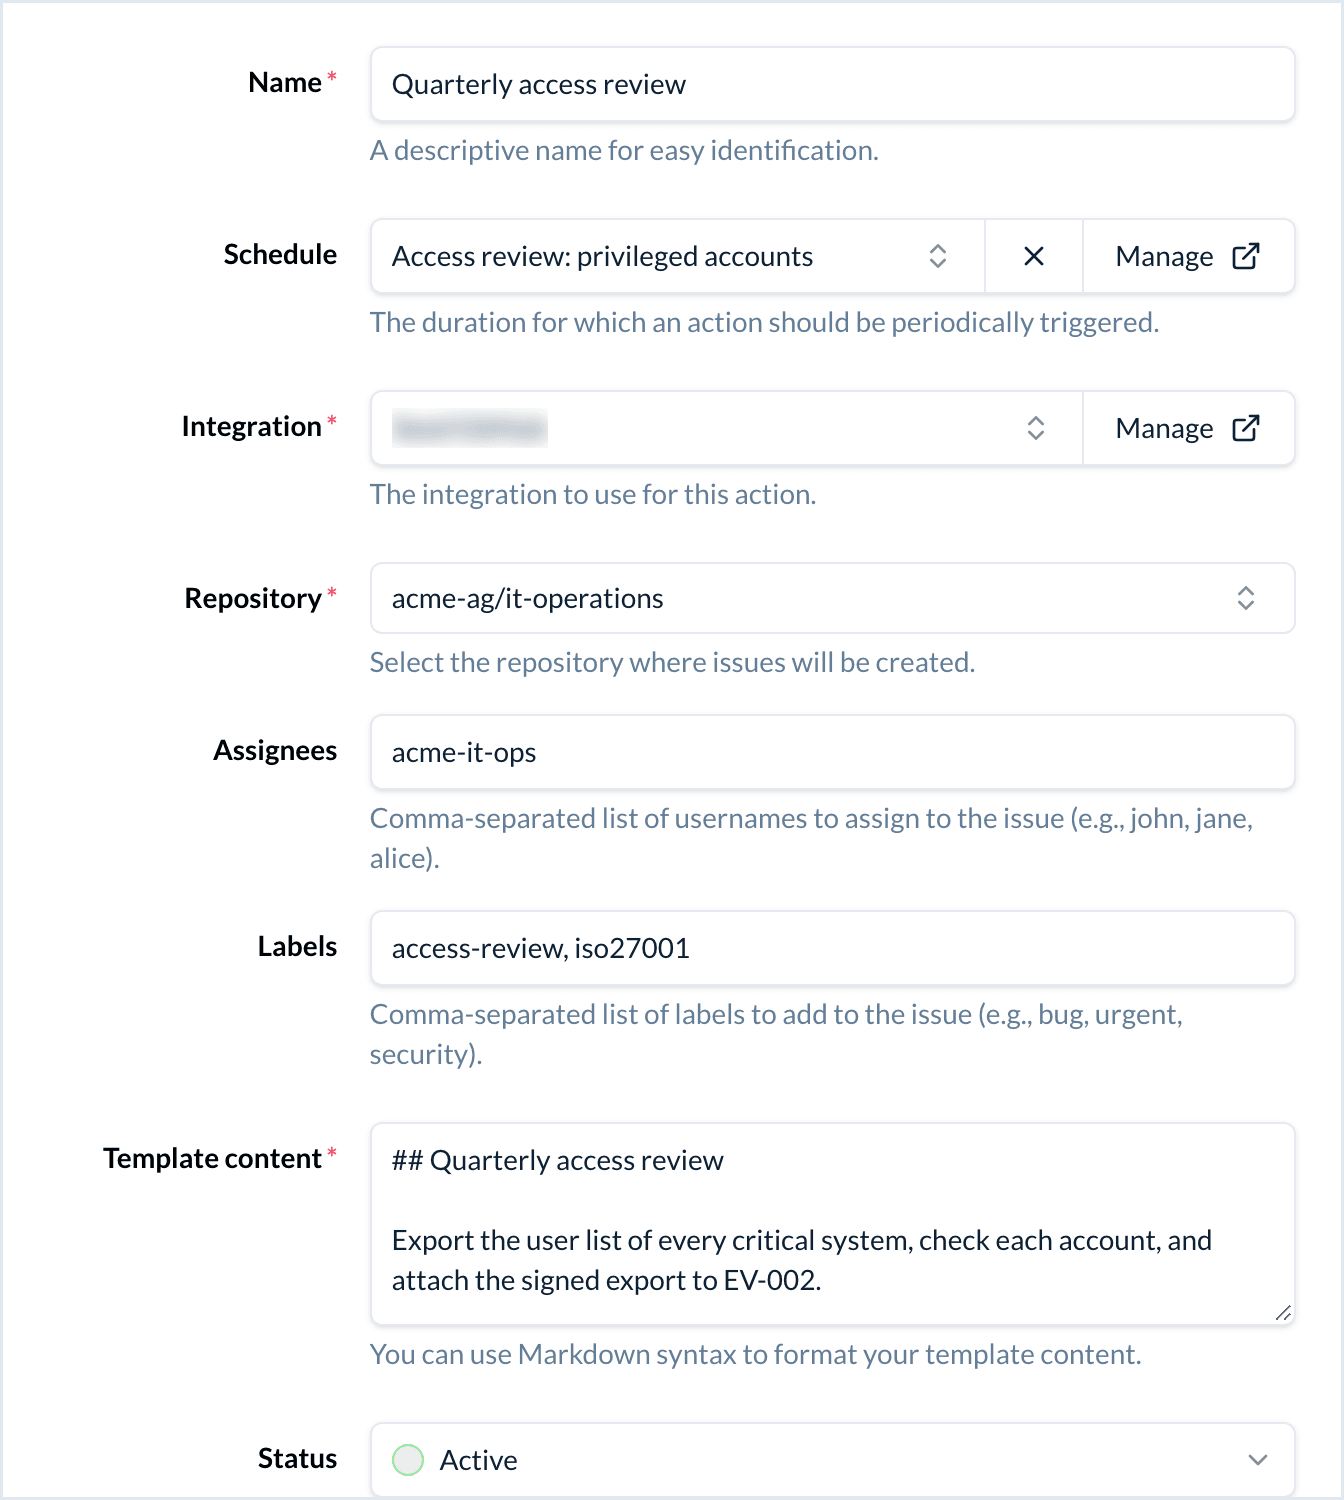
On each date in the schedule, devguard opens one ticket. The title is the rule number, a running number and the name, for example "A-011-1 Quarterly access review". GitHub and GitLab issues also get the label devguard. devguard opens at most one ticket between two dates of the schedule. On the next date it opens a new ticket, even if the last one is still open.
Follow the tickets
- Open the rule. The Detail tab shows the newest tickets under Recent Tickets.
- Open the Tickets tab to see all of them, with their status: Open, In progress or Closed. A task deleted in Asana, or a Jira issue in a status such as Cancelled, Rejected, Won't do or Duplicate, shows the status
CANCELLED. - When someone closes the issue in GitHub, GitLab, Jira or Asana, the status changes here too.
Watch out: closing a ticket does not change any evidence record. When the work produces proof, such as a signed export, attach it to the evidence record yourself. You can link the record on the rule's Evidence tab.
To open a ticket now, outside the schedule, choose Trigger Manually in the row menu of the list. This works for active and inactive rules, but not for archived ones. An inactive rule opens no tickets on its schedule.
Deleting a rule also deletes its ticket list in devguard. The issues in the tool stay.
Reference
The list
| Column | Shows |
|---|---|
| ID | CHK-001 for a check, A-001 for a ticket rule. |
| Type | Check or Action. Action means a ticket rule. |
| Integration | The tool or the connection, such as HTTP / TLS or devguard Devices. |
| Status | Active, Inactive or Draft. |
| Result | For a check, the last result. For a ticket rule, its tickets or an error. |
| Last activity | The last run or ticket, or Never run. |
| Schedule | The schedule, or a dash. |
Filter with Type, Result and Filter (status, schedule, date created). Archived shows archived rows. Select rows to archive, restore or delete them together.
Check statuses
| Status | Meaning |
|---|---|
| Active | Runs on its schedule and writes evidence. |
| Inactive | Paused. Keeps its evidence and history. |
| Draft | Not running yet. Only checks you build start as drafts. See Build your own check. |
A check can also show Unhealthy (three errors in a row) and Archived.
Fields for each tool
| Tool | Fields after you choose the integration |
|---|---|
| GitHub | Repository (required), Assignees (GitHub user names, separated by commas), Labels |
| GitLab | Project ID (required, the path or the number), Assignees, Labels |
| Jira | Project ID (required, the project key), Issue type (required), Assignee (email or display name), Labels, Priority |
| Asana | Project ID (required, the number in the project address), Assignee |
| Slack | Channel (required) |
If Jira cannot assign the ticket, it still creates it without an assignee, and the rule shows a warning. A Slack message stays Open, because Slack sends no status back.
In Template content, these placeholders are filled in when the ticket is created. Spaces inside the braces are allowed, as in {{ action.name }}. A template with any other placeholder is not saved.
| Placeholder | Becomes |
|---|---|
{{action.name}}, {{actionName}} | The rule name |
{{action.shortId}}, {{actionId}} | The rule number |
{{organization.id}}, {{organizationId}} | Your organization's ID |
{{schedule.name}} | The schedule name, or Manual without a schedule |
{{policies}}, {{risks}}, {{assets}} | The names of all linked policies, risks or assets, separated by commas, or None |
{{policy.name}}, {{policy.slug}} | The title and slug of the first linked policy |
{{risk.name}}, {{risk.description}} | The name and description of the first linked risk |
{{asset.name}}, {{asset.description}} | The name and description of the first linked asset |
Permissions
| Role | Checks | Ticket rules |
|---|---|---|
| Owner, admin | Enable, build, edit, run, archive, delete | Create, edit, trigger, archive, delete |
| Member, auditor | Read | Read |
| Employee | No access | No access |
| Organization token | Full access over the API | Full access over the API |
Members can comment on a ticket rule. Auditors can read the comments.
Limits
| Plan | Ticket rules | Active checks |
|---|---|---|
| Free | 4 | 1 |
| Business | No limit | No limit |
Archived ticket rules do not count. Only active checks count, so a paused check does not. When you reach a limit, the buttons in New automation show Limit reached. Restoring a rule or an active check also counts. Describe it to AI needs a Business plan.
Import and export
The menu at the top right of the list has Import CSV, Download CSV template and Export all. These cover ticket rules only, not checks. The import and the template use the columns name, integrationCredentialId, externalTicketConfiguration, scheduleId, template and status. The export also includes ids and dates.
Where automations appear
| Place | What it shows |
|---|---|
| Evidence | Each check keeps one evidence record current. |
| Dashboard | Active checks whose last run failed or errored, in the Compliance Scan card. |
| Notifications | "Check failed" and "Check needs attention", sent to the evidence owner role. |
| Search | Checks and ticket rules, by name or ID. |
| AI assistant | Lists your checks and the catalog, and helps you set up a check. |
| Audit log | Creating, changing, running and deleting. Each ticket rule also has a History tab. |
| Schedules | A schedule that an automation uses cannot be deleted. |
API
- Base URL:
https://app.devguard.ch/api. - Authentication: an API token, sent as
Authorization: Bearer <token>. Send JSON withContent-Type: application/json. - Scope: the API covers ticket rules, enabling catalog checks, status, archiving and running. Building and editing check steps is in the app only.
Ticket rules (in the API, actions):
| Call | Endpoint | Organization id |
|---|---|---|
| List | GET /actions/ | query, required |
| Create | POST /actions/ | body, required |
| Read | GET /actions/{id}/ | not used |
| Update | PATCH /actions/{id}/ | not used |
| Delete | DELETE /actions/{id}/ | not used |
| Archive | POST /actions/{id}/archive/ | not used |
| Restore | POST /actions/{id}/restore/ | not used |
Checks:
| Call | Endpoint | Organization id |
|---|---|---|
| List | GET /integration-checks/ | query, required |
| Enable from the catalog | POST /integration-checks/ | body, required |
| Read by number | GET /integration-checks/{shortId}/ | query, required |
| Activate or deactivate | POST /integration-checks/{id}/status/ | body, required |
| Archive | POST /integration-checks/{id}/archive/ | body, required |
| Restore | POST /integration-checks/{id}/restore/ | body, required |
| Run now | POST /integration-checks/{id}/run/ | body, required |
{id} is the record's id. {shortId} is the number: CHK-001 is shortId 1. GET /actions/ returns { "items": [...], "total": <number>, "page": 1, "limit": 100 }. GET /integration-checks/ returns a plain list. Add filterByArchived=archived to either list to get archived rows.
To enable a check, send the catalogCheckId, a scheduleId and, if needed, name, variableValues, integrationCredentialId, ownerId and approverId. There is no REST endpoint for the catalog. Take catalogCheckId from a check you enabled in the app, or ask the AI assistant to list the catalog. The status call takes ACTIVE or INACTIVE. Activating fails when the schedule, a required variable or a required connection is missing. variableValues takes only the variables the check declares: a number for a number, true or false for a yes/no, one of the listed values for a choice.
externalTicketConfiguration holds the fields of the tool, as JSON. assignees and labels are one string with commas, not a list.
| Tool | Keys |
|---|---|
| GitHub | owner and name of the repository (required), assignees, labels |
| GitLab | projectId (required), assignees, labels |
| Jira | projectKey and issueType (required), assignee, labels, priority |
| Asana | projectGid (required, digits only), assignee |
| Slack | one of channelId, channel (an object with id and name) or defaultChannel (required) |
The API has no endpoint for runs or findings. POST /integration-checks/{id}/run/ only queues the run. To get the result, read the check again with GET /integration-checks/{shortId}/ until lastRunAt changes, then read lastVerdict.
To create a ticket rule for GitHub, send the whole rule. PATCH /actions/{id}/ needs name, integrationCredentialId and template every time, even when they do not change. Fields you leave out (externalTicketConfiguration, scheduleId, status) keep their values. The API reference marks externalTicketConfiguration as required, so send it too, as in the example below, to be safe.
{
  "organizationId": "<organization id>",
  "name": "Quarterly access review",
  "integrationCredentialId": "<connection id>",
  "scheduleId": "<schedule id>",
  "status": "ACTIVE",
  "template": "Export the user list and attach it to EV-002.",
  "externalTicketConfiguration": {
    "owner": "acme-ag",
    "name": "it-operations",
    "assignees": "acme-it-ops",
    "labels": "access-review, iso27001"
  }
}
Take the connection id from integrationCredentialId of an existing rule in GET /actions/, and the schedule id from GET /schedules/.
curl -s -X POST \
  -H "Authorization: Bearer $DG_TOKEN" \
  -H "Content-Type: application/json" \
  -d "{\"organizationId\": \"$ORG_ID\"}" \
  "https://app.devguard.ch/api/integration-checks/$CHECK_ID/run/"
Errors return { "message": ..., "code": ..., "issues": [...] }. A member's or auditor's token gets 403 on every write. An id from another organization returns 403, and an id that does not exist returns 404.
How is this guide?
CLI and API
Use the devguard CLI to upload the output of your checks into evidence records on a schedule, or call the Evidence API directly from your own scripts.
Build your own check
Write a check that the catalog does not have, with the AI or step by step, test it, and publish it so it keeps an evidence record current.