Settings
Set your organization's name, logo and sign-in rules, check its plan, export its data, and hand it over or delete it.
Organization Settings is where you manage your organization as a whole. Here you set its name and logo, the sign-in rules for members, the plan, the branding and the employee portal. Owners and admins change these settings. Members and auditors can read most of them.
The tasks below follow the order in which a new organization usually needs them:
- Set the name and logo
- Set the time zone
- Require two-factor authentication
- Turn AI or the calendar feed on or off
- Brand your reports and vendor pages
- Choose what employees see in the portal
- Check your plan and usage
- Export all data
- Hand over or delete the organization
Scripts and integrations: see For developers below.
Set the name and logo
The name and the logo appear in the app, on the cover of each report PDF and in the employee portal.
- Open Settings in the sidebar. The Settings tab opens.
- Choose Upload and pick an image. devguard crops it to a square of 200 x 200 pixels, so use a square image of at least that size.
- Next to Organization Name, choose Edit, type the name and save. The name needs 2 to 255 characters.
- To give support or a script your organization's id, choose Copy next to Organization UUID.
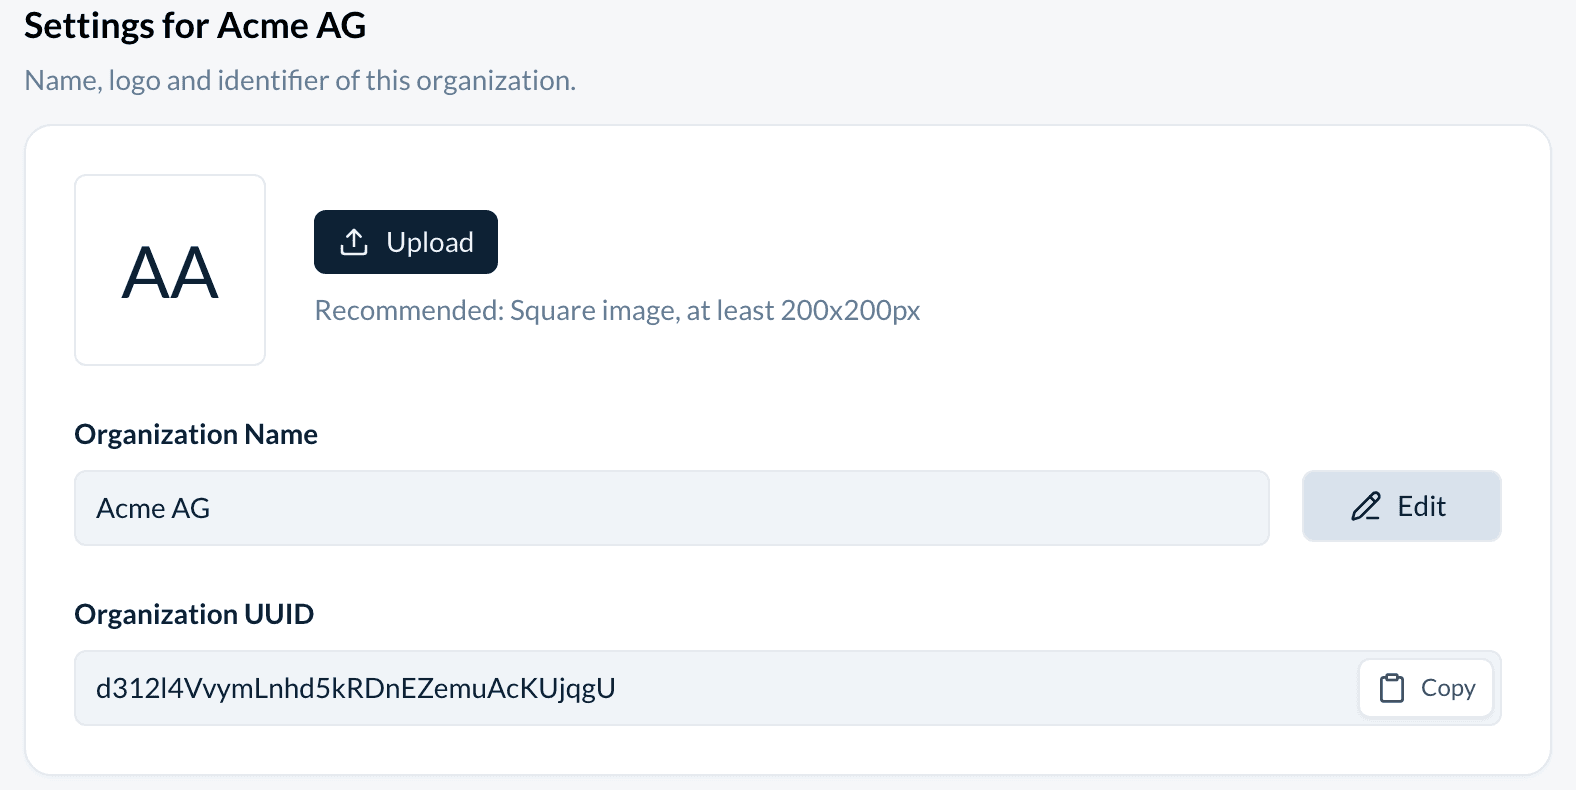
This square logo is the organization's icon. A wide logo for reports and vendor pages goes on the Branding tab.
Set the time zone
The time zone decides which day it is for your organization. A due date turns overdue when that day has passed in this zone, and a schedule's time of day falls on this clock. The zone applies to everyone in the organization, wherever they work. It is Europe/Zurich until you change it.
- On the Settings tab, find Time zone.
- Open the list, type part of a city or region name to search, and pick the zone.
- Choose Save. A message confirms it. Nothing changes until you save.
Members and auditors see the zone but cannot change it. Changing it is written to the audit log.
How organization settings differ from your account
An organization is one company's compliance work, with its own members, data and plan. Your account is you: your profile, your sign-in, your notification preferences and your personal API tokens. With one account you can belong to several organizations.
Everything on this page applies to the organization you have open. Your own settings are under Account, the link at the right end of the tab bar.
To start another organization, for example for a second company, open Account, then Organizations, and choose Create Organization. You become its owner, and it has its own plan. You can create one as long as you belong to fewer than 5 organizations yourself. Organizations you reach through a mandate do not count. Joining by invitation has no limit, and the managers of a mandate have no limit either.
Require two-factor authentication
With this setting on, devguard checks the sign-in behind every request to the organization, from the browser, a personal token or a connected app. A member without two-factor authentication must set up an authenticator app first. A sign-in through Google, Microsoft or Apple or with a passkey already carries a second factor and meets the requirement. So does a sign-in through the organization's own single sign-on, in this organization only. You can turn it on only when your own sign-in meets it, so the setting never locks you out.
- If you have not done so yet, turn on two-factor authentication for your own account, or sign in through Google, Microsoft or Apple or with a passkey. See Protect your sign-in.
- On the Settings tab, go to Security and turn on Require Two-Factor Authentication.
- Leave Allow trusted devices on if members may tick Trust this device at sign-in. That browser then skips the code for 30 days. Turn it off to ask for the code at every sign-in, also on devices that were trusted before.
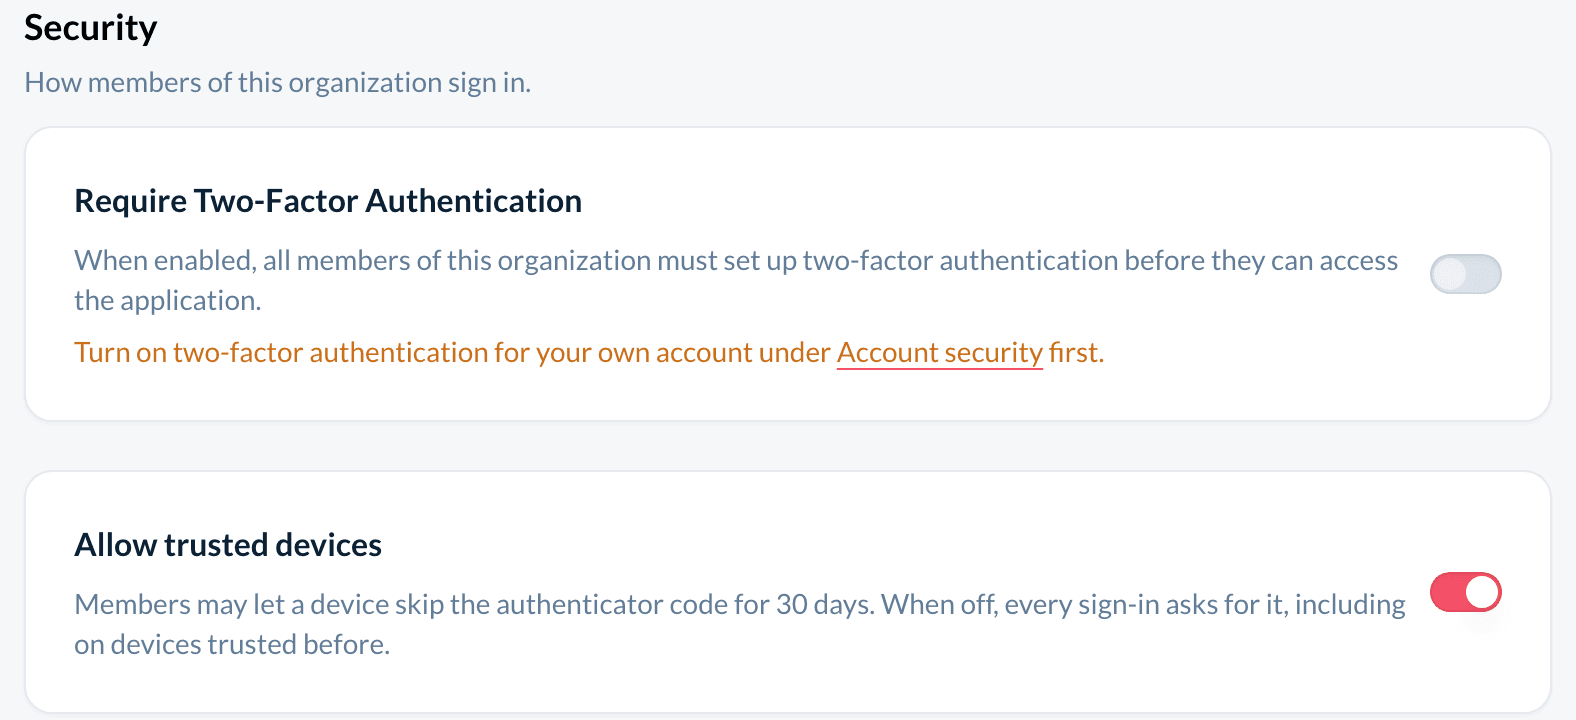
A token or a connected app, such as the CLI or an AI client, cannot show a second factor when it is used. devguard therefore records whether the sign-in that created it had one. If it was created after you turned the requirement on, from a sign-in without a second factor, this organization refuses it. Tokens and connected apps created before keep working. Organization tokens belong to no person's sign-in and are never refused.
While the requirement is on, Credentials without two-factor authentication lists your members' personal tokens and connected apps whose sign-in had no second factor, also those created before. Choose Revoke to end one. Anything still using it stops working on its next request.
While an organization requires two-factor authentication, its members cannot turn their own off.
If a person belongs to several organizations and one of them turns off trusted devices, that person enters the code at every sign-in. Changes to both settings are written to the audit log.
Turn AI or the calendar feed on or off
- On the Settings tab, find the AI features card or the Calendar Subscription card.
- Use the switch. It saves at once, and a message confirms the change.
AI features turns every AI feature on or off for the whole organization, from the AI assistant to questionnaire auto-fill and the knowledge base search of connected AI clients. With it off, nothing of your organization's content goes to an AI model. Calendar Subscription turns on a public calendar link to your Deadlines. Anyone with that link can read the deadlines. When you turn the switch off, the link stops working. When you turn it on again, devguard makes a new link, so everyone must add the calendar again.
Check your plan and usage
- Choose the Billing tab. In the Usage section, AI Usage shows how many AI requests the organization made this month and when the count resets.
- On the free plan, the tab also shows how much of each plan limit you use. On the Business plan, it says that all feature limits are lifted.
- To change the plan, see Billing below; it is on the same tab.
Export all data
The export is one ZIP file of up to 512 MB. It holds the records of your compliance work as JSON and CSV, with the stored files. It leaves out members, roles, tokens and integration secrets. Its audit log has only changes in the app: account changes, such as the name, two-factor authentication, branding or a new owner, are not in it. For the complete log, use GET /audit-log/.
- On the Settings tab, find Export all data and choose Start export.
- devguard builds the file in the background and notifies you when it is ready.
- Choose Download. The card shows the date of the last export.
A new export replaces the previous one. While an export runs, you cannot start another one.
Hand over or delete the organization
These actions are in the Danger Zone at the end of the Settings tab. Admins see the zone too, but only the owner can transfer the organization, delete its data or delete it.
To hand the organization over:
- Make sure the new owner is an admin. If not, change their role in People first.
- Choose Transfer Ownership. A dialog lists the admins.
- Choose Transfer next to the admin's name. The admin becomes the owner at once, and you become an admin. Only the new owner can transfer it back. To stop, choose Cancel.
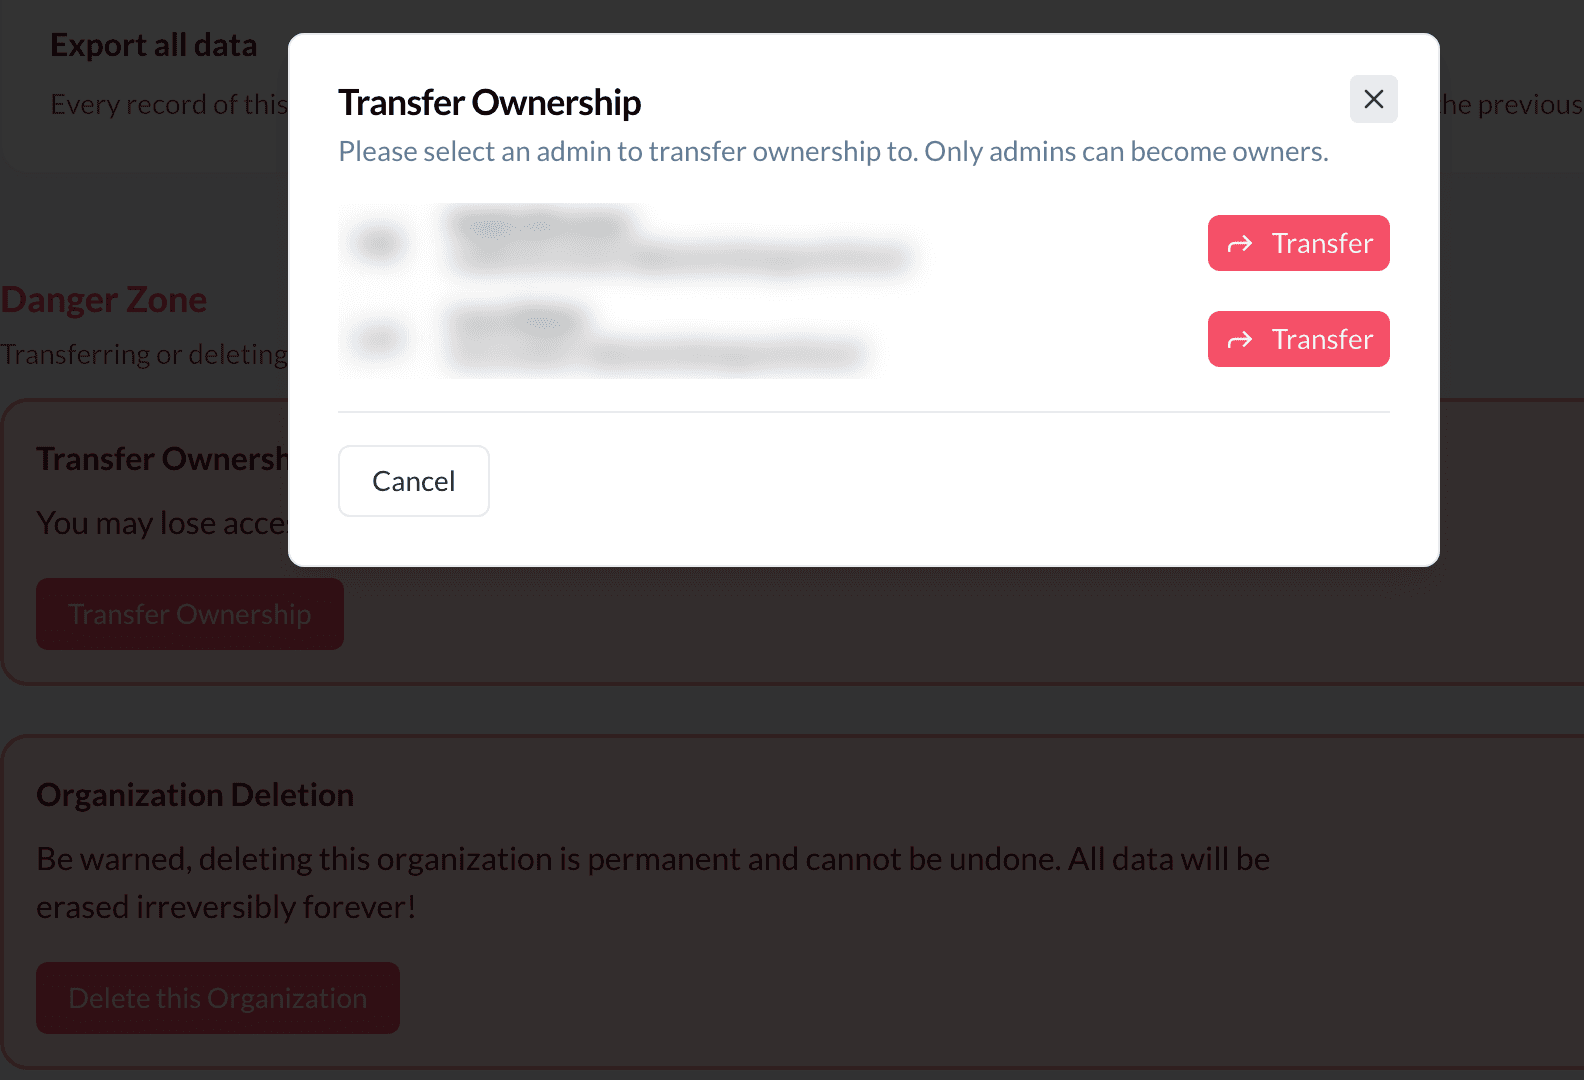
Your organization may be managed by a compliance provider: a consultancy or IT firm that runs devguard for its clients through a mandate. The provider's staff cannot become your owner.
To delete the organization:
- Choose Delete this Organization.
- Type the organization's name and choose Delete Organization.
Watch out: deletion starts as soon as you confirm. It removes all data of the organization, including policies, risks, evidence and files. You cannot undo it. If you may need the data later, export it first.
To keep the organization but start over, delete only its data:
- Choose Delete all data.
- Type the organization's name and choose Delete all data.
The organization returns to its starting point. Members, billing and the audit log stay. Policies, risks, assets, frameworks, evidence and every other record are removed for good, and so is the last export. If an export is still running, wait for it to finish first.
Reference
Tabs
| Tab | What it holds | Guide |
|---|---|---|
| Settings | Name, logo, UUID, AI features, calendar feed, security, export, transfer, deletion | This page |
| Branding | Wide logo, colors, description and links for reports and vendor pages | Branding |
| Portal | Whether the employee portal is open, and its sections | Portal |
| Trust Center | A public API that your website uses to show your certificates and frameworks | Trust Center |
| Integrations | Connections to your tools, such as GitHub, Jira or Slack, and the connected apps people allowed, such as the CLI | Integrations |
| Tokens | API tokens that belong to the organization | Tokens |
| SSO | Sign-in through your identity provider (SAML) and directory sync (SCIM) | SSO |
| Billing | Plan, payment method, invoices and add-ons, and the AI requests and plan limits used | Billing below |
Only owners and admins see Tokens and SSO, and the Connected apps card under Integrations.
Version numbers, company details and links to documentation and support open from About in the page footer, next to Site Notice.
Permissions
| Action | Owner | Admin | Member, auditor |
|---|---|---|---|
| Read the Settings tab and the usage on the Billing tab | Yes | Yes | Yes |
| Change the name, logo, time zone, switches and security | Yes | Yes | No |
| Change the branding and the portal | Yes | Yes | No |
| See and manage billing | Yes | Yes | No |
| Export all data | Yes | Yes | No |
| Transfer ownership | Yes | No | No |
| Delete all data | Yes | No | No |
| Delete the organization | Yes | No | No |
Members with the employee role use only the portal and do not see Settings. Organization tokens can read the organization but cannot change these settings.
Billing
Each organization has one subscription.
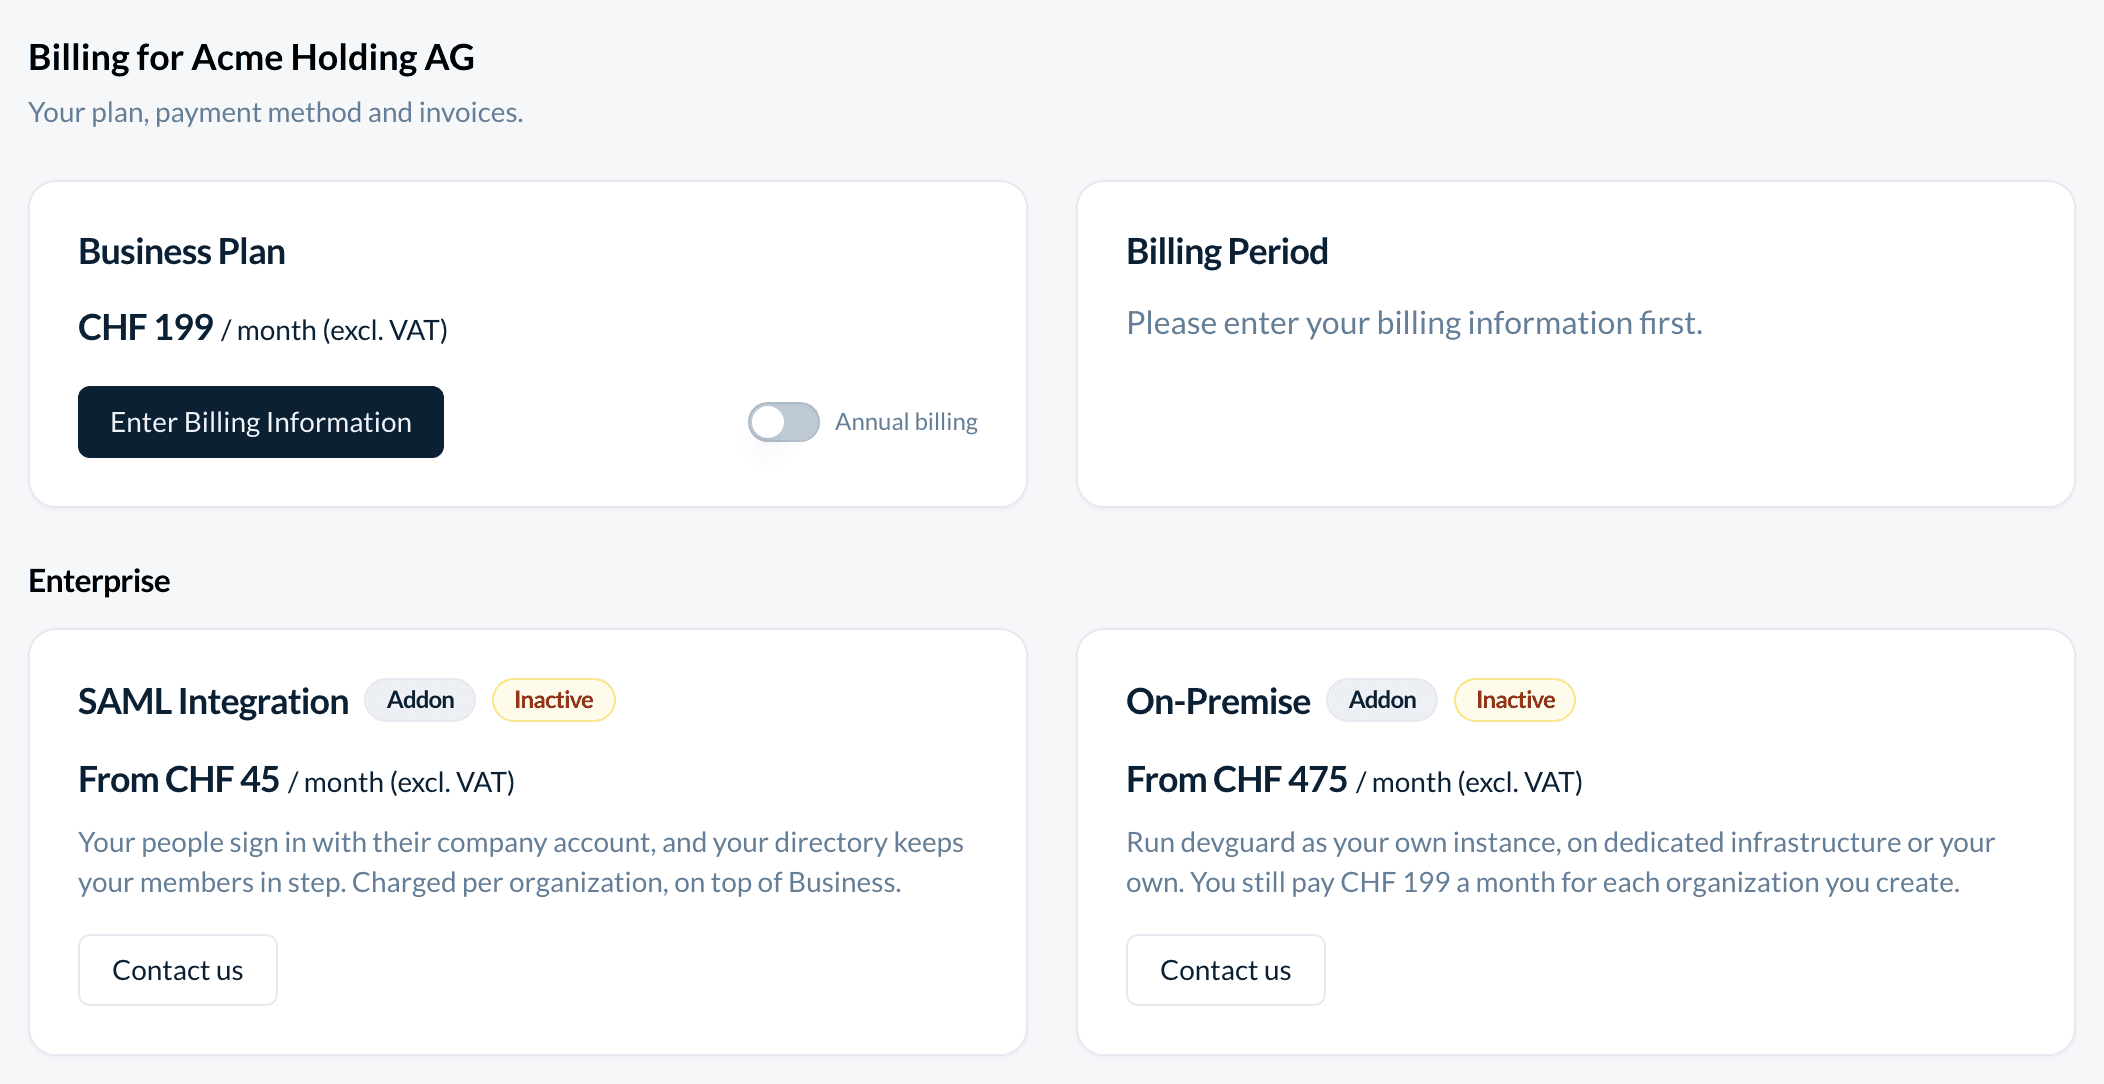
- Enter Billing Information starts the Business plan, monthly or with Annual billing. Manage plan opens the payment method and the invoices.
- Cancel plan ends the plan at the end of the period. Until then, Continue plan undoes it. After that date, the organization is on the free plan.
- Enterprise lists two add-ons with their prices, SAML Integration and On-Premise. To request either one, choose Contact us. Once SAML Integration is on, its card also links to SSO. See Add-ons.
- If a compliance provider manages your organization, the tab shows Managed by and the provider's name. Ask the provider about plans and invoices.
Add-ons
Prices are per month and exclude VAT.
| Add-on | Price | What it applies to |
|---|---|---|
| SAML Integration: single sign-on and directory sync | From CHF 45 | Each organization, on top of the Business plan |
| On-Premise: your own instance | From CHF 475 | The instance. You also pay CHF 199 for each organization you create. |
Plans
| Free | Business (monthly or annual) | |
|---|---|---|
| Branding | Not available | Yes |
| Feature limits | Yes, see Billing | None |
| Audit log kept for | 30 days | 3 years |
/admin/ is for devguard staff only.
For developers
These settings have no public API. Change them in the app.
- Organization id: the Organization UUID is the
organizationIdthat the API asks for. - Tokens: for scripts, create an organization token. Personal tokens are under Account → Tokens.
- Two-factor authentication: the requirement also holds personal tokens and connected apps to the sign-in that created them. One created after the requirement, from a sign-in without a second factor, answers
403in this organization. Organization tokens are exempt. - Calendar feed: the link from Deadlines needs no token, so treat it like a password.
- Export: the ZIP file from Export all data holds the app's records as JSON and CSV files, with the stored files, up to 512 MB. It leaves out members, roles, tokens, integration secrets and the account-side log entries (name, two-factor authentication, branding and owner changes). For the complete log, use
GET /audit-log/. - Audit log: changes to the name, the switches, the security settings, the branding, the portal and the owner appear in the audit log, and so do exports and their downloads. A new square logo is not logged. Read the entries with
GET /audit-log/.
How is this guide?