Assets
Keep one inventory of the systems, data and equipment you protect, rate how sensitive each one is, and see which ones still need a class, a risk, a control or a review.
ISO/IEC 27001 asks for an inventory of your information and of the things that hold it (Annex A 5.9). In devguard, each entry is an asset: a system, a dataset, a device, a room or a piece of equipment. Each asset has a number such as A-024, an owner role and a rating for confidentiality, integrity and availability. Risks, controls and access reviews all point back to it.
The tasks below follow the order of the work:
- Add an asset
- Import assets from a spreadsheet
- Rate it
- Link controls, risks and access
- Find what needs attention
- Archive or delete an asset
Three guides go further. Asset classes group similar assets and give them default ratings and fields. An asset review checks that each entry in the inventory is still correct. An access review checks who may use each asset. Scripts and integrations: see API below.
Add an asset
The owner is a business role, not a person. So the asset keeps its owner when staff change. Create the role first if it does not exist.
- Open Assets and choose Add asset. A form opens on the right.
- Enter a Name that people in your company recognize, such as "Supplier invoice archive". The Slug fills in from the name. It is the asset's address in the app and must be unique.
- Choose the Owner role and leave the Status on Active.
- If the asset is part of a larger one, choose the Parent asset. For example, "Backup tape rotation" can sit under "On-site backup appliance".
- Under Classification, choose the Asset class. The class gives default ratings (see Rate it) and adds its own fields under Details.
- Choose Create. The asset gets the next number.
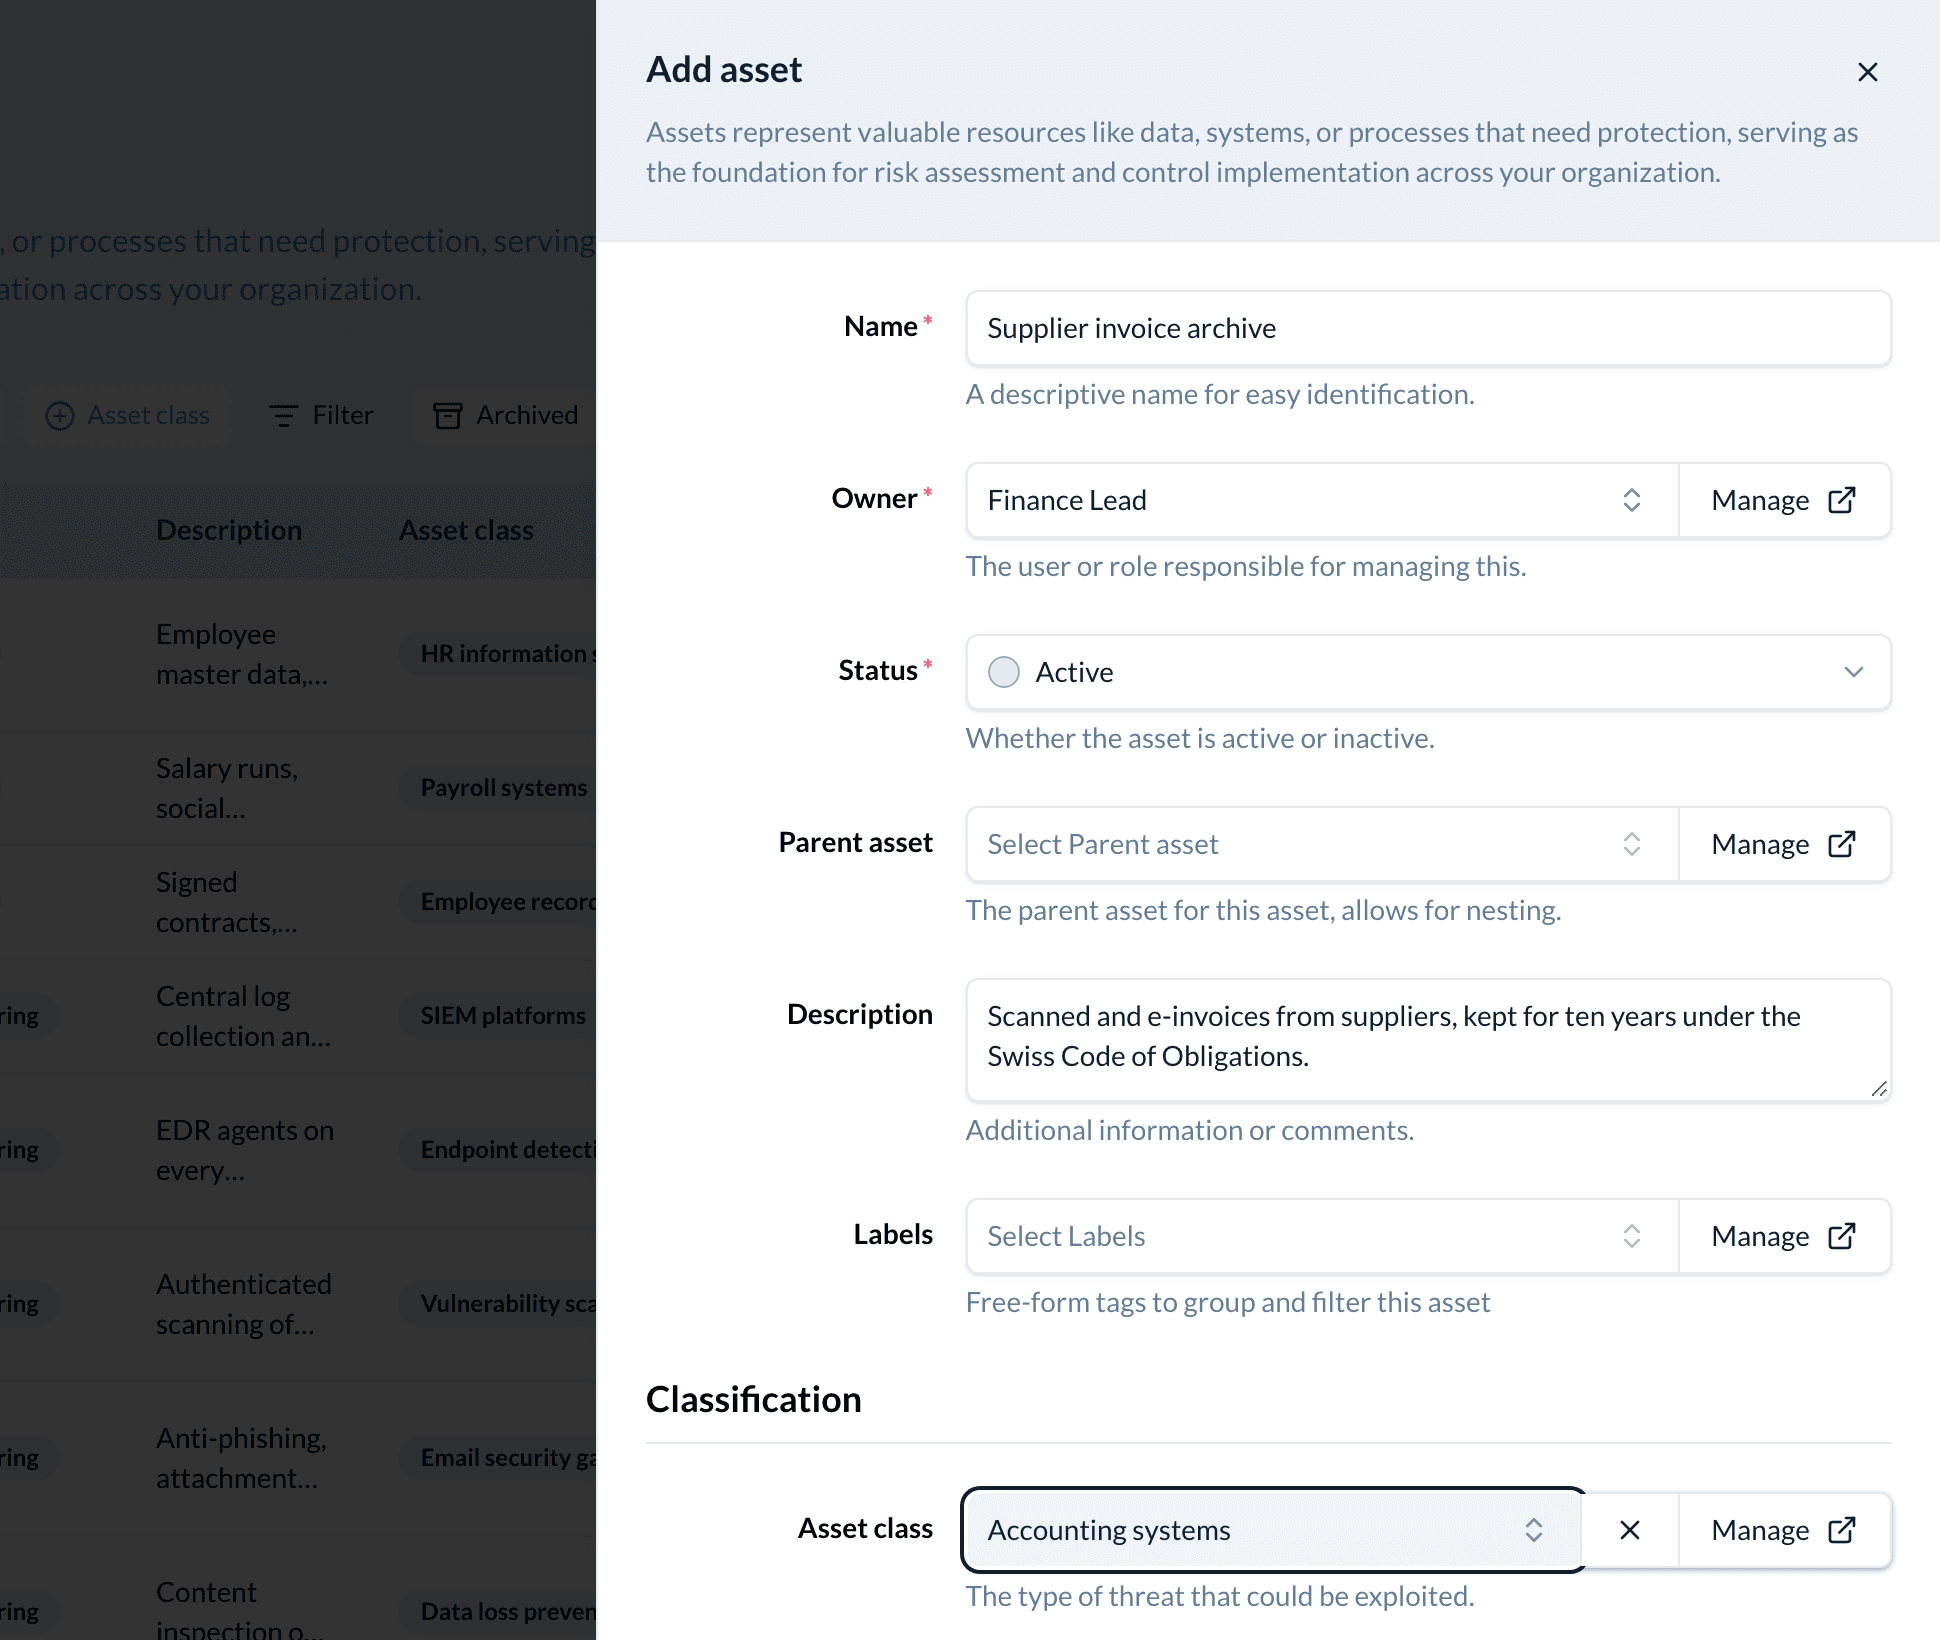
You can fill in the rest now or later: Description, Labels, Location and the links described below. To change one field later, click it on the asset's page. To change several, choose Edit.
Import assets from a spreadsheet
If your inventory is in Excel today, import it instead of typing it.
-
In the asset list, open the menu at the right of the toolbar (the three dots) and choose Download CSV template.
-
Fill one row per asset. Owner, asset class, location, labels and memberships take the names you see in the app:
assets.csv name;slug;status;ownerId;confidentialityRating Payroll export archive;;ACTIVE;Head of People;9 Badge printer;;ACTIVE;Facilities;3 -
Save the file as CSV and choose Import CSV in the same menu.
-
The Import result shows how many rows arrived. A refused row is listed with its row number, the column and the reason. Correct those rows and import only them again.
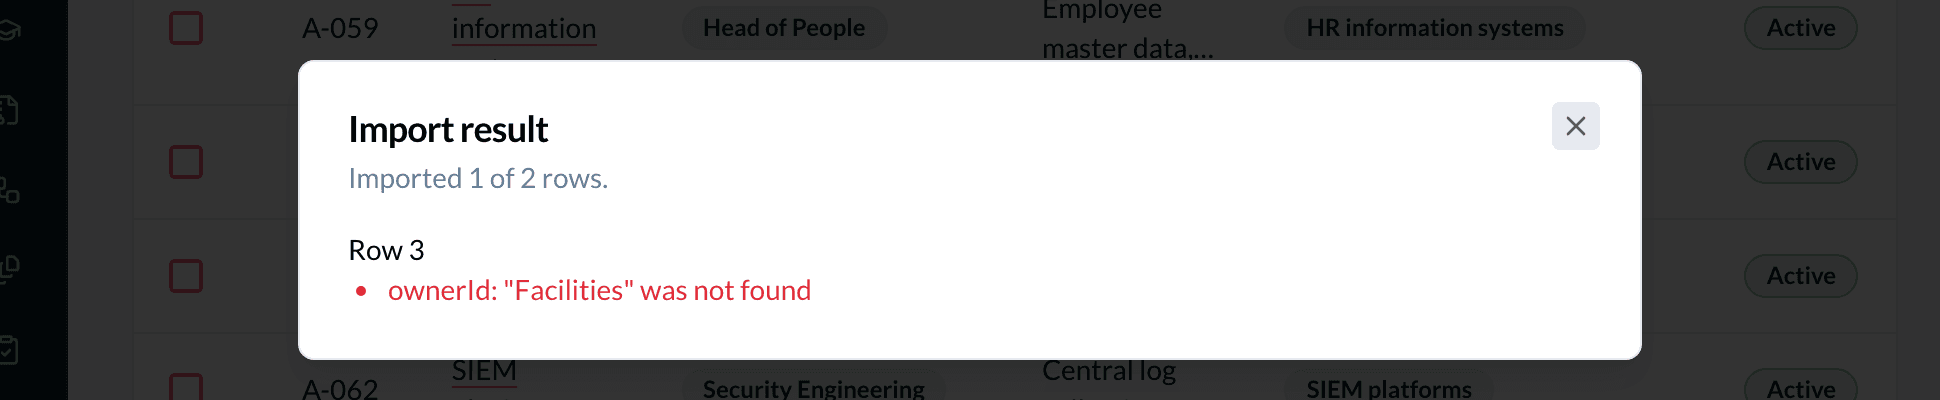
Row 1 is the header, so the first asset is row 2. The column rules are in Import format below.
How the sensitivity rating works
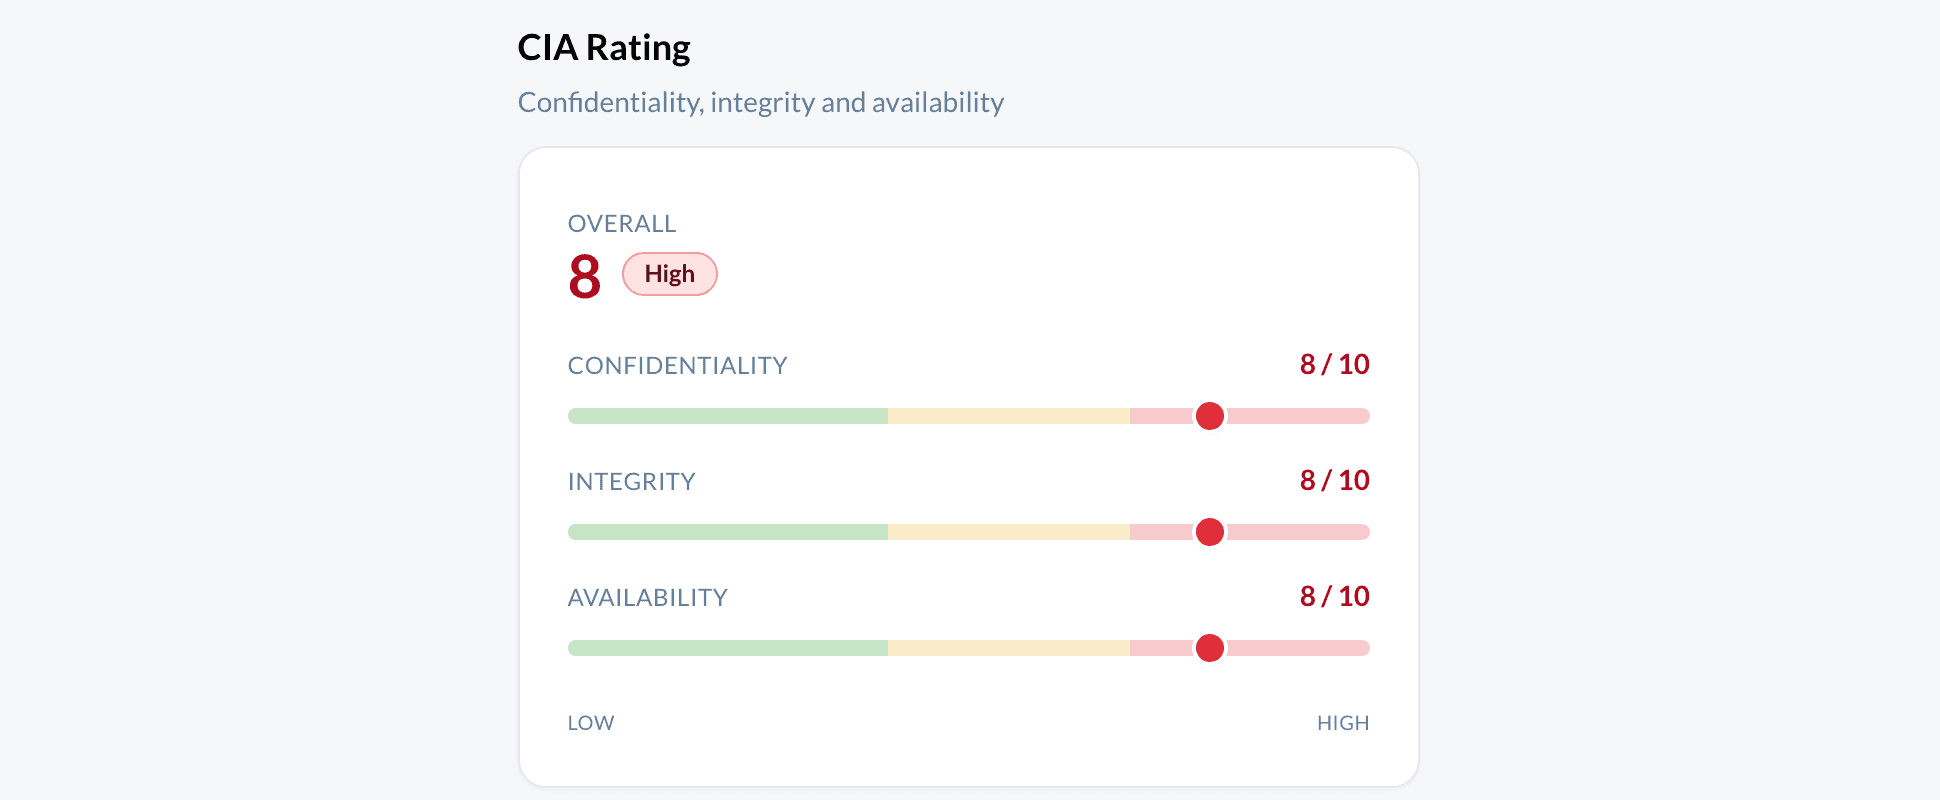
Each asset has three ratings from 1 (low) to 10 (high):
- Confidentiality: how much harm if the wrong person reads it.
- Integrity: how much harm if it is changed or wrong.
- Availability: how much harm if it is not there when you need it.
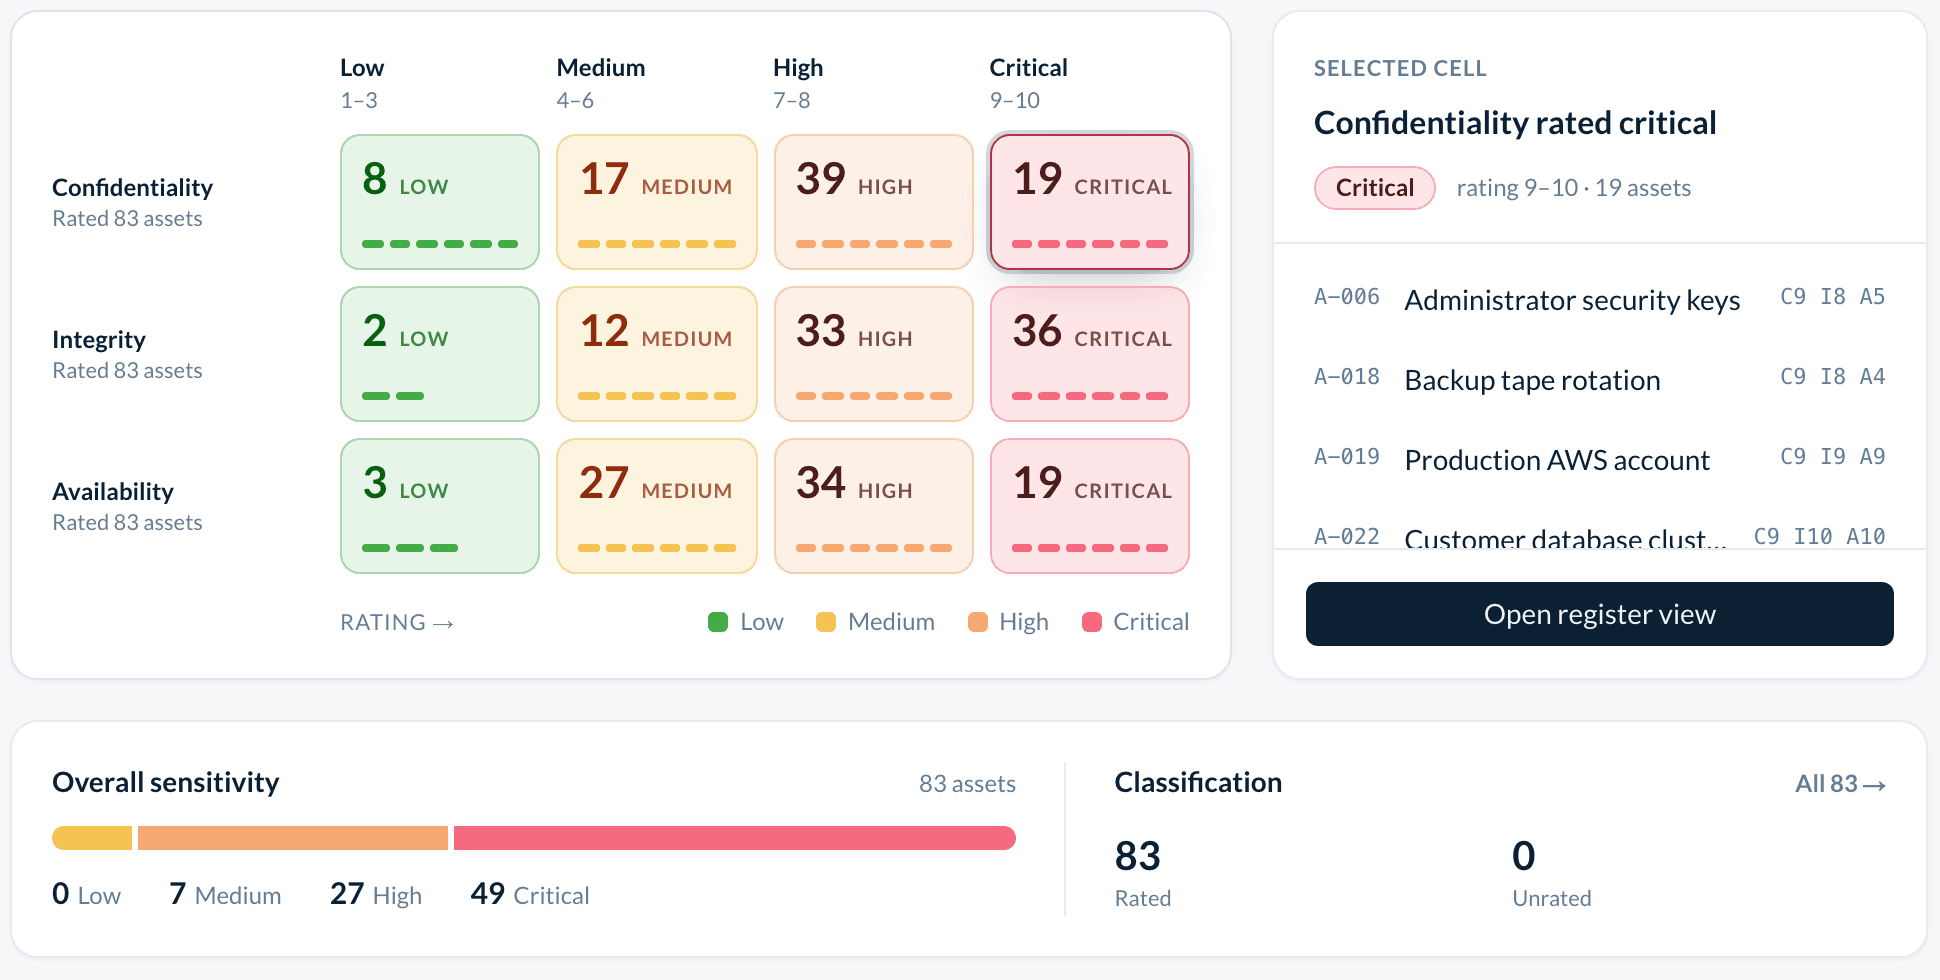
The highest of the three is the asset's overall rating, its sensitivity. The overview shows it in four levels: Low (1 to 3), Medium (4 to 6), High (7 to 8) and Critical (9 to 10). "Sensitive" means High or Critical.
An asset class can carry the same three ratings. If an asset has no rating of its own, it uses the class rating. A rating set on the asset always wins. The two are never averaged.
Rate the asset by what it holds or does, not by how well it is protected. A customer database is confidential even when it is encrypted.
Rate it
- Open the asset and choose Edit.
- Under Classification, move the Confidentiality rating, Integrity rating and Availability rating sliders. Leave a slider on Unset to use the class rating.
- Choose Save.
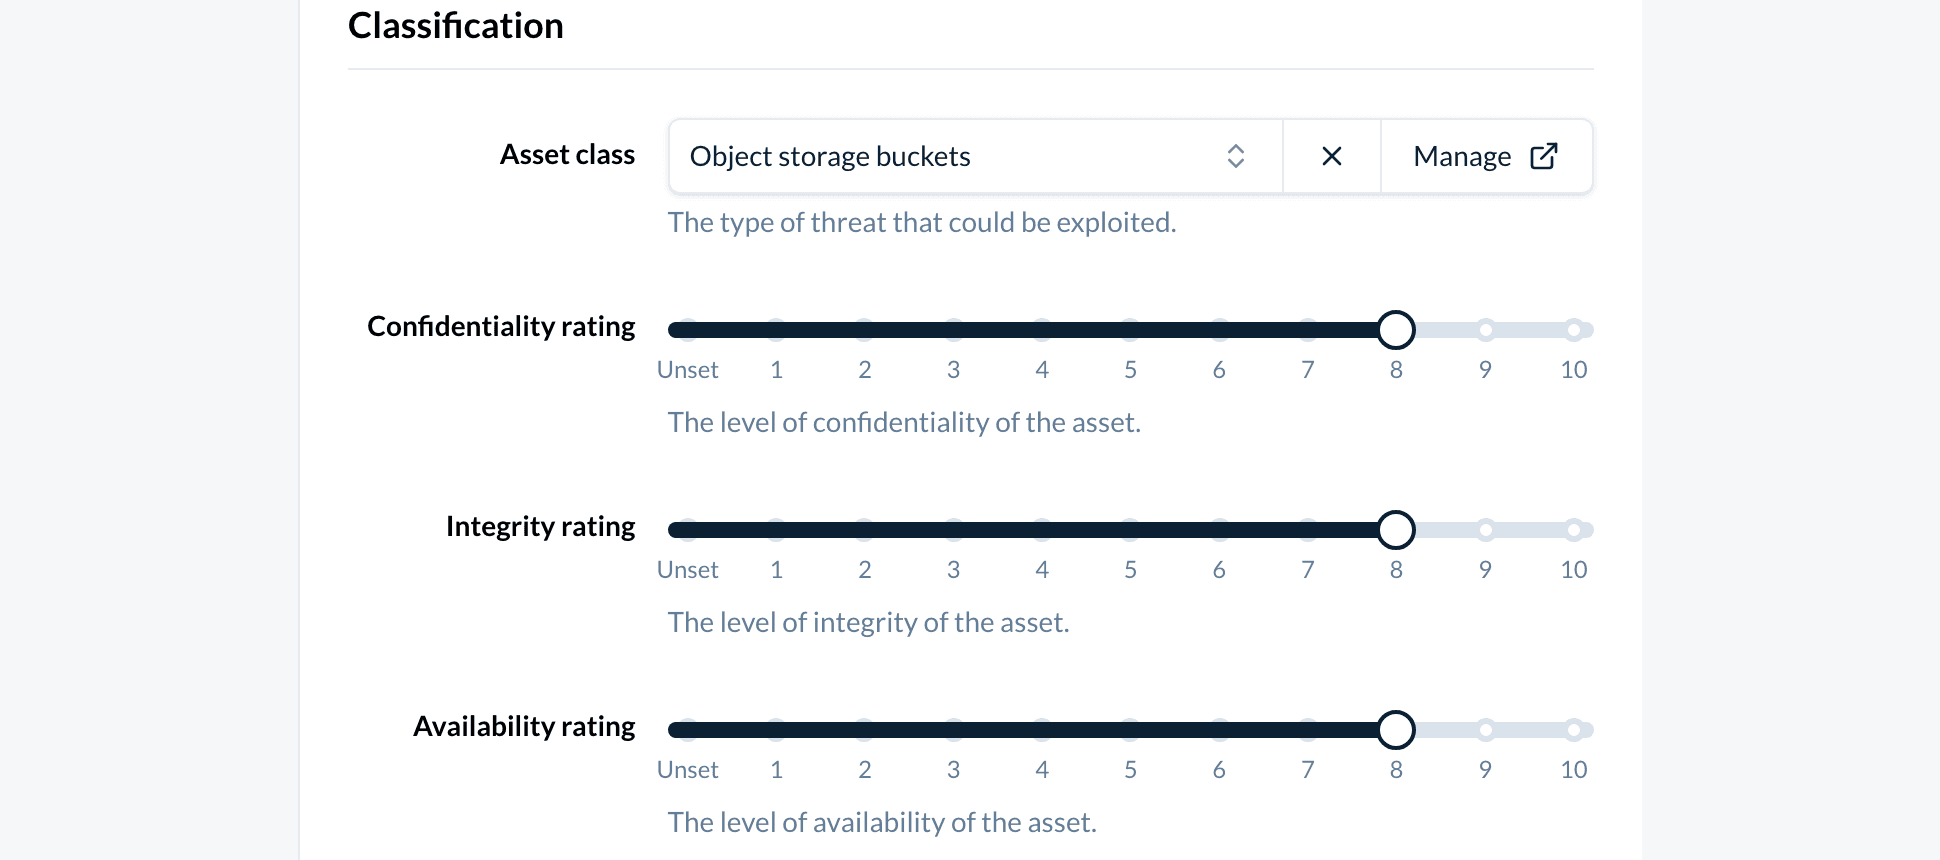
The CIA Rating card on the asset's page shows the result: the three ratings and the overall value.
Link controls, risks and access
The asset's page lists its links under Related Data.
Map a control
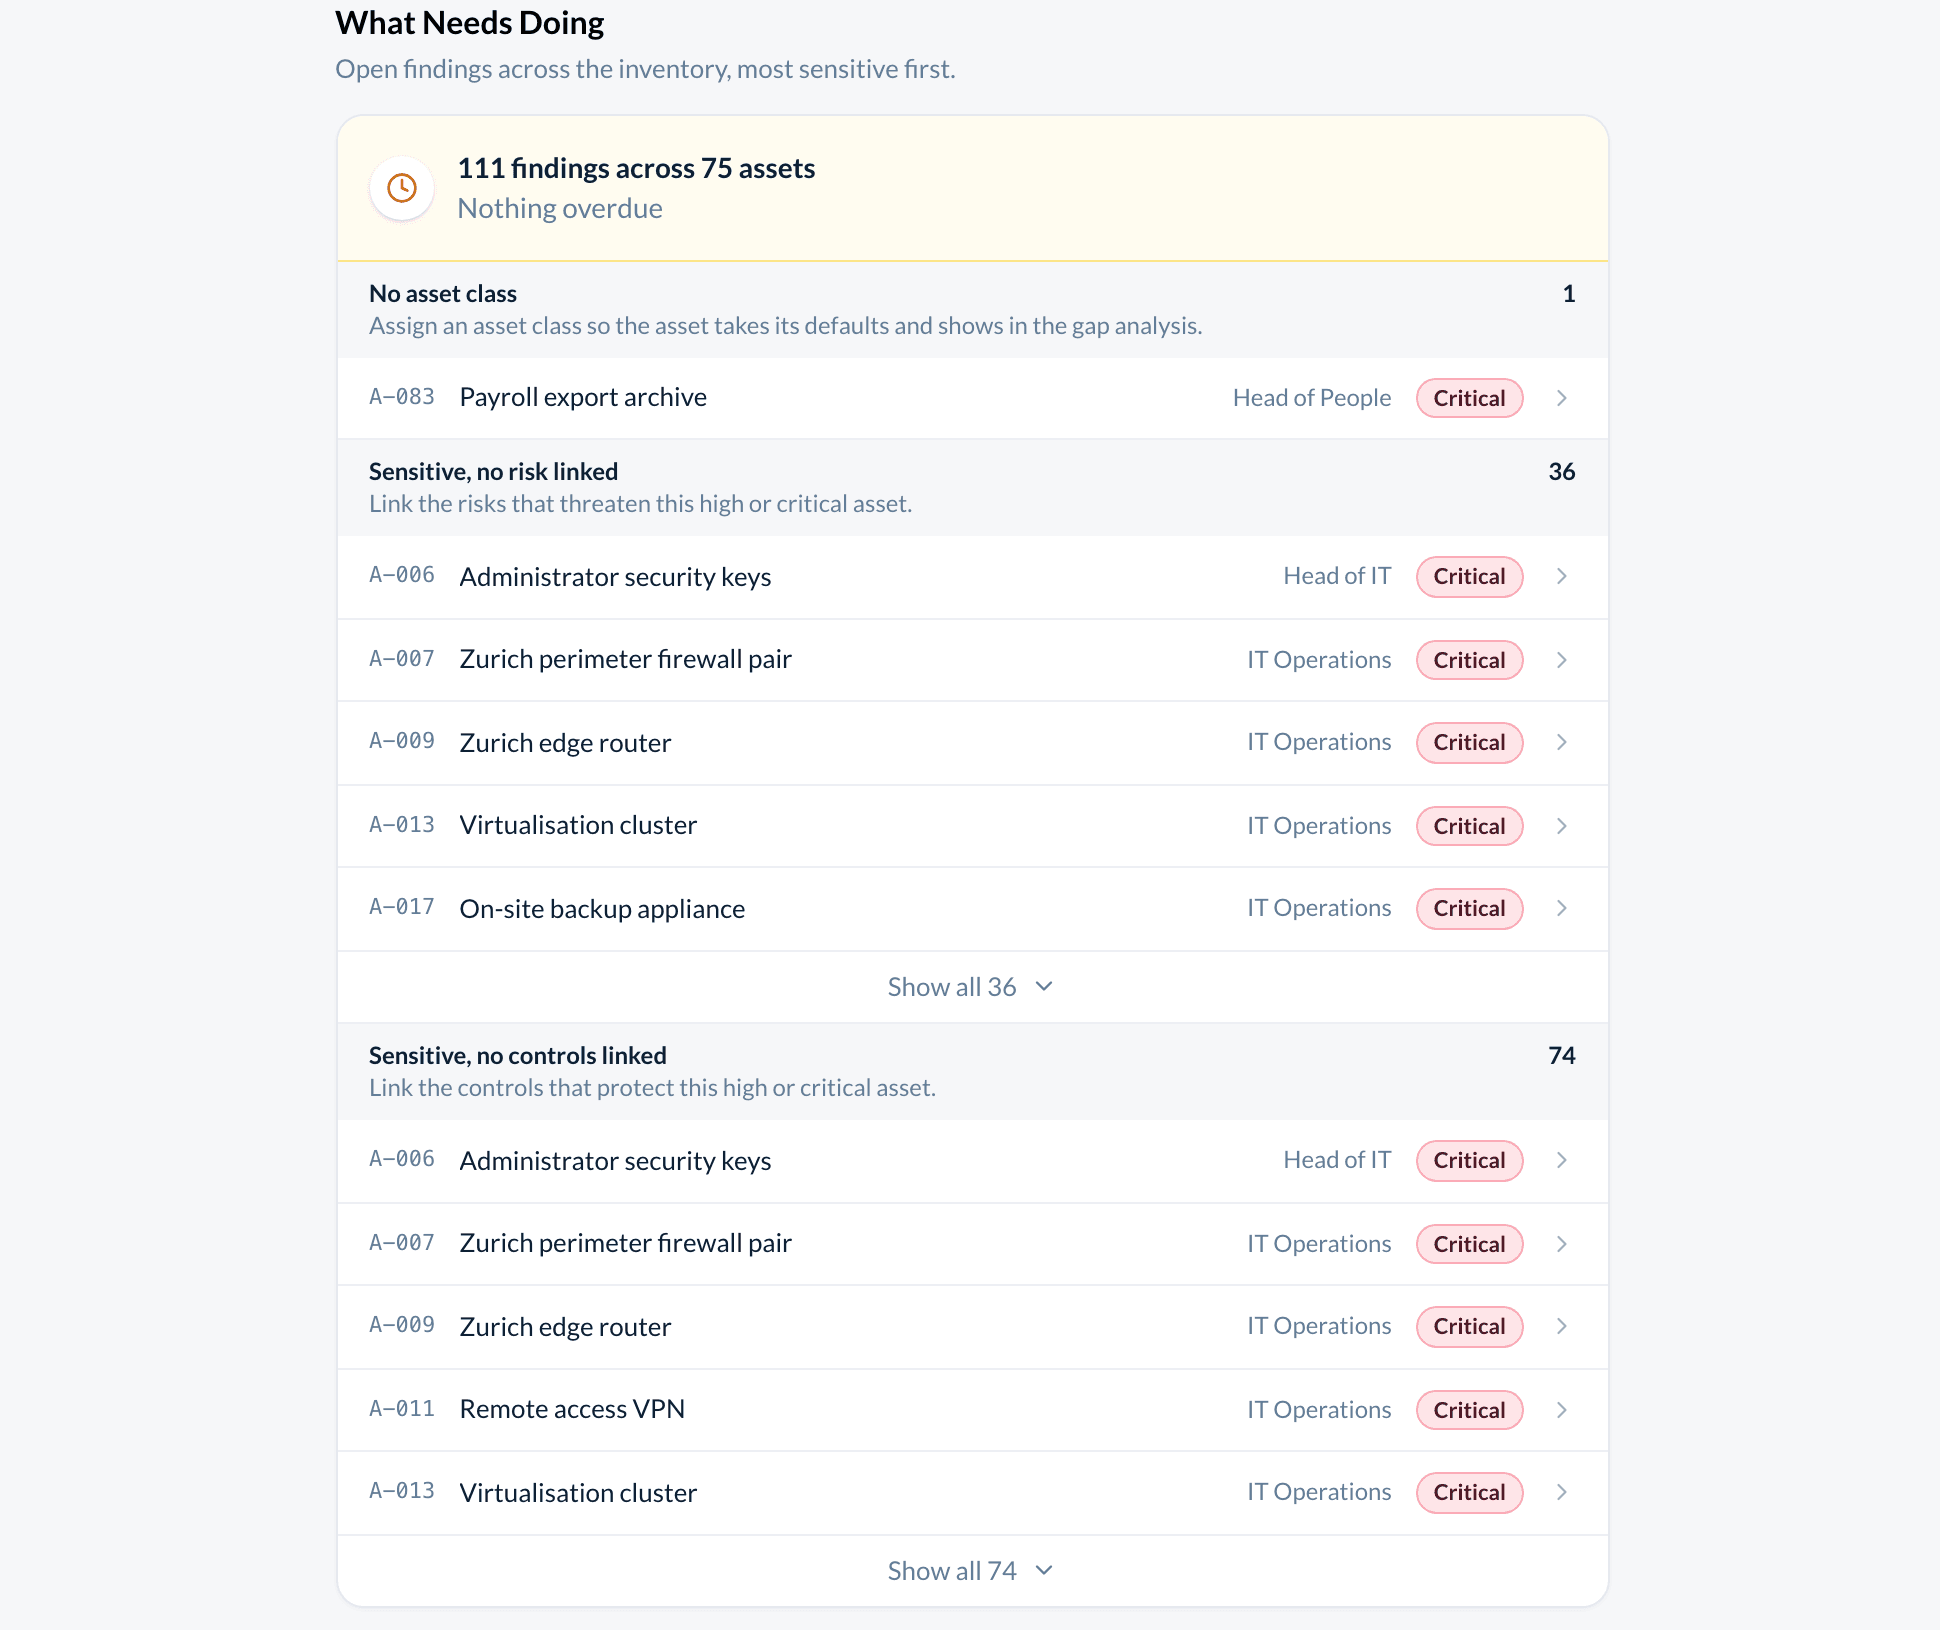
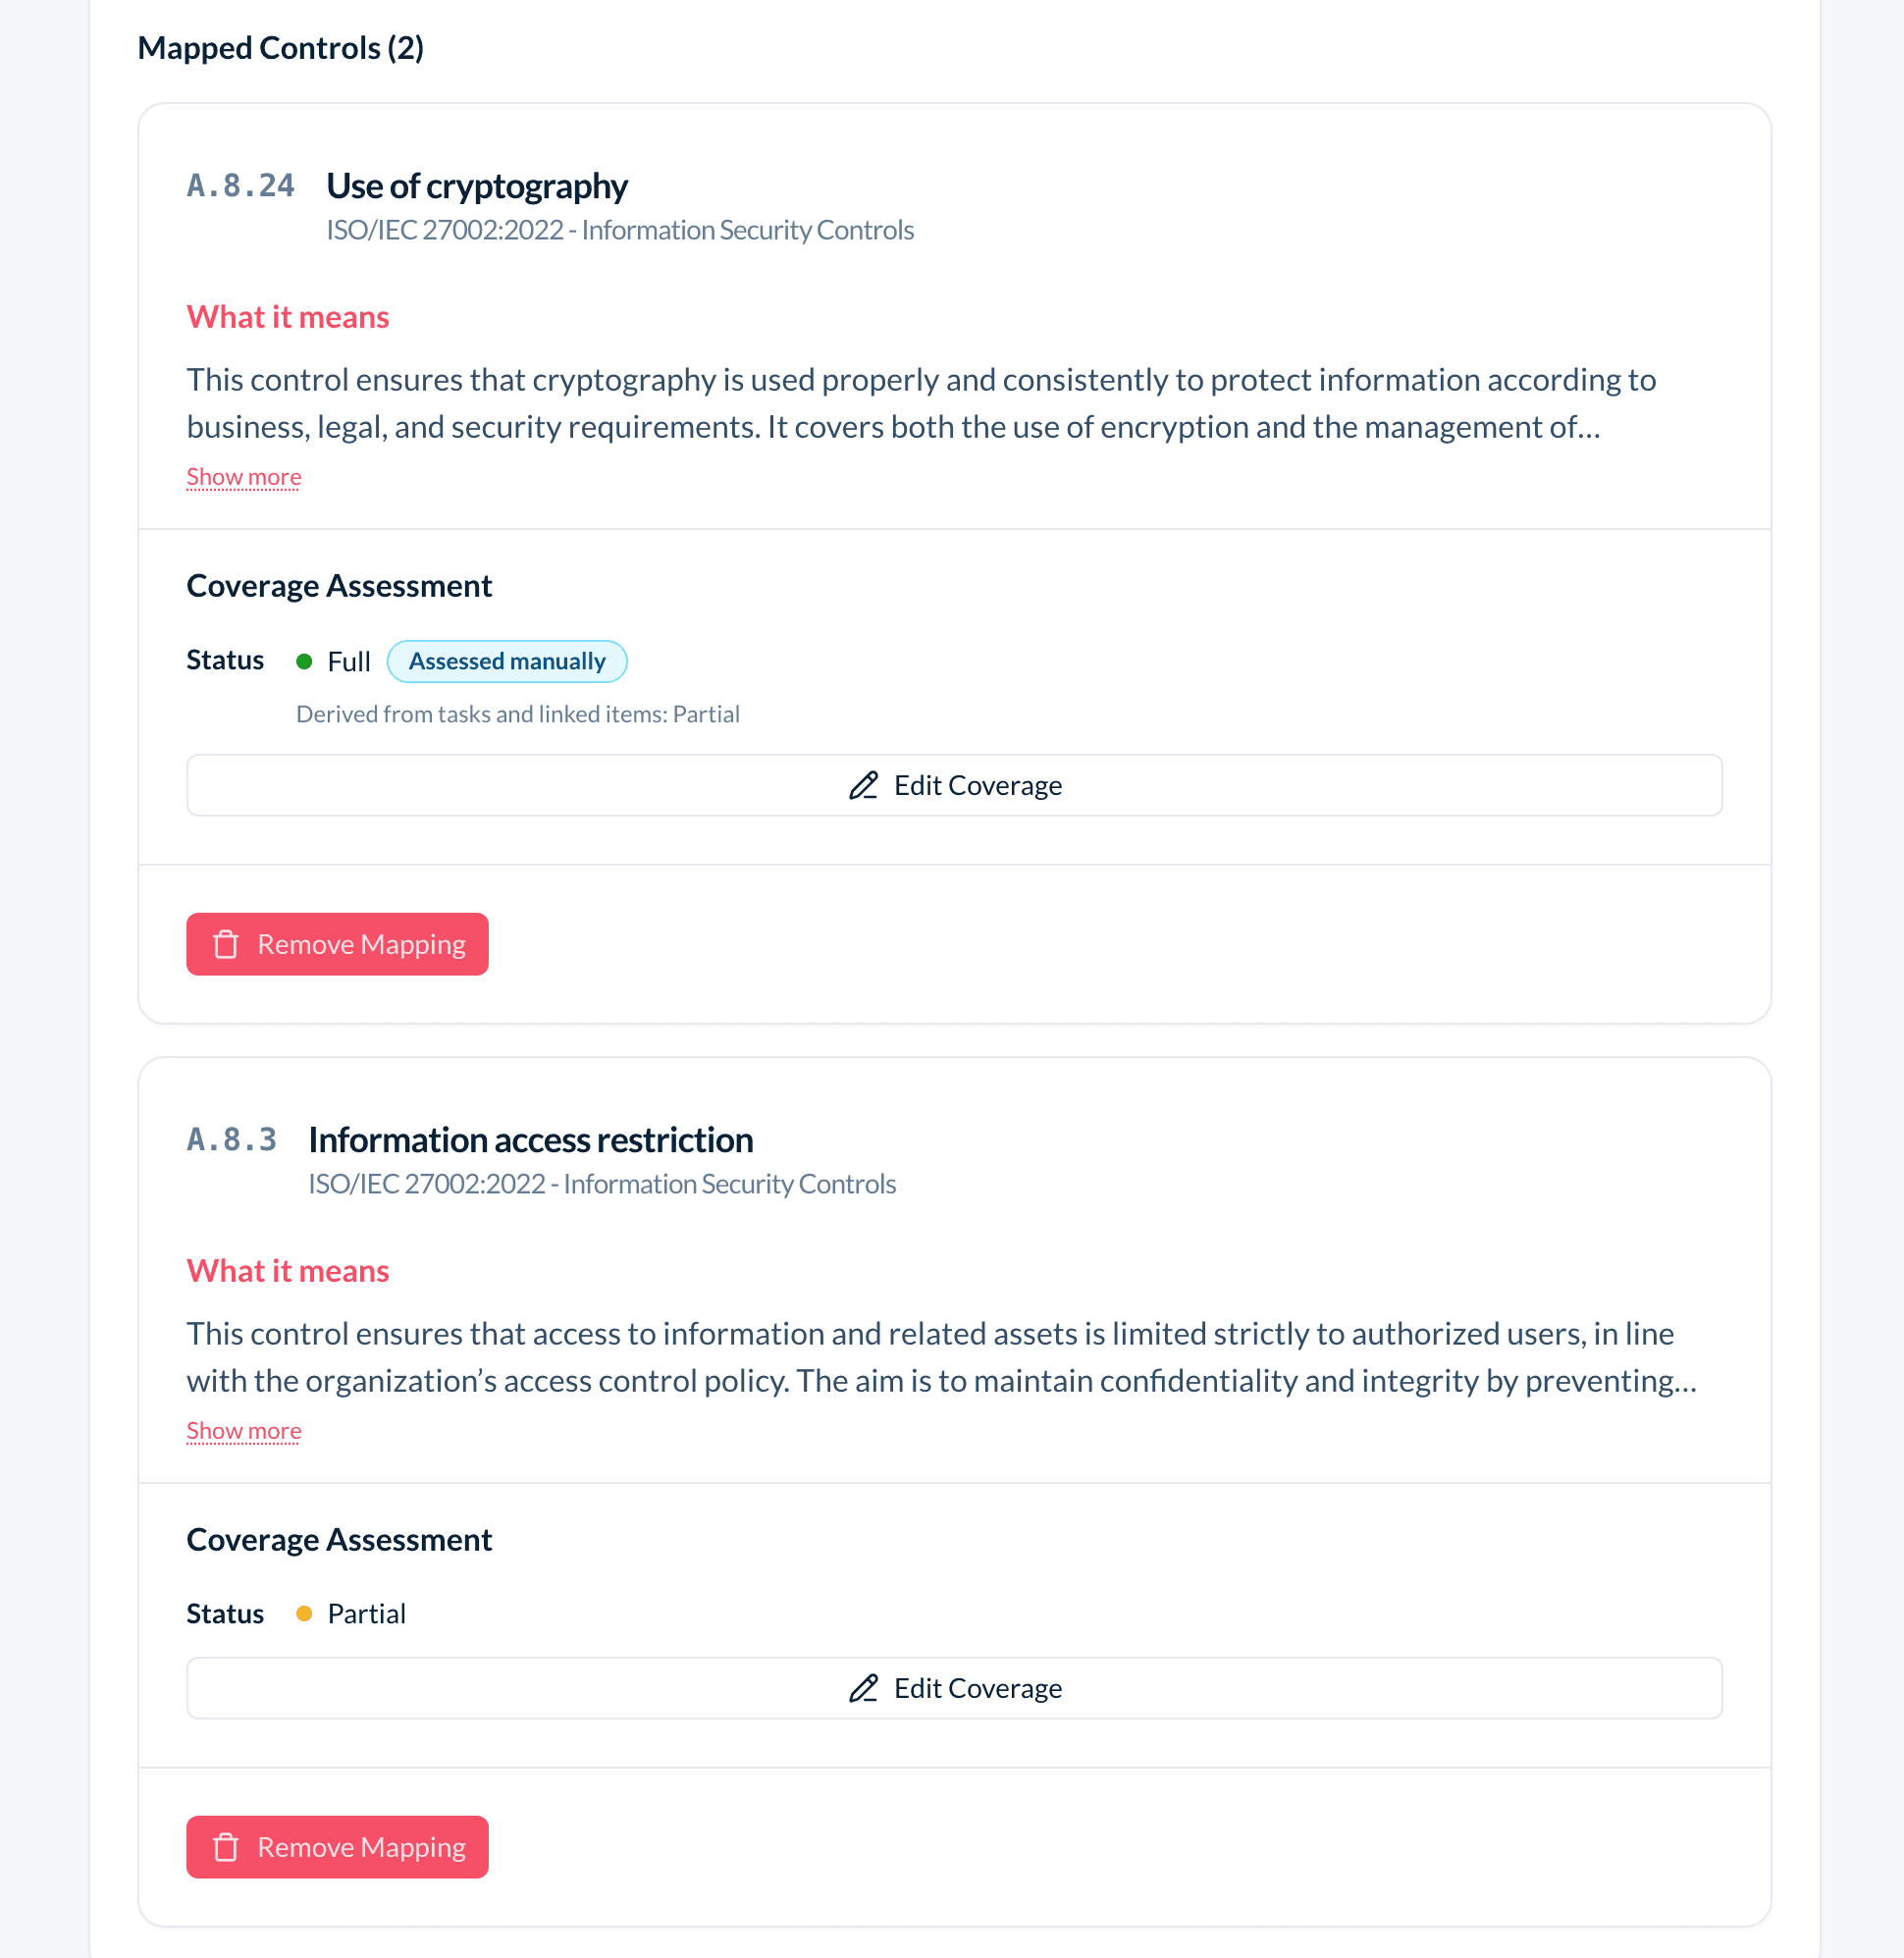
A control that is mapped to an asset protects it. Mapping one clears the overview finding Sensitive, no controls linked for that asset.
- Open the asset's Controls tab.
- Under Control Mapping, choose a Framework if you want to narrow the search.
- Open Select Control and type the identifier or part of the name. Only controls of the frameworks you have adopted are offered.
- Choose the control and then Map Control. It appears under Mapped Controls.
You can also pick controls in the Controls field of the Edit form.
Link a risk
You link a risk to an asset from the risk. Open the risk and choose the asset under Impact. The asset then counts as covered for its asset class in the gap analysis.
Record who has access
- Open the asset and choose Edit.
- Under Access Management, choose the roles in Memberships. These are the roles whose members may use the asset.
- If the asset must be reviewed on a schedule, choose a Retention period.
- Choose Save.
An access review later checks the memberships. An asset review with the scope Due Soon or Overdue picks the assets whose retention period is due.
Evidence, actions and tasks
The asset's Evidence, Actions and Tasks tabs link existing records or create new ones. A task added there also appears in Tasks.
Find what needs attention
Open Assets → Overview. It covers every active asset. Retired and archived assets are left out.
- Asset Posture counts your assets and shows their sensitivity as a bar.
- What Needs Doing lists the open findings, grouped by finding and most sensitive asset first. Click a row to open the asset.
- Asset Coverage shows how many assets are classified and rated, how many sensitive assets have a risk and a control, and how many were reviewed in the last 12 months.
- Open Gaps lists the asset classes with expected threats that no risk covers yet, from the gap analysis.
Each finding clears when you do the step it names:
| Finding | It clears when |
|---|---|
| Not yet rated | the asset or its class has at least one rating |
| No asset class | you choose an asset class |
| Sensitive, no risk linked | a risk links this High or Critical asset |
| Sensitive, no controls linked | a control is mapped to this High or Critical asset |
| Review due | an asset review approves the asset. Only assets created more than 12 months ago can be due. |
To see where your most sensitive assets are, open Assets → Assessment Matrix. Click a cell of the Heat map to list its assets on the right. The other tabs are described under Assessment matrix.
Archive or delete an asset
Archive an asset you no longer use but want to keep on record. If it still exists but is out of service, set the Status to Retired instead.
- In the asset list, open the asset's row menu and choose Archive.
- If the asset has active child assets, choose what happens to them. Archive children too archives every active asset below it. Move children up moves its direct children to its own parent, or to the top level.
An archived asset keeps all its data and history. It no longer counts toward your plan limit. It also no longer counts toward a control's coverage status, but the control still lists it as linked.
To see archived assets, switch on Archived above the list. Restore one from its row menu.
Watch out: Delete cannot be undone. It removes the asset, its comments and its links to controls, risks, evidence, labels and roles. It also removes the asset's rows in access reviews, even in completed ones. Its child assets move to the top level. Archive instead if an auditor may ask about the asset.
Reference
Fields
| Field | Required | Notes |
|---|---|---|
| Name | yes | Shown everywhere the asset appears. |
| Slug | yes | Lowercase, unique in your organization. The asset's address: /assets/detail/<slug>/. |
| Owner | yes | A business role. |
| Status | yes | Active or Retired. |
| Parent asset | no | Builds a tree. An asset cannot sit under itself or its own children. |
| Description | no | Free text. |
| Labels | no | Shared with risks and vendors, managed under Labels. |
| Asset class | no | Gives default ratings and extra fields. See asset classes. |
| Confidentiality, integrity, availability rating | no | Whole numbers 1 to 10. Unset (0) takes the class rating. |
| Controls | no | Controls that protect the asset. |
| Location | no | A location from Locations. |
| Memberships | no | Roles whose members may use the asset. |
| Retention period | no | The review schedule for the asset, picked from your schedules. An asset review with the scope Due Soon or Overdue includes the asset when its next date is within 14 days or past. |
| Details | no | The fields of the asset's class. |
Statuses
| Status | Meaning |
|---|---|
| Active | In use. Counted on the overview. |
| Retired | Out of service but kept on record. Left out of the overview, but still in the list and the matrix. |
| Archived | Hidden from the list. Archiving is separate from the status, so a retired asset can be archived too. |
Sensitivity levels
The overview, the matrix and the CIA Rating card on the asset's page use four levels: Low (1 to 3), Medium (4 to 6), High (7 to 8) and Critical (9 to 10). The dashboard and the asset report use three: Low (1 to 3), Medium (4 to 6) and High (7 to 10).
Assessment matrix
- Heat map: one row each for confidentiality, integrity and availability, and one column per level. A cell shows how many assets have that rating.
- Triad: where each asset sits between the three ratings. Assets with the same balance share one bubble.
- Plot: confidentiality against integrity, with the number of highly sensitive assets beside it.
The matrix shows every asset that is not archived, retired ones included.
Permissions
| Role | Assets, classes, reviews | Comments |
|---|---|---|
| Owner, admin | Create, edit, archive, delete, decide review items | Write |
| Member | Read | Write, edit and delete own |
| Auditor | Read | Read |
| Organization token | Same as an admin, over the API |
Limits
On the Free plan you can keep 100 assets, 100 memberships, 4 asset reviews and 4 access reviews. Archived assets and reviews do not count. Retired assets do. Restoring an archived asset checks the limit again. Paid plans have no limit.
Where assets show up
- Risks: a risk links the assets it threatens.
- Gap analysis: crosses asset classes with threat classes.
- Controls: a mapped asset counts toward a control's coverage.
- Evidence: a record can prove something about an asset.
- Processes: a process run about an asset shows under Process Runs on the asset's page.
- Reports: the asset report and the review reports.
- The Comments and History tabs on every asset.
Import format
- Required columns:
name,ownerIdandstatus. A blankslugis made from the name: "Customer database Zürich" becomescustomer-database-zuerich. - Names instead of ids:
ownerId,assetClassId,locationId,labelsandassetMembershipstake the name as shown in the app (case does not matter) or the id. If two entries share a name, use the id.parentId,retentionPeriodIdandcontrolLinkstake ids only. - Several values in one cell: separate them with a comma or a semicolon.
- Status:
ACTIVEorRETIRED, in any case. The label in the language of your app also works, for exampleAktivwhen the app is set to German. - Ratings: whole numbers from 0 to 10.
- File: devguard detects the separator. UTF-8 and the Windows encoding that Excel uses both work.
API
- Base URL:
https://app.devguard.ch/api. - Authentication: an API token, sent as
Authorization: Bearer <token>. Send JSON withContent-Type: application/json.
| Call | Endpoint | Organization id |
|---|---|---|
| List | GET /assets/ | query, required |
| Overview | GET /assets/overview/ | query, required |
| Create | POST /assets/ | body, required |
| Read | GET /assets/{id}/ | not used |
| Update | PATCH /assets/{id}/ | not used |
| Archive | POST /assets/{id}/archive/ | not used |
| Restore | POST /assets/{id}/restore/ | not used |
| Delete | DELETE /assets/{id}/ | not used |
| Map a control | POST /asset-control/map/ | body, required |
| Remove a control | DELETE /asset-control/unmap/ | query, required |
The calls for classes and reviews are on the asset classes, access reviews and asset reviews pages.
{id} is the asset's UUID, shown on its page under Metadata. For these calls you do not send organizationId. If the id belongs to another organization, the API returns 403. If it does not exist, it returns 404.
List. The response is { "items": [...], "total": 82, "page": 1, "limit": 100 }. limit is at most 100. Without filters, the list holds the top-level assets. Their children are nested inside, up to maxDepth levels deep (1 to 10, default 4), and total counts only the top-level assets. With any filter, the list is flat. Retired assets are included. filterByPriority takes low, medium or high (7 to 10) and uses the effective ratings. low also returns unrated assets.
Single asset. GET /assets/{id}/ returns one asset without a wrapper: id, shortId, slug, name, status, ownerId and owner, the three ratings, assetClass, location, parent, labels, controlLinks, assetMemberships, riskLinks, fieldValues, createdAt and updatedAt. The ratings are the asset's own values, with null for unset. The class ratings are under assetClass.
Update. PATCH needs name, slug, ownerId and all three ratings in every call, even if they do not change. Send null for an unset rating. controlLinks (control ids), assetMemberships (role ids) and labels (label ids) replace the current lists. A control outside your adopted frameworks is refused, and nothing is saved. Fields you leave out keep their value.
Archive. POST /assets/{id}/archive/ needs "children": "archive" or "moveUp" when the asset has active child assets. Without it, the call returns 412.
Controls. DELETE /asset-control/unmap/ takes the id of the link (controlAssetLinkId), not the control id. GET /asset-control/mappings/{assetId}/ lists the links.
Errors. An error returns its HTTP status and a body with message, code and status. A validation error reads { "message": "Input validation failed", "code": "BAD_REQUEST", "status": 400, "issues": [...] }, with one entry in issues per field that failed.
These calls use DG_TOKEN (your API token) and DG_ORG (your organization id). The first creates an asset:
API=https://app.devguard.ch/api
curl -sS -X POST "$API/assets/" \
  -H "Authorization: Bearer $DG_TOKEN" \
  -H "Content-Type: application/json" \
  -d '{
    "organizationId": "'"$DG_ORG"'",
    "name": "Supplier invoice archive",
    "slug": "supplier-invoice-archive",
    "ownerId": "<role id>",
    "status": "ACTIVE",
    "confidentialityRating": 7
  }'
The second retires it. PATCH repeats the required fields and sends null for the two unset ratings:
curl -sS -X PATCH "$API/assets/<asset id>/" \
  -H "Authorization: Bearer $DG_TOKEN" \
  -H "Content-Type: application/json" \
  -d '{
    "name": "Supplier invoice archive",
    "slug": "supplier-invoice-archive",
    "ownerId": "<role id>",
    "status": "RETIRED",
    "confidentialityRating": 7,
    "integrityRating": null,
    "availabilityRating": null
  }'
How is this guide?
Vulnerability classes
Keep the catalog of weaknesses that classifies your risks, so the same weakness has the same name across the register.
Asset classes
Group similar assets so they share default ratings and record the same details, such as a serial number and a calibration date for measuring equipment.