Device policy
Choose which security checks every computer must pass, set the limits for screen lock, password length and updates, and decide when a silent device counts as a problem.
The Device policy is the security baseline for all devices in your organization. It decides which checks a computer must pass to be Compliant, and the limits each check uses. There is one policy per organization. A change reaches each computer at its next check-in, within about an hour, and you do not need to reinstall the agent. A computer's status, Compliant or Non-compliant, is decided at each check-in, so it changes only then. A phone's status changes the next time its owner chooses Confirm settings. Until then, a device can show Non-compliant with Failing checks at 0, for example after you switch off the check it failed.
The tasks below follow the order of the work:
Scripts and integrations: see API below.
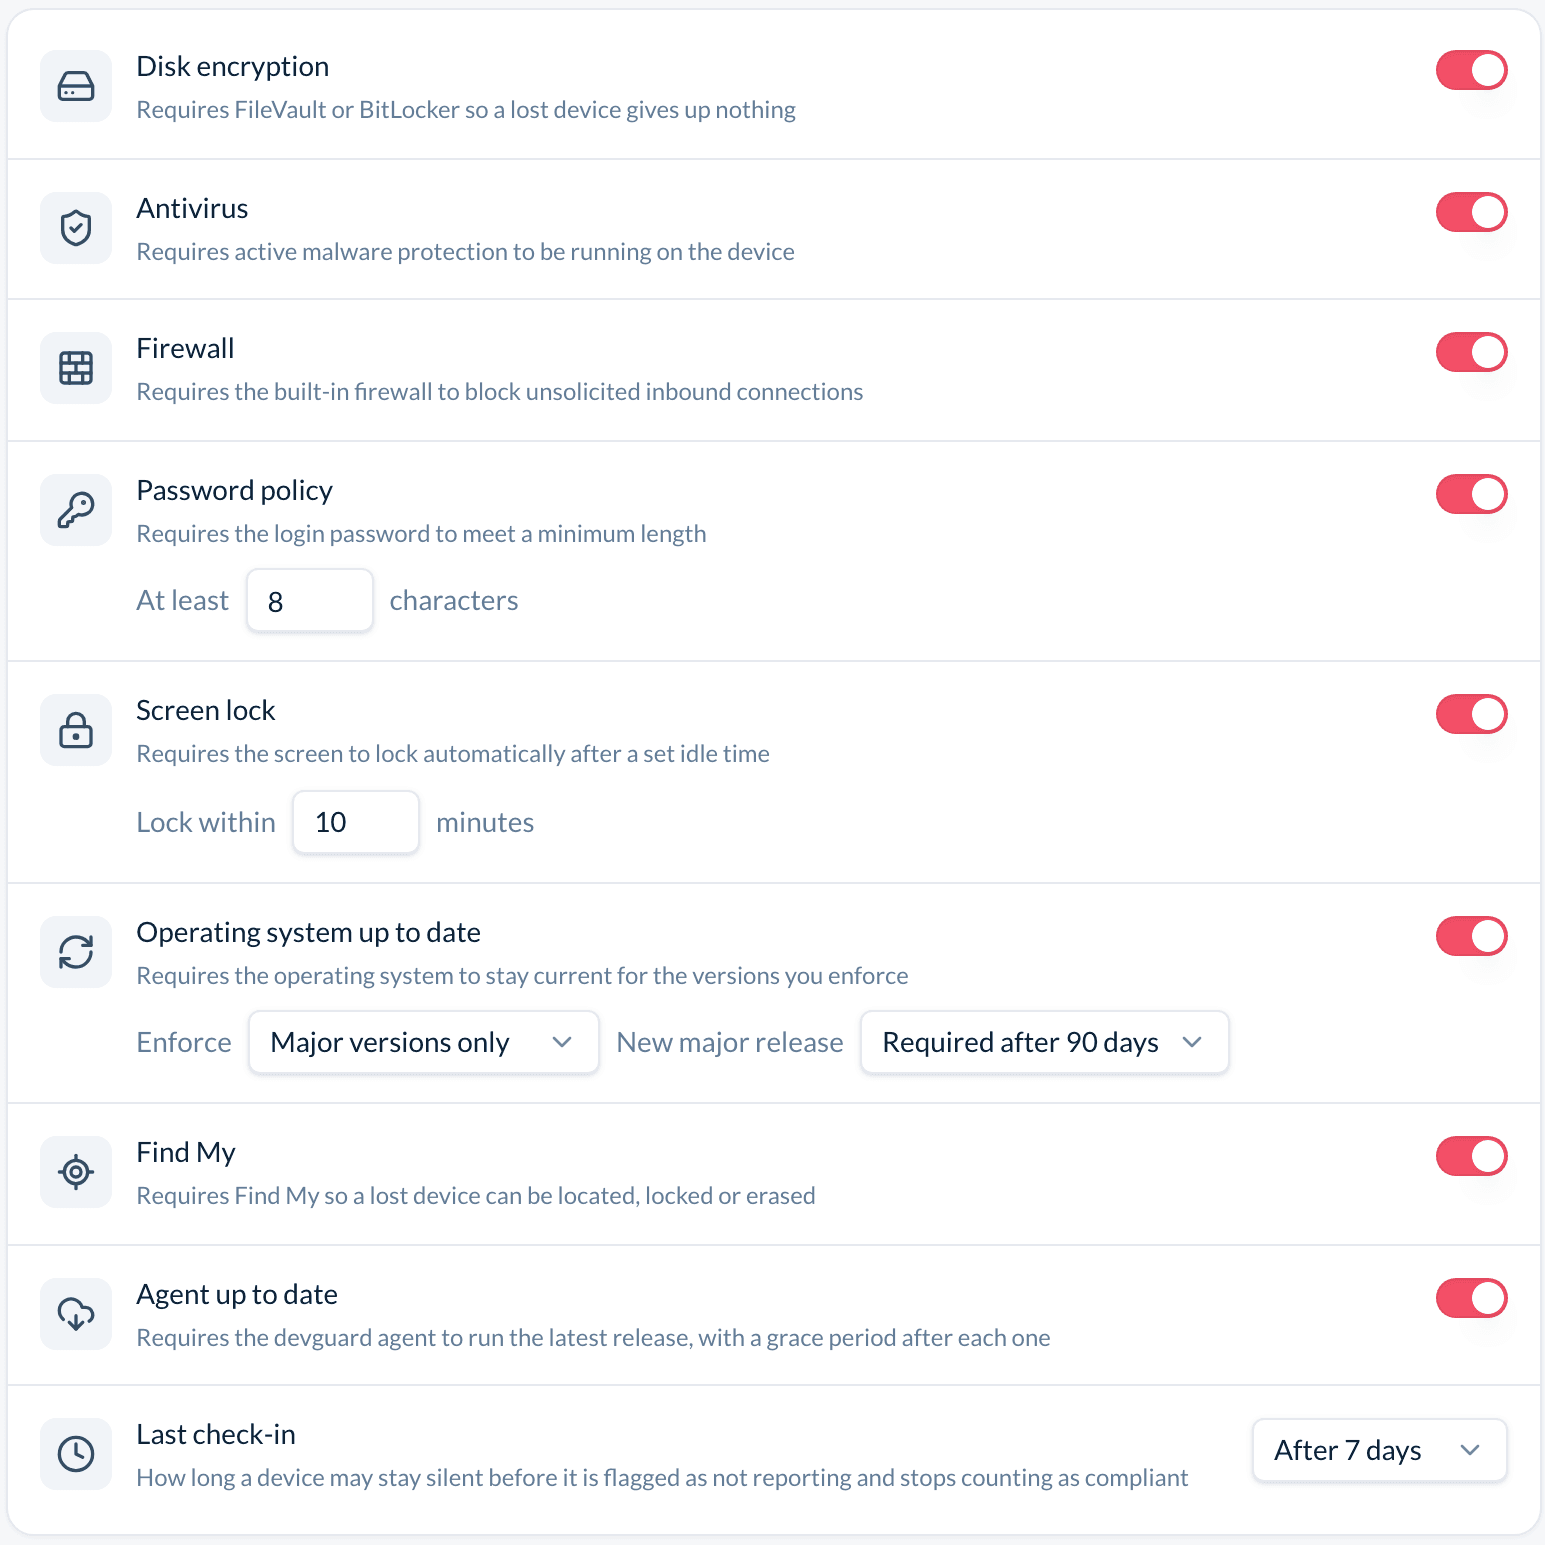
Choose the checks
- In the sidebar, under Devices, choose Device Policy.
- Use the switch next to a check to require it or not. The change is saved at once.
A check that is switched off is not run. It shows Not required on each device and never counts for or against a device. Switch on the checks that match your obligations, for example the controls you must prove for ISO 27001.
Set the limits
- Under Password policy, enter the minimum length after At least. You can choose from 1 to 128 characters.
- Under Screen lock, enter the longest idle time after Lock within. You can choose from 1 to 1440 minutes.
- Click outside the field. The value is saved.
The agent compares these limits with the settings on the computer.
Set the update rule
The Operating system up to date check decides how current the system must be. devguard decides it, not the computer. The agent sends the version number, and devguard compares it with public release data.
- Under Operating system up to date, choose an option next to Enforce.
- If the option includes major versions, choose New major release: how many days after a new major release (for example macOS 26) the computers must run it. You can choose 30, 60, 90 or 180 days.
- If the option includes minor versions, choose New patch: how many days after a patch the computers must have it. You can choose Required immediately, 7, 14 or 30 days.
| Option | A computer fails when |
|---|---|
| Major and minor versions | It does not run the newest major release after the grace period, or it misses a patch after the grace period. |
| Major versions only | It does not run the newest major release after the grace period. A missing patch is allowed. |
| Minor versions only | It misses a patch for its own release after the grace period. It may stay on an older release that is still supported. |
With every option, a release that is no longer supported fails. Patches are tracked for macOS, Windows and Ubuntu. For Debian and Fedora, devguard checks only the end of support and the newest release.
Flag devices that stop reporting
A computer that stops reporting may have a stopped agent, or it may be gone. In the last row, Last check-in, choose how long a device may stay silent.
- Choose After 1 day, or after 7, 14 or 30 days.
- A computer silent for longer shows Not reporting. It no longer counts as compliant in the list, in the evidence figures and in the report.
- Choose Never flag to keep the last result however long the computer is silent. The time of the last check-in still shows everywhere.
Phones do not use this setting. Their owners confirm them every 90 days.
How a check is decided
Most checks run on the computer. The agent reads the setting, compares it with your limit, and sends Pass, Fail or Unknown. Unknown means the agent could not read the setting, for example a password rule that a domain controller sets. Unknown counts against the device, but the list does not show it as a failing check.
Two checks are decided by devguard. Operating system up to date uses the version number and the public release data. Agent up to date compares the agent version with the latest release.
Reference
Checks
| Check | What passes | Default |
|---|---|---|
| Disk encryption | FileVault (macOS), BitLocker (Windows) or LUKS (Linux) is on. | On |
| Antivirus | Malware protection is running. | On |
| Firewall | The built-in firewall blocks unrequested incoming connections. | On |
| Password policy | The login password must have at least the set length. | On, 8 characters |
| Screen lock | The screen locks after at most the set idle time. | On, 15 minutes |
| Operating system up to date | The system meets the update rule. | On, Major and minor versions, 90 days and 14 days |
| Find My | Find My Mac or the Windows Find my device service is on. | On |
| Agent up to date | The agent is on the latest release, or the release is less than 14 days old. | On |
- Find My does not apply to Linux. It is neither passed nor failed there.
- A phone answers only Screen lock and Find My, confirmed by its owner.
- devguard does not track some Linux distributions, such as Arch. On these, Operating system up to date passes. A note says that the version was recorded but not checked.
- devguard does not track some Windows builds, such as Windows Server. On these, the check shows Unknown.
- Until the owner accepts the latest agent disclosure, the agent sends no Find My result. The device then shows Not reported, which does not count against it.
- If devguard cannot reach the release list, Agent up to date keeps its last result.
Permissions
Owners and admins can change the policy. Members and auditors can read it. An organization token can read it over the API.
API
- Endpoint:
GET /devices/policy/withorganizationIdin the query. The policy can be changed in the app only. - Response: one object with a switch per check (
diskEncryptionEnabled,antivirusEnabled,firewallEnabled,passwordPolicyEnabled,screenLockEnabled,osUpToDateEnabled,findMyEnabled,agentUpToDateEnabled) and the limits:
| Field | Meaning |
|---|---|
passwordMinLength | Minimum password length. |
screenLockMaxMinutes | Longest idle time before the screen locks. |
osUpdatePolicy | MAJOR_AND_MINOR, MAJOR_ONLY or MINOR_ONLY. |
osMajorGraceDays | Days until a new major release is required. |
osPatchGraceDays | Days until a new patch is required. |
staleAfterDays | Days of silence before Not reporting. null means Never flag. |
curl -sS -G "https://app.devguard.ch/api/devices/policy/" \
  -H "Authorization: Bearer $DG_TOKEN" \
  --data-urlencode "organizationId=$DG_ORG"
The other calls for devices are on the Devices page.
How is this guide?
App policy
Name the apps every company computer must have, such as a password manager, and the apps none may have, and see on each device whether it follows the list.
Security Questionnaires
Answer the security questionnaires your customers send you, check every answer before it leaves, and reuse each approved answer in the next questionnaire.