App policy
Name the apps every company computer must have, such as a password manager, and the apps none may have, and see on each device whether it follows the list.
The App policy is two lists for all devices in your organization. Required apps must be installed on every computer, for example a password manager. Forbidden apps must not be installed on any computer, for example a remote access tool that IT does not support. The agent checks each list at every check-in. It only answers whether these apps are present. It never sends a list of all installed apps.
The tasks below follow the order of the work:
Scripts and integrations: see API below.
Add an app
- In the sidebar, under Devices, choose App Policy.
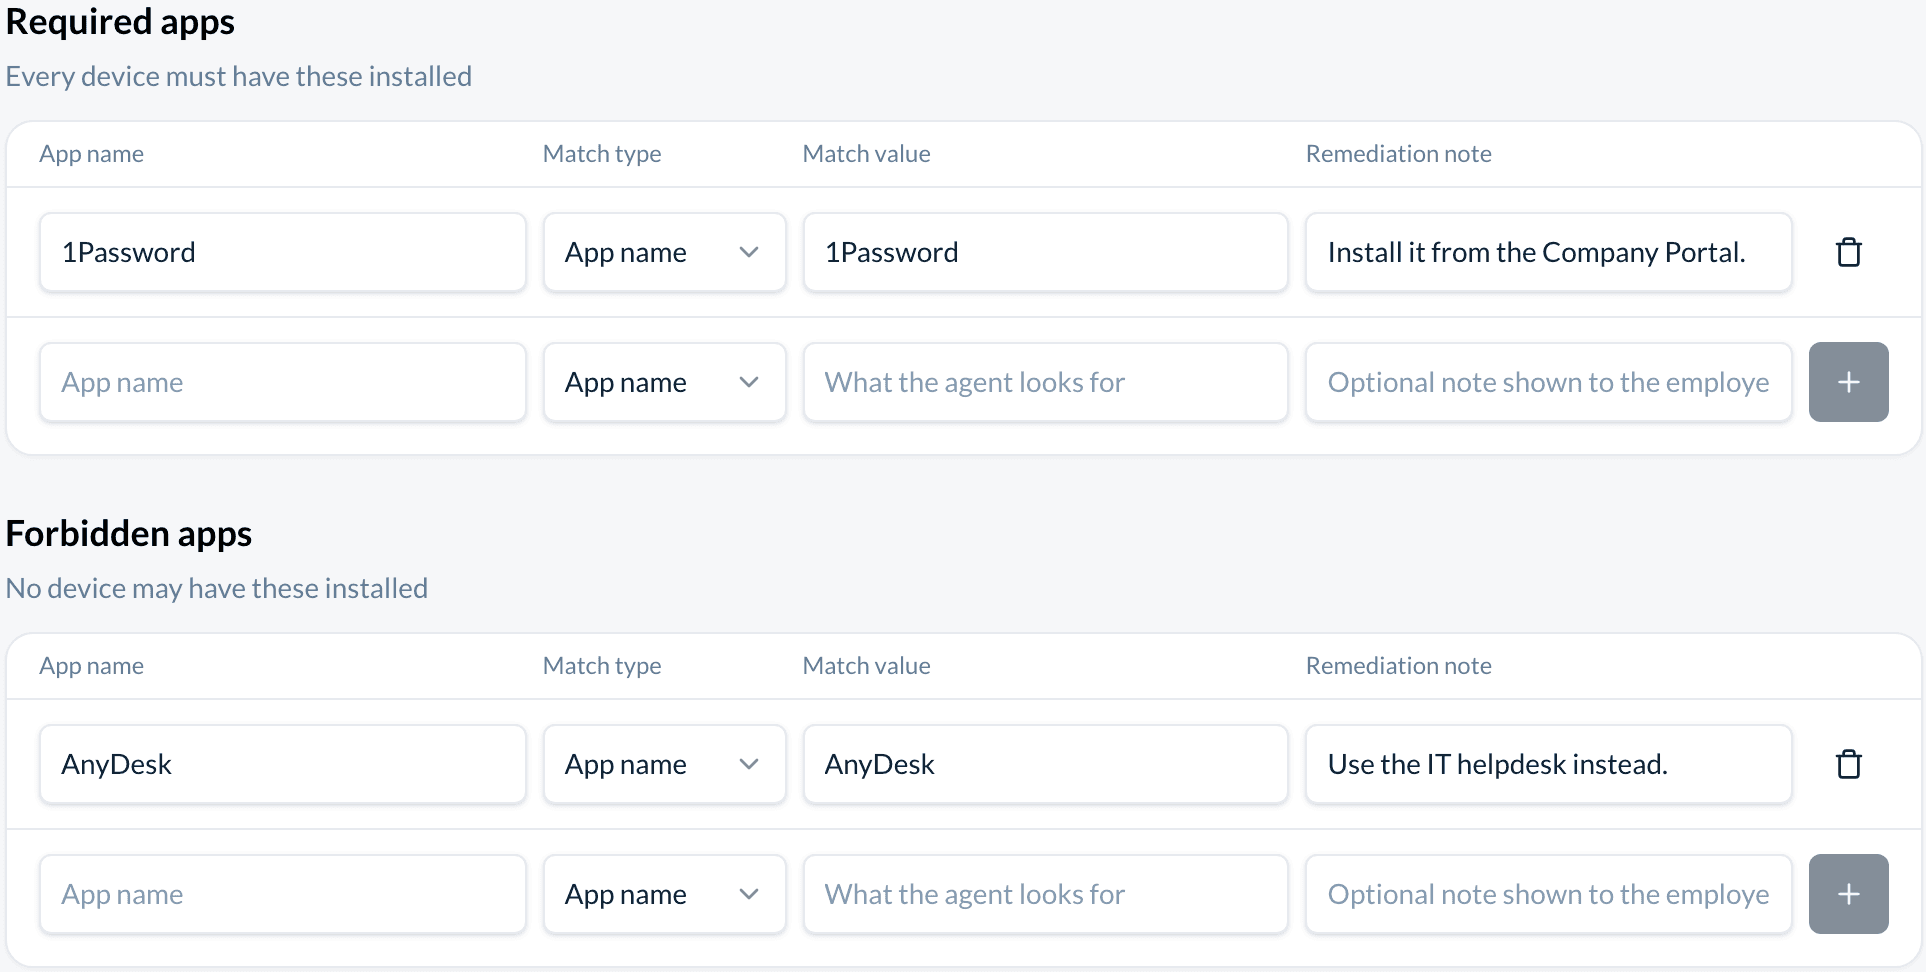
- Go to the empty row under Required apps or Forbidden apps.
- In App name, enter a name that helps you recognize the entry. The agent does not use it to search.
- Choose the Match type and enter the Match value, the text the agent looks for:
- App name: the name the app shows, such as
1Password. Upper and lower case, spaces and punctuation are ignored. For a required app, a name that contains the value also counts. - Bundle id: the macOS identifier, such as
com.1password.1password. Upper and lower case are ignored. - Package name: a Linux package or a Windows Store package, such as
1password. For other Windows programs, use App name.
- App name: the name the app shows, such as
- If you want, write a Remediation note. The employee sees it when the device fails this entry.
- Choose the + button to add the entry.
Change or remove an app
- Change a field in the row. The change is saved when you leave the field.
- To remove an entry, choose the trash icon at the end of its row.
Every computer picks up the change at its next check-in, within about an hour.
Check the results
- Open a device from the Devices list.
- The App policy panel lists each entry with Must be installed or Must not be installed, and the result: Pass, Fail or Not reported.
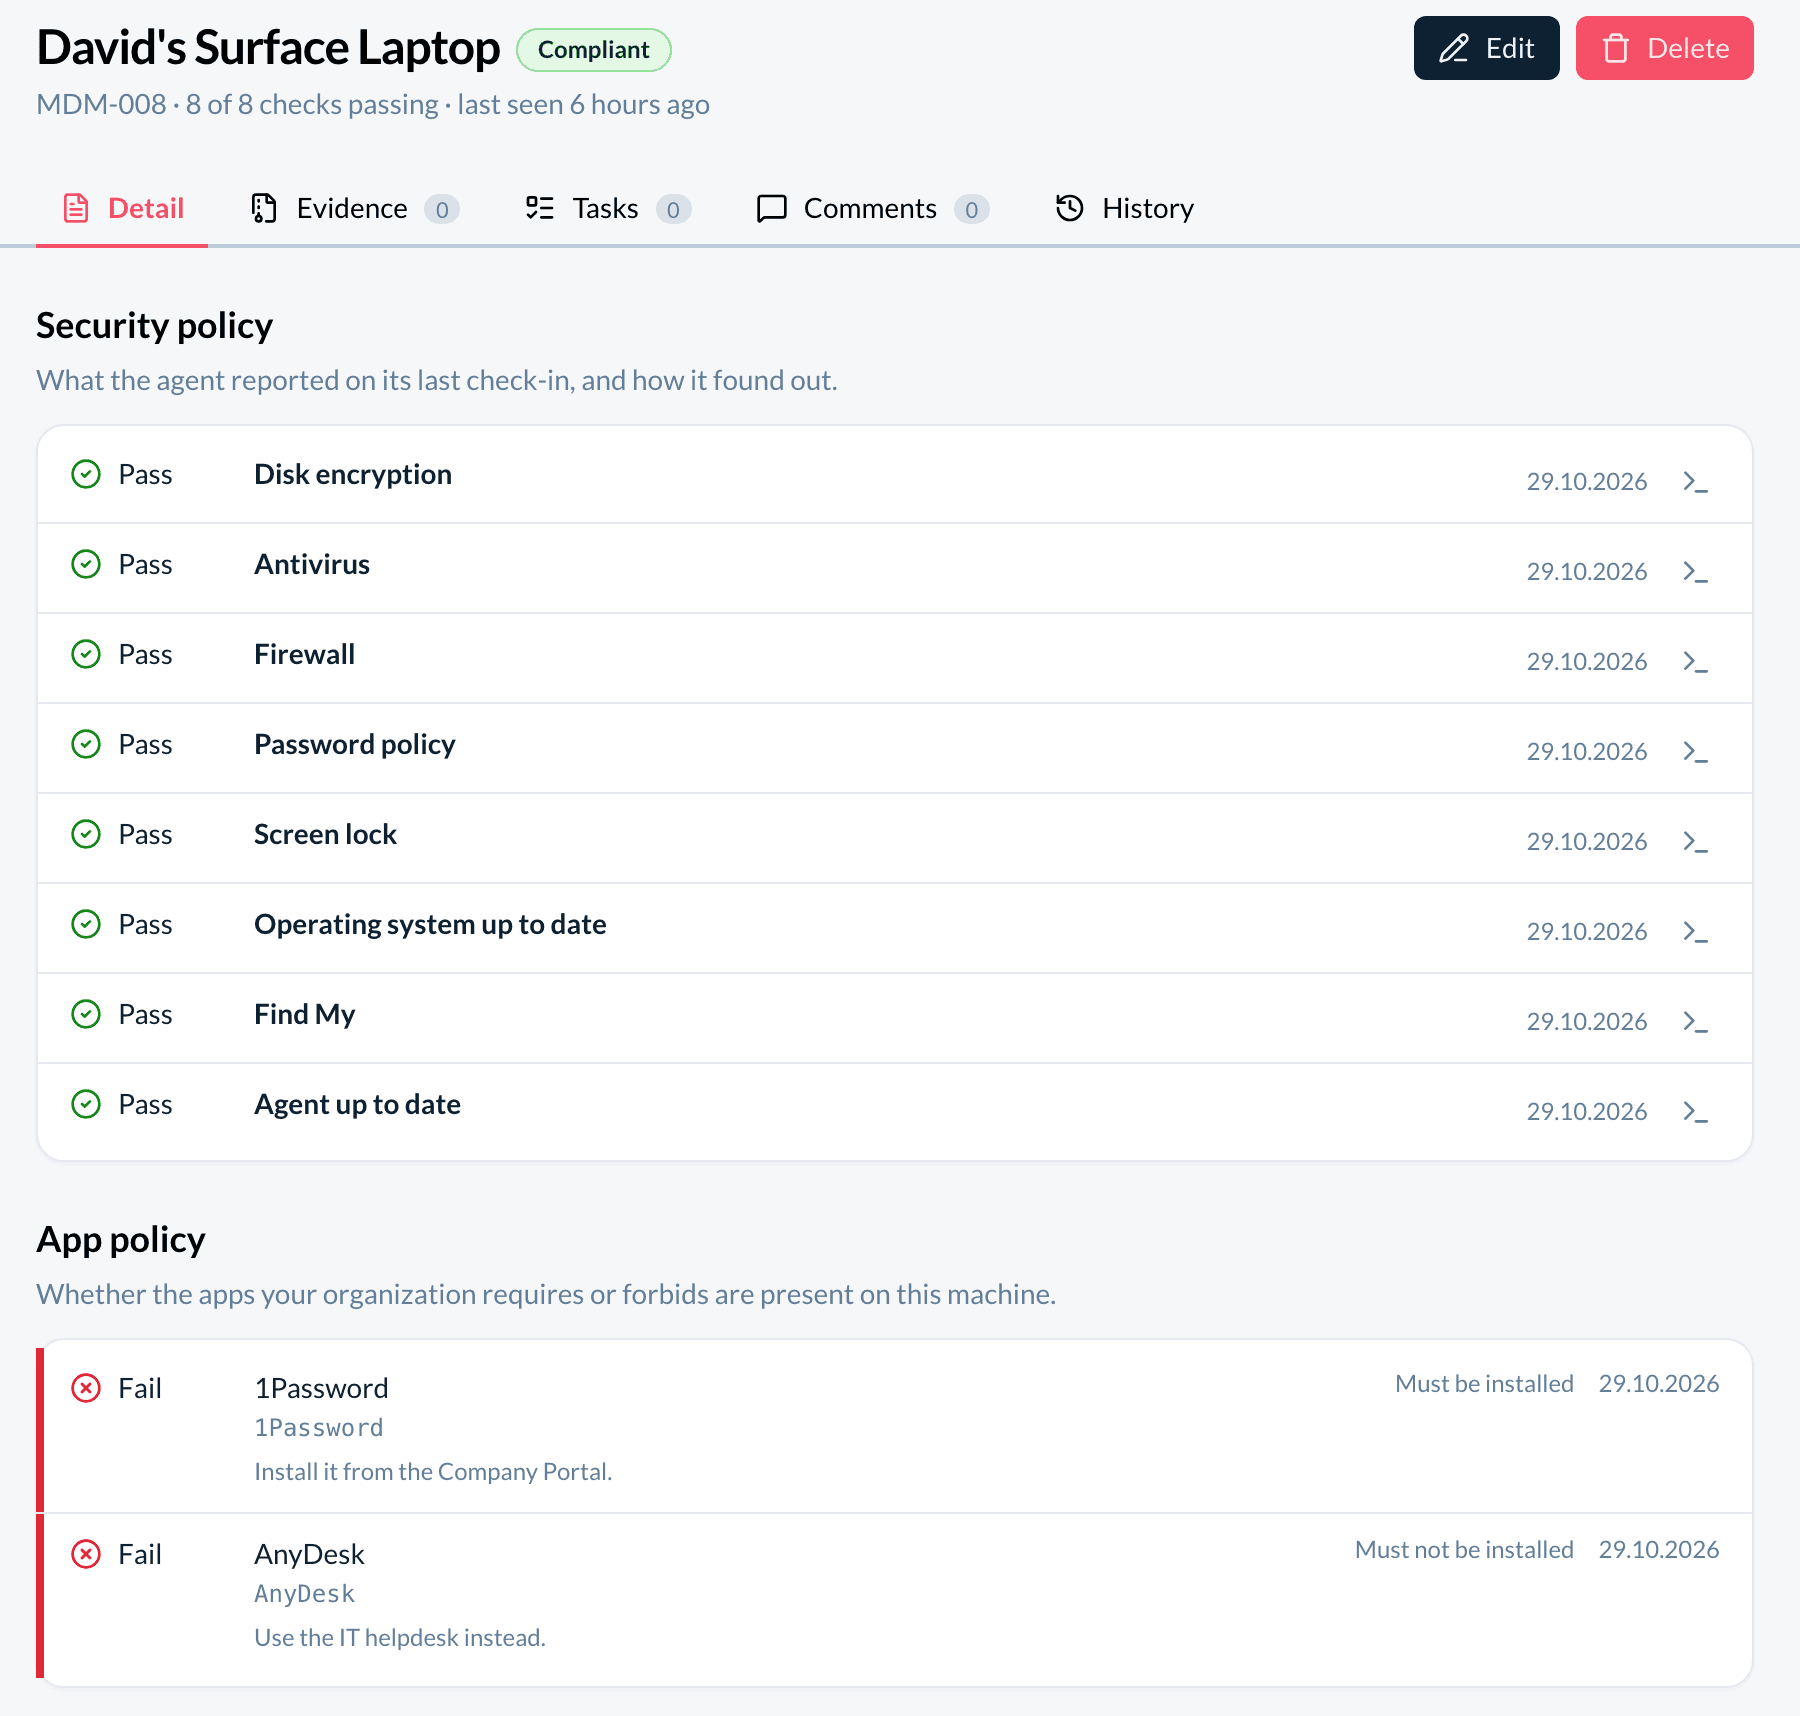
Watch out: the App policy results do not change a device's status. A device can be Compliant and still fail an App policy entry. Check the panel, or ask the employee to follow the note.
In the employee portal, the employee sees the same list for each computer, with your remediation note on each failed entry.
Reference
Fields
| Field | Required | Notes |
|---|---|---|
| App name | yes | A label for you. 2 to 255 characters. |
| Match type | yes | App name, Bundle id or Package name. Starts as App name. |
| Match value | yes | The text the agent looks for. Up to 255 characters. |
| Remediation note | no | Shown to the employee when the entry fails. Up to 1000 characters. |
The same match type and value can appear only once in each list. Phones are not checked against the App policy.
Permissions and limits
Owners and admins can change the lists. Members and auditors can read them. An organization token can read them over the API. The App policy is not part of the Free plan.
API
- Endpoint:
GET /devices/app-policy/withorganizationIdin the query. The lists can be changed in the app only. - Response: an array of entries, each with
id,organizationId,createdAt,updatedAt,name,policyType(REQUIREDorFORBIDDEN),matchType(NAME,BUNDLE_IDorPACKAGE),matchValueandremediationNote.
curl -sS -G "https://app.devguard.ch/api/devices/app-policy/" \
  -H "Authorization: Bearer $DG_TOKEN" \
  --data-urlencode "organizationId=$DG_ORG" \
  | jq '.[] | select(.policyType == "REQUIRED") | .name'
The other calls for devices are on the Devices page.
How is this guide?
Devices
Keep a list of every company computer and phone, check each one against your security rules every hour, and give an auditor the result.
Device policy
Choose which security checks every computer must pass, set the limits for screen lock, password length and updates, and decide when a silent device counts as a problem.