Risk reviews
Review the register at regular intervals, approve or reject each risk against its snapshot, and raise a finding for what does not hold.
A review keeps the register up to date. When it starts, it takes a snapshot (a copy) of every risk in its scope. It has a coordinator and a deadline, and it asks for a decision on each item: approved, or rejected with a reason.
A rejection raises a finding in the findings register. The finding is then tracked to closure like any other nonconformity. A finished review is locked. Its snapshots record what the register said on that day.
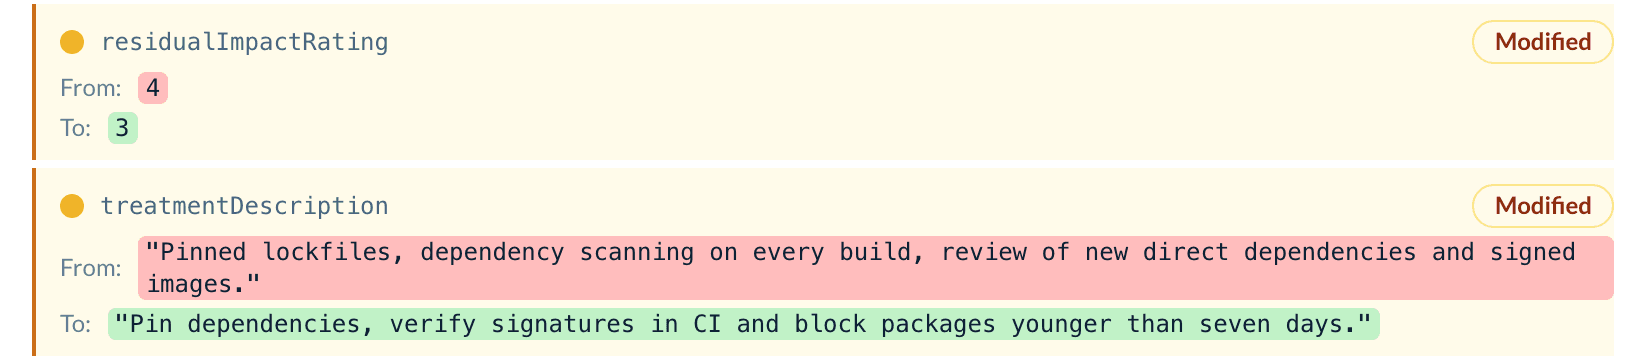
When the member list of the owner role changes, the comparison shows it as a field owner.memberIds with the member's internal id.
Start a review
- Open Risks → Reviews and select Start Risk Review.
- Give it a title, for example "Annual risk register review", and choose the coordinator role.
- Pick the priority: All Risks, or only the High, Medium, or Low ones.
- Set the deadline and add notes for the reviewers. Save.
For a band, devguard uses the higher of a risk's initial and residual level. High covers every level that is not acceptable, so on the defaults it includes Critical. Low is only the lowest level, and Medium covers the other acceptable levels. A risk with no rating is left out of a band review. Opportunities join only a review of all risks.
The review creates one item per risk in scope. Each item holds a snapshot of the risk and the version of the risk criteria in force. The coordinator role gets a notification, and the deadline appears on Deadlines.
Decide each item
- Open the review. Each item shows its snapshot. Under Compare with, choose the risk's latest version or the snapshot of another review. Switch between Inline View and Split View. Summary of Changes lists what changed, or says No changes.
- Select Approve when the risk is still correct.
- Select Reject when it is not. Give a reason and a finding type: major or minor nonconformity, observation, or opportunity for improvement.
- To set an item back to pending while the review is open, select Withdraw.
A rejected item's finding gets the next free number: NC-, OBS-, or OFI-. If a later review of the same kind is already planned, its deadline becomes the finding's deadline. Withdrawing or approving a rejected item archives its finding with a note that says why. devguard never deletes the finding.
The review page lists the findings it raised. It also lists the open findings from earlier risk reviews, so the coordinator sees what is still open.
Finish the review
- When every item is approved or rejected, select Finish Review and confirm. The review is now locked. Its items cannot change, and you cannot reopen it.
- Select Generate Report to open the review under Reports, for the auditor or the management review.
A risk counts as reviewed as soon as it is approved in a review that is not archived, before the review is finished. It then clears the overview's Review due finding and counts for the Reviewed within the interval step.
Reference
Fields
| Field | Holds |
|---|---|
| Title | The name of the review; required |
| Coordinator | The role that runs it; required and notified |
| Priority | All Risks, High Risks Only, Medium Risks Only, or Low Risks Only; fixed once started |
| Deadline | When the review should be finished |
| Notes | Information for the reviewers |
A review gets an ID: RAR-001, RAR-002, and so on. The list shows the coordinator, the start and end, the deadline, and how many items are approved and how many remain. It filters by Coordinator, In progress, and Archived. A review's detail has Comments, Tasks, and History tabs.
What a review does not do
A review does not change the risks. It records a decision about the register as it was. You correct the risk itself, and the finding tracks the follow-up. Editing a risk during a review does not change the snapshot. The comparison shows the difference.
Limits and permissions
The free plan holds 4 risk reviews. The business plans have no limit. Owners, admins, and organization tokens start, decide, finish, archive, and delete reviews. Members and auditors can only read.
API
| Method | Path | Purpose |
|---|---|---|
GET, POST | /risk-reviews/ | List and start reviews |
PATCH | /risk-reviews/{id}/ | Update title, notes, deadline, coordinator, or finishedAt |
POST | /risk-reviews/{id}/archive/ | Archive |
POST | /risk-reviews/{id}/restore/ | Restore |
GET, DELETE | /risk-review/{id}/ | Read or delete (singular path) |
PATCH | /risk-review-items/{id}/ | approved true to approve, or null to withdraw |
POST | /risk-review-items/{id}/reject/ | Reject with reason and findingType; returns the finding |
Sending finishedAt finishes the review. It works only when every item is decided, and a finished review cannot be reopened. The AI assistant and MCP list reviews with listRiskReviews.
How is this guide?