Access reviews
Check, asset by asset, that the right roles have access when someone joins, when someone leaves, and on a regular schedule, and keep a record an auditor can follow.
ISO/IEC 27001 asks you to review access rights at regular intervals and when people join or leave (Annex A 5.18). An access review does this in devguard. It lists every asset that the chosen roles have access to, and a reviewer decides each one. Wrong access becomes a finding in the findings register.
An access review checks the Memberships of your assets: the roles whose members may use them. Record those first, on each asset under Access Management. An access review is not an asset review, which checks that the inventory itself is still correct.
The tasks below follow the order of the work:
Scripts and integrations: see API below.
Start an access review
- Open Assets → Access Reviews and choose Start Entitlement Review.
- Enter a Title, such as "Quarterly access review".
- Choose the Review Type:
- Onboarding for someone who joins. Each asset asks you to grant access.
- Offboarding for someone who leaves. Each asset asks you to revoke access.
- Periodic Review for a regular check. Each asset asks you to verify access.
- Choose the Coordinator role. Its members are notified and run the review.
- Set a Deadline if you want one.
- Under Targets, choose the Target Roles, or one Target Employee. For an employee, the review uses all roles the person holds.
- Choose Create. The review lists every asset on which one of these roles has a membership.
If the roles have no membership on any asset, devguard refuses the review, because there is nothing to check.
Decide each asset
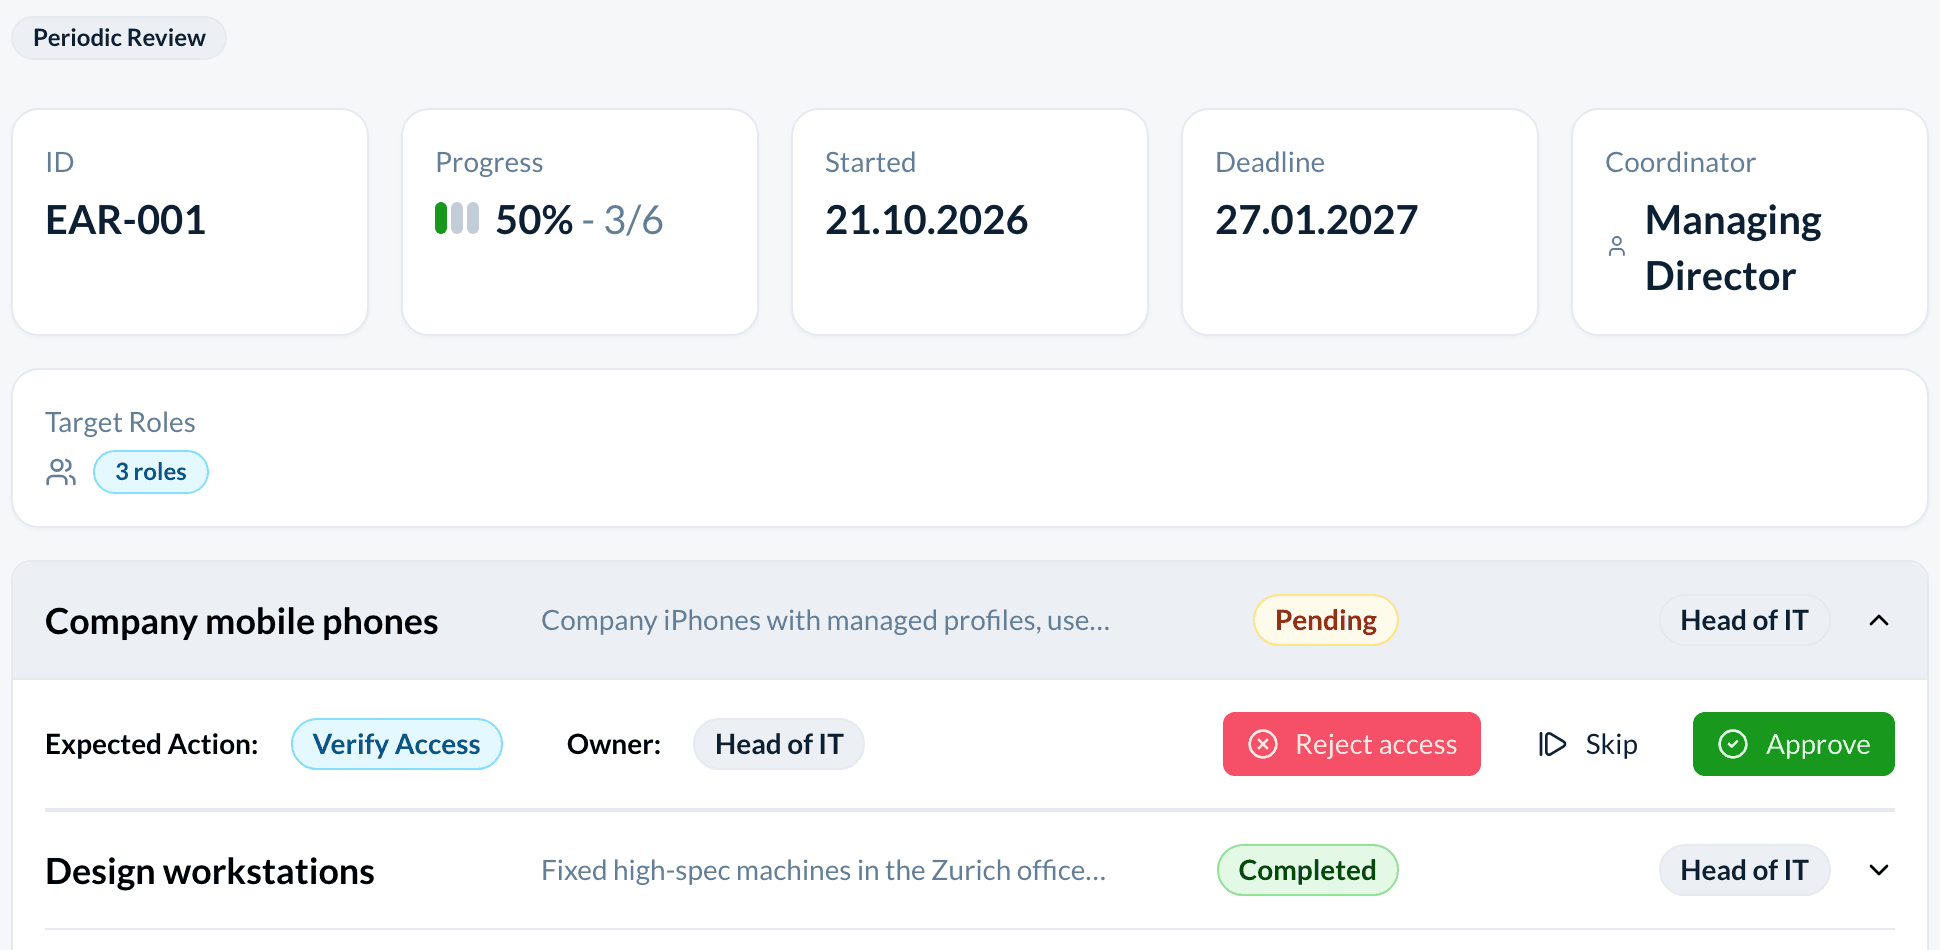
- Open the review and click an asset to expand it. It shows the Expected Action (Grant Access, Revoke Access or Verify Access) and the asset's Owner role.
- Check the access in the system itself, for example in the admin console of your cloud provider.
- Choose one of these:
- Approve when the access is correct, or when you have made the change. The asset shows Completed.
- Skip when the asset does not apply. The asset shows Skipped.
- Reject access when the access is wrong and you cannot fix it now. Choose a Finding type, write the Reason and choose Reject and raise finding.
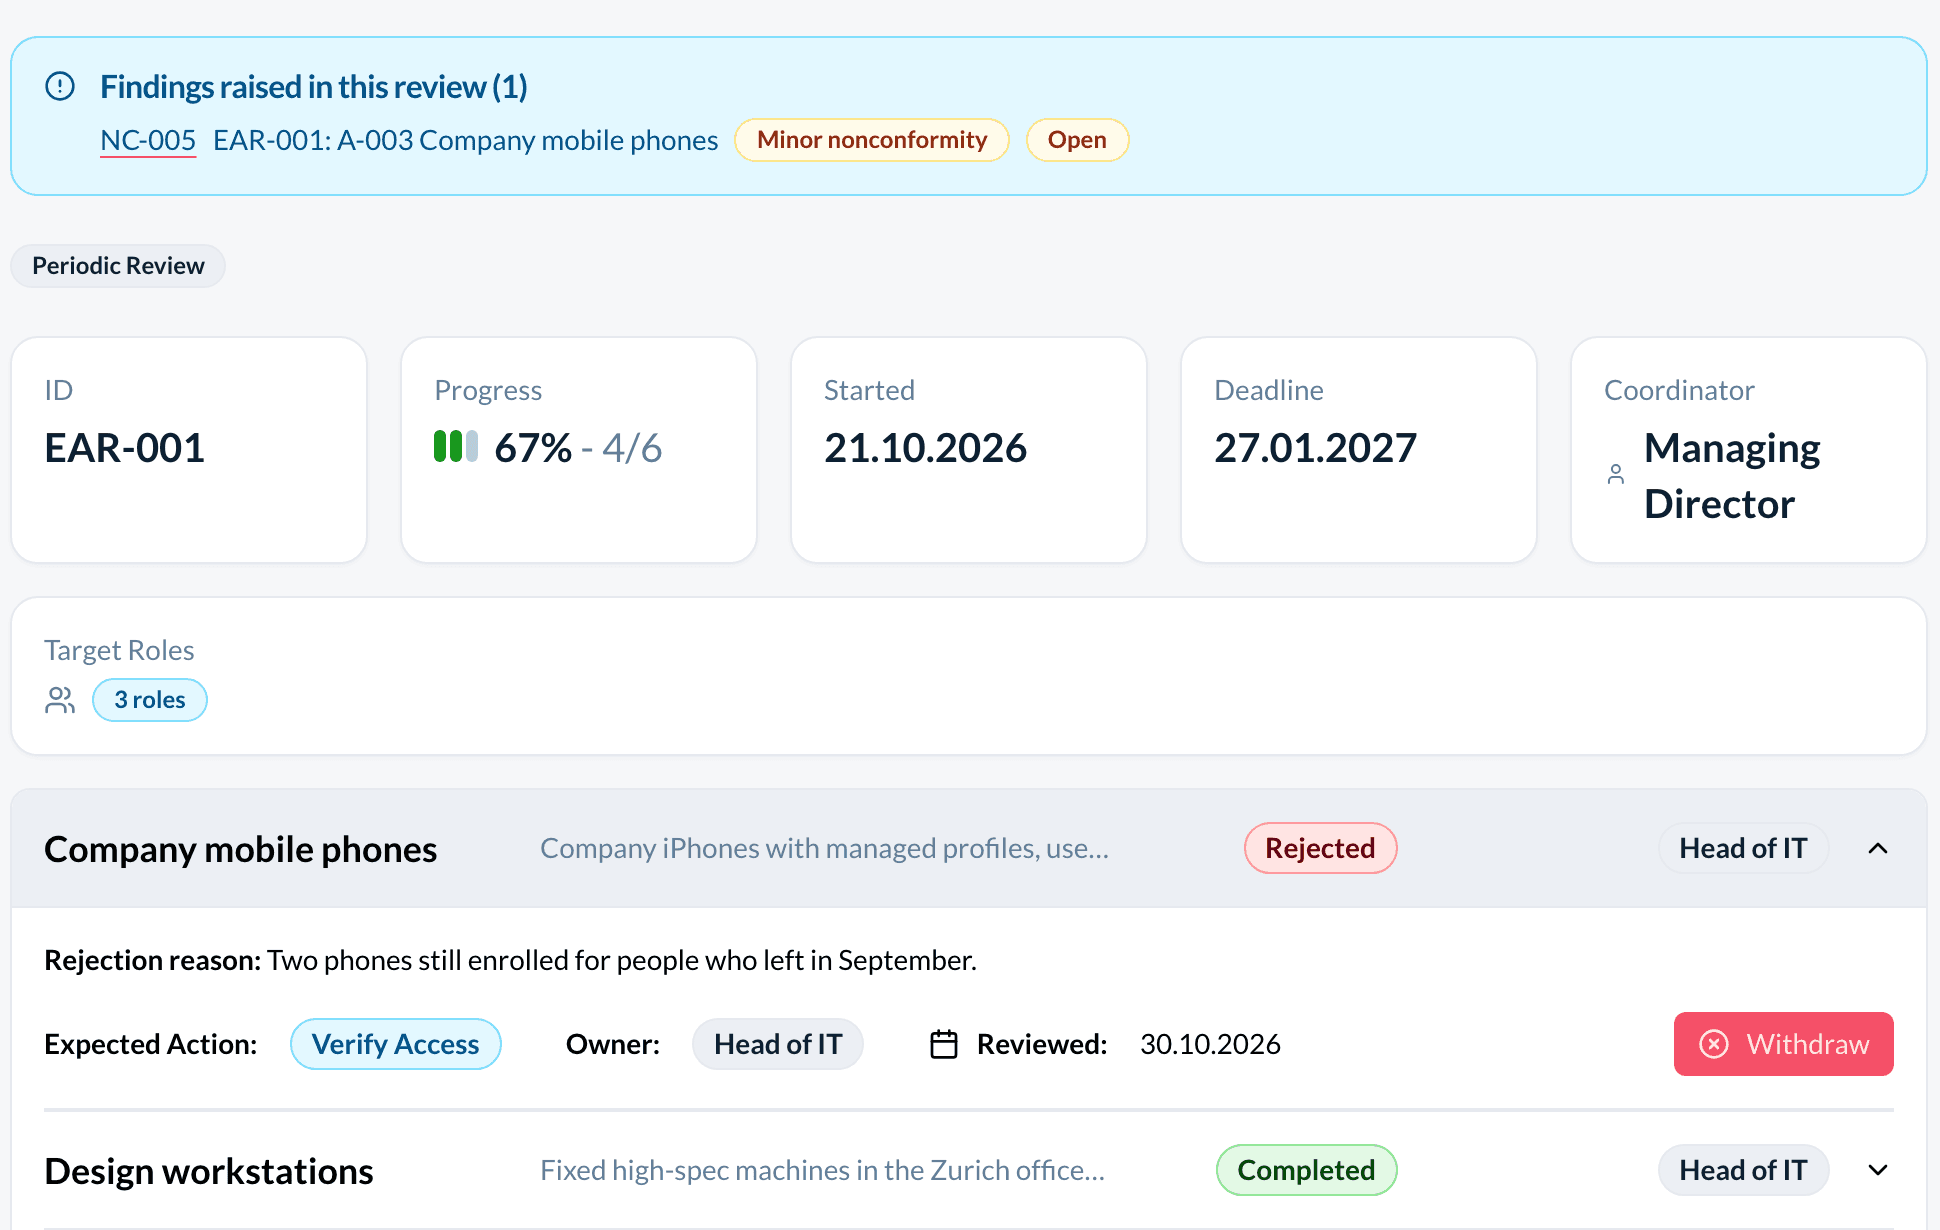
A rejected asset shows Rejected with its reason. The finding is numbered NC-, OBS- or OFI-, after the findings you already have. It stays open in the findings register until you close it, and the next access review of the same type shows it.
To change a decision, choose Withdraw. The asset goes back to Pending, and the finding of a rejected asset is archived with a note.
Watch out: devguard records your decision. It does not grant or remove any access. Make the change in the system itself.
Complete the review
- When no asset is Pending any more, choose Complete Review.
- To keep a copy for the auditor, open Actions and choose Generate Report.
A completed review is locked. Its decisions cannot change, but you can still edit its title and deadline.
Reference
Fields
| Field | Required | Notes |
|---|---|---|
| Title | yes | |
| Review Type | yes | Onboarding, Offboarding or Periodic Review. |
| Coordinator | yes | A business role. Its members are notified. |
| Deadline | no | Shown in the list and on the review. |
| Description | no | |
| Target Roles | one of the two | Roles whose memberships are reviewed. |
| Target Employee | one of the two | A person. The review uses all of their roles. |
Statuses of an asset in the review
| Status | Set by |
|---|---|
| Pending | The start, or Withdraw |
| Completed | Approve |
| Skipped | Skip |
| Rejected | Reject access, with a finding |
The review shows its progress as the decided assets out of all assets. A rejected asset counts as decided. Each review gets a number such as EAR-001.
Permissions and limits
Owners and admins start reviews and decide assets. Members and auditors read them. On the Free plan you can keep 4 access reviews. Archived reviews do not count. See Assets.
Watch out: deleting an asset also deletes its rows in access reviews, even in completed ones. Archive the asset instead.
API
| Call | Endpoint | Organization id |
|---|---|---|
| List | GET /entitlement-reviews/ | query, required |
| Start | POST /entitlement-reviews/ | body, required |
| Read | GET /entitlement-review/{id}/ | not used |
| Update or complete | PATCH /entitlement-reviews/{id}/ | not used |
| Archive | POST /entitlement-reviews/{id}/archive/ | not used |
| Restore | POST /entitlement-reviews/{id}/restore/ | not used |
| Delete | DELETE /entitlement-review/{id}/ | not used |
| Decide an asset | PATCH /entitlement-review-items/{id}/ | not used |
| Reject an asset | POST /entitlement-review-items/{id}/reject/ | not used |
Read and delete use the singular path /entitlement-review/{id}/. All other calls use the plural.
The review type is ONBOARDING, OFFBOARDING or REVIEW (Periodic Review). Send businessRoleIds or an employeeId, which is the person's member id, not their user id.
To decide an asset, send actualStatus: COMPLETED (Approve), SKIPPED (Skip) or PENDING (Withdraw). The reject call takes reason and findingType: MAJOR_NONCONFORMITY, MINOR_NONCONFORMITY, OBSERVATION or OPPORTUNITY_FOR_IMPROVEMENT. To complete the review, send finishedAt with PATCH /entitlement-reviews/{id}/. While an asset is still pending, the call returns 412.
How is this guide?
Asset classes
Group similar assets so they share default ratings and record the same details, such as a serial number and a calibration date for measuring equipment.
Asset reviews
Confirm once a year, or more often, that every entry in your asset inventory is still correct, and turn what is wrong into a finding.